
libfido2
 yubico/libfido2
Provides library functionality for FIDO2, including communication with a device over USB or NFC.
authenticationcryptographyhardware-security+2
74911 days ago
yubico/libfido2Provides library functionality for FIDO2, including communication with a device over USB or NFC.
 wolfssl/wolfguard
FIPS 140-3 compliant VPN kernel module and user tool, drop-in replacement for WireGuard with AES-256-GCM, SHA2-256, and SECP256R1 cryptography for…
 vid4l-07/klip
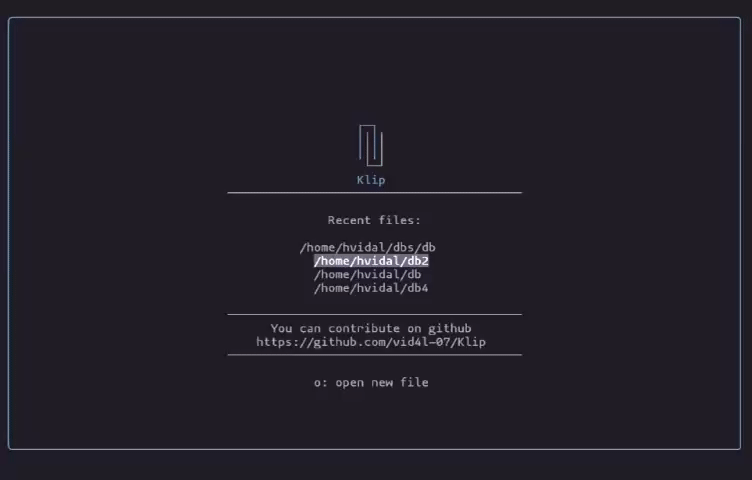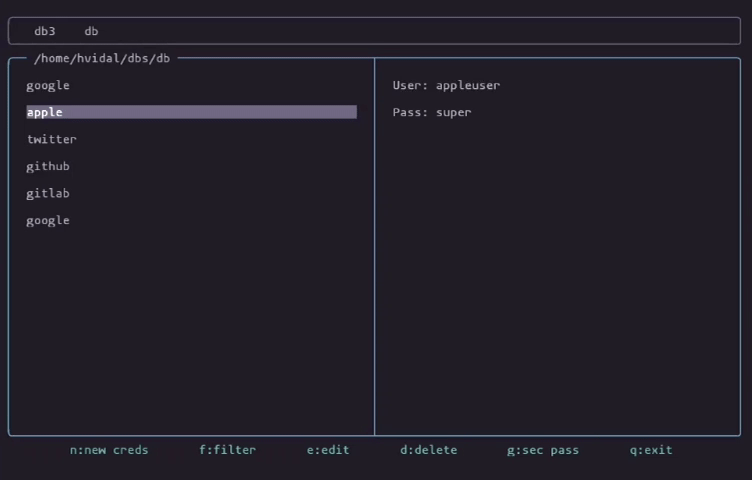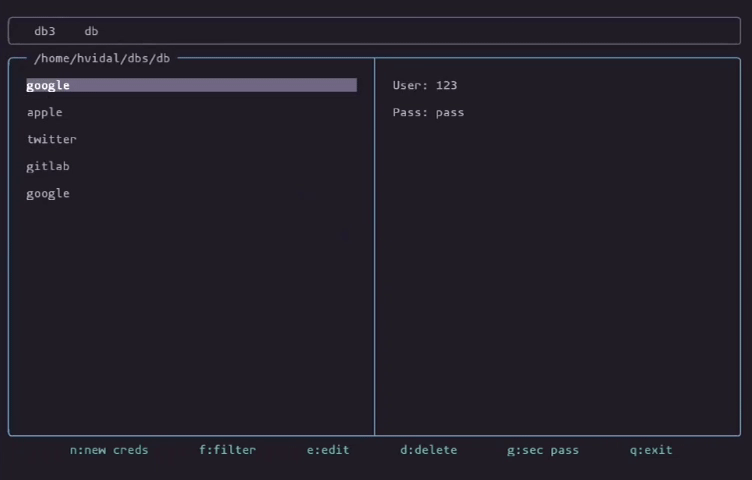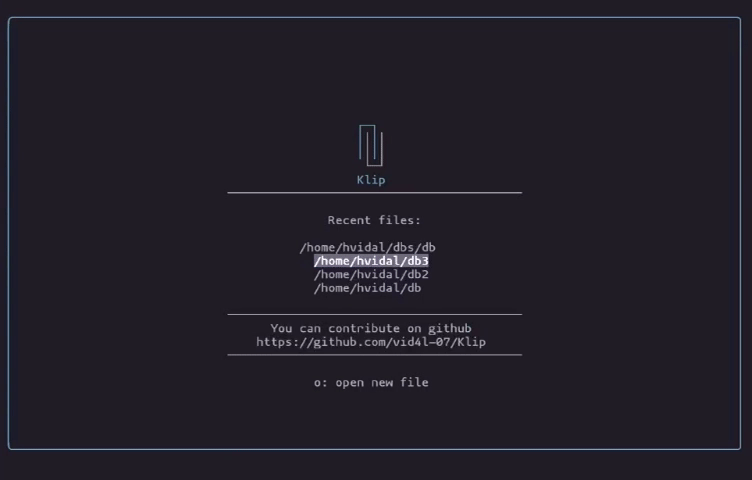
Minimal terminal-based password manager
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 openssh/openssh-portable
Portable OpenSSH
 foxboron/attezt
An open-source TPM device-attest-01 CA server

 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
 secnigma/cve-2021-3560-polkit-privilege-esclation
Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 bugch3ck/imposter
Proof of concept for CVE-2015-0006. Fixed in MS15-005 https://docs.microsoft.com/en-us/security-updates/SecurityBulletins/2015/ms15-005 .
 shivshantp/cve-2025-5777-trendmicro-apexcentral-rce
PoC for CVE-2025-5777 – Auth Bypass and RCE in Trend Micro Apex Central
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…