Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
42 results
Exploit-CVE-2024-9513-NetAdmin-IAM-Allows-User-Enumeration-In-Active-Directory preview

Exploit-CVE-2024-9513-NetAdmin-IAM-Allows-User-Enumeration-In-Active-Directory

GitHubelizeuopain/exploit-cve-2024-9513-netadmin-iam-allows-user-enumeration-in-active-directory

Proof-of-concept exploit for CVE-2024-9513 targeting user enumeration in NetAdmin IAM via HTTP POST request to…

authenticationexploitationinformation-gathering+3
2
1 year ago
CVE-2026-44596 preview

CVE-2026-44596

GitHubex-cal1bur/cve-2026-44596

YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…

api-security-testingauthenticationpassword-attacks+3
3 months ago
CVE-2025-31161 preview

CVE-2025-31161

GitHubshisones/cve-2025-31161

A proof of concept for CVE-2025-31161, using mangled HTTP header to perform unauthenticated impersonation of any user in Crush FTP server.

authenticationexploitationpenetration-testing+3
6 months ago
PoC_CVE-2019-0217 preview

PoC_CVE-2019-0217

GitHubsavsch/poc_cve-2019-0217

Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…

authenticationeducationexploitation+3
1 year ago
Digisol-DG-GR1321-s-Password-Policy-Bypass-CVE-2024-2257 preview

Digisol-DG-GR1321-s-Password-Policy-Bypass-CVE-2024-2257

GitHubredfox-security/digisol-dg-gr1321-s-password-policy-bypass-cve-2024-2257

Exploit for CVE-2024-2257: bypasses password policy on Digisol DG-GR1321 routers via crafted HTTP request, enabling unauthorized access for…

authenticationexploitationpenetration-testing+2
2 years ago
CVE-2025-0108-Authentication-Bypass-checker preview

CVE-2025-0108-Authentication-Bypass-checker

GitHubbarcrange/cve-2025-0108-authentication-bypass-checker

Python script that tests PAN-OS devices for CVE-2025-0108 authentication bypass by sending crafted HTTP requests and analyzing responses.

authenticationexploitationpenetration-testing+3
1 year ago
tough-cookie-patch-cve-2023-26136 preview

tough-cookie-patch-cve-2023-26136

GitHubguy2610/tough-cookie-patch-cve-2023-26136

RFC6265-compliant cookie parsing and CookieJar management library for Node.js, with CVE-2023-26136 security patch. Supports cookie creation,…

authenticationencryption-decryption-toolsgeneral-purpose-utilities+2
1 year ago
Responder preview
Archived

Responder

GitHubspiderlabs/responder

Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…

authenticationdns-analysisexploitation+8
4.9k6 years ago
ExchangeRelayX preview

ExchangeRelayX

GitHubquickbreach/exchangerelayx

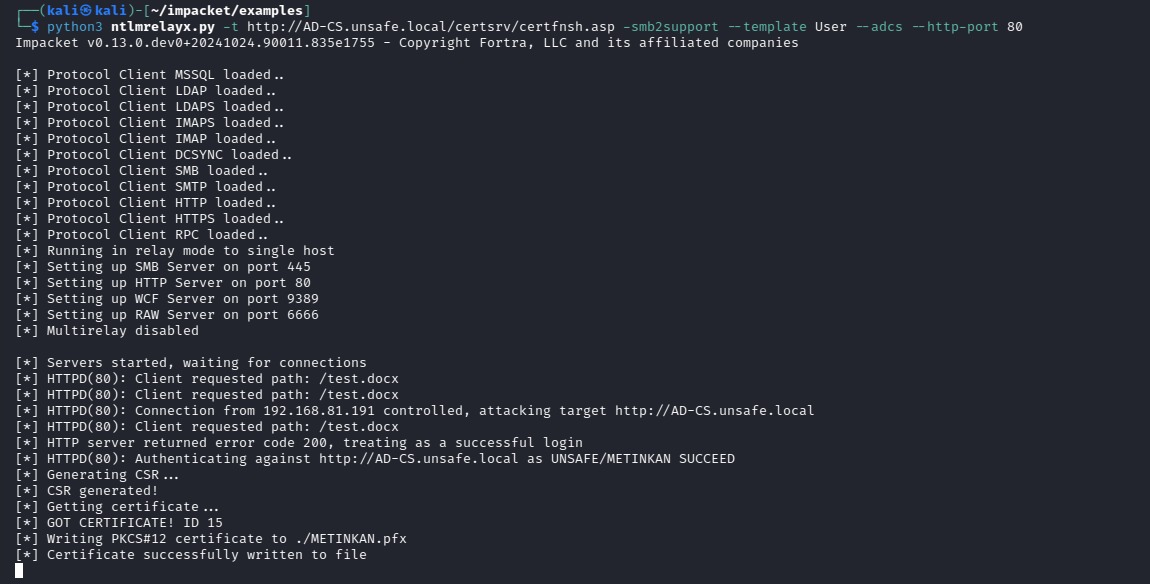
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.

authenticationemail-securityexploitation+7
3058 years ago
route-detect preview

route-detect

GitHubmschwager/route-detect

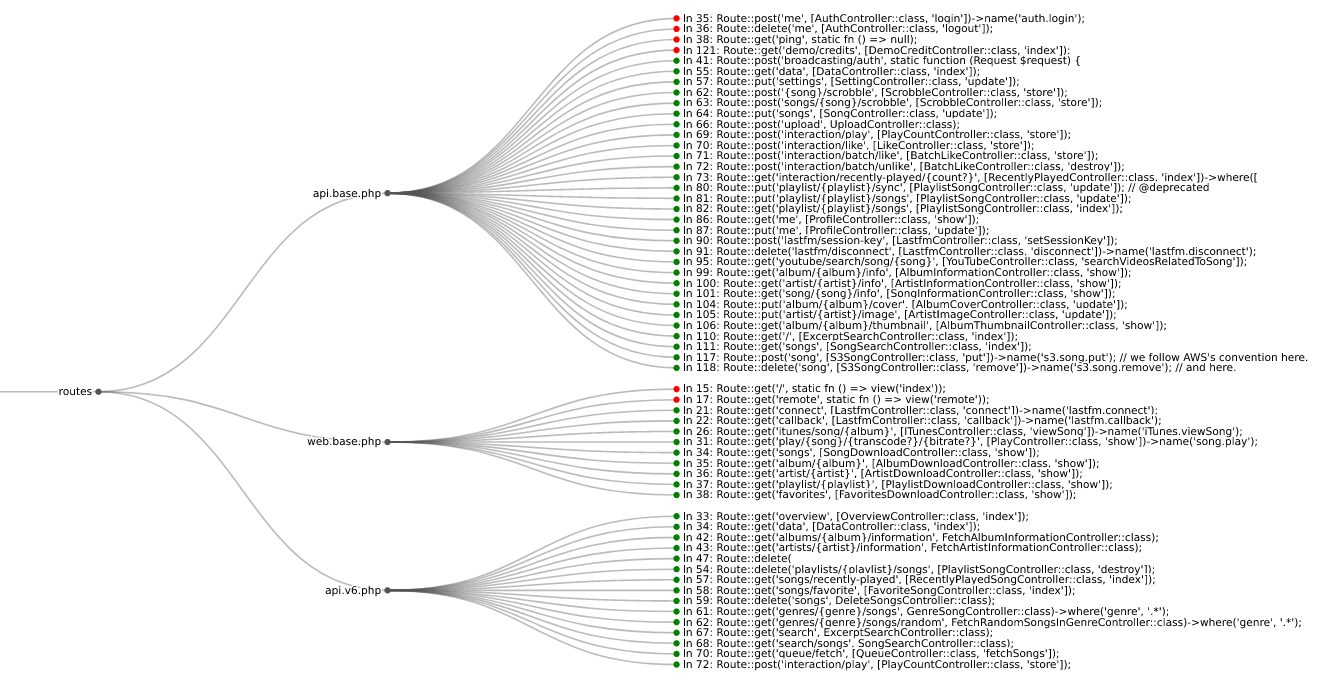
Find authentication (authn) and authorization (authz) security bugs in web application routes.

authenticationstatic-analysisvulnerability-analysis+1
2801 year ago
CVE-2024-38200 preview

CVE-2024-38200

GitHubpasstheticket/cve-2024-38200

CVE-2024-38200 & CVE-2024-43609 - Microsoft Office NTLMv2 Disclosure Vulnerability

authenticationeducationexploitation+4
1471 year ago
Prox-Ez preview

Prox-Ez

GitHubsynacktiv/prox-ez

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

authenticationimpersonation-toolslateral-movement+4
1133 months ago
knocker preview

knocker

GitHubfariszr/knocker

Knocker, a knock based access control service for your homelab

api-securityauthenticationcloud-security+2
13519 days ago
CVE-2023-20198 preview

CVE-2023-20198

GitHubsmokeintheshell/cve-2023-20198

CVE-2023-20198 Exploit PoC

authenticationcommand-and-controlexploitation+3
665 months ago
CVE-2017-14263 preview

CVE-2017-14263

GitHubzzz66686/cve-2017-14263

Proof-of-concept exploit for CVE-2017-14263 in Honeywell NVR devices. Demonstrates session hijacking and privilege escalation from guest to admin via…

authenticationexploitationiot-security+3
59 years ago
CVE-2026-66908 preview

CVE-2026-66908

GitHuboscerd/cve-2026-66908

Proof-of-concept reproducer for Apache Camel JWT authentication bypass (CVE-2026-66908) demonstrating missing iss/aud validation in…

authenticationeducationexploitation+2
22 days ago
CVE-2026-24207 preview

CVE-2026-24207

GitHuboffseckit/cve-2026-24207

CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.

authenticationcloud-securitycommand-and-control+8
12 months ago
CVE-2026-40022 preview

CVE-2026-40022

GitHuboscerd/cve-2026-40022

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths

authenticationexploitationmisconfiguration+3
2 months ago
Previous123Next