CVE-2016-6210-Exploit
 justlce/cve-2016-6210-exploit
OpenSSH Username Enumeration - CVE-2016-6210
authenticationexploitationinformation-gathering+3
3
justlce/cve-2016-6210-exploitOpenSSH Username Enumeration - CVE-2016-6210
 randomrobbiebf/cve-2024-6624
JSON API User <= 3.9.3 - Unauthenticated Privilege Escalation
 bugch3ck/imposter
Proof of concept for CVE-2015-0006. Fixed in MS15-005 https://docs.microsoft.com/en-us/security-updates/SecurityBulletins/2015/ms15-005 .
 ap0dexme0/cve-2023-27350
Perfom With Massive Authentication Bypass In PaperCut MF/NG
 d0n601/cve-2025-4603
eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Deletion
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
 jenderal92/cve-2026-5118
CVE-2026-5118 – Python2 mass exploit for Divi WordPress plugin Unauthenticated administrator registration via admin-ajax.php. Multi‑threaded scanner…
 wr0x00/cve-2022-23131
Exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Generates a signed session cookie to gain unauthorized admin access.
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…
 d0n601/cve-2025-4602
eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Read
 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
 d0n601/buffalo
A python3 multithreaded SSH dictionary attack tool
 t3slaa/cve-2024-55374
CVE-2024-55374
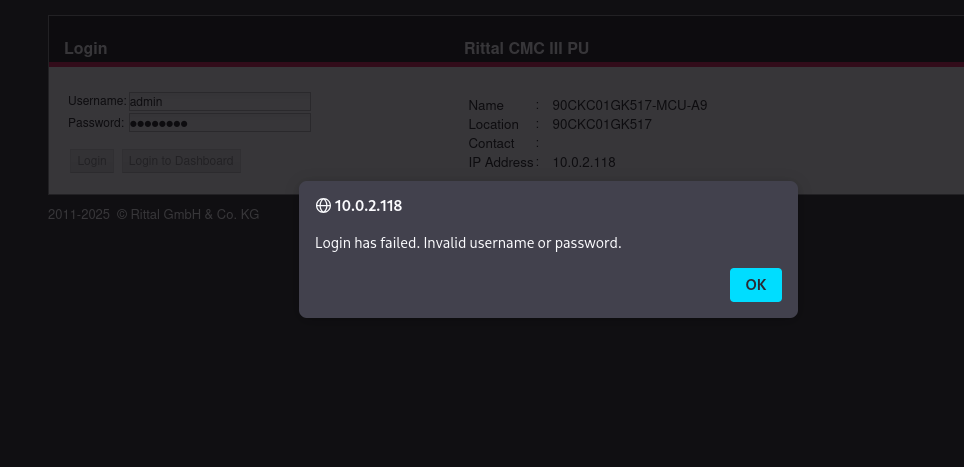 nrtlox/cve-2025-63587
CVE-2025-63587
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 rxerium/cve-2024-7593
Incorrect implementation of an authentication algorithm in Ivanti vTM other than versions 22.2R1 or 22.7R2 allows a remote unauthenticated attacker…
 randomrobbiebf/cve-2024-50485
Exam Matrix <= 1.5 - Unauthenticated Privilege Escalation