

CVE-2018-15473-py3
 dirty-racoon/cve-2018-15473-py3
Python3 exploit for CVE-2018-15473 that enumerates valid usernames on OpenSSH servers via timing-based authentication analysis.
authenticationexploitationpenetration-testing+1
dirty-racoon/cve-2018-15473-py3Python3 exploit for CVE-2018-15473 that enumerates valid usernames on OpenSSH servers via timing-based authentication analysis.
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 lukaszstu/smartasset-ue-cve-2020-26526
It is possible to enumerate valid usernames on the login page.
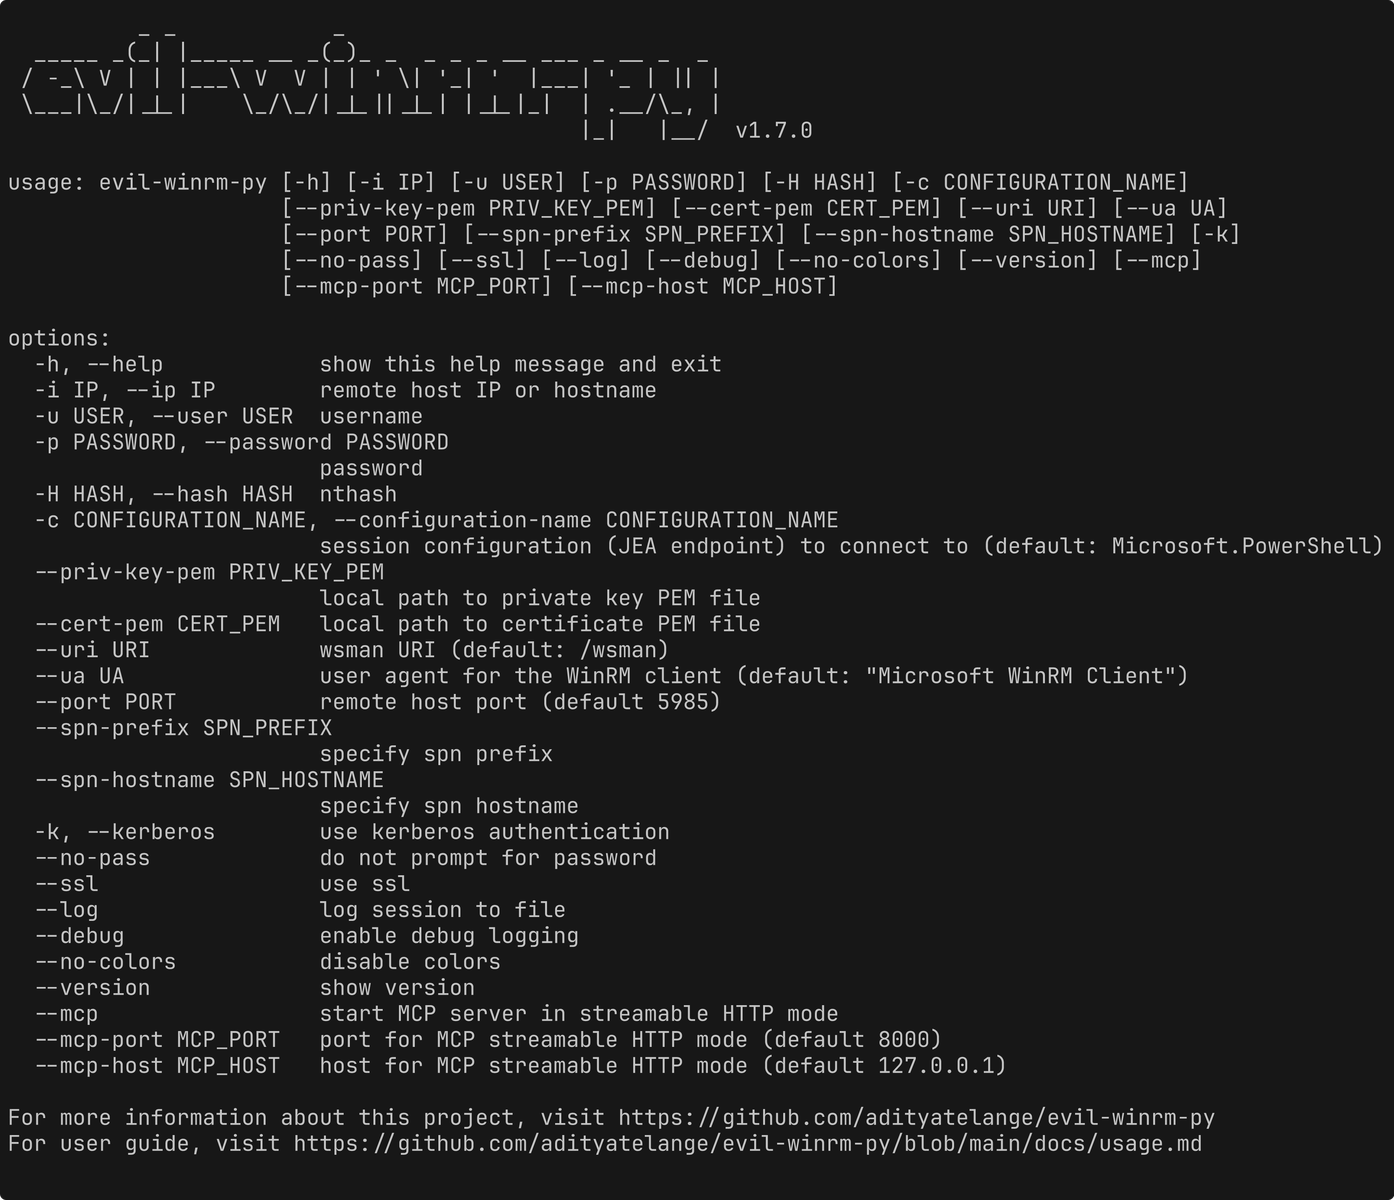 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
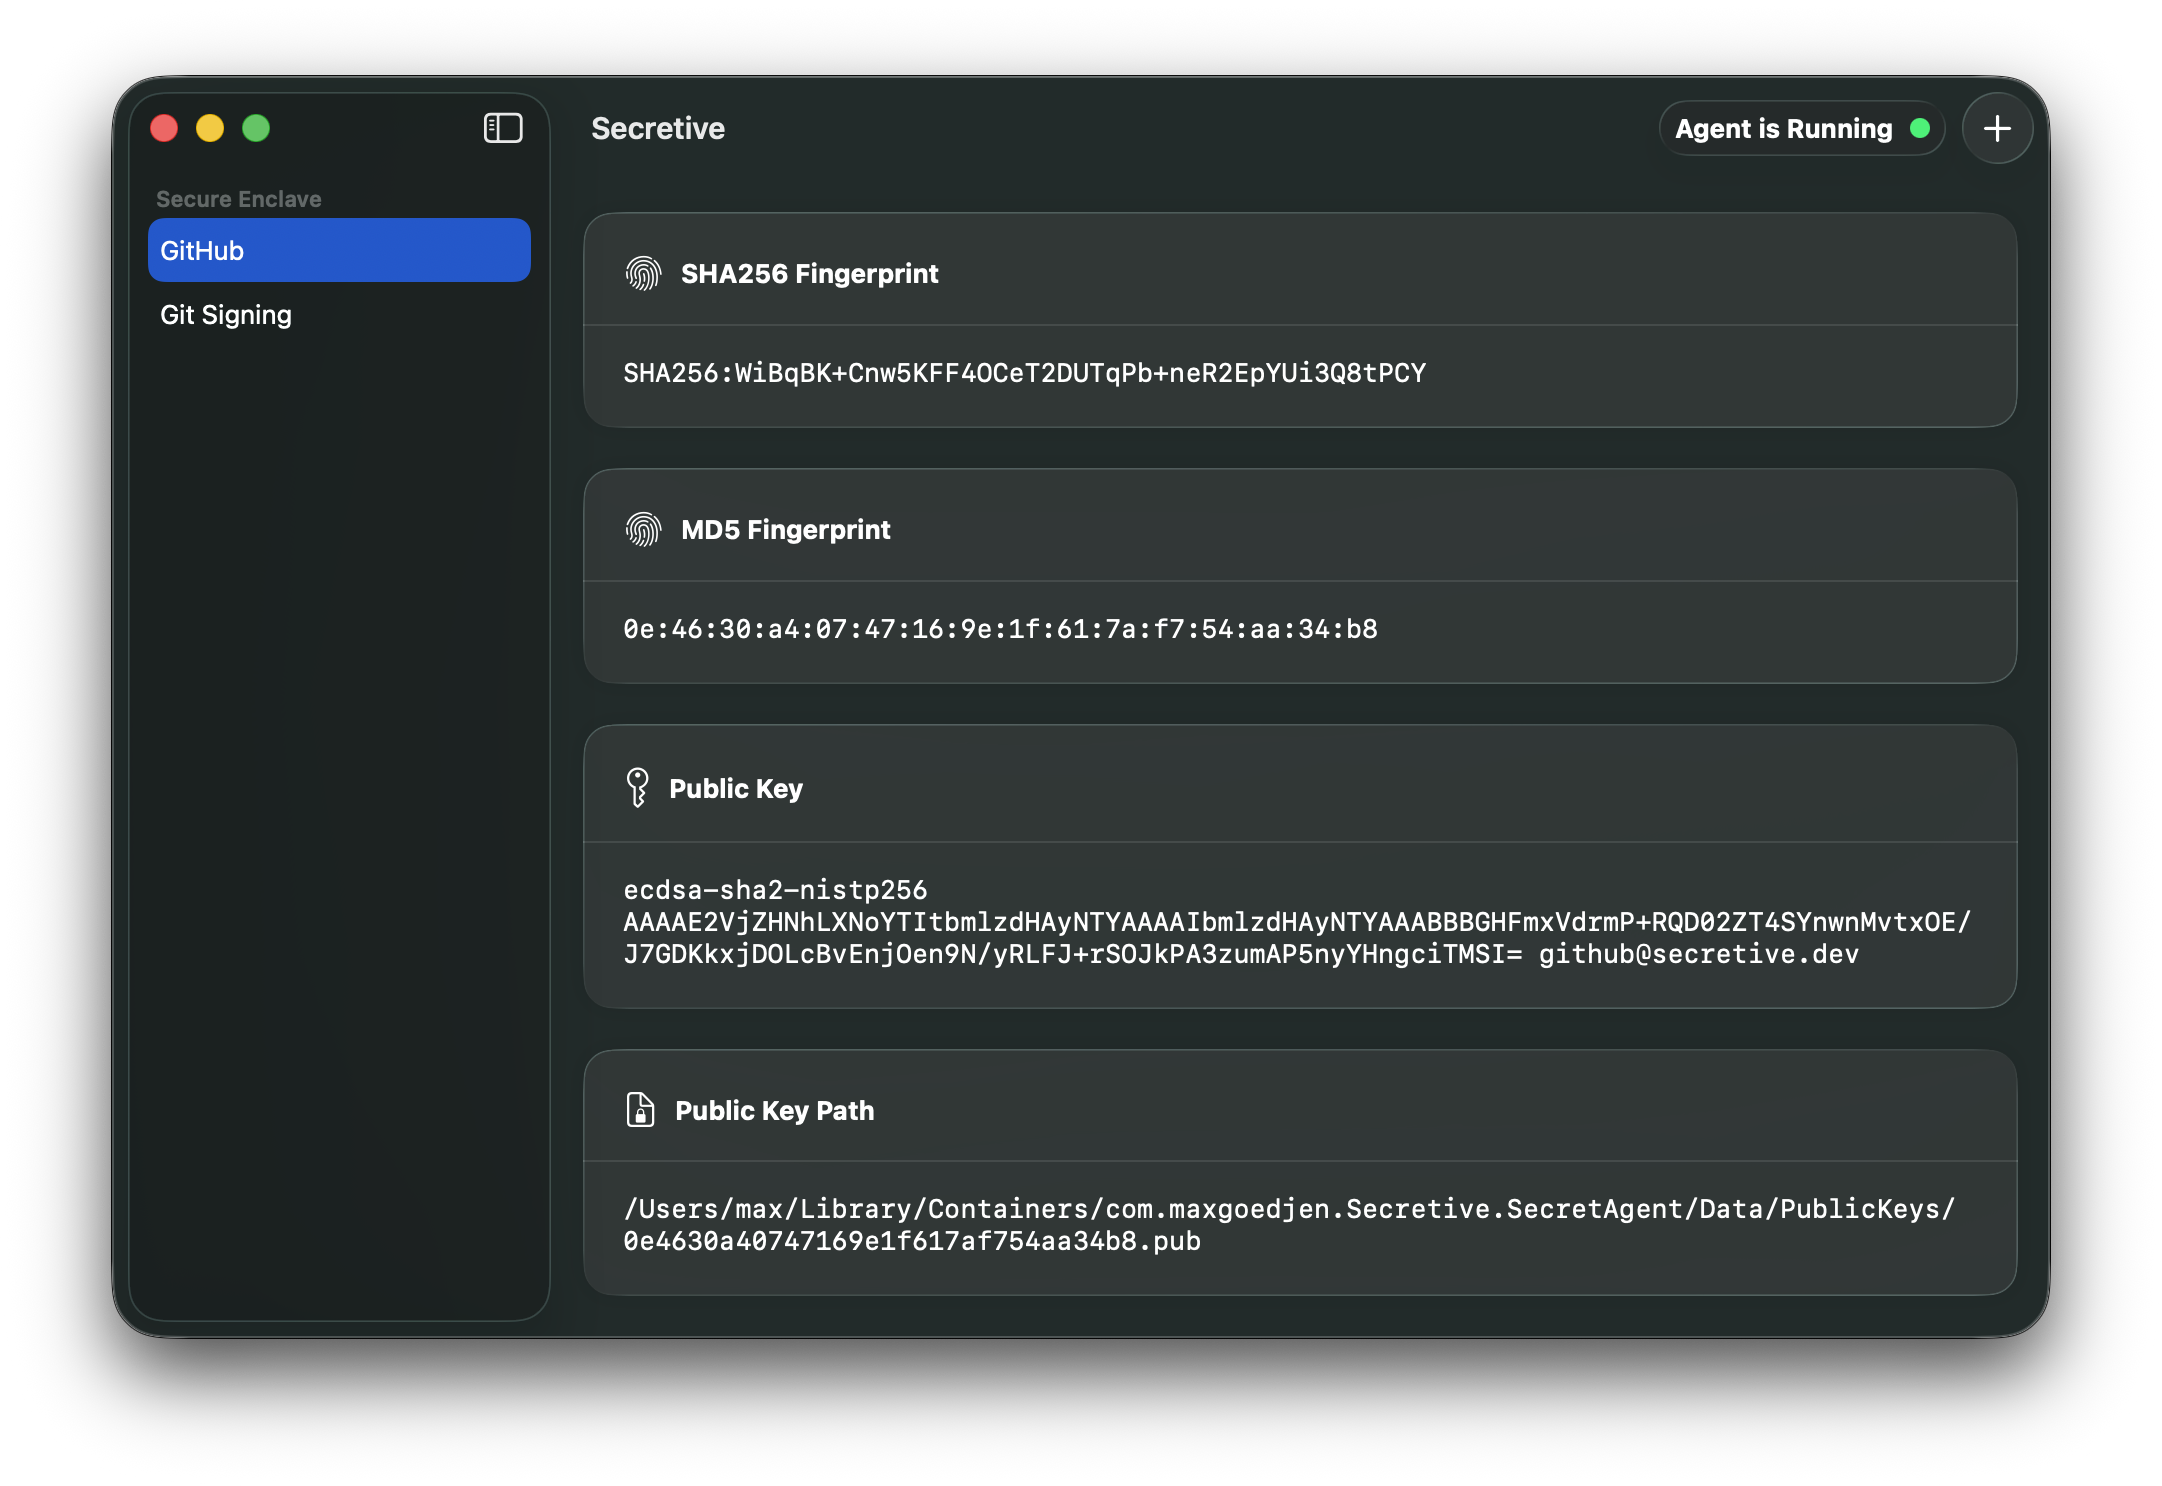 maxgoedjen/secretive
Protect your SSH keys with your Mac's Secure Enclave
 ghostpack/rubeus
Trying to tame the three-headed dog.
 skelsec/pypykatz
Mimikatz implementation in pure Python
 mrash/fwknop
Single Packet Authorization > Port Knocking
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
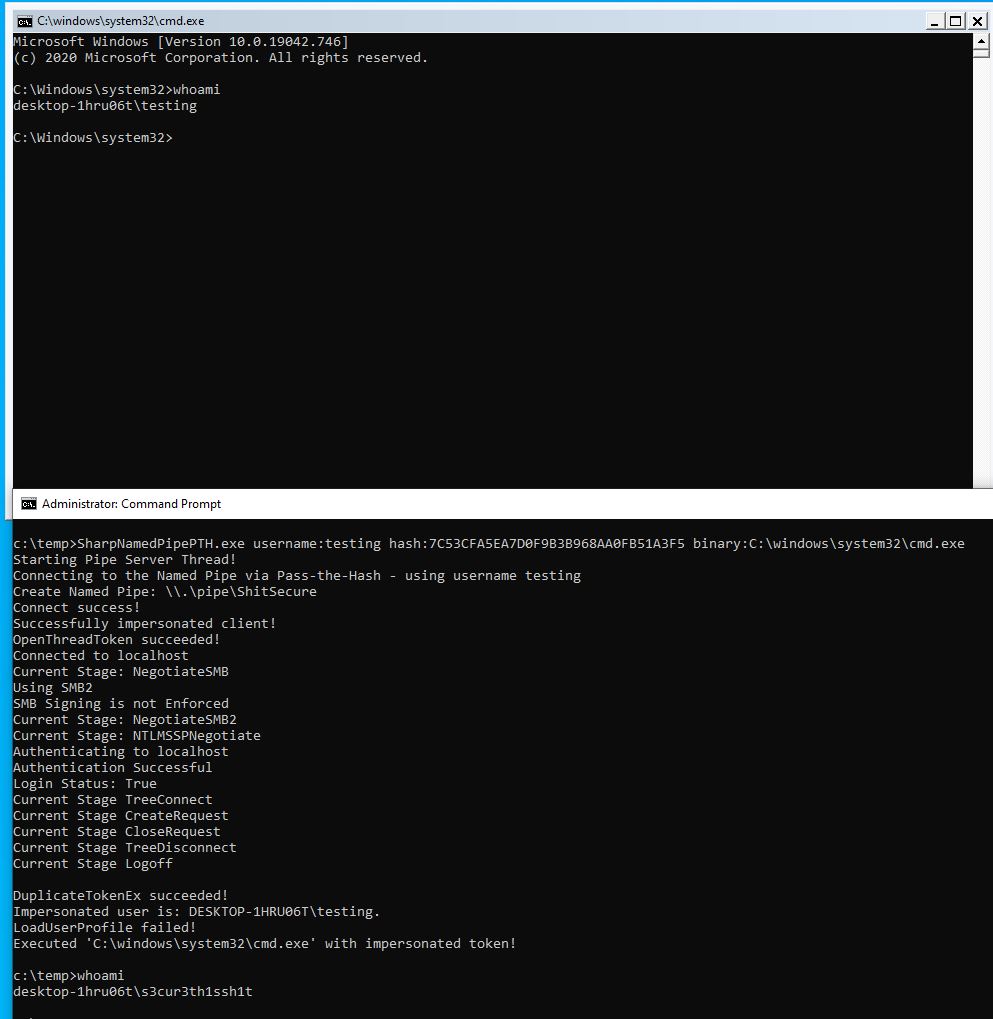 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 sinsinology/cve-2024-4358
Progress Telerik Report Server pre-authenticated RCE chain (CVE-2024-4358/CVE-2024-1800)
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 0katz/cve-2019-12476
PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…
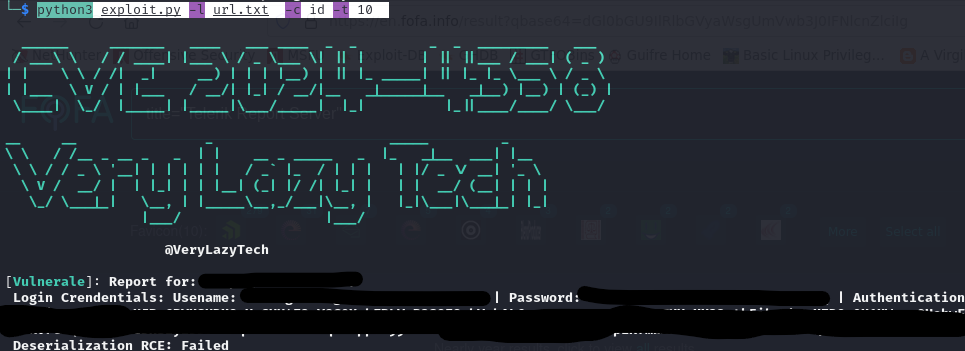 verylazytech/cve-2024-4358
Authentication Bypass Vulnerability — CVE-2024–4358 — Telerik Report Server 2024
 horizon3ai/cve-2024-28987
Proof-of-concept exploit for CVE-2024-28987 targeting SolarWinds Web Help Desk hardcoded credential vulnerability. Automates exploitation via URL…
 leonjza/inetutils-telnetd-auth-bypass
A small docker lab to play with cve-2026-24061, the inetutils-telnetd authentication bypass.
 keerthivasan-sankar/secure-vault-for-commercial
secure vault for your files