
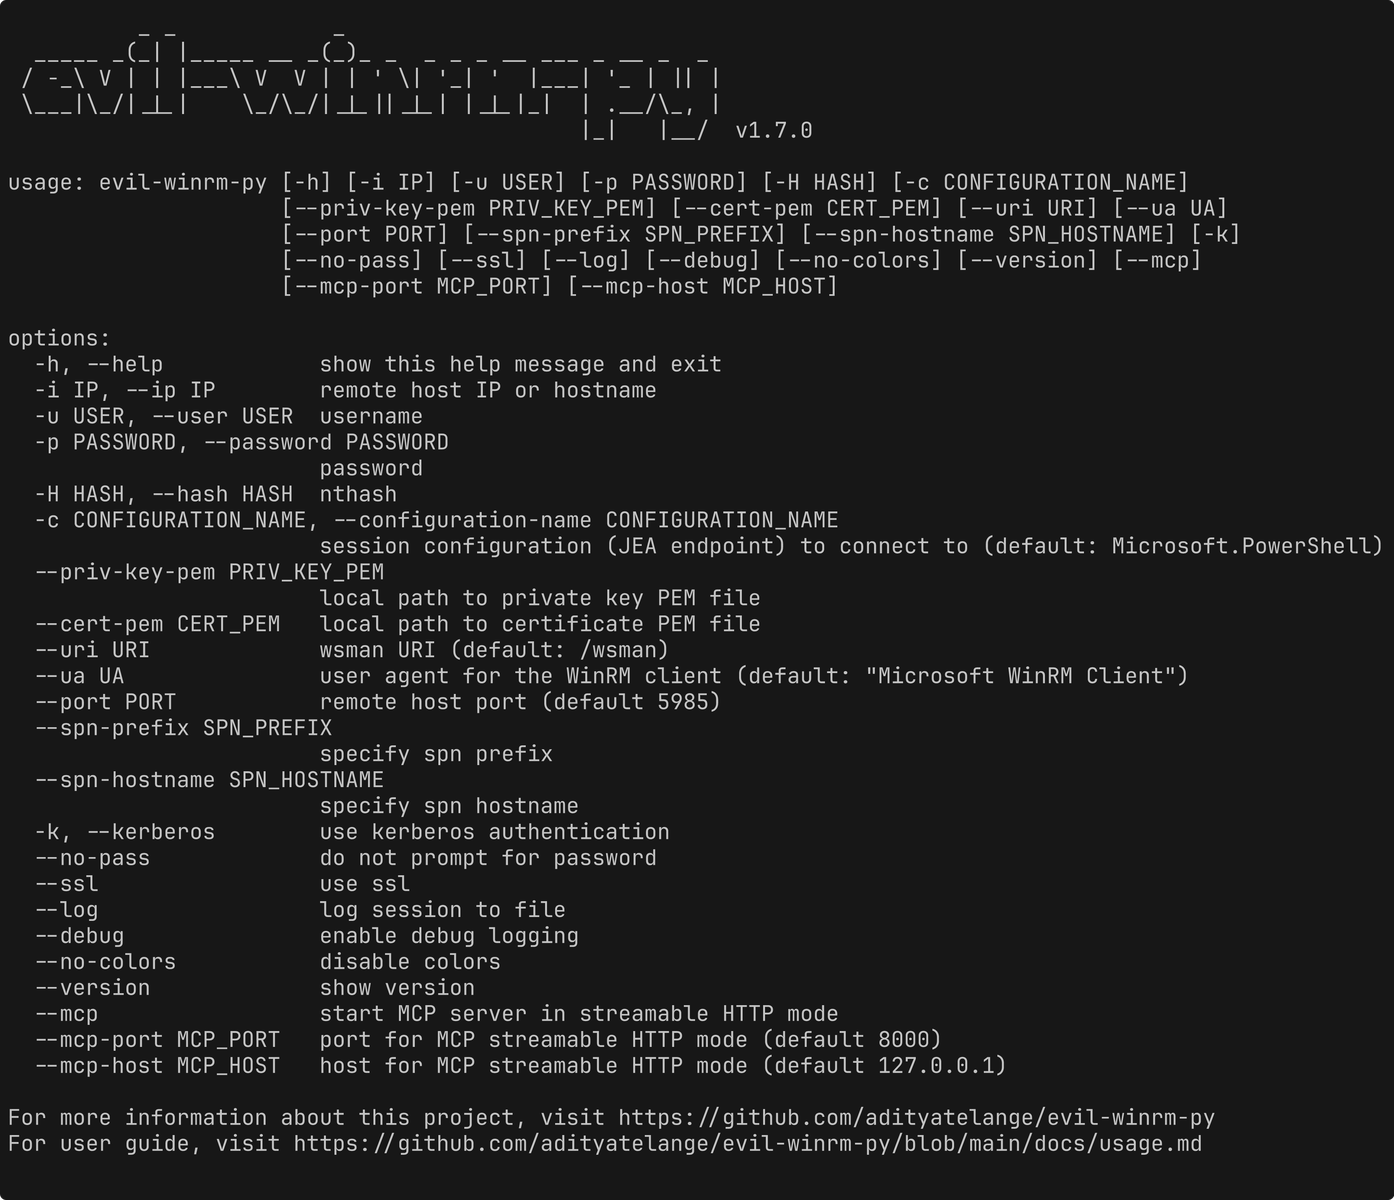
evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
400
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
 naheeju/poc-cve-2026-0073
Security research PoC for CVE-2026-0073: ADB authentication bypass verification
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 mihat2/resetnightmare-impacket
CVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
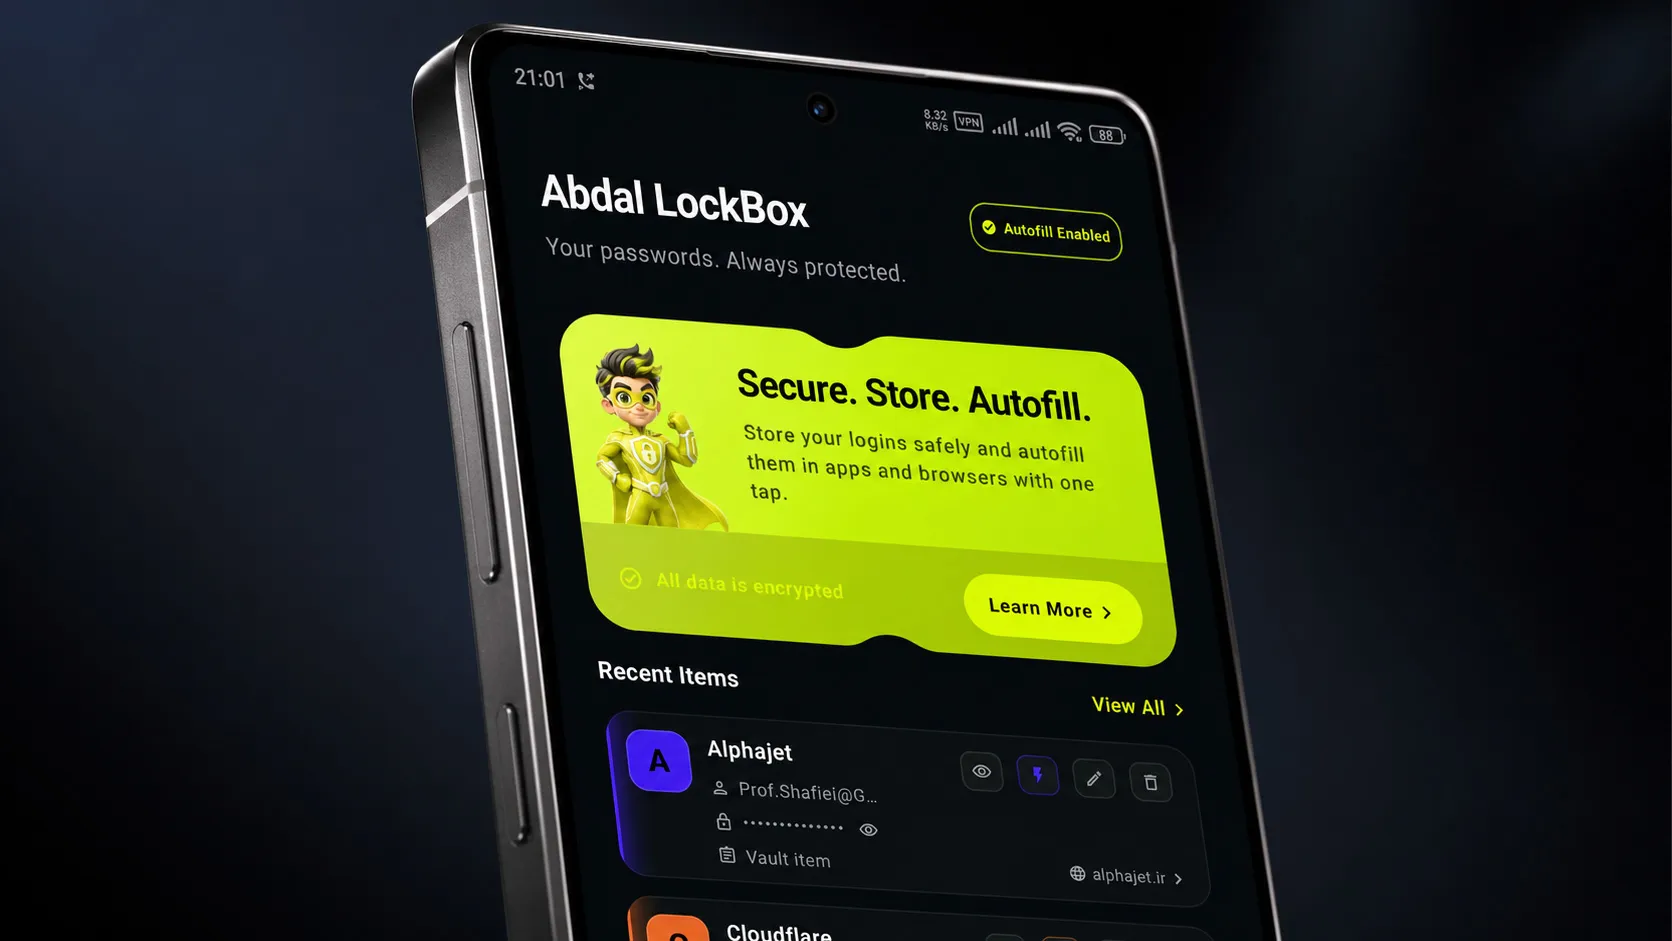
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…

 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
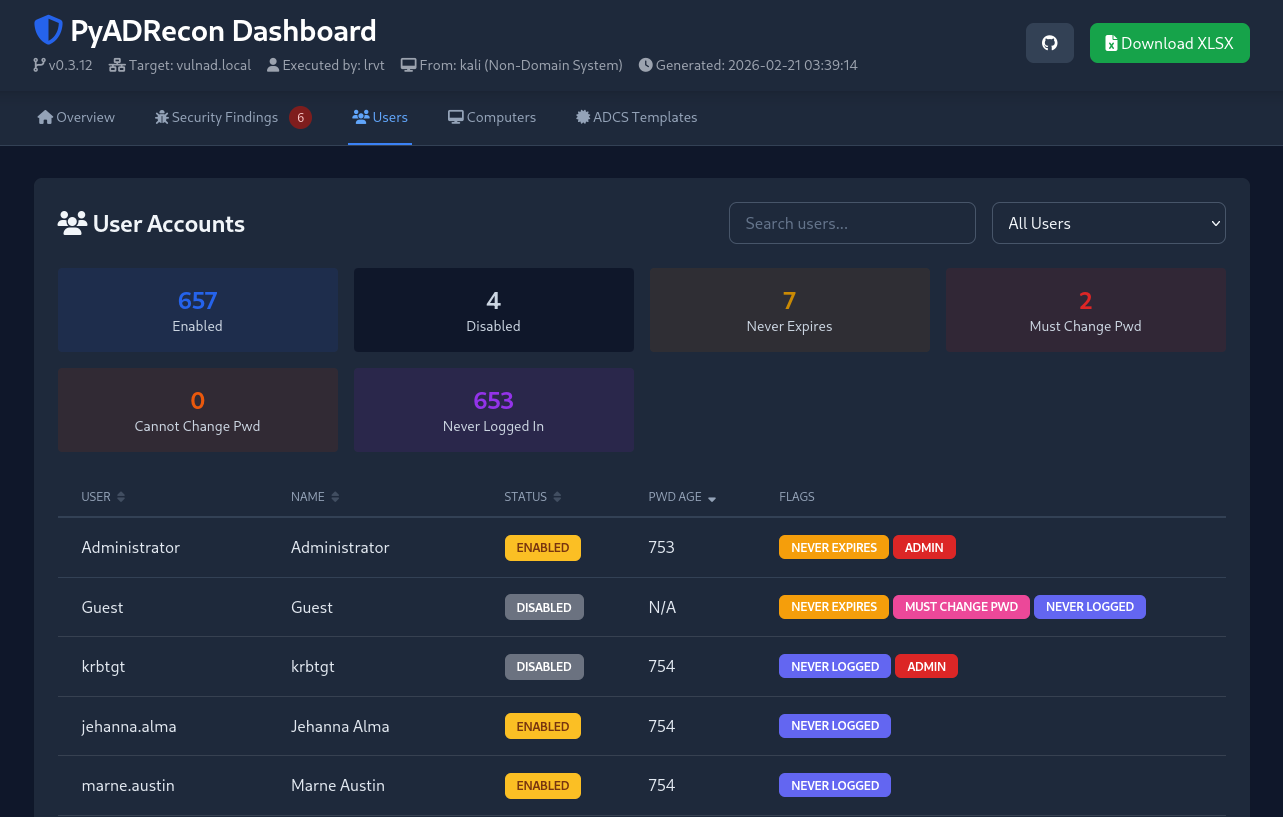 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 jenderal92/cve-2026-8181
CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.
