

intra-handshake-fail
 muhammad-usama-sardar/intra-handshake-fail
Early Attestation Considered Very Harmful (CVE-2026-92701, CVE-2026-92702, CVE-2026-33697, and more to come)
authenticationcryptographyeducation+3
3
muhammad-usama-sardar/intra-handshake-failEarly Attestation Considered Very Harmful (CVE-2026-92701, CVE-2026-92702, CVE-2026-33697, and more to come)
 supermagnum/galdralag-firmware
A cryptographic framework for Baochip-1x .
 bunnie/dc34-vault
Vault app for DC34 badge
 evilsocket/legba
The fastest and more comprehensive multiprotocol credentials bruteforcer / password sprayer and enumerator. 🥷
 rustcrypto/rsa
Pure Rust library for RSA public-key cryptography: key generation, PKCS#1 v1.5 and OAEP encryption/decryption, PSS signatures, plus key import/export.
 dokter69/cve-2025-2563
Multi-threaded exploit for CVE-2025-2563 targeting unauthenticated privilege escalation in the WordPress User Registration & Membership plugin.…
 randeepajayasekara/cve-2026-20127
Walkthrough of the CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN from first malformed peering request to root on the management plane.
 shoucheng3/apache__jspwiki_cve-2019-10078_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…
 shoucheng3/apache__jspwiki_cve-2019-0225_2-11-0-m2
Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…
 sagsooz/cve-2025-29927
🔐 Python-based smart scanner for CVE-2025-29927 — Next.js middleware authentication bypass vulnerability. Detects meta refresh, keyword-based…
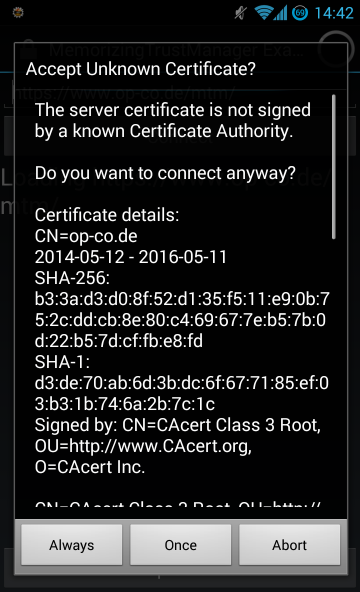 ge0rg/memorizingtrustmanager
A "plugin" for Android Java to allow asking the user about SSL certificates
 ludovicpatho/cve-2022-26923_ad-certificate-services
The vulnerability allowed a low-privileged user to escalate privileges to domain administrator in a default Active Directory environment with the…
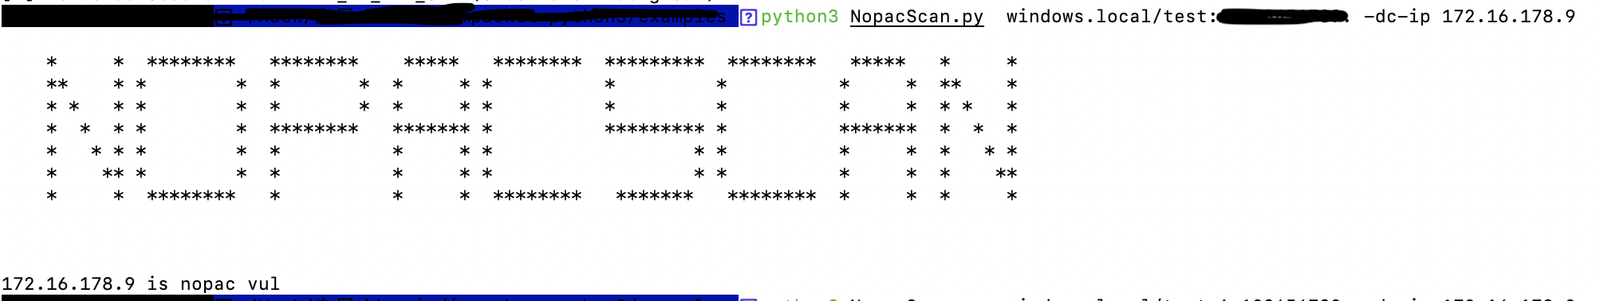 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 pingport80/cve-2019-17240
This is the exploit of CVE-2019-17240.
 jmalinen/hostap
Clone of w1.fi hostap.git - NOTE: This is not the main development location and pull requests for this repository are ignored. See the upstream…