
swift-nio-ssh
 apple/swift-nio-ssh
SwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO
authenticationencryption-decryption-toolsnetwork-security+2
520
apple/swift-nio-sshSwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 pervinzahidli/cve-2026-103977
Session-scoped TOTP rate limiting permits repeated verification attempts
 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 vxssroott/cve-2026-78905-facebook-account-takeover
Social Media Infrastructure Vulnerability Research. CVE-2026-78905: OAuth token reuse and session hijacking in Facebook's Graph API.
 nel-droid/cve-2026-71206-poc
PoC: Shiori JWT CheckToken never re-validates account state (CVE-2026-71206, High 8.2)
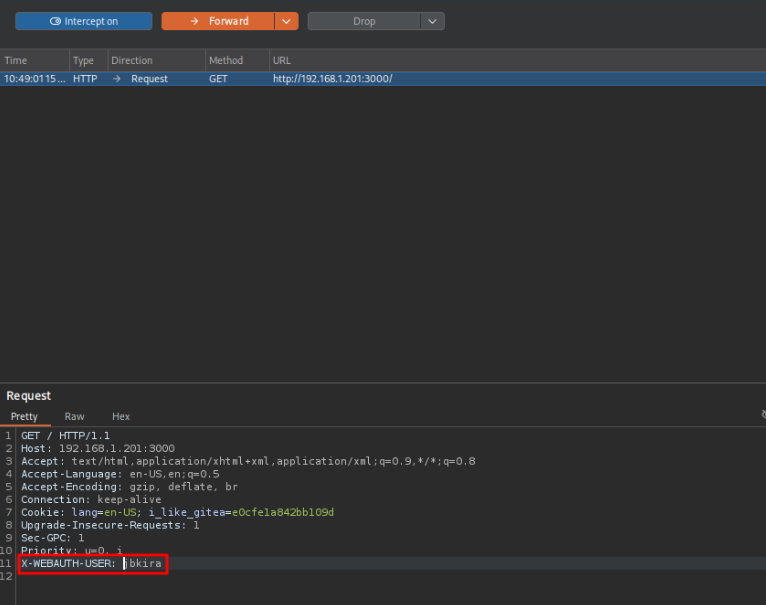 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
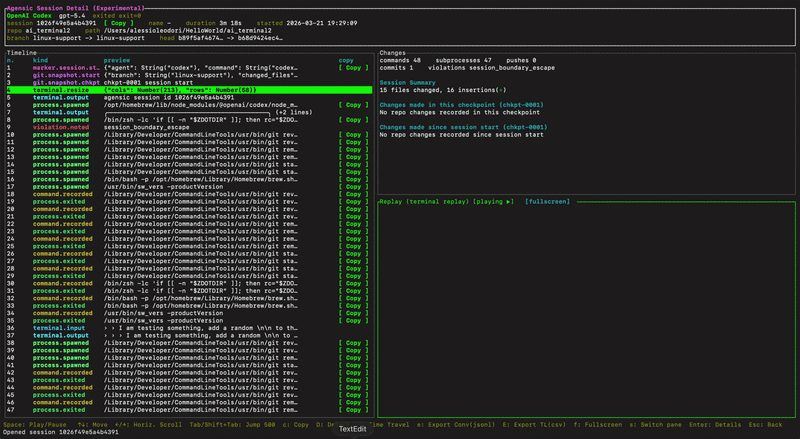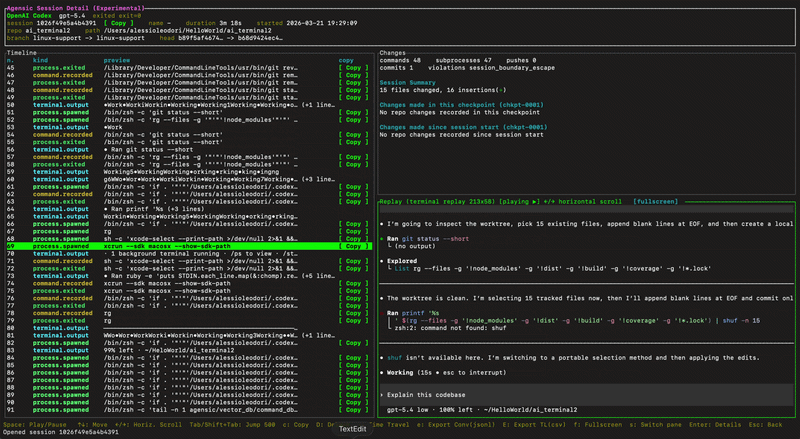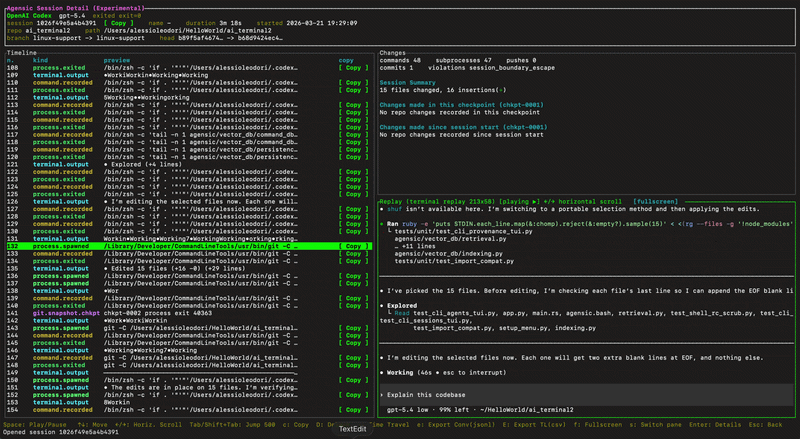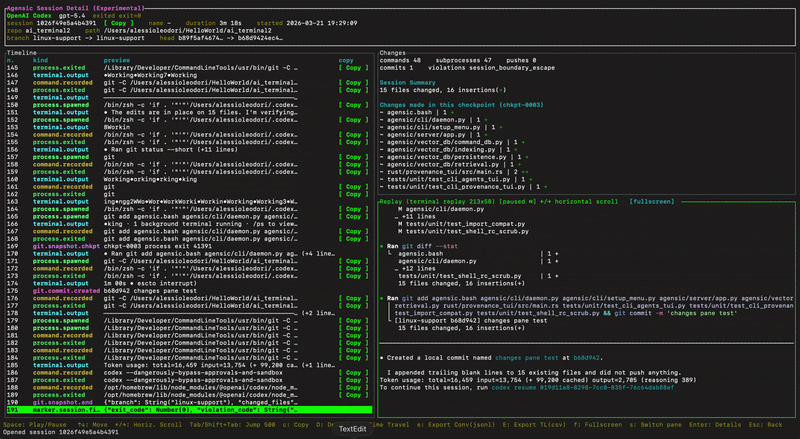 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
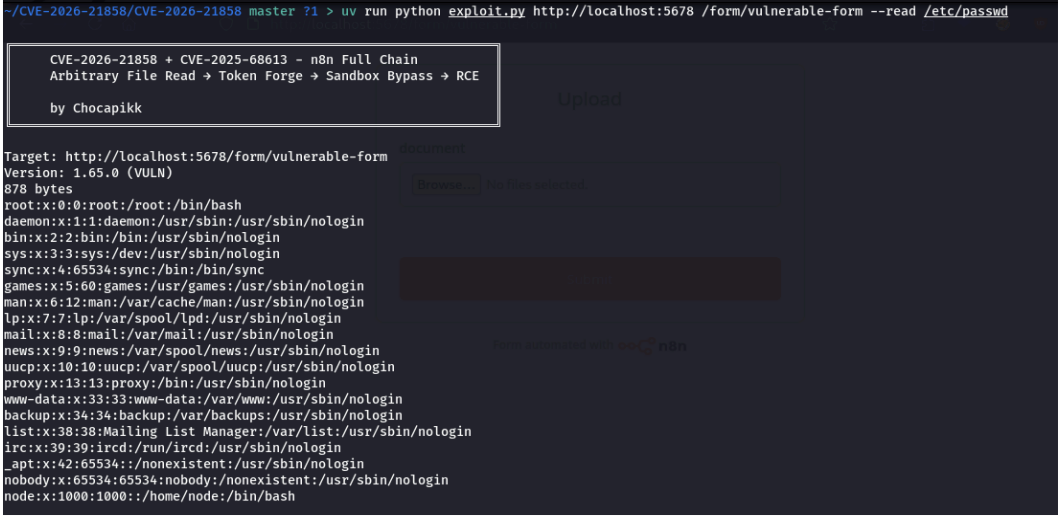 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping