
nextcloud-federated-ocm-token
 abraxas/nextcloud-federated-ocm-token
Nextcloud 35.0.0 — federated share secret is an unscoped app password for the sharer's whole Files tree
authenticationexploitationinformation-gathering+5
abraxas/nextcloud-federated-ocm-tokenNextcloud 35.0.0 — federated share secret is an unscoped app password for the sharer's whole Files tree
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
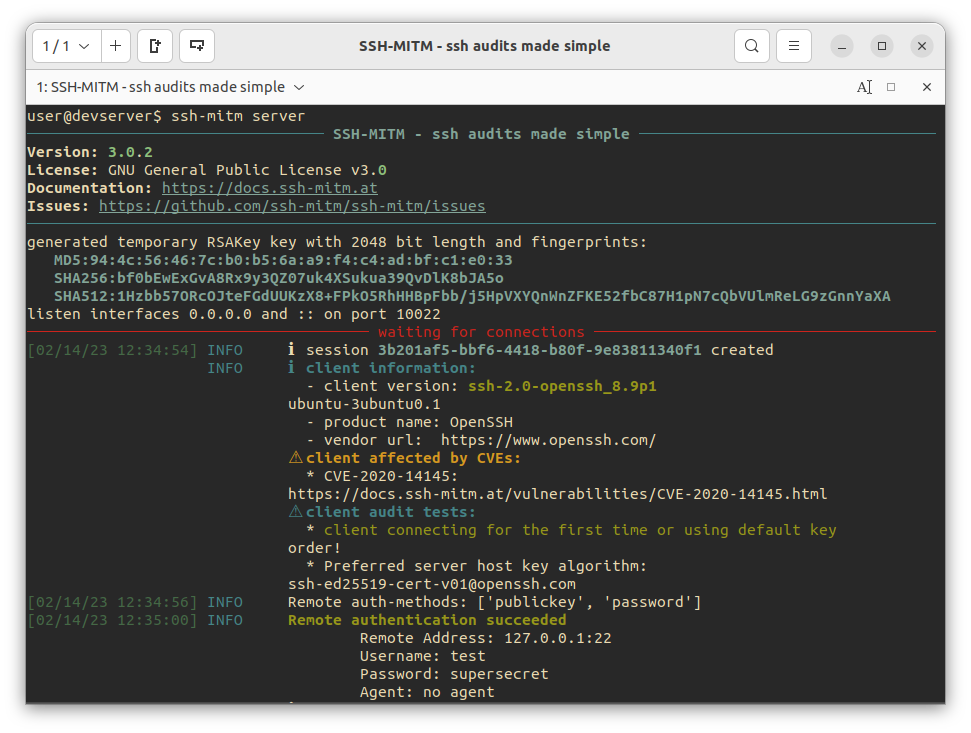 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
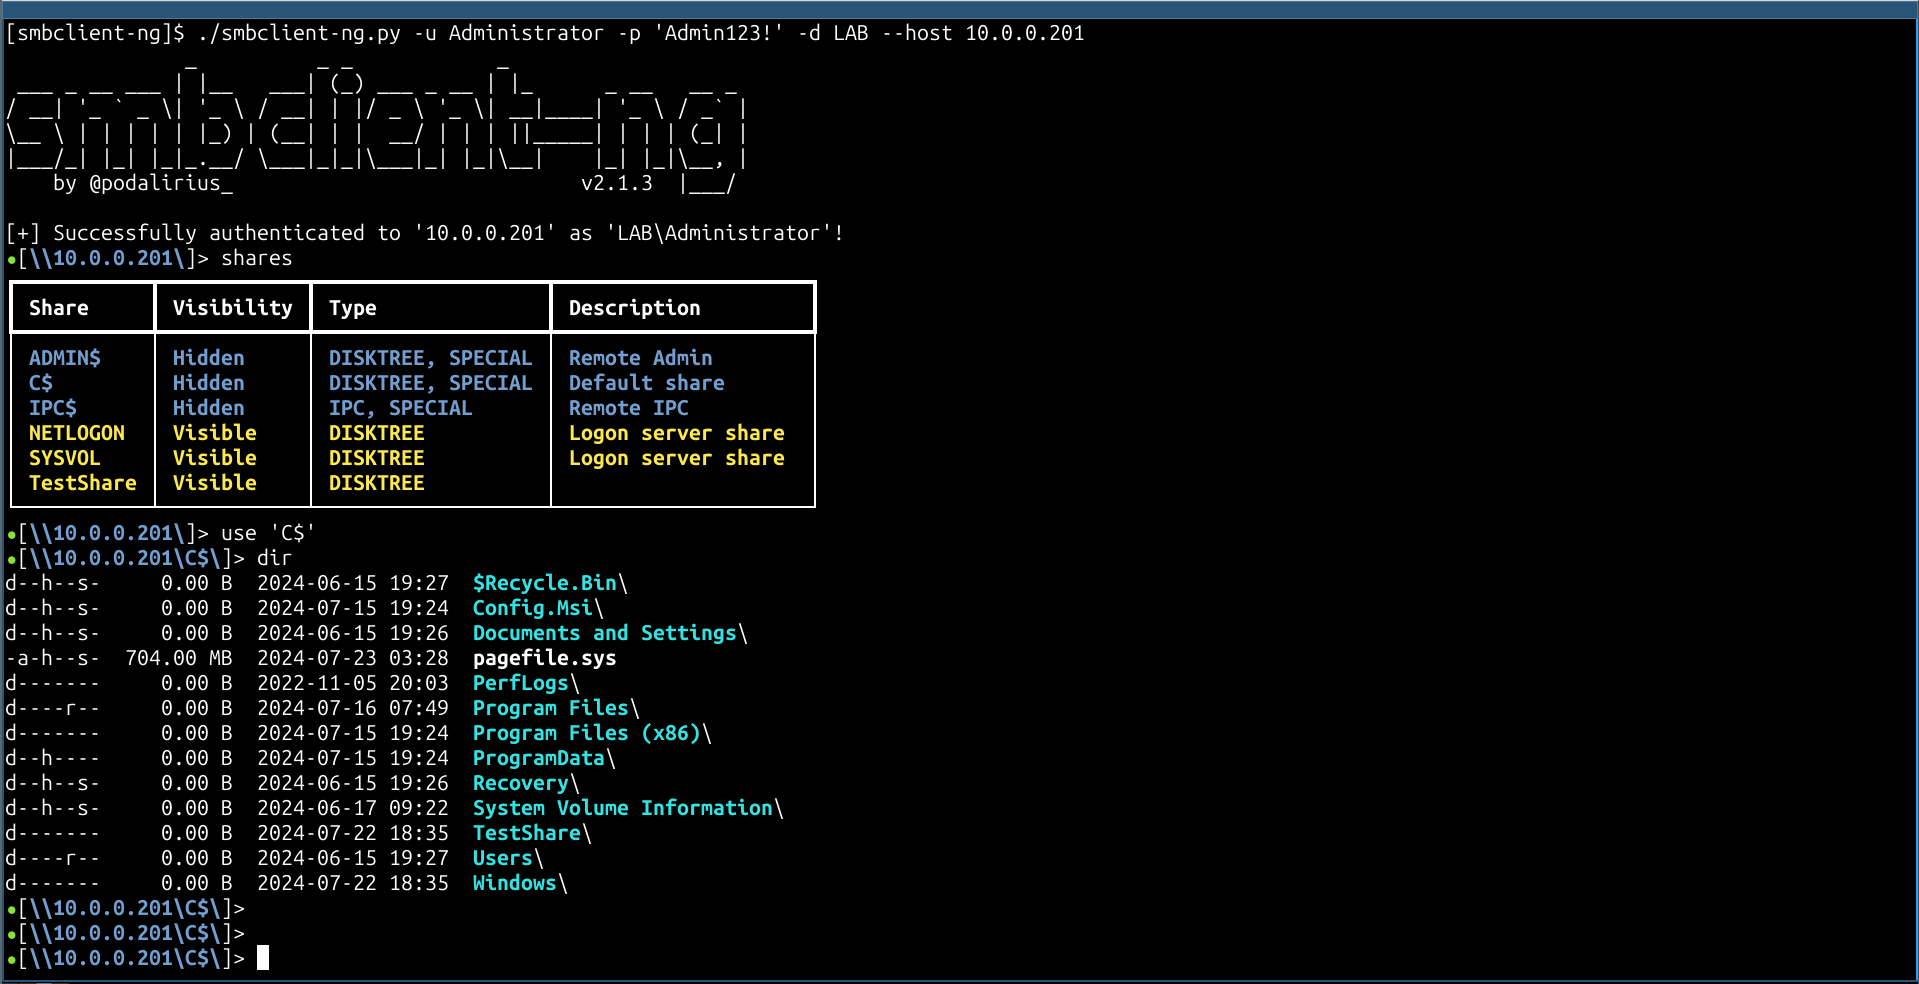 p0dalirius/smbclient-ng
smbclient-ng, a fast and user friendly way to interact with SMB shares.
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 trustedsec/titanis
Windows protocol library, including SMB and RPC implementations, among others.
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…