
freeradius-server
High-performance multi-protocol AAA server for RADIUS, DHCPv4/v6, DNS, TACACS+, and VMPS, centralizing network authentication, authorization, and…

High-performance multi-protocol AAA server for RADIUS, DHCPv4/v6, DNS, TACACS+, and VMPS, centralizing network authentication, authorization, and…

The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.

The official Asterisk Project repository.

Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…

A simple super fast django reusable app that blocks people from brute forcing login attempts

General purpose TLS and crypto library

Asynchronous RDP client for Python (headless)

Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability

A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.

PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.

Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…

Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…

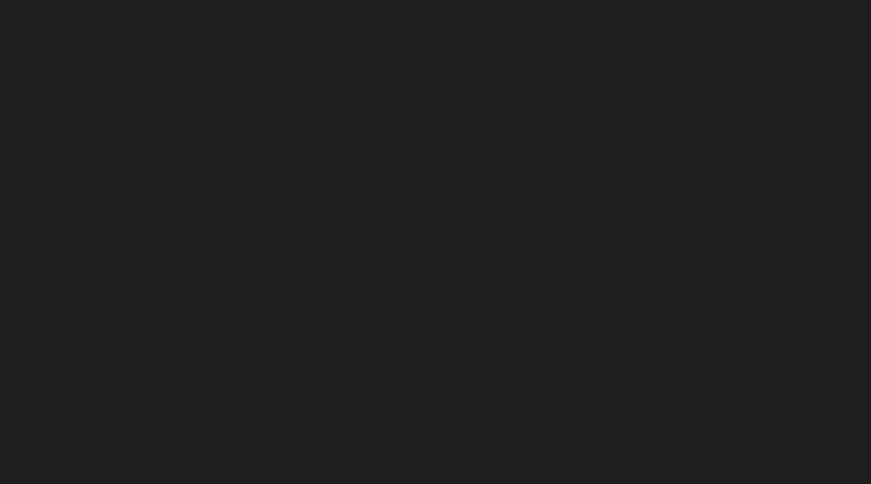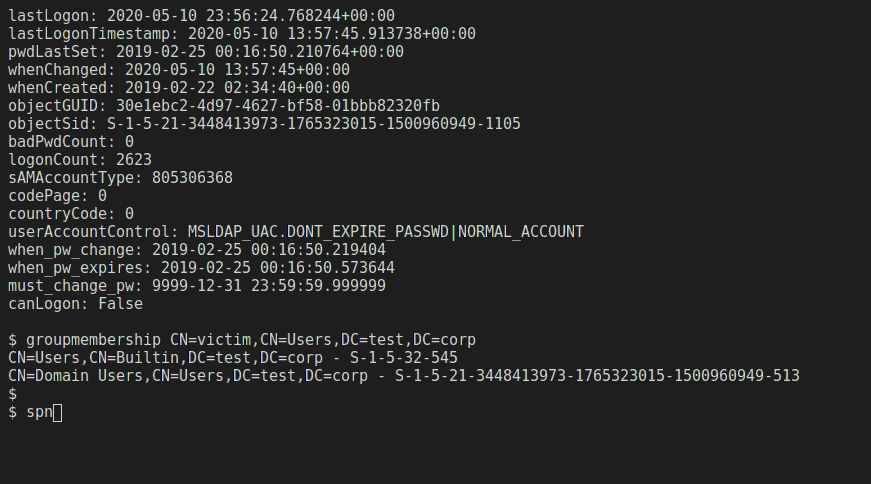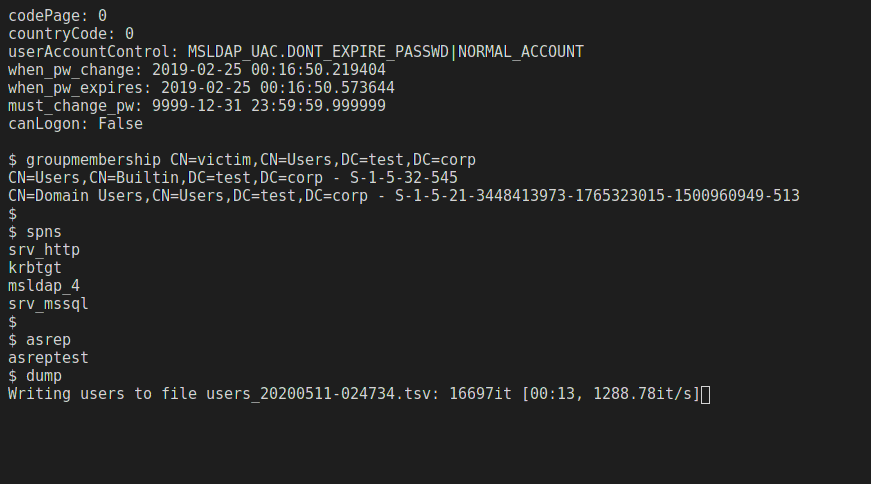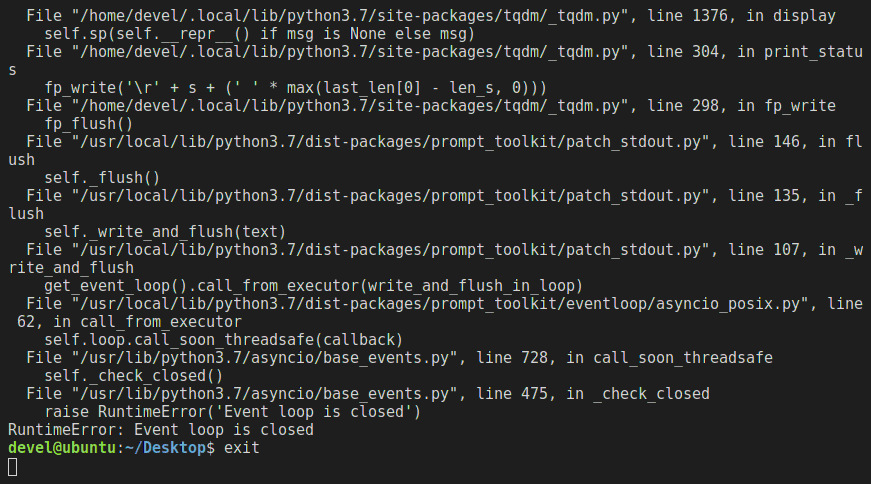
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…

Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…

Python library for auditing Microsoft Active Directory via LDAP, supporting NTLM, Kerberos, SSPI authentication, channel binding, encryption, and…

The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning

Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.

CVE-2026-34348 - Draft or TODO