
adPEAS
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
authenticationexploitationinformation-gathering+6
61106960/adpeasPowershell tool to automate Active Directory enumeration.
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
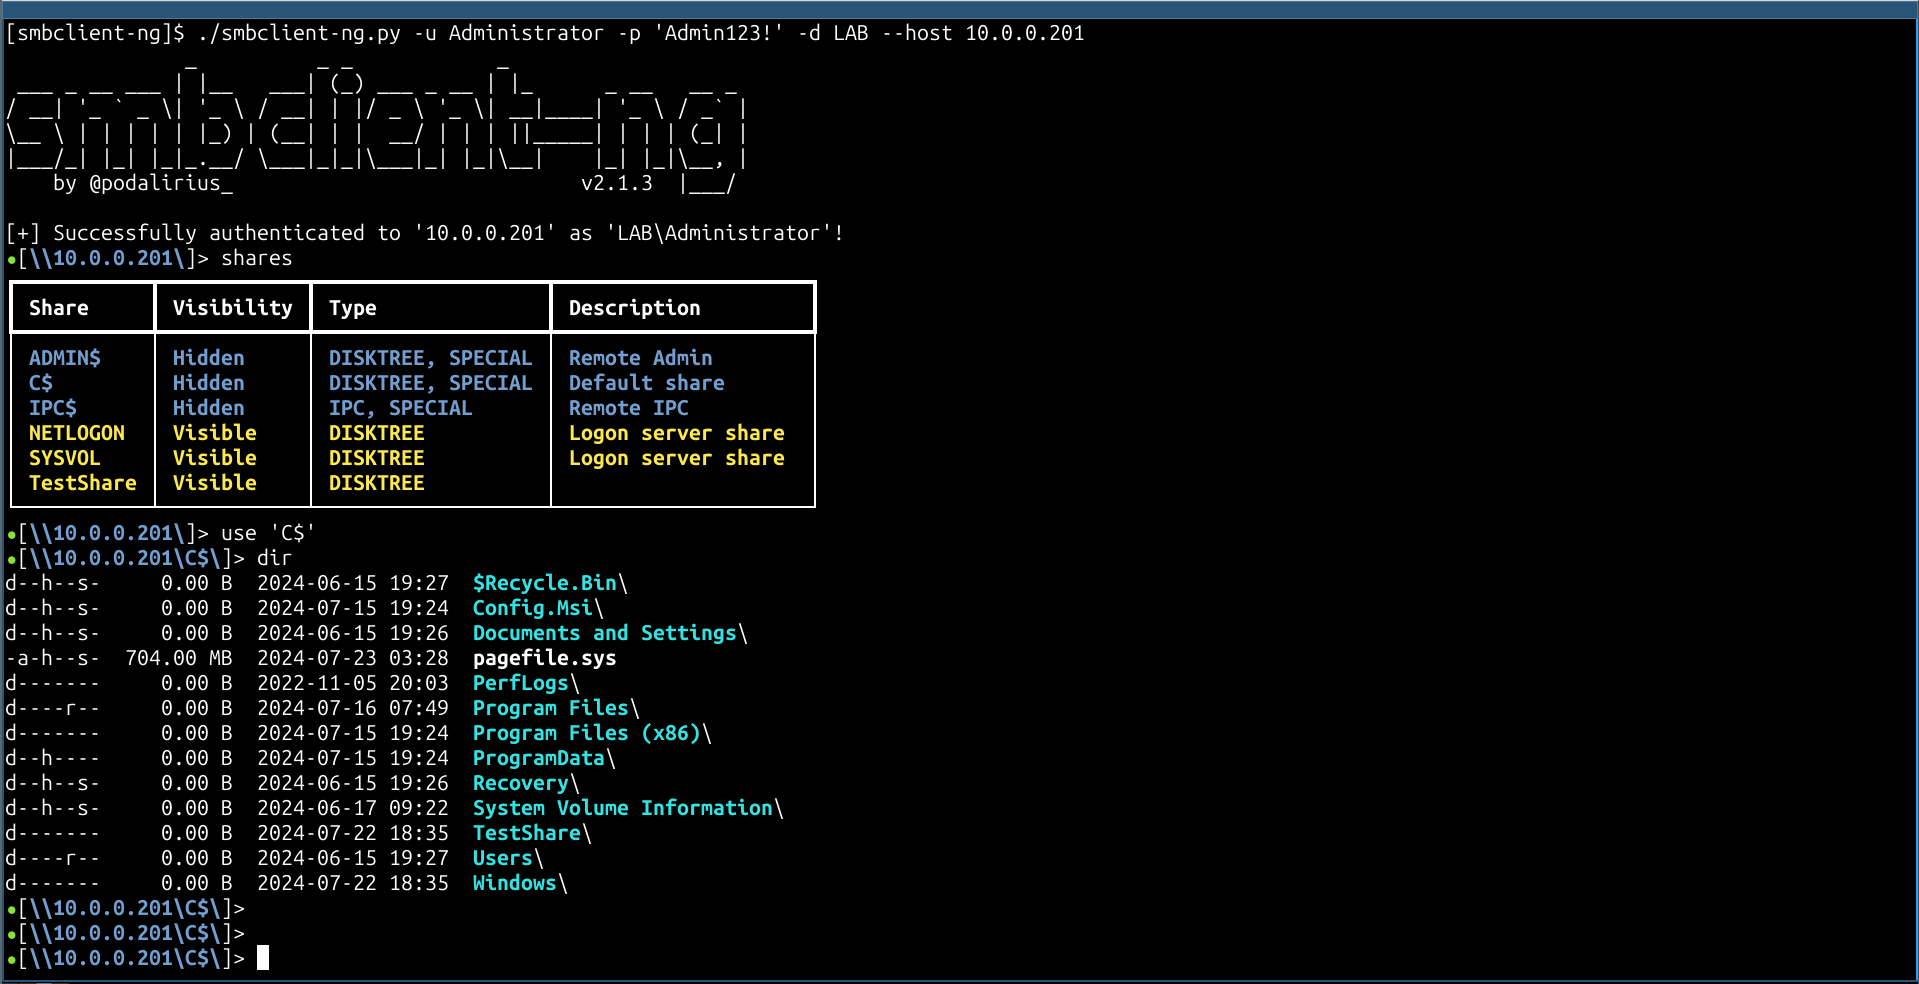 p0dalirius/smbclient-ng
smbclient-ng, a fast and user friendly way to interact with SMB shares.
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
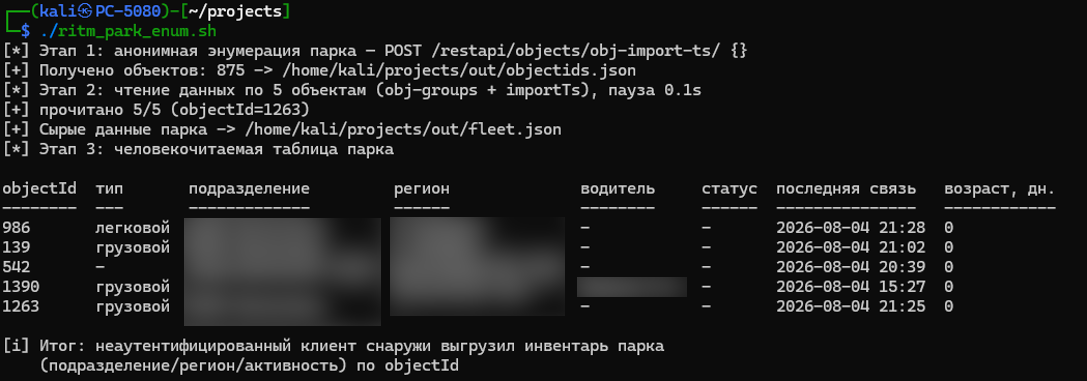 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 murrez/cve-2026-100835
Python PoC for CVE-2026-100835: audits Contrast manifests for AllowedChipIDs/AllowedPIIDs, detects versions, and probes Coordinator endpoints to…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…