

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.7k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 kimdir01/cve-2026-9090-poc
PoC for CVE-2026-9090 — Casdoor SAML signature bypass (CWE-347). Reproduction-only; coordinated via CERT/CC VU#780781.
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…
 0xgh057r3c0n/cve-2026-9198
IBM Langflow Unauthenticated RCE via Auto-Login Bypass
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 1beelze/cve-2026-5118
Automated exploit and mass scanner for CVE-2026-5118, an unauthenticated privilege escalation in WordPress Divi Form Builder <=5.1.2, enabling admin…
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 biitts/cve-2026-49230-apisix-jwe-decrypt-auth-bypass
PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 jfriedli/cve-2025-11986
Proof-of-concept exploit for CVE-2025-11986 demonstrating unauthenticated access bypass in WordPress crypto_connect plugin via nonce extraction and…
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 imjdl/cve-2026-31816-rshell
Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.
 dedsecteam-blackhat/cve-2025-68860
Exploit script for CVE-2025-68860 targeting WordPress Mobile Builder plugin. Generates forged JWT tokens using a hardcoded secret to authenticate as…
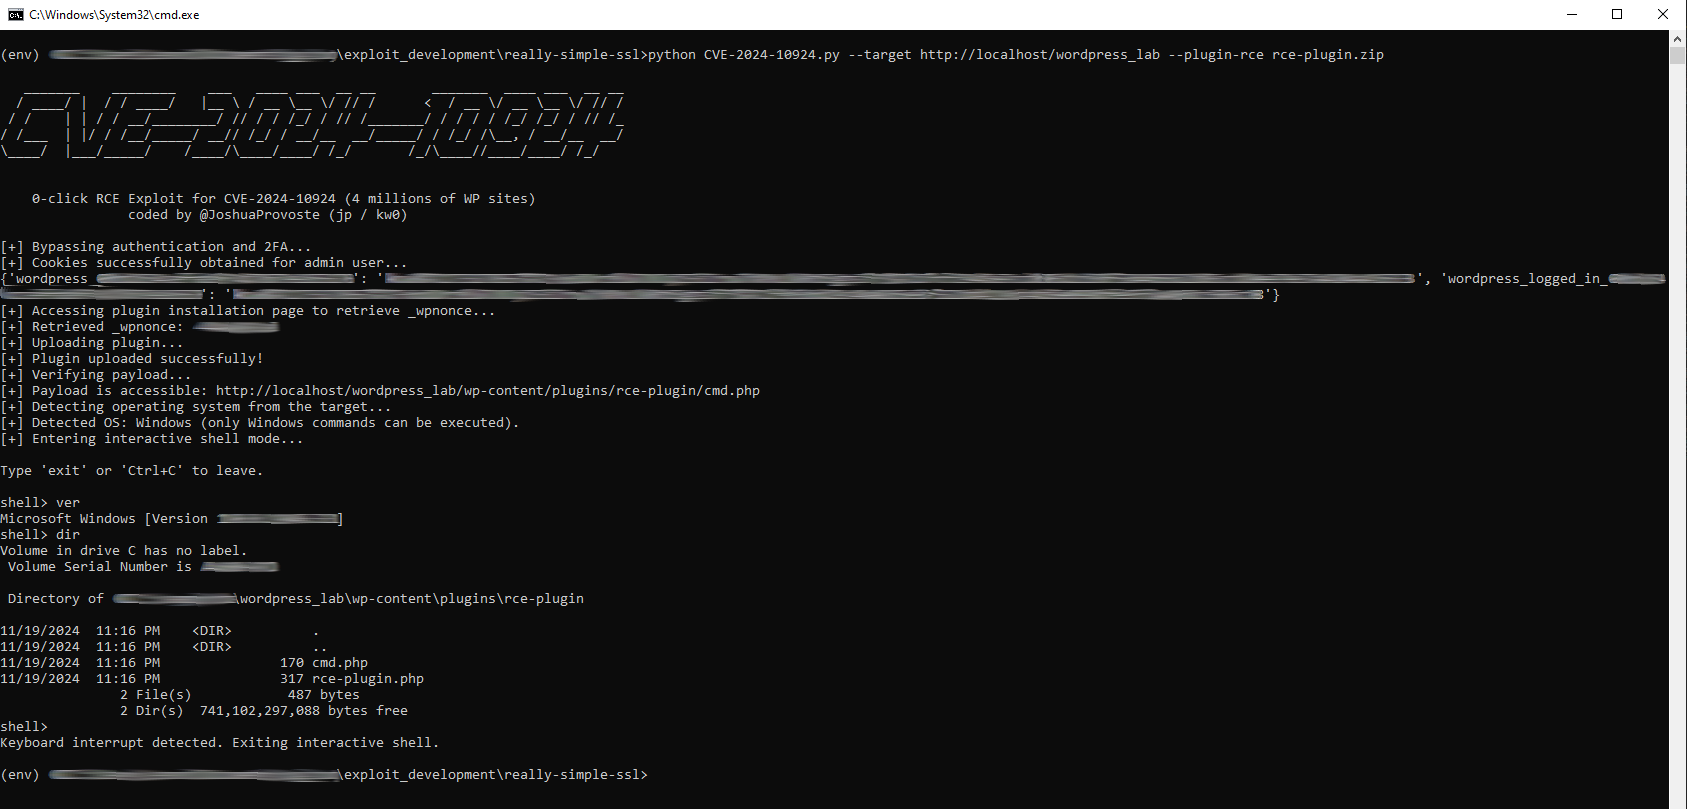 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.