
ad-password-protection
 lithnet/ad-password-protection
Active Directory password filter featuring breached password checking and custom complexity rules
authenticationconfiguration-auditingidentity-access-management+1
577
lithnet/ad-password-protectionActive Directory password filter featuring breached password checking and custom complexity rules
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 openssl/openssl
General purpose TLS and crypto library
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 polosss/by-poloss..-..cve-2026-10580
Hippoo Mobile App for WooCommerce <= 1.9.4 - Unauthenticated Authentication Bypass to Administrator Account Takeover
 sanupl/cve-2021-46067
CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.
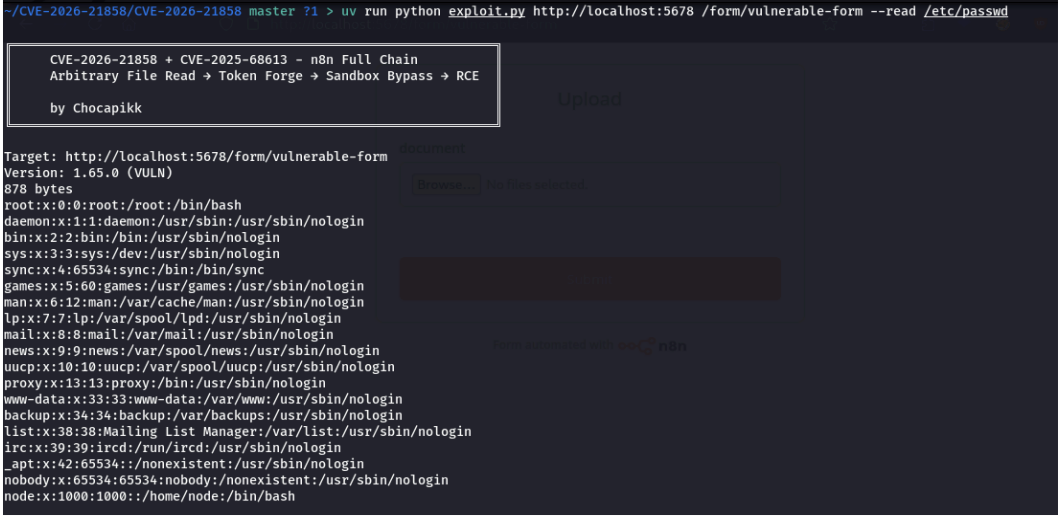 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 cveteam/flowiseai-critical-killchain
Critical unauthenticated kill chain leading to full RCE in FlowiseAI (CVE-2025-58434 + CVE-2025-59528)
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 kaleth4/cve-2026-21858
Automated exploit chain for n8n achieving unauthenticated arbitrary file read, admin token forgery, and sandbox bypass to remote code execution via…
 umair-aziz025/dahua-cve-research
Dahua IP camera CVE research toolkit (CVE-2021-33044/33045, CVE-2025-31700/31701)
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 hd0x01/cve-2026-24061-nse
The script performs a full Telnet negotiation mirroring the exact byte sequence of a real telnet -a client session.
 pl4tyz/cve-2025-14611-centrestack-and-triofox-full-poc-exploit
CVE-2025-14611 CentreStack and Triofox full Poc/Exploit