

spire
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
authenticationauthentication-authorizationcloud-infrastructure-security+5
2.6k
spiffe/spireWorkload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 openssh/openssh-portable
Portable OpenSSH
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 keepassxreboot/keepassxc
Secure offline storage of credentials with encrypted vaults, password generator, TOTP, YubiKey/OnlyKey support, browser integration, and CLI.
 yubico/libfido2
Provides library functionality for FIDO2, including communication with a device over USB or NFC.
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 phinode-labs/nginx-cve-2026-97629
Proof-of-concept exploit, root-cause analysis and one-line patch for CVE-2026-97629, an nginx TLS session-ticket forgery that bypasses…
 wolfssl/wolfguard
FIPS 140-3 compliant VPN kernel module and user tool, drop-in replacement for WireGuard with AES-256-GCM, SHA2-256, and SECP256R1 cryptography for…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 markqvist/reticulum
The cryptography-based networking stack for building unstoppable networks with LoRa, Packet Radio, WiFi and everything in between.
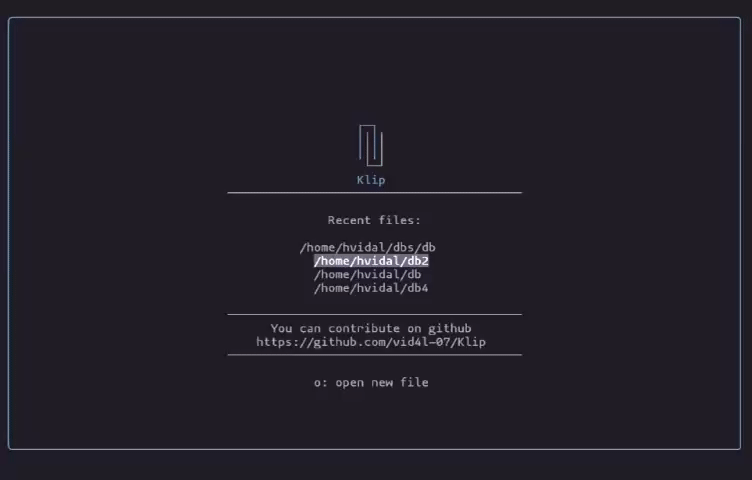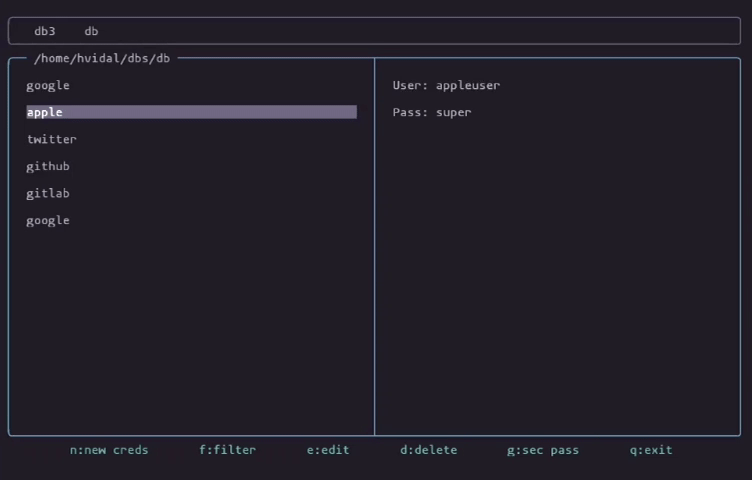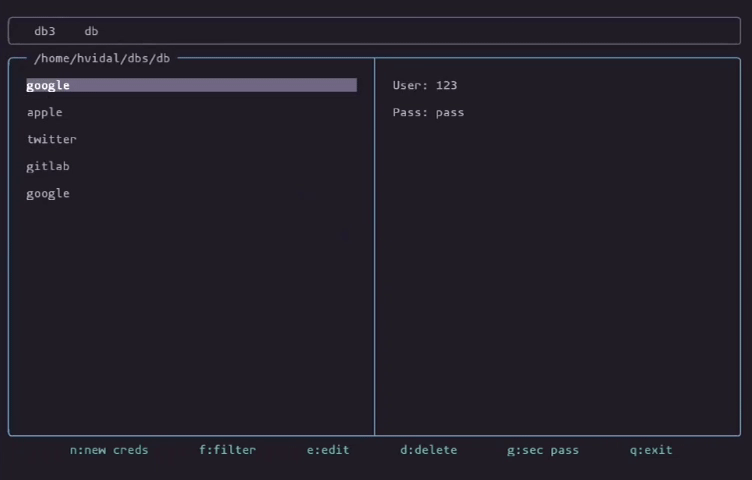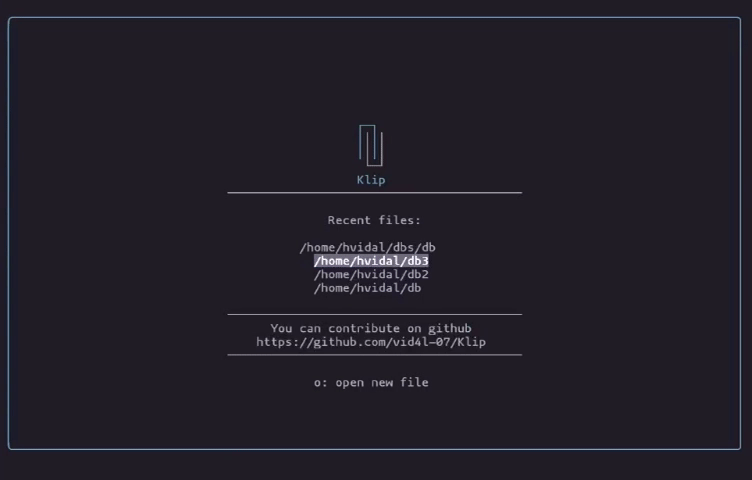 vid4l-07/klip
Minimal terminal-based password manager
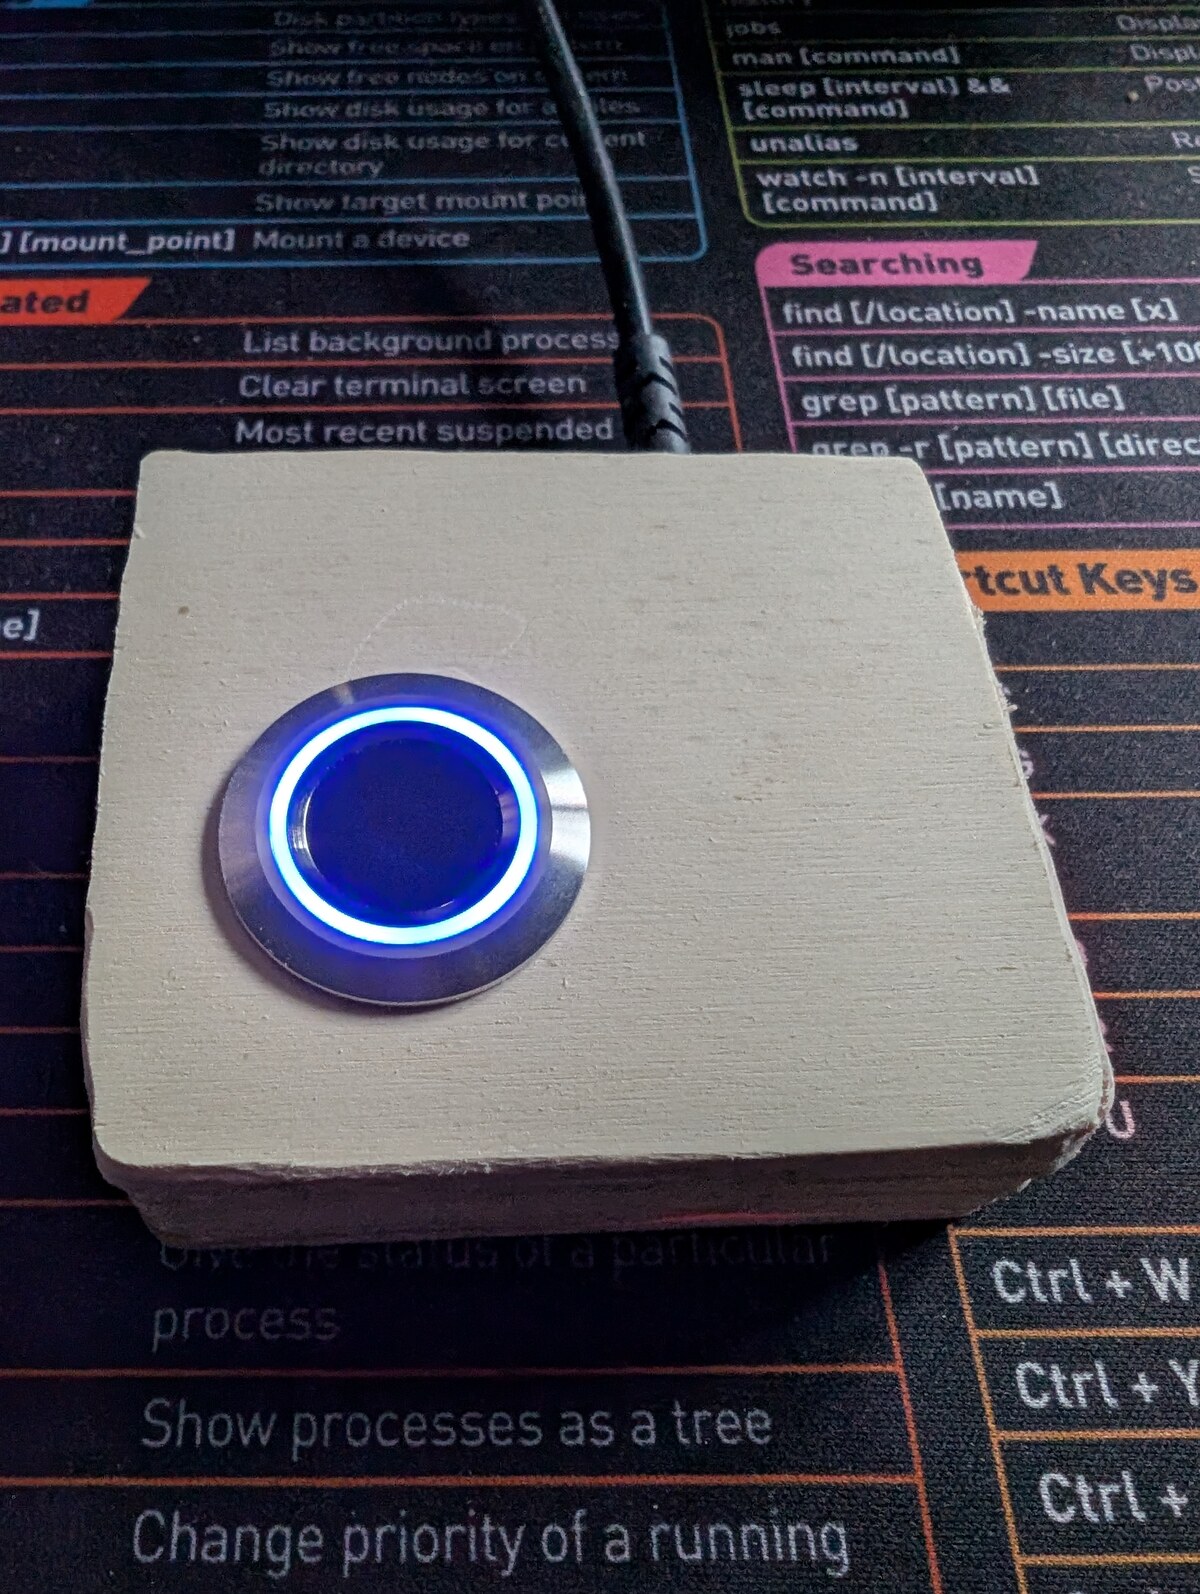 matpb/linux-fingerprint-r503
Linux desktop fingerprint login using a Grow R503 sensor + Arduino + a Rust fprintd-replacement daemon
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…