CVE-2026-82329-PoC-Exploit

Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…

Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…

Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…

CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit

Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…

Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…

CVE Reproduction: cve-2025-24472-fortinet_authbypass_reproduction

Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…

Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…

CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner

Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…

Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.

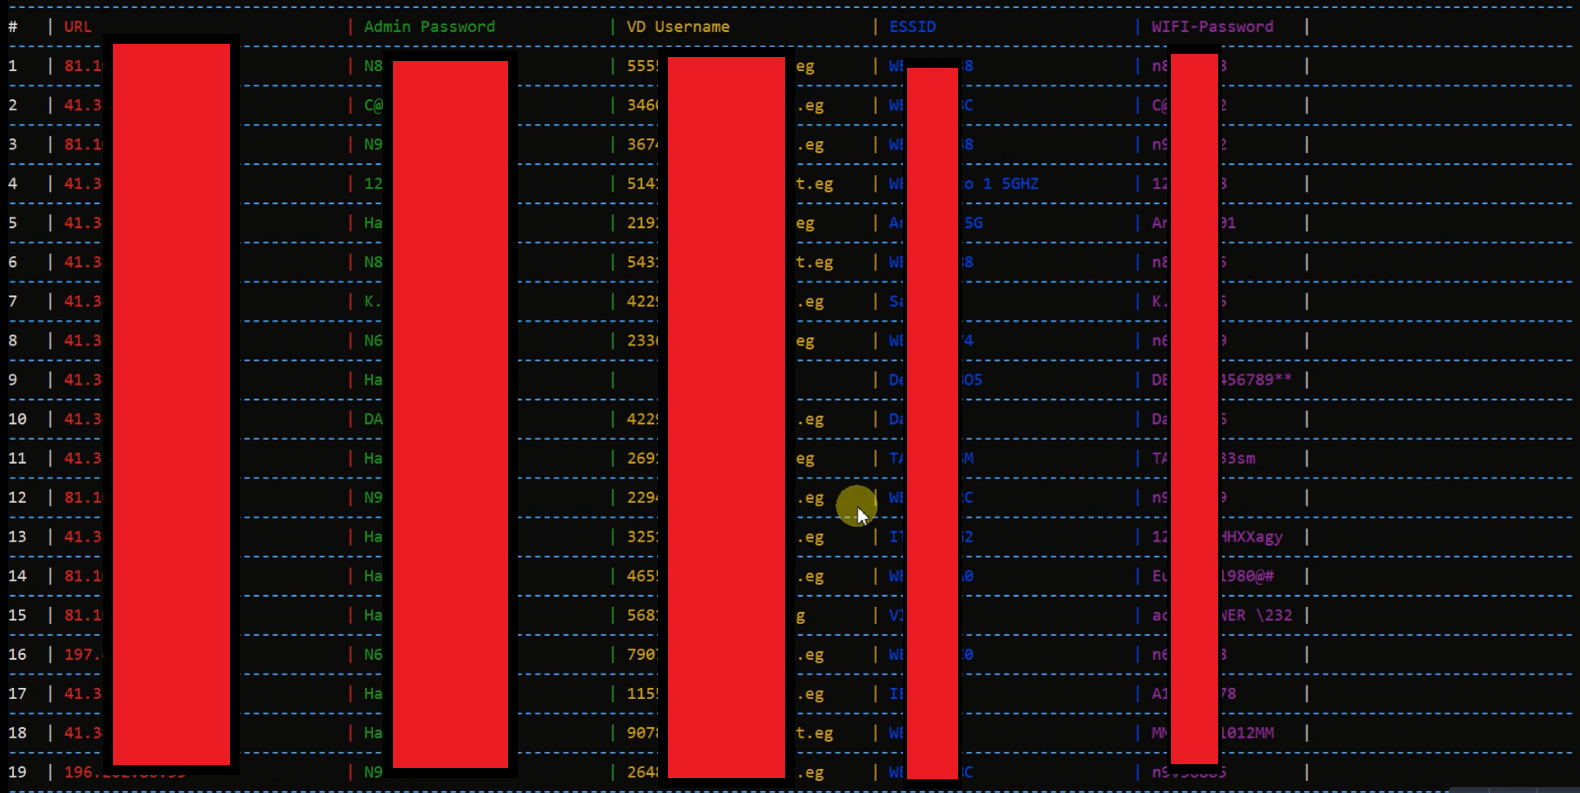
Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…

Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…

Snipe-IT < 8.3.7 Mass Assignment Vulnerability Leading to Privilege Escalation

Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…

CVE-2025-63587

An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…

CVE-2025-40554 Exploitation