

 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability
 covepseng/cve-2026-102268-poc
Exploitability PoC for CVE-2026-102-268 (PyJWT Asymmetric-PEM detection bypass).
 muhammad-usama-sardar/intra-handshake-fail
Early Attestation Considered Very Harmful (CVE-2026-92701, CVE-2026-92702, CVE-2026-33697, and more to come)
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.

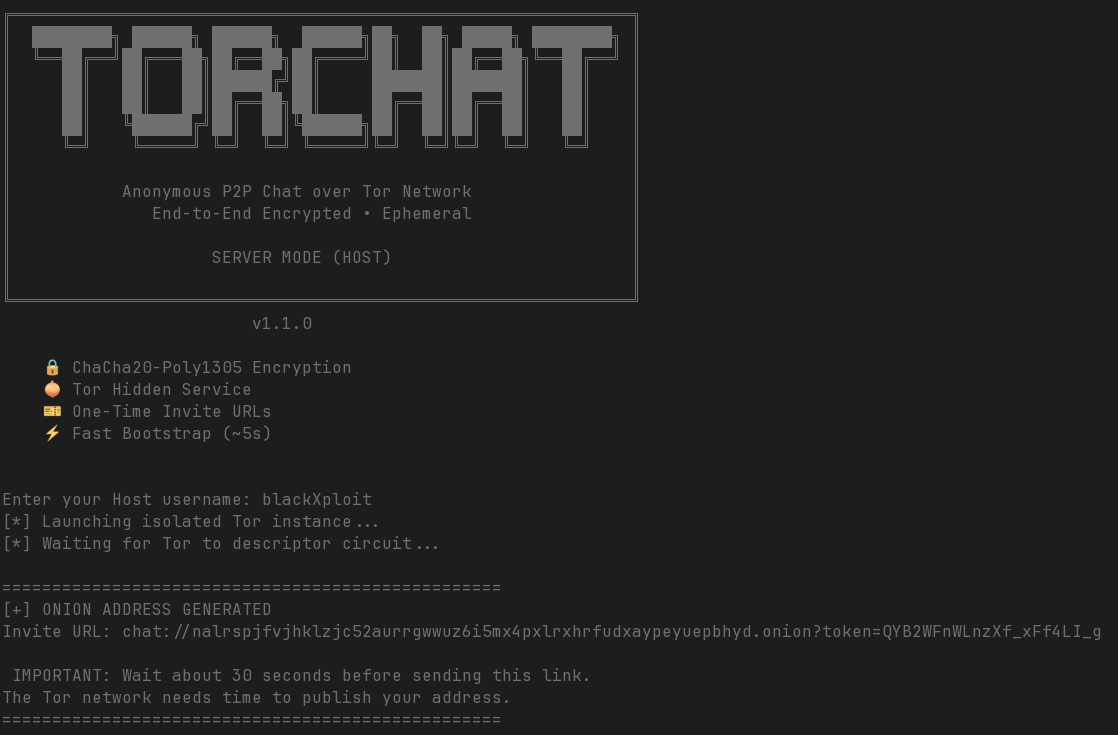 blackxploit-404/torchat
TorChat - Secure, private, and anonymous peer-to-peer chat over the Tor network
 google/longfellow-zk
Implementation of the Google Zero-Knowledge library for Identity Protocols.
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…
 minh3102011/cve-2026-18963_analyst
Docker-based lab for reproducing Keycloak CVE-2026-18963, including vulnerable version setup, realm seeding, and source-level workflow analysis with…
 gagaltotal/cve-2026-mikrotik-poc
CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
 het-p301204/afterlife
Revocation persistence detection lab: when the password reset succeeds but the attacker never leaves. Reproduces the Strapi CVE-2026-22706…
 ivanesk315/cve-2026-53519
Docker lab reproducing CVE-2026-53519, a pre-auth path traversal in Nezha Dashboard that leaks jwt_secret_key and enables JWT forgery and admin…
 ivanesk315/cve-2026-18963
Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…
 sassoftware/shiro
CVE-2026-49268 — Analysis and Remediation of an LDAP Injection Authentication Bypass Vulnerability
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass