
nimux
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
authenticationcommand-and-controlexploitation+6
9
blue0x1/nimuxPure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
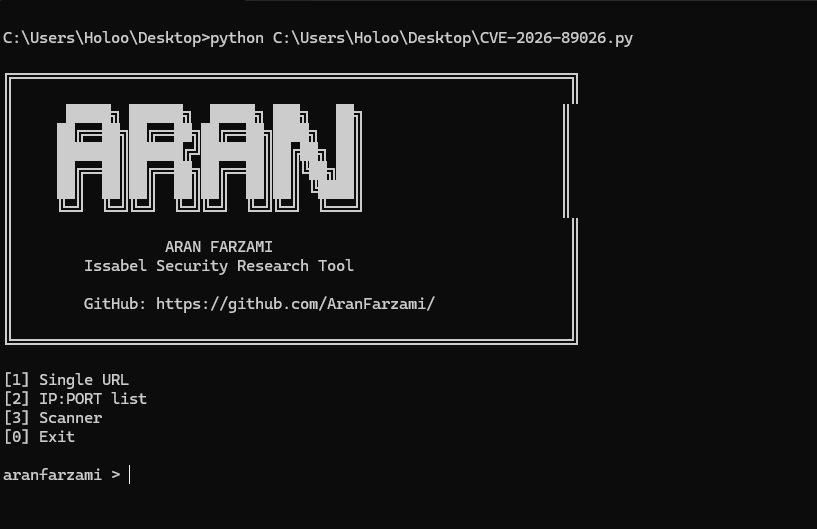 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 ilokaas/cve-2026-24061-payload
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 almondoffsec/passthecert
Proof-of-Concept tool to authenticate to an LDAP/S server with a certificate through Schannel
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 0xgh057r3c0n/cve-2026-9198
IBM Langflow Unauthenticated RCE via Auto-Login Bypass
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 secdev02/easytokens
Kali365 - EvilTokens Replica
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…