CVE-2026-82329-PoC-Exploit

Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…

Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…

Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…

Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…

CVE-2025-14269 PoC exploit

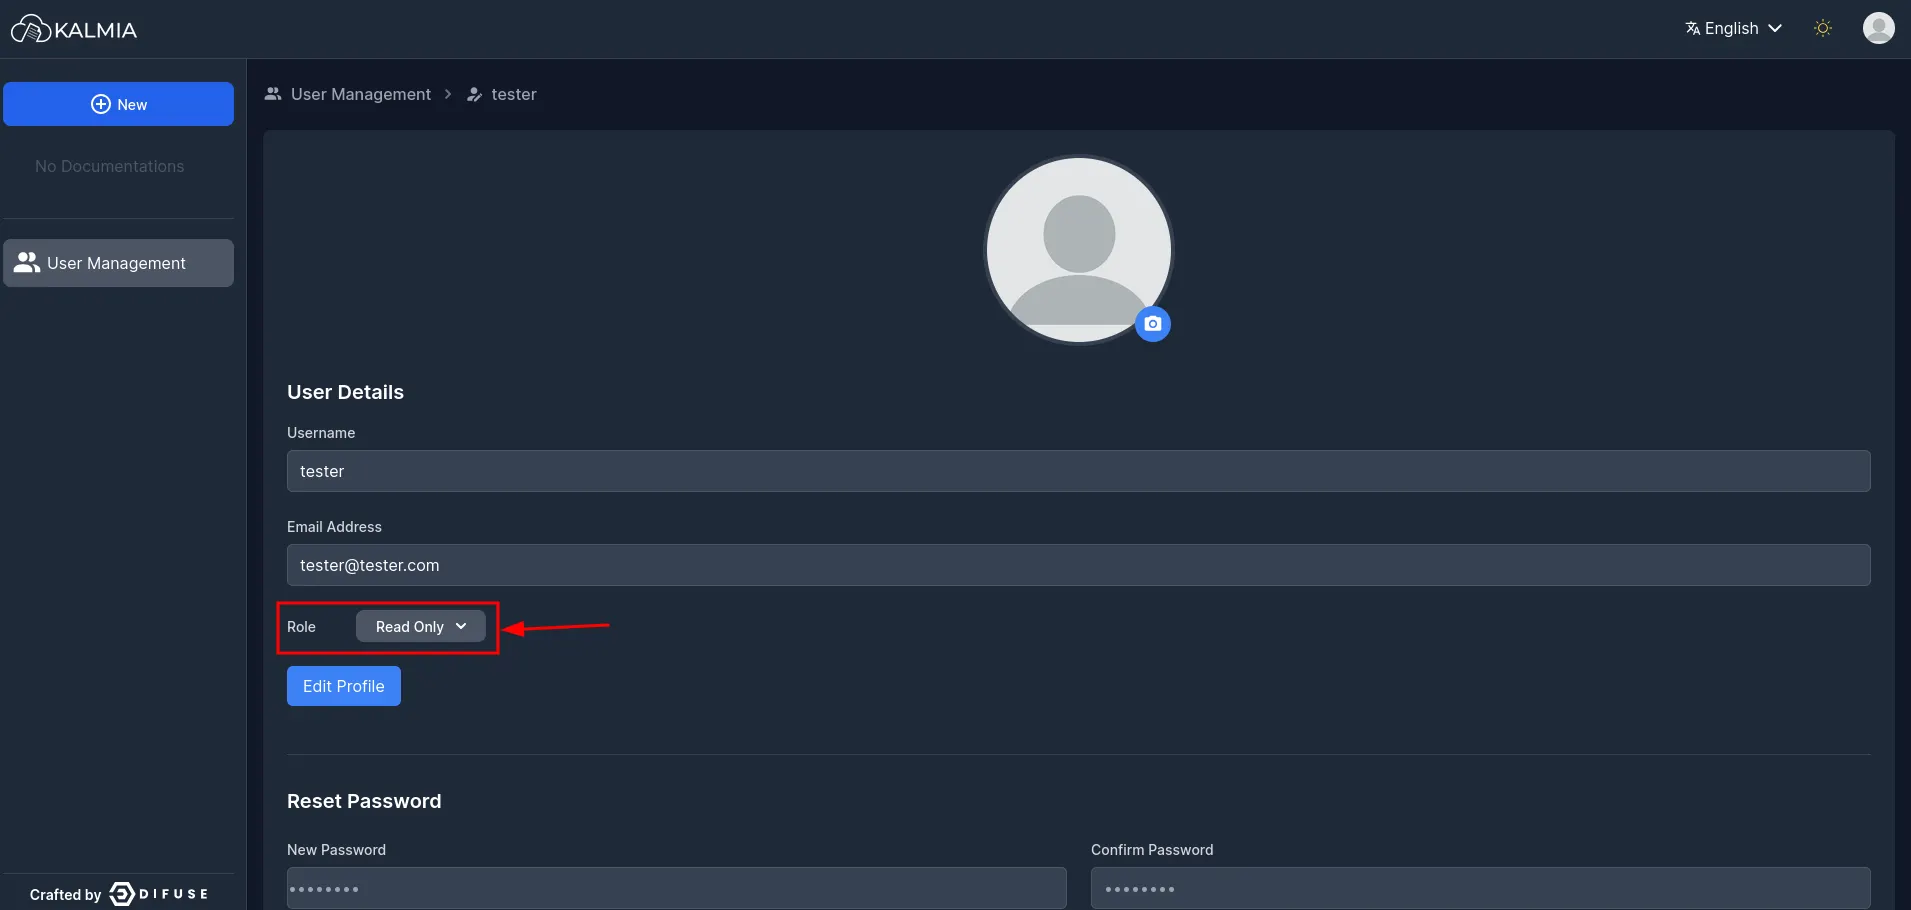
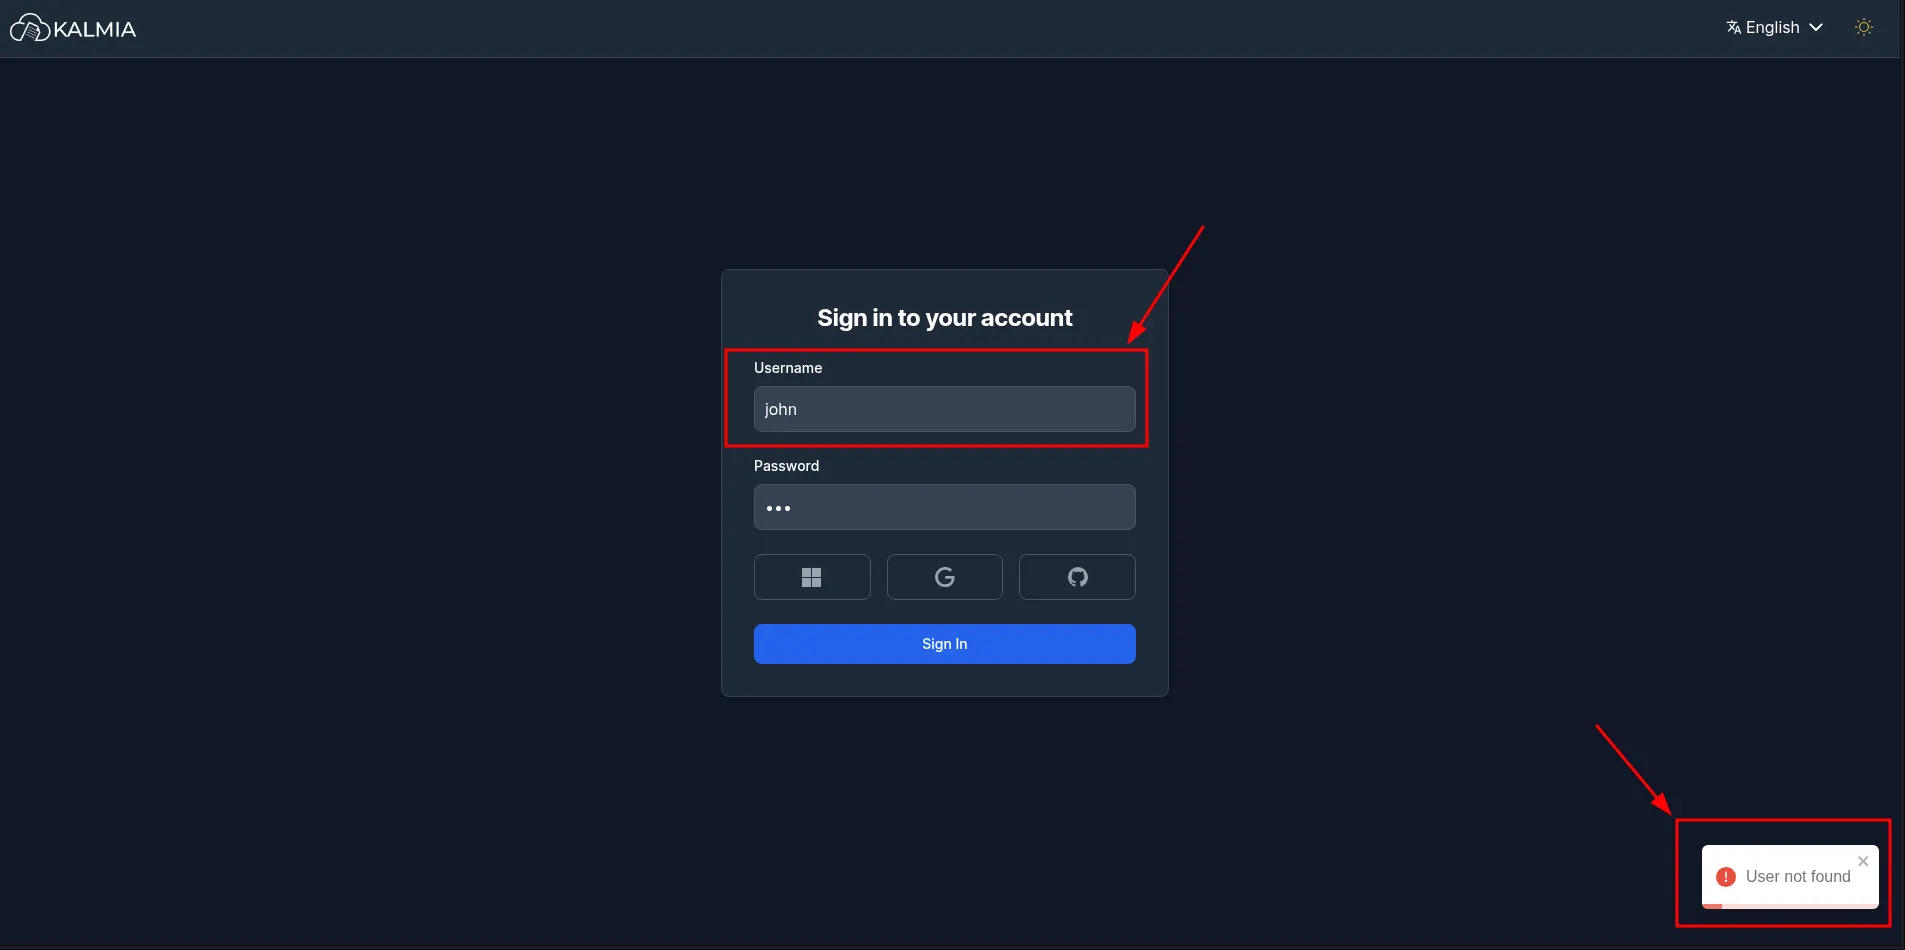
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…

DifuseHQ Kalmia CMS version 0.2.0 is vulnerable to user enumeration through distinguishable error responses in the /kal-api/auth/jwt/create…

PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…

Demonstration of CVE-2025-29927: Next.js middleware authentication bypass via x-middleware-subrequest header spoofing. Includes vulnerable and fixed…

Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.

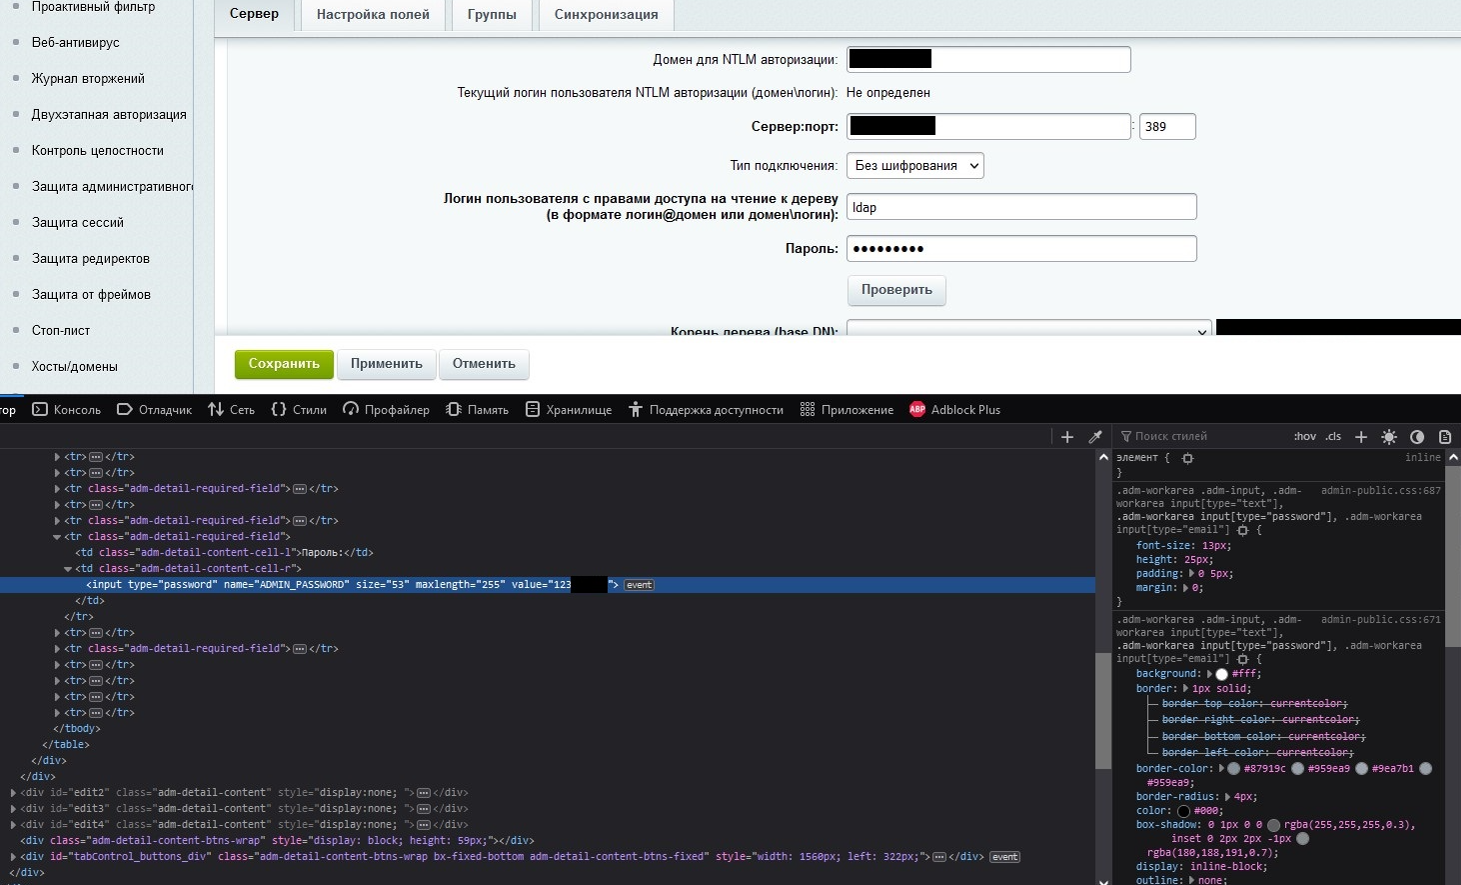
Bitrix Vulnerability CVE-2022-43959

check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949

CentOS Control Web Panel, Root Privilege Escalation