
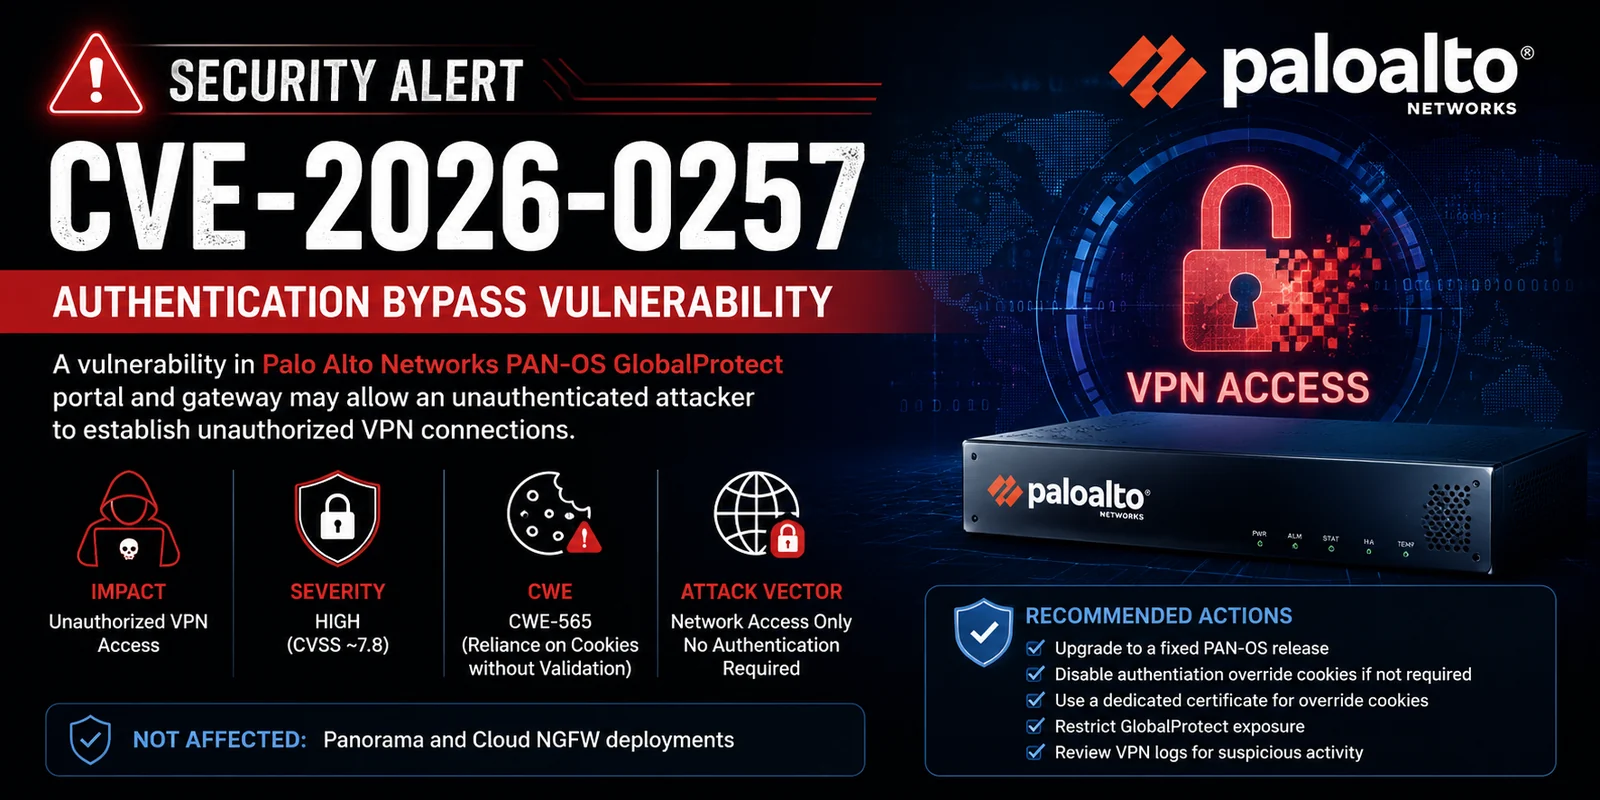
CVE-2026-0257
 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
authenticationexploitationnetwork-security+4
3
0xredash/cve-2026-0257Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
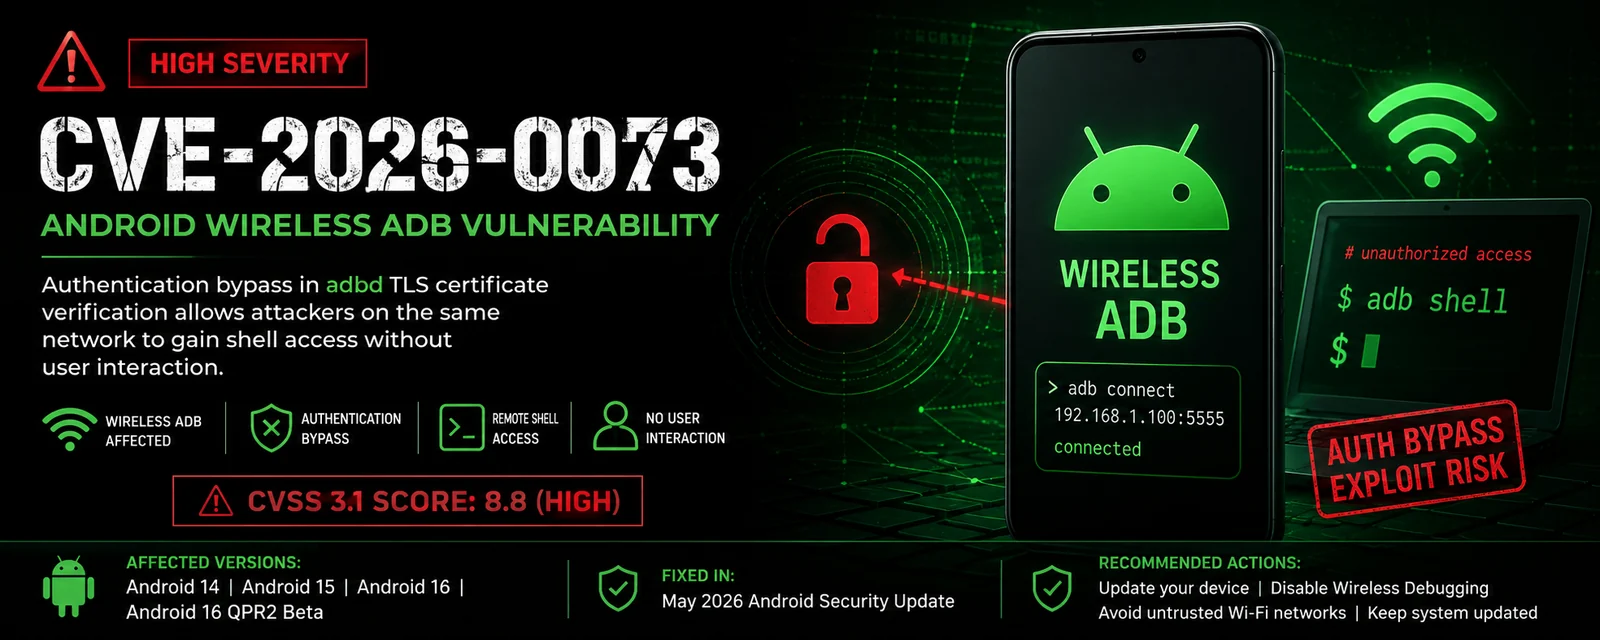 0xredash/cve-2026-0073
C++ proof-of-concept checker and exploit for CVE-2026-0073, an Android Wireless ADB authentication bypass allowing unauthenticated remote shell…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 orevim/cve-2026-18963-poc
Proof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 d0ge/xsw
XML Signature Wrapping Burp Suite Extensions
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
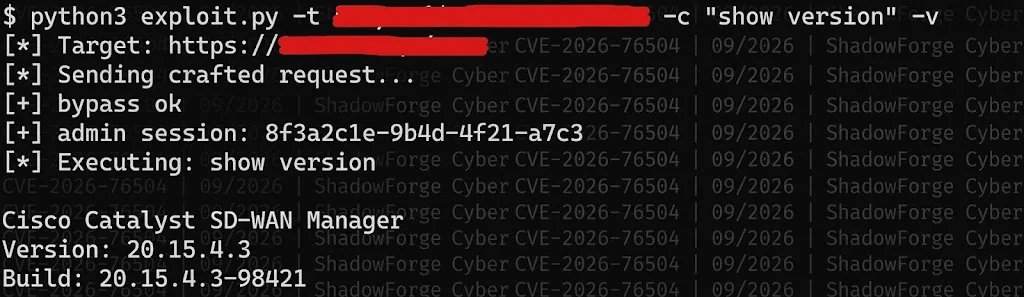 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
 anoxhunterdump-ctrl/cve-2026-14378-devkit-pro-auth-bypass
Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
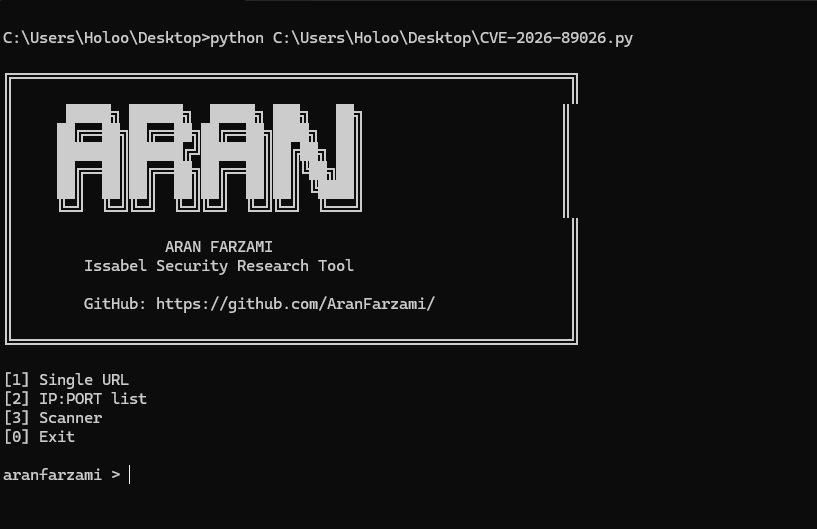 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 o-sec/cve-2026-41452-poc
Proof-of-concept exploit for CVE-2026-41452, a critical authentication bypass in Krayin CRM <= 2.2.4 allowing unauthenticated admin account takeover…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…