Exploit-For-CVE-2026-18963

Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…

Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…

Simple and sane cryptographic wrapper library.

NLA Honeypot Associated Research

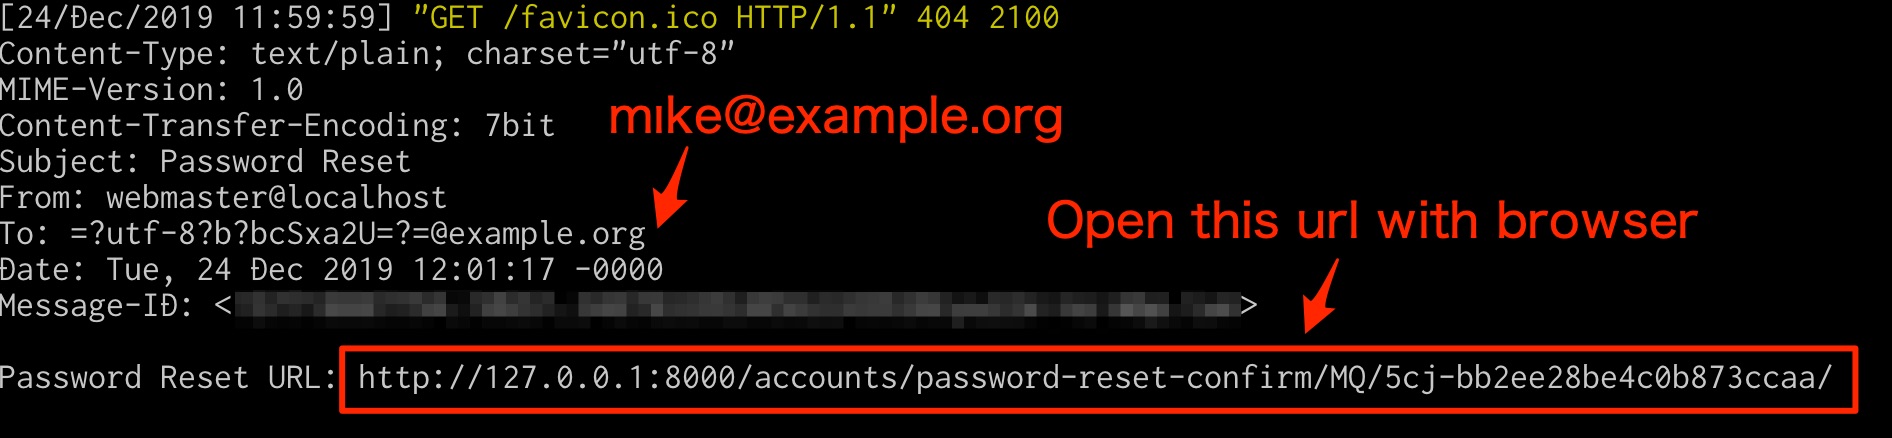
PoC for CVE-2019-19844(https://www.djangoproject.com/weblog/2019/dec/18/security-releases/)

Lightweight Python checker that tests Active Directory credentials for exposure to CVE-2022-33679 (Kerberos AS-REP roast without pre-authentication).…

Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…

Exploit for CVE-2022-1162: hardcoded password bypass in GitLab CE/EE OmniAuth accounts, enabling unauthorized login with a known credential.

SwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO

Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…

WireBug is a toolset for Voice-over-IP penetration testing

A tool for checking if MFA is enabled on multiple Microsoft Services

Enumerate information from NTLM authentication enabled web endpoints 🔎