
pfsense-api-example-ssl-verify
 abraxas/pfsense-api-example-ssl-verify
pfSense Plus MIM API toolkit b4acd7ca - Medium - Remote - Privilege leftover - official samples verify_ssl=False
authenticationdefensive-toolsexploitation+6
abraxas/pfsense-api-example-ssl-verifypfSense Plus MIM API toolkit b4acd7ca - Medium - Remote - Privilege leftover - official samples verify_ssl=False
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments
 abraxas/nextcloud-federated-ocm-token
Nextcloud 35.0.0 — federated share secret is an unscoped app password for the sharer's whole Files tree
 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
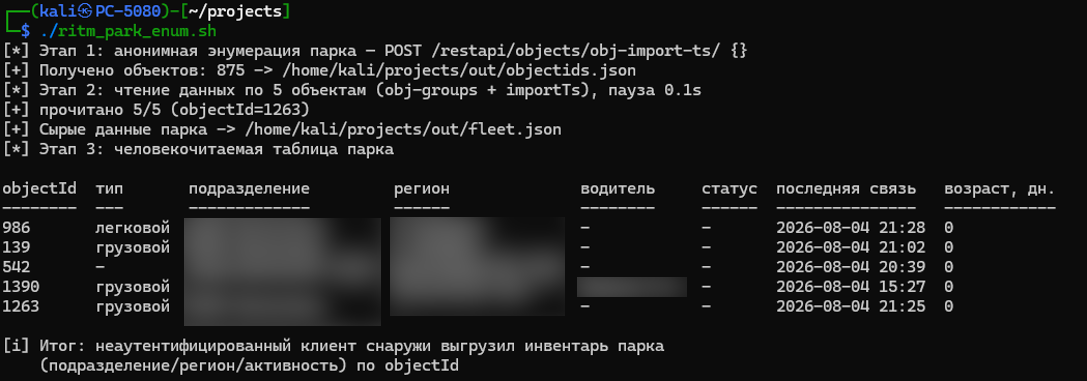 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 bishopfox/cve-2026-19490-check
Safely detect Citrix NetScaler SAML auth bypass CVE-2026-19490
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).