
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
28 results
synology-nas-cli preview

synology-nas-cli

GitLabaa22396584/synology-nas-cli

nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…

ai-securityauthenticationconfiguration-auditing+9
1
4 days ago
vaultwarden preview

vaultwarden

GitHubdani-garcia/vaultwarden

Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs
authenticationauthentication-authorizationcontainer-security+5
70.3k21h 48m ago
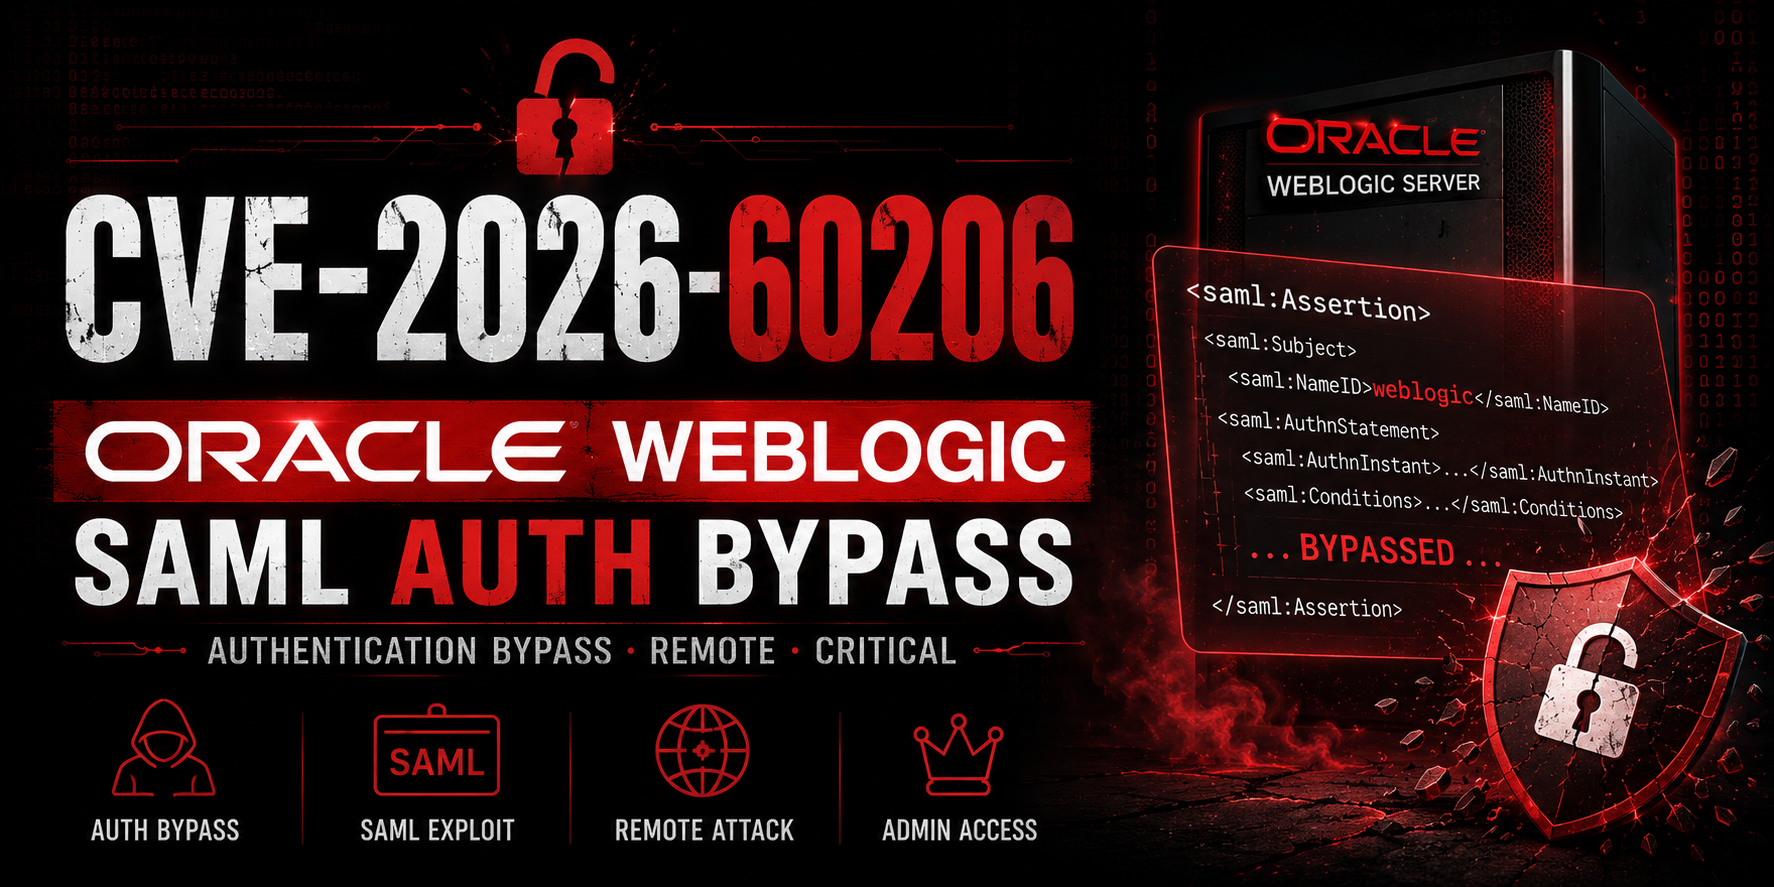
CVE-2026-60206 preview

CVE-2026-60206

GitHubdebajyoti0-0/cve-2026-60206

Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
authenticationexploitationpenetration-testing+2
13 months ago
CVE-2026-35616-check preview

CVE-2026-35616-check

GitHubbishopfox/cve-2026-35616-check

Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
api-security-testingauthenticationexploitation+3
27 months ago
pritunl-CVE-2020-25200 preview

pritunl-CVE-2020-25200

GitHublukaszstu/pritunl-cve-2020-25200

Exploit for CVE-2020-25200: enumerates valid Pritunl VPN usernames by analyzing HTTP response code changes after repeated login attempts.

authenticationinformation-gatheringpenetration-testing+3
46 years ago
CVE-2022-23342 preview

CVE-2022-23342

GitHubinitroot/cve-2022-23342

Proof-of-concept for Active Directory username enumeration vulnerability in Hyland OnBase via login endpoint response differences, enabling…

authenticationinformation-gatheringreconnaissance+2
34 years ago
MultiExploit preview

MultiExploit

GitHubvesu-nights/multiexploit

CVE-2023-21173 Exploit - Remote Code Execution in SQL Server 2022

authenticationdatabase-securityexploitation+3
1 year ago
CVE-2026-40022 preview

CVE-2026-40022

GitHuboscerd/cve-2026-40022

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
authenticationexploitationmisconfiguration+3
4 months ago
WantasticCore preview

WantasticCore

GitHubwantasticapp/wantasticcore

AIO Cloud Managment Server
ai-securityauthenticationcloud-security+6
1420 days ago
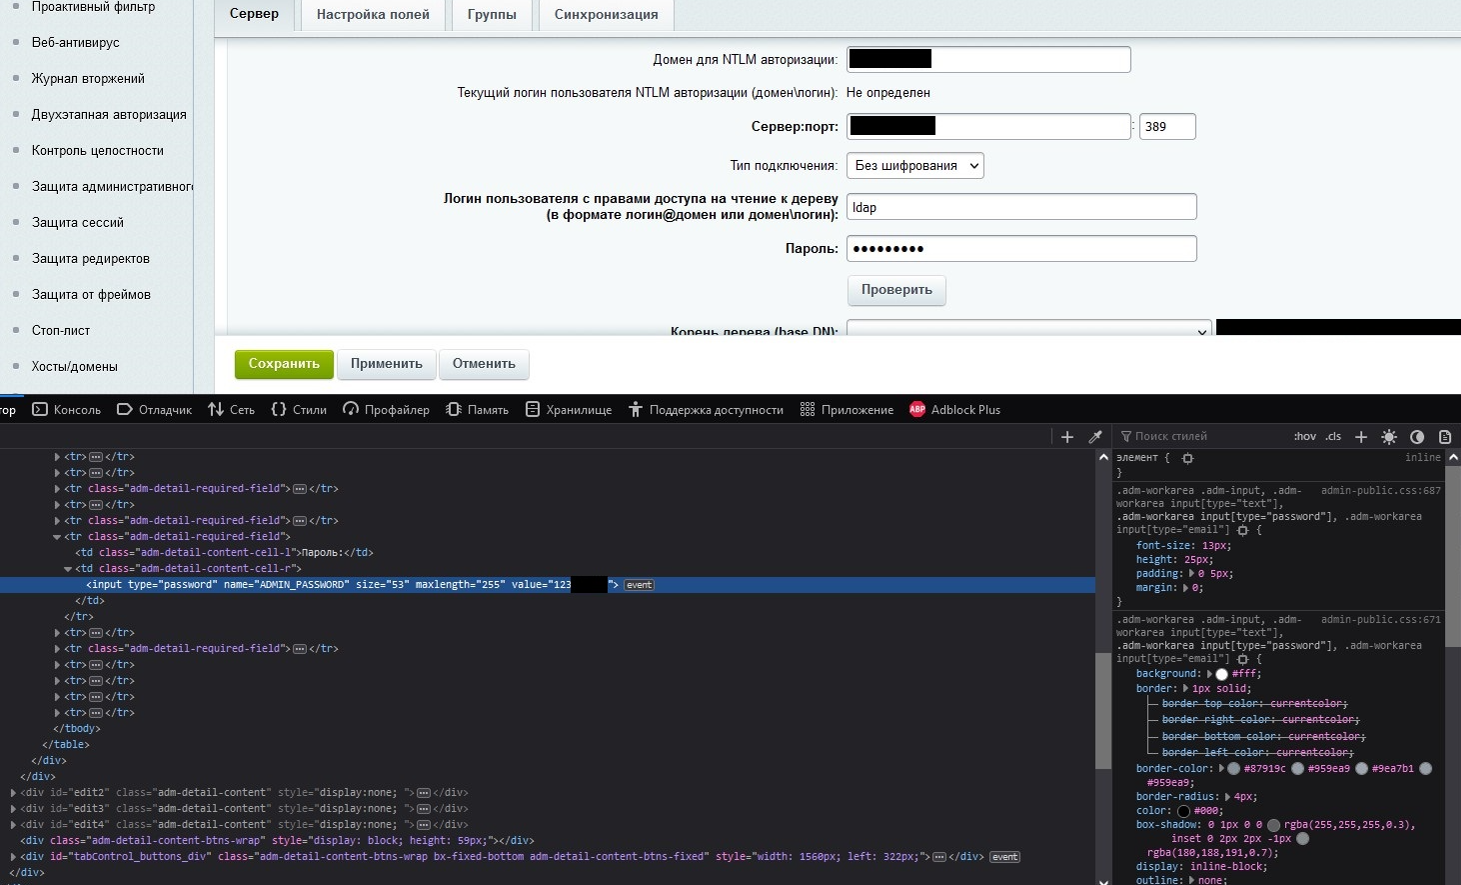
CVE-2022-43959 preview

CVE-2022-43959

GitHubsecware-ru/cve-2022-43959

Bitrix Vulnerability CVE-2022-43959
authenticationconfiguration-auditingmisconfiguration+3
43 years ago
CVE-2026-41940 preview

CVE-2026-41940

GitHubjenderal92/cve-2026-41940

Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
authenticationcommand-and-controlexploitation+6
45 months ago
asf__james-project_CVE-2022-22931_3-6-0 preview

asf__james-project_CVE-2022-22931_3-6-0

GitHubshoucheng3/asf__james-project_cve-2022-22931_3-6-0

Modular Java mail server supporting IMAP, SMTP, POP3, and JMAP with Docker deployment, distributed architecture, and CLI management for secure…
authenticationcloud-securityconfiguration-auditing+5
1 year ago
CVE-2023-27524 preview

CVE-2023-27524

GitHubhorizon3ai/cve-2023-27524

Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset
authenticationexploitationmisconfiguration+3
1133 years ago
CVE-2024-4040 preview

CVE-2024-4040

GitHubgotr00t0day/cve-2024-4040

Exploit for CrushFTP SSTI vulnerability (CVE-2024-4040) enabling unauthenticated file read, authentication bypass, and remote code execution on…
authenticationexploitationinformation-gathering+3
82 years ago
CVE-2025-4602 preview

CVE-2025-4602

GitHubd0n601/cve-2025-4602

eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Read

authenticationexploitationinformation-gathering+3
11 year ago
CVE-2024-4040-SSTI-LFI-PoC preview

CVE-2024-4040-SSTI-LFI-PoC

GitHubstuub/cve-2024-4040-ssti-lfi-poc

CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
authenticationexploitationinformation-gathering+3
662 years ago
CVE-2025-2825-CrushFTP-AuthBypass preview

CVE-2025-2825-CrushFTP-AuthBypass

GitHubshivshantp/cve-2025-2825-crushftp-authbypass

Authentication Bypass PoC for CVE-2025-2825 – Exploiting CrushFTP 10.x
authenticationexploitationinformation-gathering+5
51 year ago
Bash-Script-CVE-2019-17662 preview

Bash-Script-CVE-2019-17662

GitHubkxisxr/bash-script-cve-2019-17662

ThinVNC 1.0b1 is vulnerable to arbitrary file read, which leads to a compromise of the VNC server. The vulnerability exists even when authentication…

authenticationexploitationinformation-gathering+3
14 years ago
Previous12Next