

evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
406
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
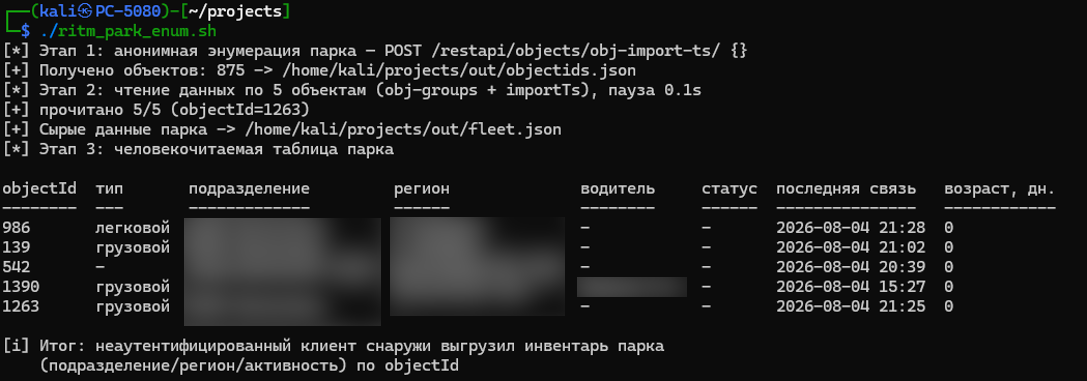 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 murrez/cve-2026-100835
Python PoC for CVE-2026-100835: audits Contrast manifests for AllowedChipIDs/AllowedPIIDs, detects versions, and probes Coordinator endpoints to…
 murrez/cve-2026-14378
Python PoC scanner and exploit helper for CVE-2026-14378, an unauthenticated admin session takeover in the DevKit Pro WordPress plugin via forged…
 murrez/cve-2026-19660
Python PoC scanner and exploit for CVE-2026-14378, a pre-auth administrator session takeover in the DevKit Pro WordPress plugin via forged…
 hasanuyarrr/cve-2026-18782-trex-mes-uygulamalarinda-sql-zafiyeti
Advisory and technical write-up for CVE-2026-18782, a critical SQL injection in TREX MES web API endpoints enabling auth bypass, data theft, and RCE…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 gagaltotal/cve-2026-mikrotik-poc
CVE-2026-86060 - CVE-2026-67279 - CVE-2026-67276 RouterOS SSH
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 biitts/cve-2026-72001-pangolin-cross-org-auth-bypass
PoC for CVE-2026-72001 — Pangolin < 1.22.0 cross-organization resource authentication bypass via the share-link access-token endpoint (CWE-639, CVSS…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…