

CVE-2026-18963-PoC
 orevim/cve-2026-18963-poc
Proof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…
authenticationexploitationpenetration-testing+3
orevim/cve-2026-18963-pocProof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 o-sec/cve-2026-41452-poc
Proof-of-concept exploit for CVE-2026-41452, a critical authentication bypass in Krayin CRM <= 2.2.4 allowing unauthenticated admin account takeover…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
 bombobombone/cve-2026-73310
Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 0xlyvio/cve-2026-1529-keycloak-exploit-tool
Keycloak: Unauthorized organization registration via improper invitation token validation
 0xlyvio/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a Keycloak reset-credentials bypass leading to account takeover. Demonstrates the vulnerability and…
 ull0a/cve-2024-55591-poc
Educational implementation in Go for CVE-2024-55591 (Fortinet FortiOS Authentication Bypass). Designed for security research, vulnerability…
 eqstlab/cve-2026-18963
Proof-of-concept exploit for CVE-2026-18963, demonstrating unauthenticated account takeover by bypassing the reset-credentials flow in web…
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 malikhamza7/cve-2026-22794-poc
🔴 CVE-2026-22794 - Appsmith Password Reset Account Takeover via Origin Header Injection | PoC Exploit + Nuclei Template
 jarnovandenbrink/cve-2026-26128
Exploits Kerberos reflection via Unicode normalization in Windows Active Directory to relay authentication to ADCS and MSSQL, enabling…
 amirhosseinjamshidi64/cve-2026-7567-poc
Proof-of-concept exploit for CVE-2026-7567, an authentication bypass in WordPress Temporary Login Plugin <= 1.0.0, enabling account takeover. For…
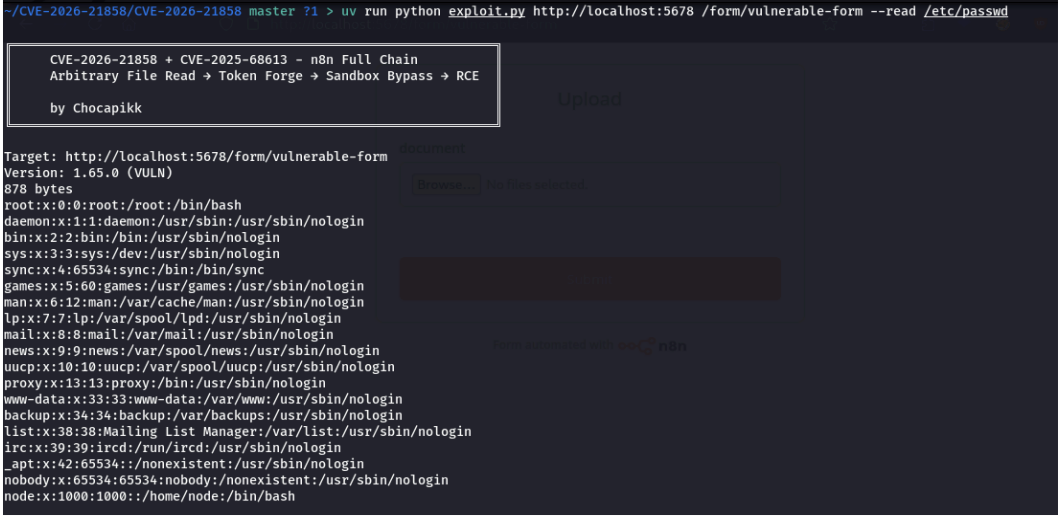 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)