

E2EAuth
 roxanne_ardary/e2eauth
Cross-platform TOTP/HOTP authenticator specification with end-to-end encrypted vault sync, local-first storage, device management, and threshold…
authenticationcryptographydefensive-tools+4
roxanne_ardary/e2eauthCross-platform TOTP/HOTP authenticator specification with end-to-end encrypted vault sync, local-first storage, device management, and threshold…
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…
 nvicloud/cve-2026-12352
Proof-of-concept for CVE-2026-12352, an authentication bypass in Digi PortServer TS that discloses device configuration including plaintext RADIUS…
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
 nfc-tools/mfoc
Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 yubico/libfido2
Provides library functionality for FIDO2, including communication with a device over USB or NFC.
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 george0papasotiriou/cve-2026-11116-snmpv3-authentication-bypass-via-default-engineid
Demonstrates CVE-2026-11116 SNMPv3 authentication bypass caused by guessable default EngineIDs, with a Python pysnmp simulation and guidance for…
 mayyhem/maestro
Abusing Azure services over C2
 zb3/tiandy-research
This repository contains the results of my August 2020 research of Tiandy's IPC/NVR firmware. I found two vulnerabilities that could be used to…
 danmcinerney/device-pharmer
Opens 1K+ IPs or Shodan search results and attempts to login
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 ccordeiro/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
 carlosevieira/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
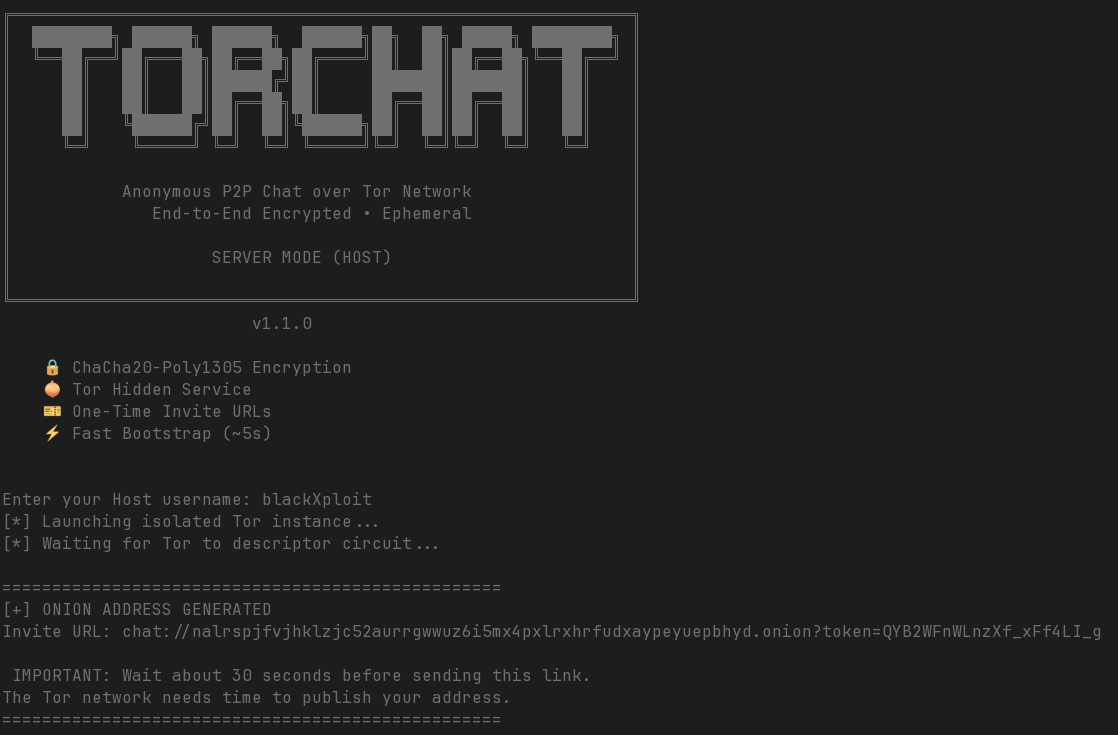 blackxploit-404/torchat
TorChat - Secure, private, and anonymous peer-to-peer chat over the Tor network
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…