
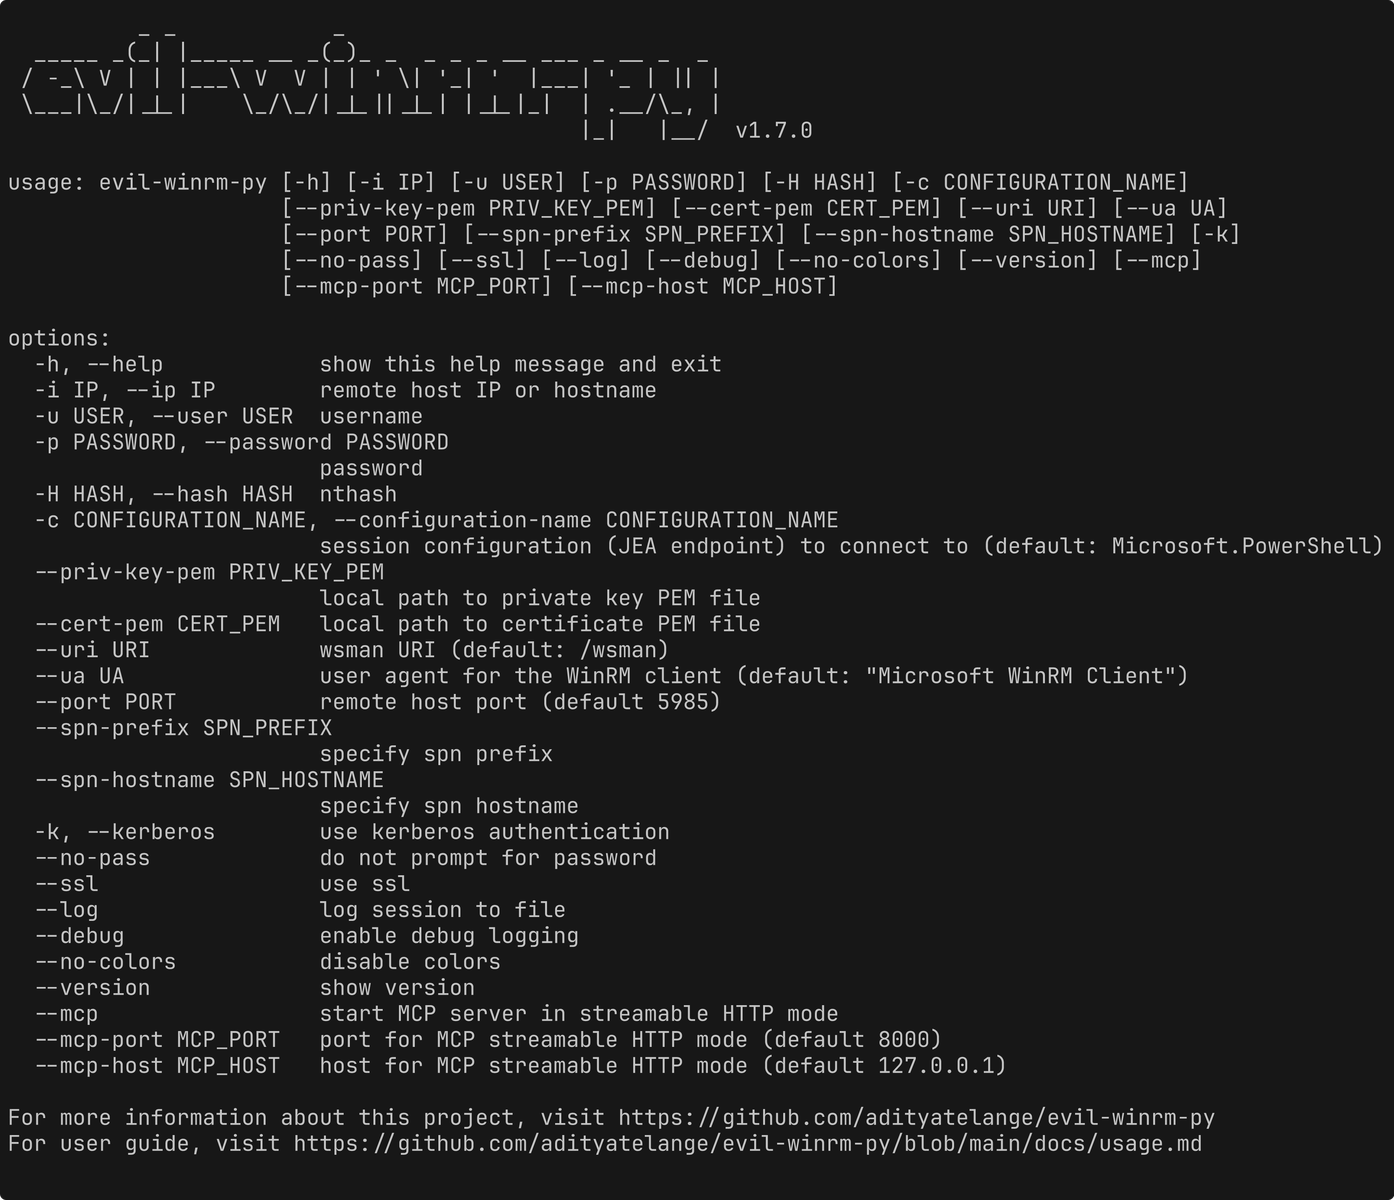
evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
400
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
 chewkeanho/research-cve-2026-85649
[MIRROR] The CVE-2026-85649 Security Research Publication.
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 naheeju/poc-cve-2026-0073
Security research PoC for CVE-2026-0073: ADB authentication bypass verification
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 caginkyr/cve-2026-7671
Proof-of-concept for CVE-2026-7671, demonstrating OTP brute-force on Tornet Scooter Android app due to missing rate limiting on /TwoFactor endpoint.
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
 randeepajayasekara/cve-2026-20127
Walkthrough of the CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN from first malformed peering request to root on the management plane.
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
 martinfrancois/cve-2021-36460
Advisory detailing a pass-the-hash vulnerability in VeryFitPro app (<=3.3.7) where SHA-1 password hashes are used for authentication, enabling…