CVE-2026-29000
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
authenticationctfeducation+5
clayofgilgamesh/cve-2026-29000CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 ge0rg/memorizingtrustmanager
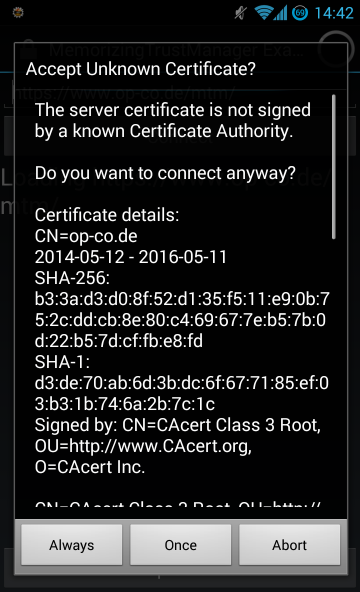
A "plugin" for Android Java to allow asking the user about SSL certificates
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 volodymyr-hladkyi-symphony/demo-cve-2022-21449
Educational demo of CVE-2022-21449 Java ECDSA signature bypass using real and fake JWT tokens to illustrate the vulnerability and its impact on…
 shoucheng3/asf__james-project_cve-2022-22931_3-6-0
Modular Java mail server supporting IMAP, SMTP, POP3, and JMAP with Docker deployment, distributed architecture, and CLI management for secure…