
pfsense-api-enroll-autoadd
 abraxas/pfsense-api-enroll-autoadd
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - Paramiko AutoAddPolicy enroll
authenticationcryptographyexploitation+6
abraxas/pfsense-api-enroll-autoaddpfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - Paramiko AutoAddPolicy enroll
 abraxas/pfsense-api-example-ssl-verify
pfSense Plus MIM API toolkit b4acd7ca - Medium - Remote - Privilege leftover - official samples verify_ssl=False
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments
 abraxas/nextcloud-federated-ocm-token
Nextcloud 35.0.0 — federated share secret is an unscoped app password for the sharer's whole Files tree
 abraxas/uptime-kuma-setup-toctou
Proof-of-concept for a TOCTOU race in Uptime Kuma's first-run Socket.IO setup, letting an unauthenticated attacker plant a hidden second admin and…
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 cyrusimap/cyrus-sasl
Cyrus SASL API implementation providing client- and server-side authentication and authorization services via pluggable SASL mechanisms per RFC 4422.
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 softethervpn/softethervpn
Cross-platform multi-protocol VPN server and client supporting SSL-VPN, WireGuard, OpenVPN, IPsec, L2TP, MS-SSTP, L2TPv3 and EtherIP with AES-256…
 j-baines/even-you-brutus
Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
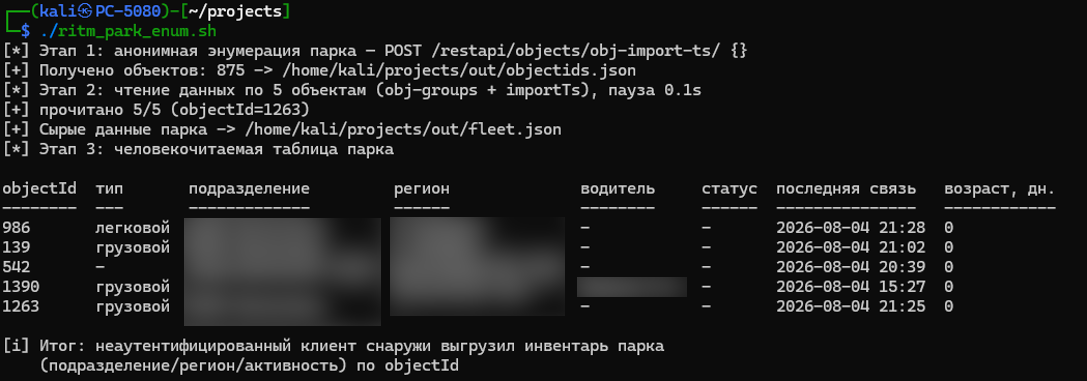 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.