
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
ntlmscout preview

ntlmscout

GitHubboydhacks/ntlmscout

Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
authenticationdns-analysisinformation-gathering+8
52
13 days ago
CVE-2026-19490 preview

CVE-2026-19490

GitHubtarpeg007/cve-2026-19490

NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
authenticationbinary-analysisexploitation+4
1729 days ago
CVE-2026-66908 preview

CVE-2026-66908

GitHuboscerd/cve-2026-66908

Proof-of-concept reproducer for Apache Camel JWT authentication bypass (CVE-2026-66908) demonstrating missing iss/aud validation in…
authenticationeducationexploitation+2
1 month ago
Berserko preview

Berserko

GitHubnccgroup/berserko

Burp Suite extension to perform Kerberos authentication
authenticationpenetration-testingweb-proxies-interception+1
1062 years ago
HTTPSignatures preview

HTTPSignatures

GitHubnccgroup/httpsignatures

A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
api-securityapi-security-testingauthentication+3
434 years ago
Prox-Ez preview

Prox-Ez

GitHubsynacktiv/prox-ez

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

authenticationimpersonation-toolslateral-movement+4
1133 months ago
CP-PLUS-EZ-P21-CVE-2026-65893-65894 preview

CP-PLUS-EZ-P21-CVE-2026-65893-65894

GitHubcybervinner/cp-plus-ez-p21-cve-2026-65893-65894

Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
authenticationeducationembedded-systems-security+5
2 months ago
CVE-2025-23048-POC preview

CVE-2025-23048-POC

GitHubabsholi7ly/cve-2025-23048-poc

Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
authenticationexploitationpenetration-testing+3
411 months ago
CVE-2026-35616-check preview

CVE-2026-35616-check

GitHubbishopfox/cve-2026-35616-check

Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…

api-security-testingauthenticationexploitation+3
25 months ago
raider preview

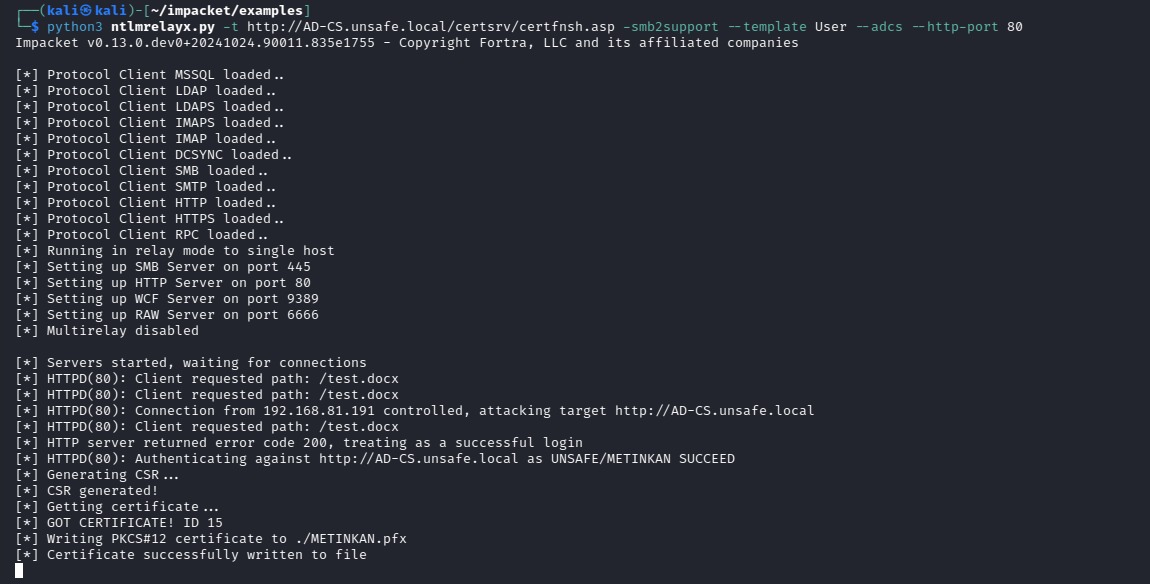
raider

GitHubowasp/raider

OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
1003 years ago
CVE-2024-38200 preview

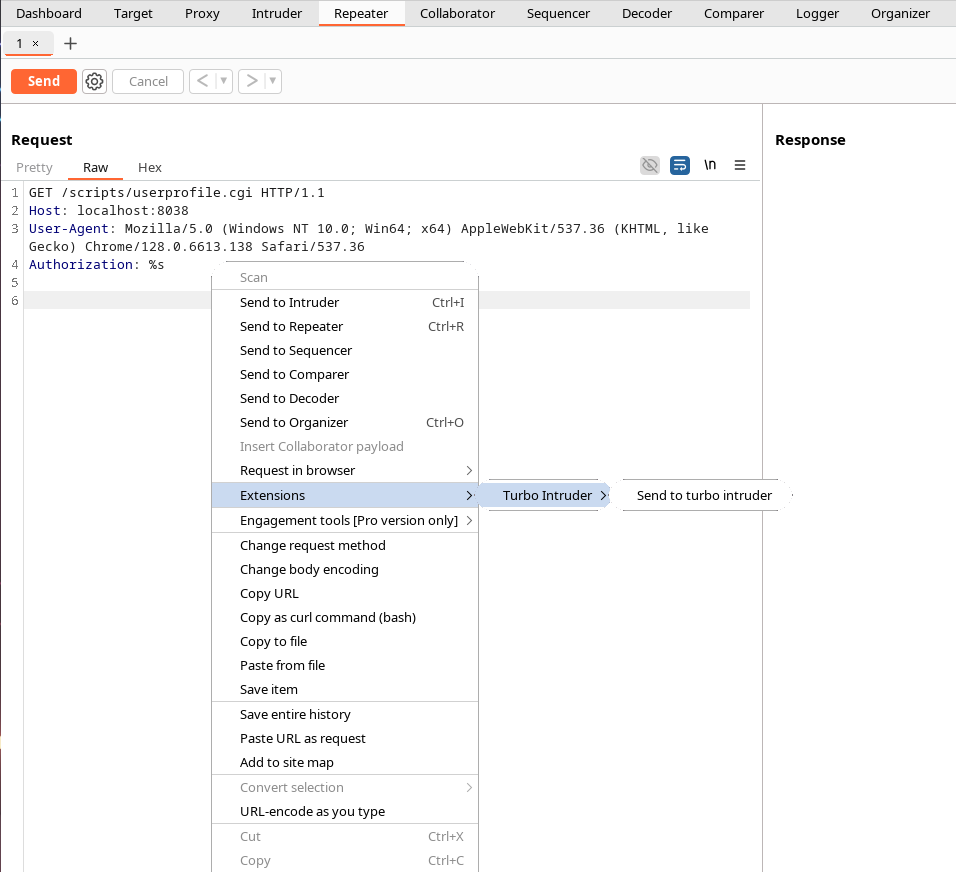
CVE-2024-38200

GitHubpasstheticket/cve-2024-38200

CVE-2024-38200 & CVE-2024-43609 - Microsoft Office NTLMv2 Disclosure Vulnerability
authenticationeducationexploitation+4
1471 year ago
PoC_CVE-2019-0217 preview

PoC_CVE-2019-0217

GitHubsavsch/poc_cve-2019-0217

Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
authenticationeducationexploitation+3
1 year ago
pritunl-CVE-2020-25200 preview

pritunl-CVE-2020-25200

GitHublukaszstu/pritunl-cve-2020-25200

Exploit for CVE-2020-25200: enumerates valid Pritunl VPN usernames by analyzing HTTP response code changes after repeated login attempts.
authenticationinformation-gatheringpenetration-testing+3
46 years ago
Exploit-CVE-2024-9513-NetAdmin-IAM-Allows-User-Enumeration-In-Active-Directory preview

Exploit-CVE-2024-9513-NetAdmin-IAM-Allows-User-Enumeration-In-Active-Directory

GitHubelizeuopain/exploit-cve-2024-9513-netadmin-iam-allows-user-enumeration-in-active-directory

Proof-of-concept exploit for CVE-2024-9513 targeting user enumeration in NetAdmin IAM via HTTP POST request to…

authenticationexploitationinformation-gathering+3
21 year ago
Digisol-DG-GR1321-s-Password-Policy-Bypass-CVE-2024-2257 preview

Digisol-DG-GR1321-s-Password-Policy-Bypass-CVE-2024-2257

GitHubredfox-security/digisol-dg-gr1321-s-password-policy-bypass-cve-2024-2257

Exploit for CVE-2024-2257: bypasses password policy on Digisol DG-GR1321 routers via crafted HTTP request, enabling unauthorized access for…

authenticationexploitationpenetration-testing+2
2 years ago
CVE-2026-40022 preview

CVE-2026-40022

GitHuboscerd/cve-2026-40022

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
authenticationexploitationmisconfiguration+3
2 months ago
CVE-2026-24207 preview

CVE-2026-24207

GitHuboffseckit/cve-2026-24207

CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
authenticationcloud-securitycommand-and-control+8
13 months ago
CVE-2025-29927-Nextjs-Bypass-PoC preview

CVE-2025-29927-Nextjs-Bypass-PoC

GitHubdanielhallbro/cve-2025-29927-nextjs-bypass-poc

A Proof of Concept for CVE-2025-29927 demonstrating a middleware bypass in Next.js versions prior to 13.5.9

authenticationeducationexploitation+3
18 months ago
Previous123Next