
kafka-keycloak-oauth
 oriolrius/kafka-keycloak-oauth
Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
authenticationcloud-infrastructure-securityconfiguration-auditing+3
oriolrius/kafka-keycloak-oauthApache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…
 cyeezy08/kimai-cve-2026-49865-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 mauroeldritch/gevaudan
Exploit for Red Hat / GlusterFS CVE-2018-1088 & CVE-2018-1112, featured @ DEFCON 26, Las Vegas!
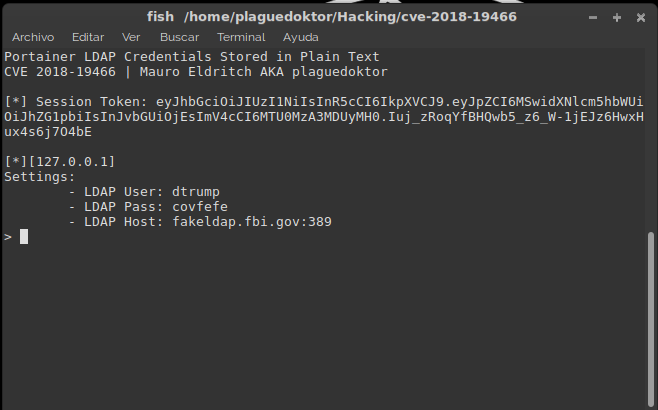 mauroeldritch/lempo
LEMPO (Ldap Exposure on POrtainer) is an exploit for CVE-2018-19466 (LDAP Credentials Disclosure on Portainer). Featured @ DevFest Siberia 2018
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 grantbirki/redash-vulnerable
A Dockerized Redash instance that is vulnerable to CVE-2021-21239