
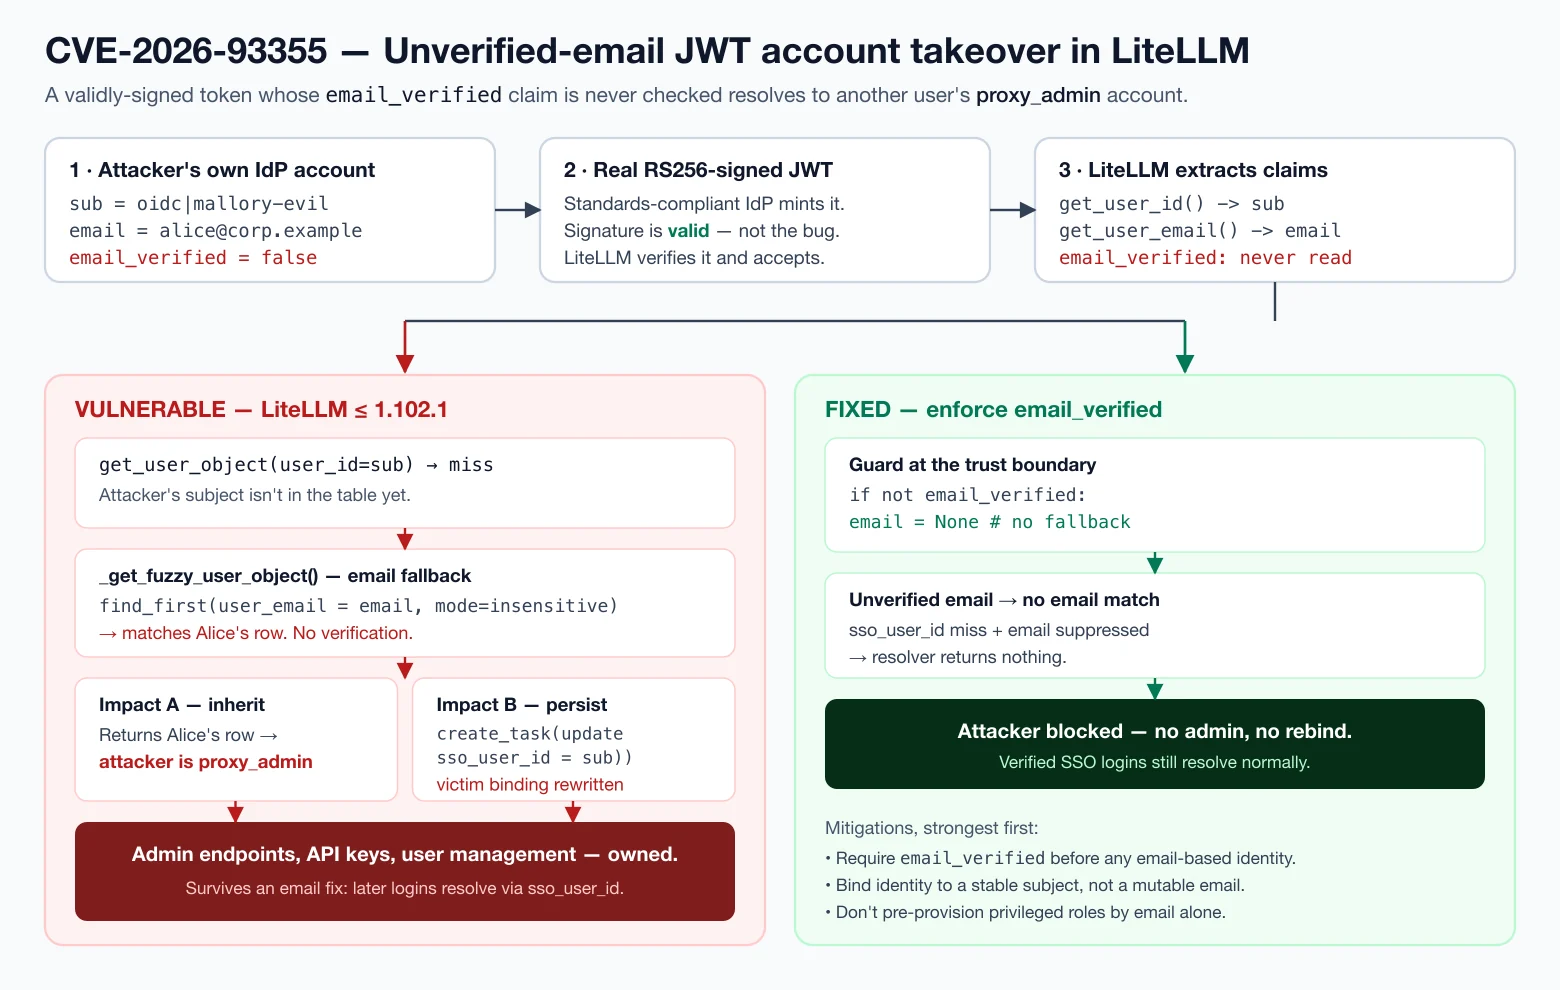
cve-2026-93355-lab
 inertfluid/cve-2026-93355-lab
Benign, offline reproduction of CVE-2026-93355 — LiteLLM unverified-email JWT account takeover (runs LiteLLM's real code)
authenticationeducationidentity-access-management+5
inertfluid/cve-2026-93355-labBenign, offline reproduction of CVE-2026-93355 — LiteLLM unverified-email JWT account takeover (runs LiteLLM's real code)
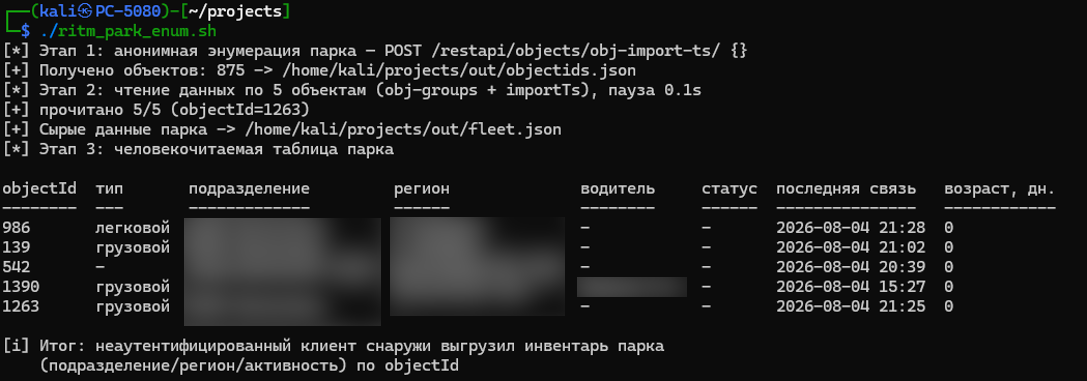 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
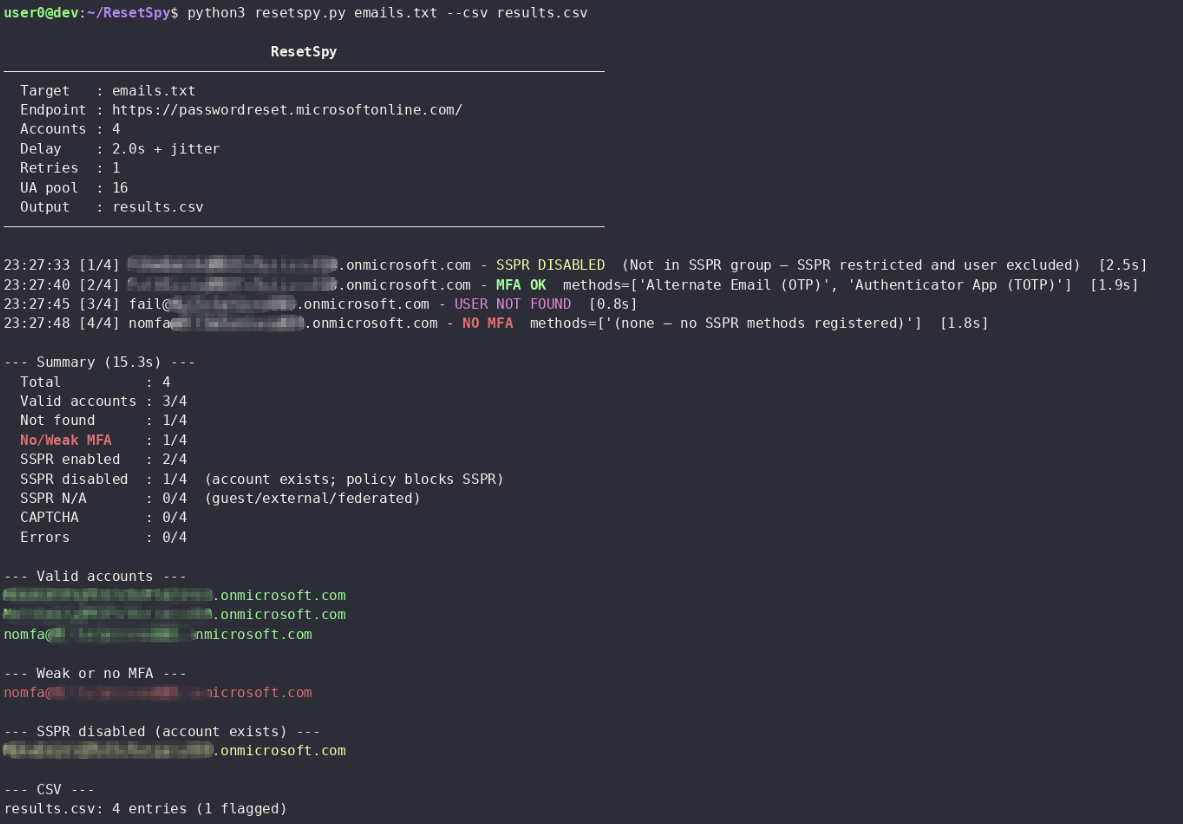 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
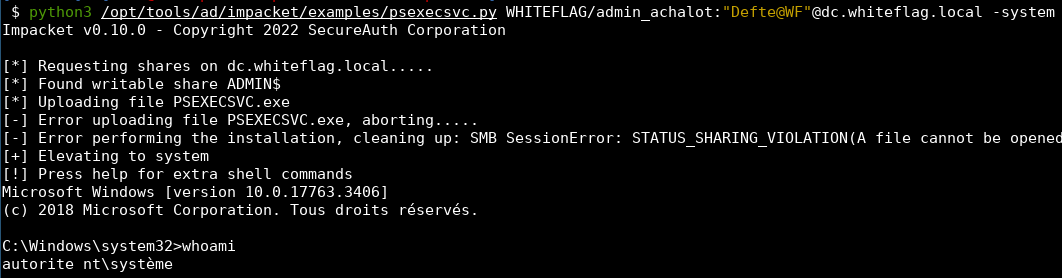 sensepost/susinternals
psexecsvc - a python implementation of PSExec's native service implementation
 pingport80/cve-2019-17240
This is the exploit of CVE-2019-17240.
 huyvo2910/cve-2025-25749-weak-password-policy-in-hoteldruid-3.0.7
Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…
 elandio-com/sharemylogin
Zero-Knowledge Credential Sharing

 kit-lang/packages/kit-oauth
OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…
 dropbox/securitybot
Distributed alerting for the masses!