
CVE-2021-32648
 daftspunk/cve-2021-32648
Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
authenticationcode-analysisvulnerability-analysis+1
1
daftspunk/cve-2021-32648Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
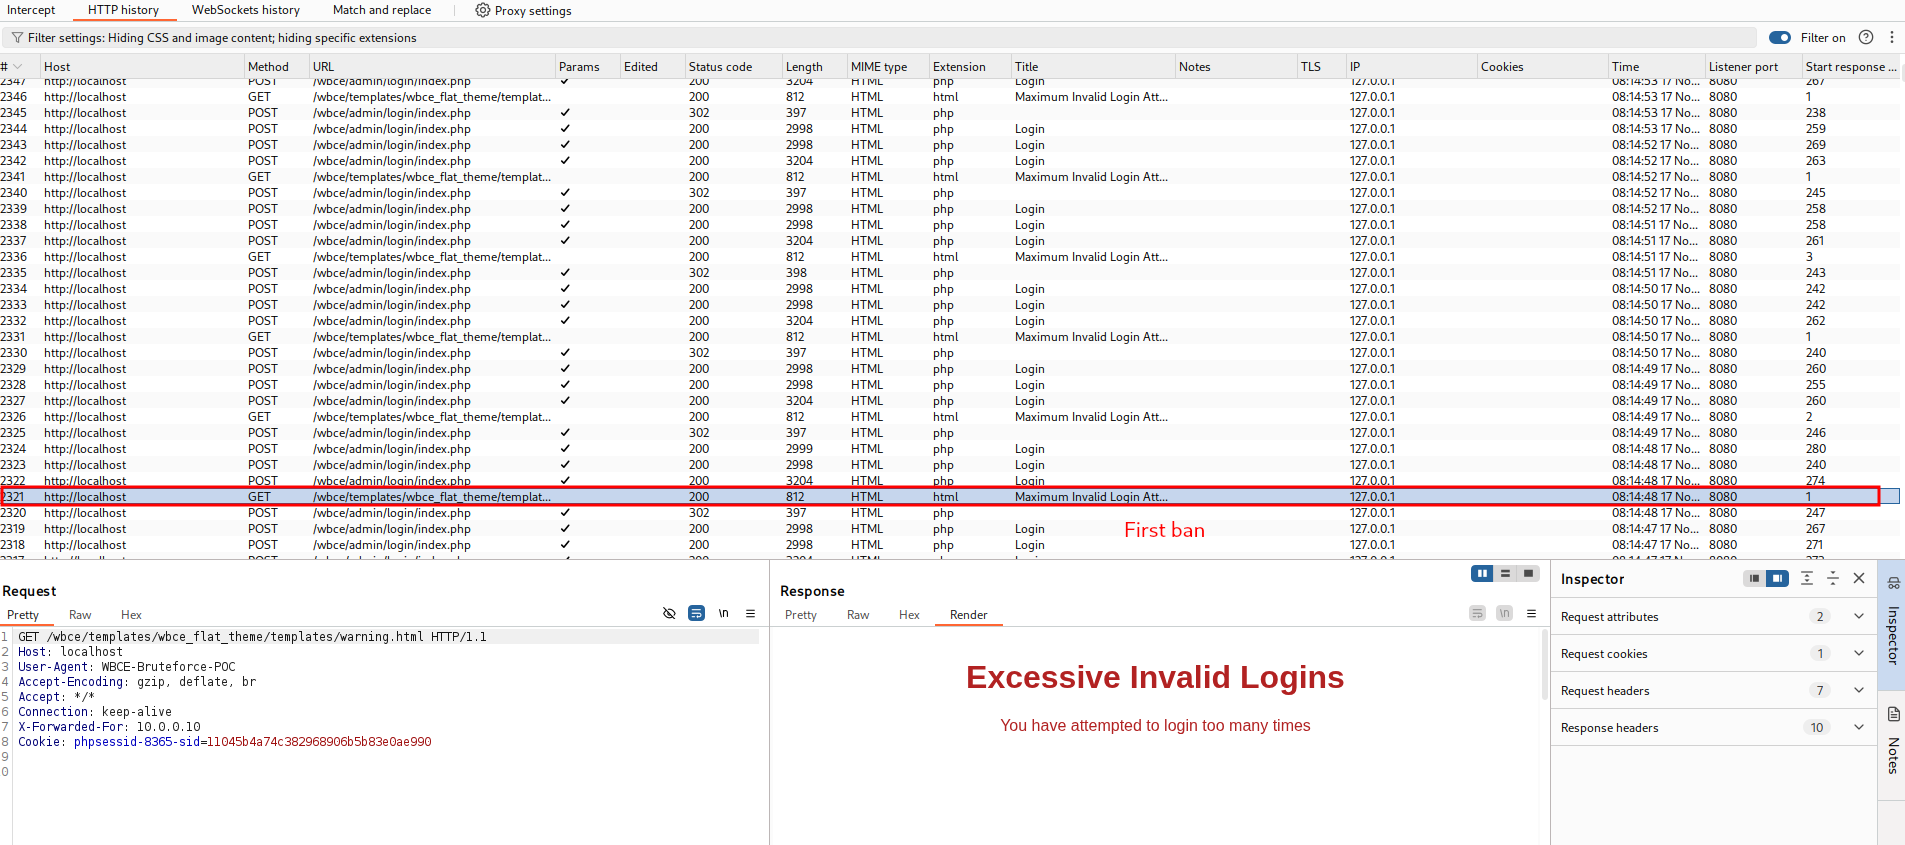 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 padayali-jd/cve-2025-63314
Detailed disclosure of CVE-2025-63314: static, non-expiring password reset token in Acora CMS 10.7.1 enabling account takeover and privilege…
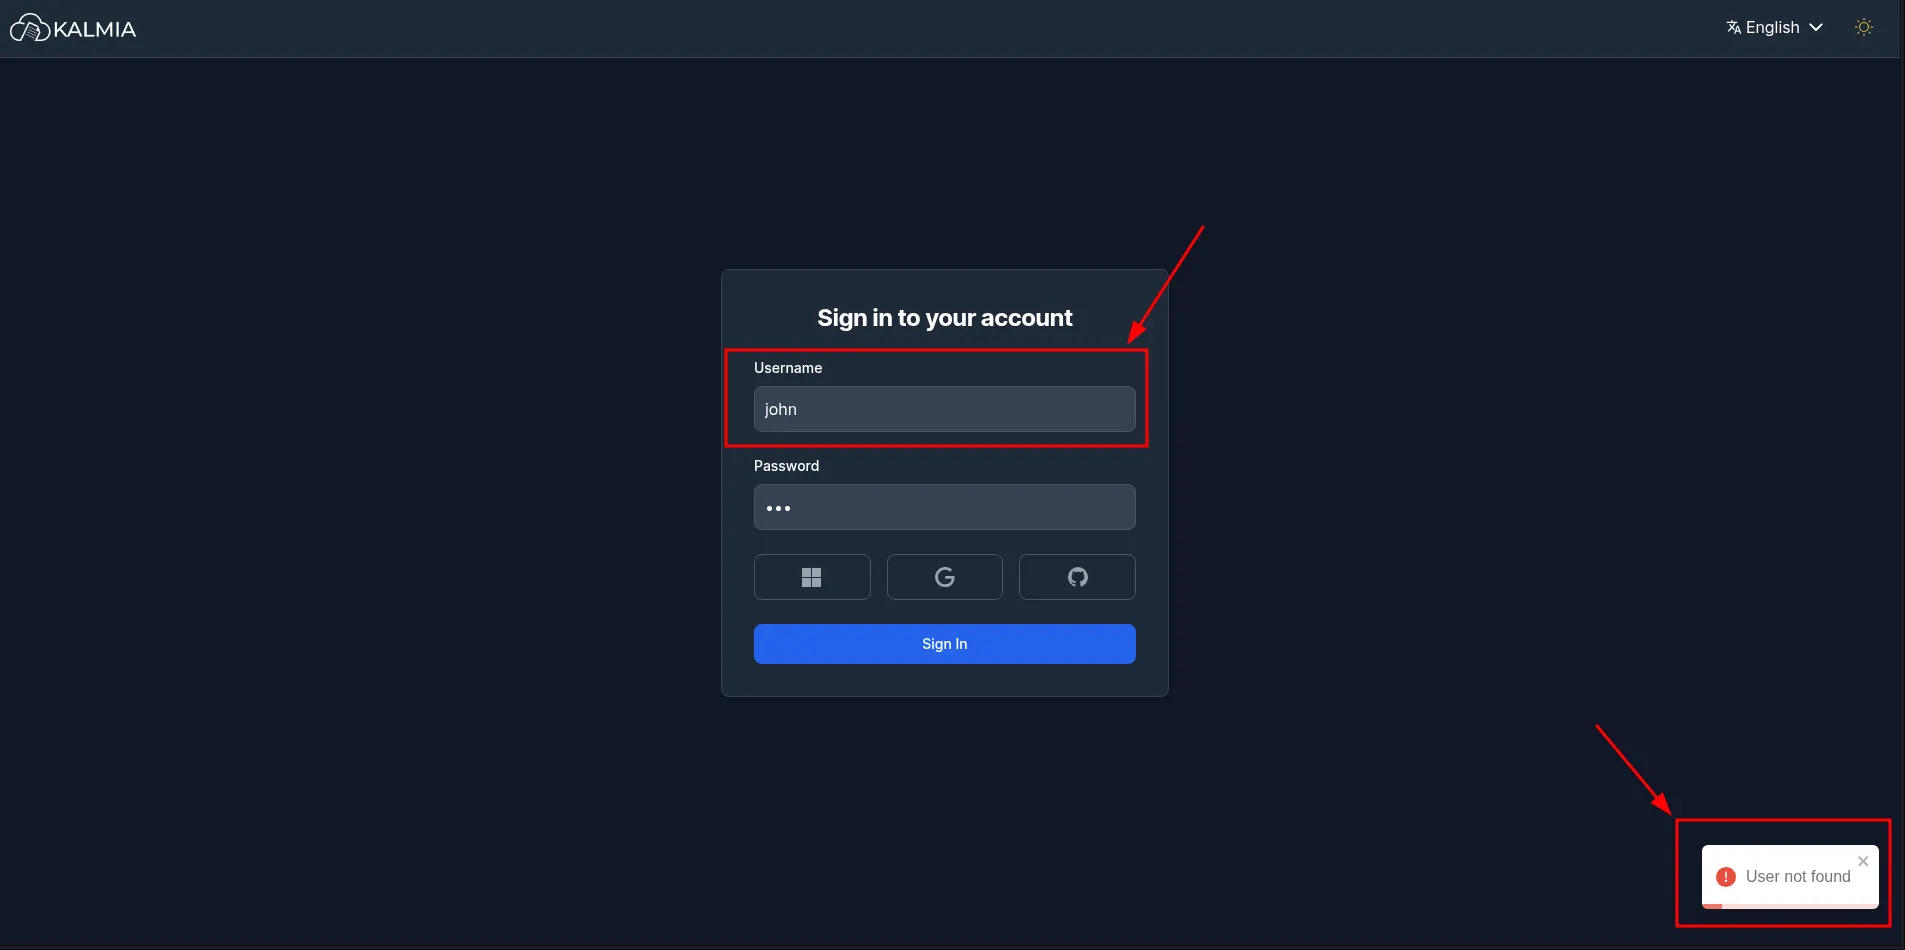 noxurge/cve-2025-65899
DifuseHQ Kalmia CMS version 0.2.0 is vulnerable to user enumeration through distinguishable error responses in the /kal-api/auth/jwt/create…
 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 paragbagul111/cve-2024-41290
FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data
 pingport80/cve-2019-17240
This is the exploit of CVE-2019-17240.
 helloandrewpaul/session-fixation-in-vvveb-cms-v1.0.6.1
CVE-2025-8517 proof-of-concept demonstrating session fixation in Vvveb CMS v1.0.6.1, enabling full administrative account takeover via arbitrary…
 abdugafforov-bobur/cve-2026-54415-poc
PoC for CVE-2026-54415 — Azuriom CMS (<1.2.11) Broken Access Control → account takeover
 0xdtc/bludit-3.9.2-auth-bruteforce-bypass-cve-2019-17240
Bludit 3.9.2 - Auth Bruteforce Bypass CVE:2019-17240 Refurbish In bash
 0xrixet/craftcms-poc-cve-2026-31266
Security research on Craft CMS authentication mechanism